
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
24 results
CVE-2021-40113 preview

CVE-2021-40113

GitHubkarammahmad/cve-2021-40113

CVE documentation repository detailing unauthenticated remote vulnerabilities in Cisco Catalyst PON Series Switches ONT, including default credential…
authenticationconfiguration-auditingexploitation+3
3 years ago
lsawhisper-bof preview

lsawhisper-bof

GitHubdazzyddos/lsawhisper-bof

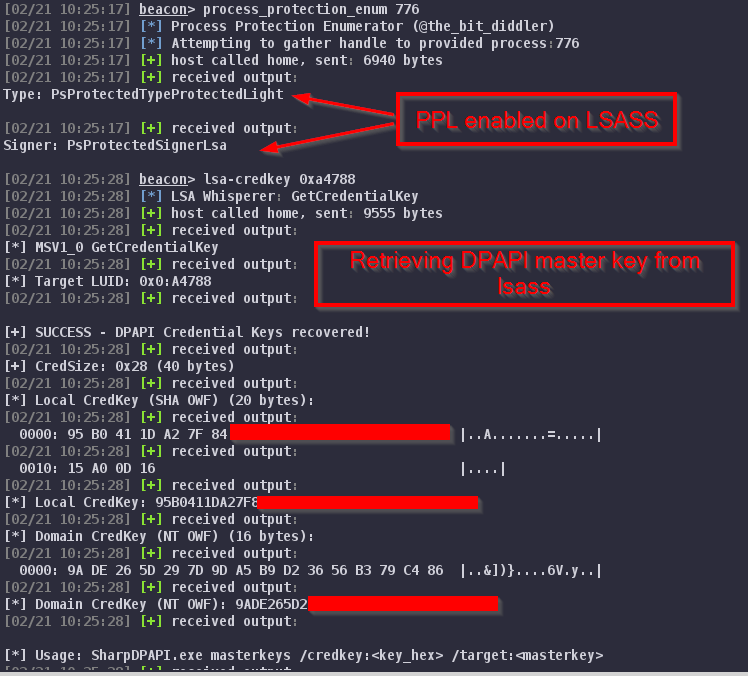
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
authenticationcommand-and-controlexploitation+4
3008 months ago
CVE-2024-0012 preview

CVE-2024-0012

GitHub0xjessie21/cve-2024-0012

CVE-2024-0012 PAN-OS: Authentication Bypass in the Management Web Interface (PAN-SA-2024-0015) RCE POC

authenticationcommand-and-controlexploitation+3
31 year ago
poisontap preview

poisontap

GitHubsamyk/poisontap

Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…

authenticationcommand-and-controldata-exfiltration+7
6.5k7 years ago
securesystemslib preview

securesystemslib

GitHubsecure-systems-lab/securesystemslib

Cryptographic and general-purpose routines for Secure Systems Lab projects at NYU
authenticationcryptographyhardware-security+1
542 days ago
CVE-2022-40684 preview

CVE-2022-40684

GitHubund3sc0n0c1d0/cve-2022-40684

Utilities for exploiting vulnerability CVE-2022-40684 (FortiOS / FortiProxy / FortiSwitchManager - Authentication bypass on administrative interface).
authenticationexploitationpenetration-testing+2
43 years ago
domestic-system preview

domestic-system

GitHubcartosys/domestic-system

Using @charmbracelet to create an Ethereum browser with style
authenticationcryptographyencryption-decryption-tools+3
216 days ago
crushftp_cve-2025-31161 preview

crushftp_cve-2025-31161

GitHubrufflabs/crushftp_cve-2025-31161

Pre-built vulnerable CrushFTP 10.8.0 binary for authorized penetration testing of CVE-2025-31161, an unauthenticated authentication bypass…
authenticationexploitationlabs-practice+3
3 months ago
ipmitest preview

ipmitest

GitHubalexoslabs/ipmitest

Shell script for testing the IPMI cipher type zero authentication bypass vulnerability (CVE-2013-4784)
authenticationexploitationhardware-security+3
11 years ago
halite preview

halite

GitHubparagonie/halite

High-level cryptography interface powered by libsodium
authenticationcryptographyencryption-decryption-tools
1.2k10 months ago
cve-2022-31749 preview

cve-2022-31749

GitHubiveresk/cve-2022-31749

PoC checker for CVE-2022-31749 exploiting a parameter injection vulnerability in WatchGuard SSH interface to exfiltrate hashed user passwords via FTP.
authenticationdata-exfiltrationexploitation+3
14 years ago
CVE-2025-8730 preview
Archived

CVE-2025-8730

GitHubbytereaper77/cve-2025-8730

Exploit demonstrating an authentication bypass vulnerability in the web interface of Belkin F9K1009 and F9K1010 routers.
authenticationexploitationpenetration-testing+3
21 year ago
CVE-2023-37755---Hardcoded-Admin-Credential-in-i-doit-Pro-25-and-below preview

CVE-2023-37755---Hardcoded-Admin-Credential-in-i-doit-Pro-25-and-below

GitHubleekenghwa/cve-2023-37755---hardcoded-admin-credential-in-i-doit-pro-25-and-below

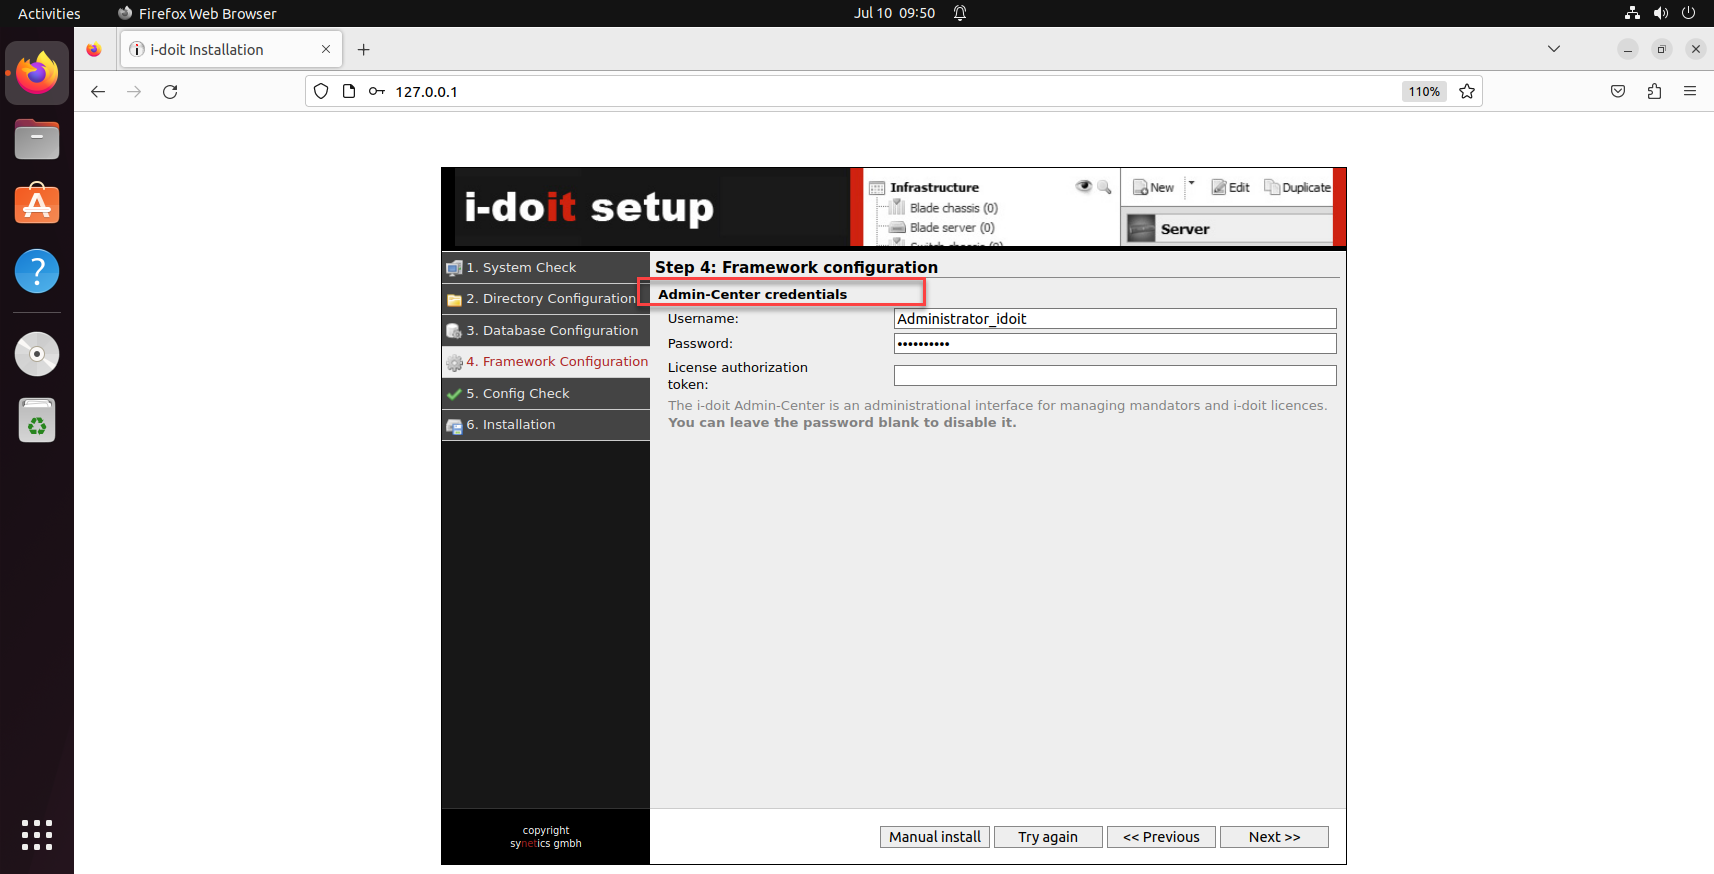
Proof-of-concept for CVE-2023-37755: hardcoded admin credentials (admin/admin) in i-doit Pro 25 and below, enabling unauthorized admin login via the…
authenticationexploitationmisconfiguration+3
3 years ago
CVE-2025-14340 preview

CVE-2025-14340

GitHubdeepsecurityresearch/cve-2025-14340

PoC for CVE-2025-14340: Admin account takeover in Payara Server
authenticationexploitationpenetration-testing+3
17 months ago
CVE-2021-3130 preview

CVE-2021-3130

GitHubjet-pentest/cve-2021-3130

Proof-of-concept for CVE-2021-3130: demonstrates credential exposure via HTML obfuscation bypass in Open-AudIT up to 4.0.2, revealing SSH, SNMP, and…
authenticationmisconfigurationpenetration-testing+2
5 years ago
self-service-password preview

self-service-password

GitHubltb-project/self-service-password

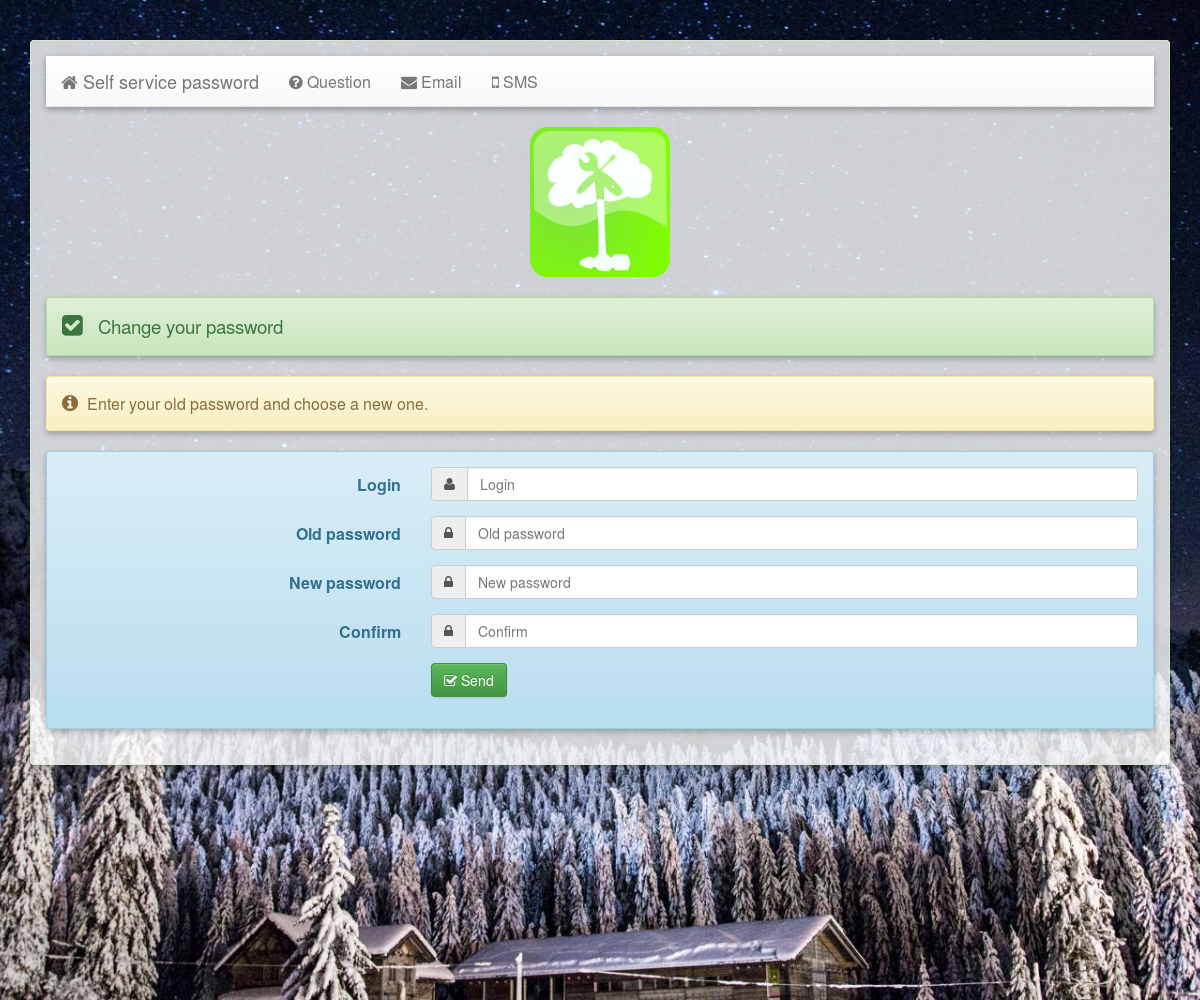
Web interface to change and reset password in an LDAP directory
authenticationcryptographyidentity-access-management+1
1.3k10h 8m ago
fortios-auth-bypass-check-CVE-2024-55591 preview

fortios-auth-bypass-check-CVE-2024-55591

GitHubwatchtowrlabs/fortios-auth-bypass-check-cve-2024-55591

Python script to detect FortiOS authentication bypass (CVE-2024-55591) by probing WebSocket connections to the management interface, identifying…
authenticationexploitationpenetration-testing+3
651 year ago
even-you-brutus preview

even-you-brutus

GitHubj-baines/even-you-brutus

Dictionary Brute Force of the Mikrotik RouterOS 6.x Web Interface

authenticationembedded-systems-securityexploitation+5
93 years ago
Previous12Next