
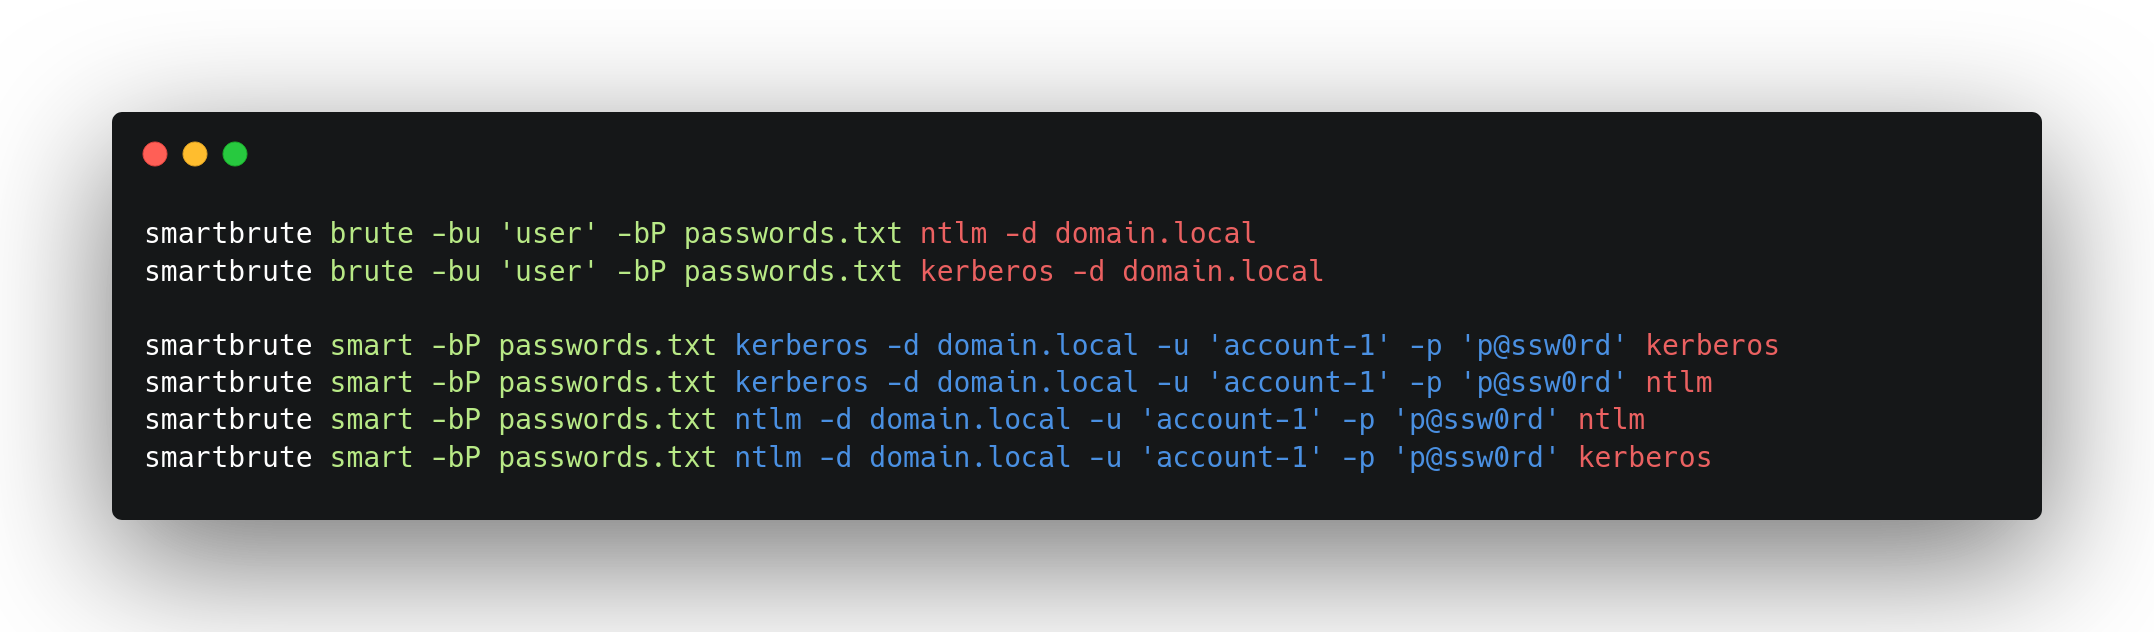
smartbrute
 shutdownrepo/smartbrute
Password spraying and bruteforcing tool for Active Directory Domain Services
authenticationinformation-gatheringpassword-attacks+1
388
shutdownrepo/smartbrutePassword spraying and bruteforcing tool for Active Directory Domain Services
 alt3kx/cve-2026-18963
Detection and verification tool for CVE-2026-18963, a Keycloak reset-credentials state bypass. Performs version fingerprinting, realm/client/user…
 wildandeveloper/cve-2026-58231
Non-destructive detection and precondition-verification tool for CVE-2026-58231, probing SAP Commerce Cloud Data Hub endpoints, default OAuth…
 tx-one/cve-2025-31161
CrushFTP CVE-2025-31161 Exploit Tool 🔓
 skynoxk/cve-2025-40554
CVE-2025-40554 Exploitation
 bytewreck/dumpguard
Proof-of-Concept tool for extracting credential material from protected sessions on modern Windows systems.
 ipsbruno/cve-2022-1162
Exploit tool for CVE-2022-1162 that enumerates GitLab users and performs authentication bypass via a crafted login request.
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 imancybersecurity/cve-2023-27350-poc
Proof-of-concept exploit for CVE-2023-27350 targeting authentication bypass in PaperCut MF/NG print management software. Includes Shodan dorks for…
 assurancemaladiesec/ad-description-password-finder
Retrieve AD accounts description and search for password in it
 nccgroup/carnivore
Tool for assessing on-premises Microsoft servers authentication such as ADFS, Skype, Exchange, and RDWeb
 greenwolf/spray
A Password Spraying tool for Active Directory Credentials by Jacob Wilkin(Greenwolf)
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 maaaaz/crackmapexecwin
The great CrackMapExec tool compiled for Windows
 oldboy21/ldap-password-hunter
Automated tool that hunts for world-readable passwords in Active Directory LDAP databases by leveraging Kerberos authentication and ldapsearch to…
 shac0x/wonka
Wonka is a sweet Windows tool that extracts Kerberos tickets from the Local Security Authority (LSA) cache. Like finding a ticket, but for security…
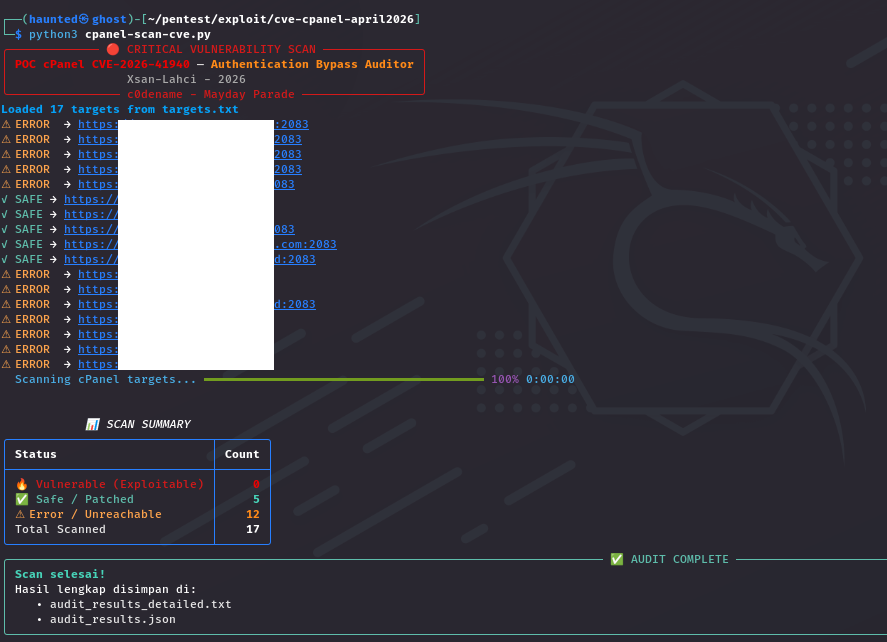 xsanflip/poc-cpanel-cve-2026-41940
Multi-threaded security auditing tool that detects CVE-2026-41940, an authentication bypass in cPanel/WHM, using CRLF injection and dynamic port…
 redteampentesting/pretender
Your MitM sidekick for relaying attacks featuring DHCPv6 DNS takeover as well as mDNS, LLMNR and NetBIOS-NS spoofing.