
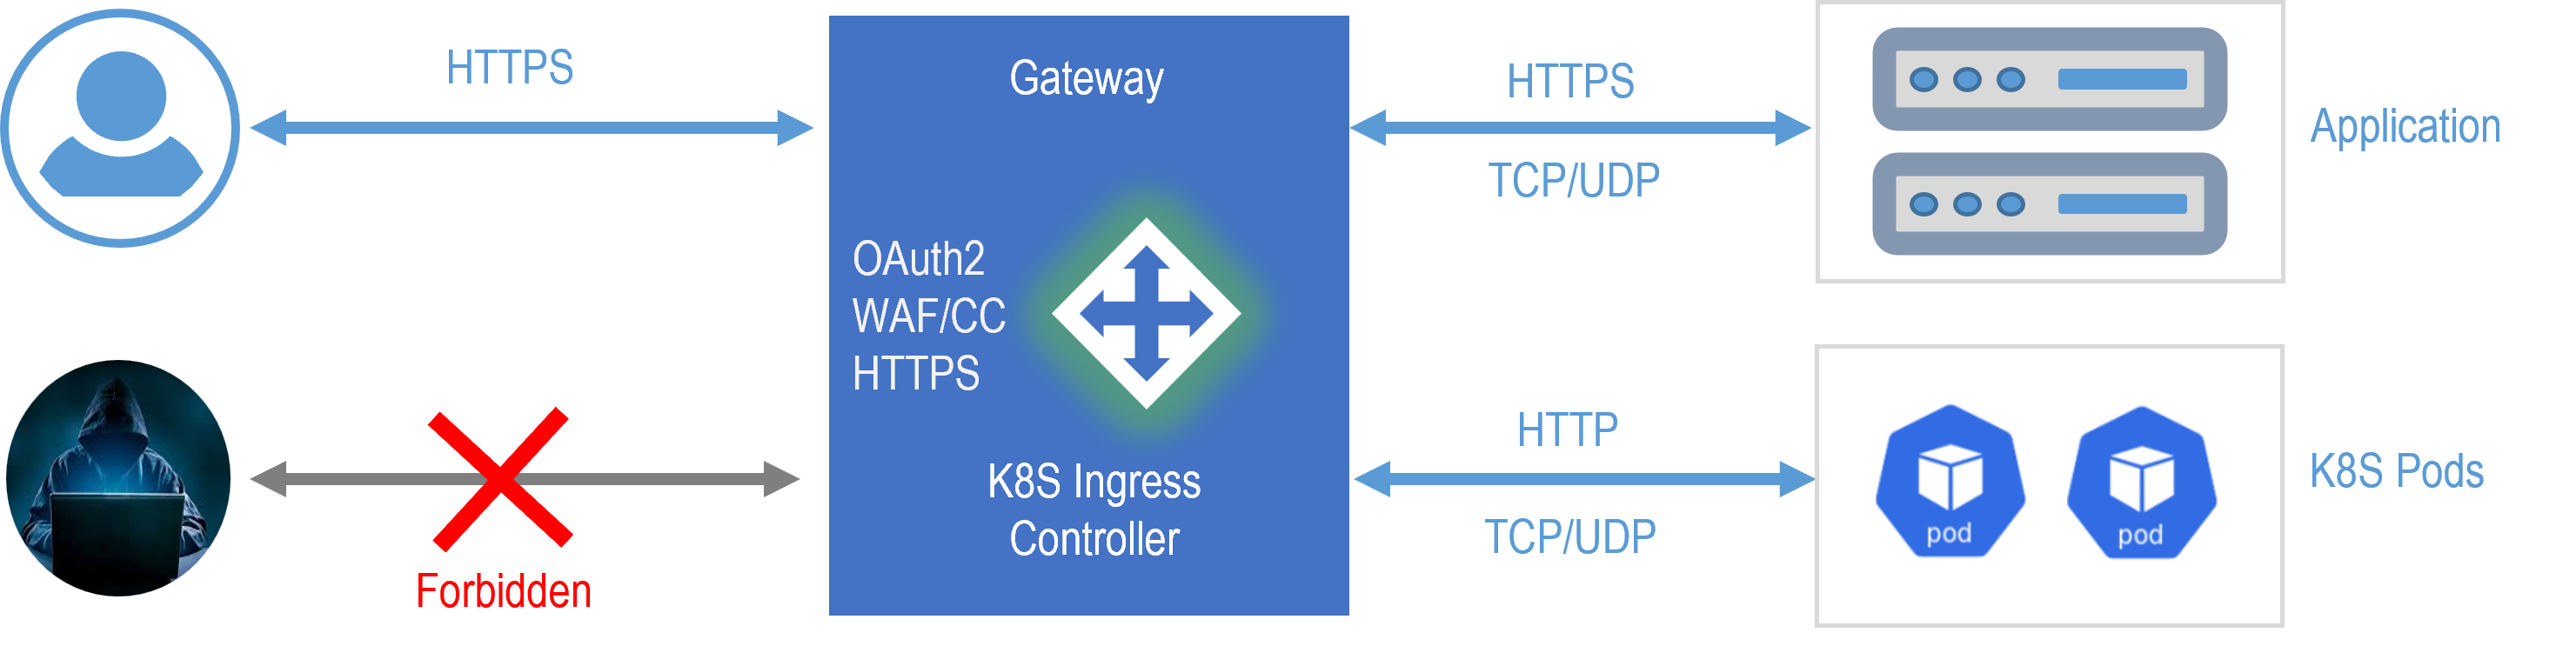
janusec
 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
api-securityauthenticationcloud-security+8
1.2k
janusec/janusecUnified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
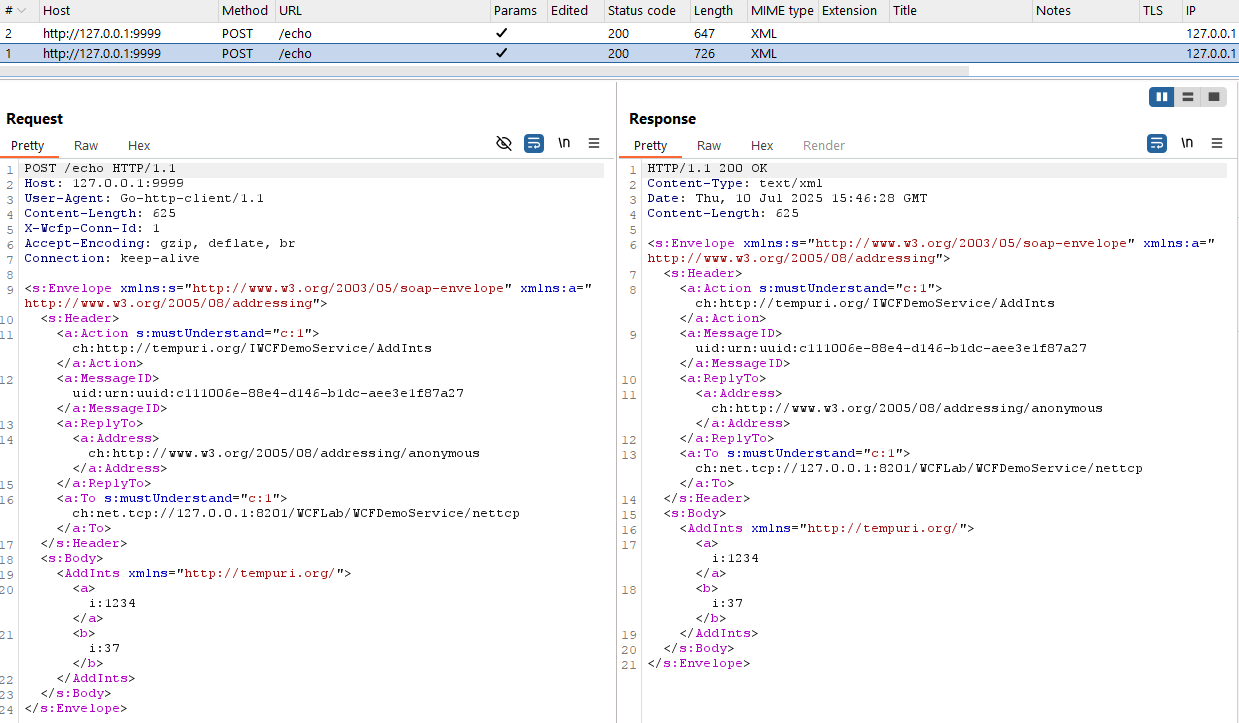 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.
 ssh-mitm/ssh-mitm
Mirror moved — see GitHub and Codeberg
 nccgroup/berserko
Burp Suite extension to perform Kerberos authentication
 quarantyne/quarantyne
Modern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
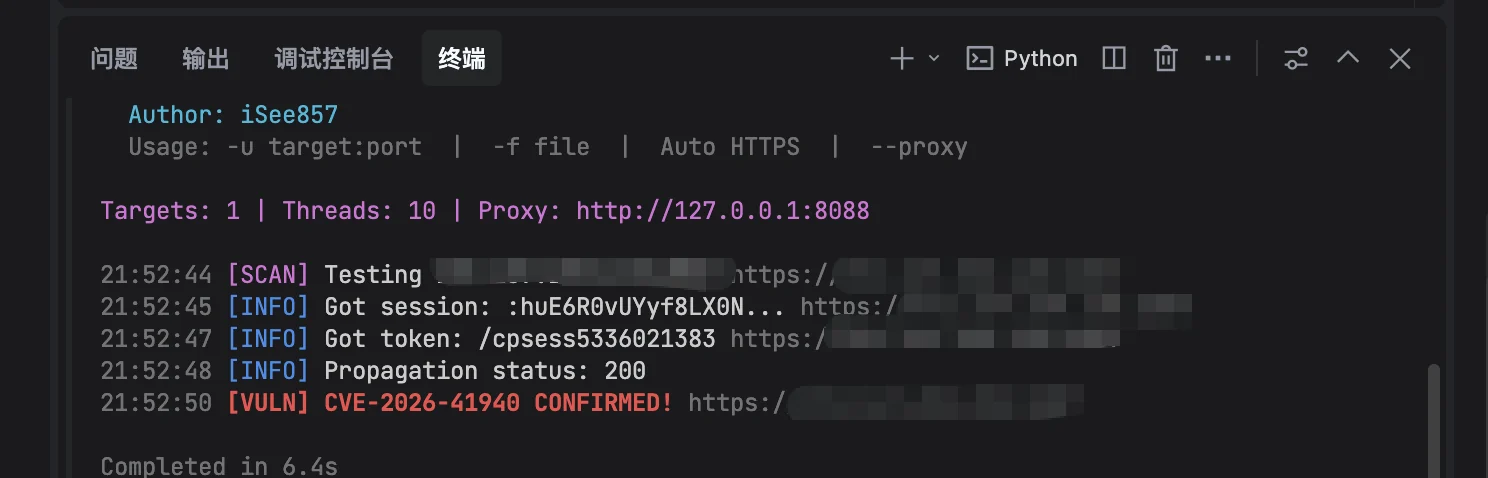 isee857/cpanel-whm-cve-2026-41940-authbypass
Scanner for cPanel & WHM authentication bypass (CVE-2026-41940) that detects vulnerable versions via CRLF injection and session manipulation, with…
 r0otk3r/cve-2025-31161
Python exploit for CVE-2025-31161, an authentication bypass in CrushFTP. Retrieves user lists via crafted CrushAuth and AWS4-HMAC-SHA256 headers.…
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 rz1027/cve-2026-20896
Public PoC and detector for CVE-2026-20896 ("Gitea Docker: One Header, Any User")
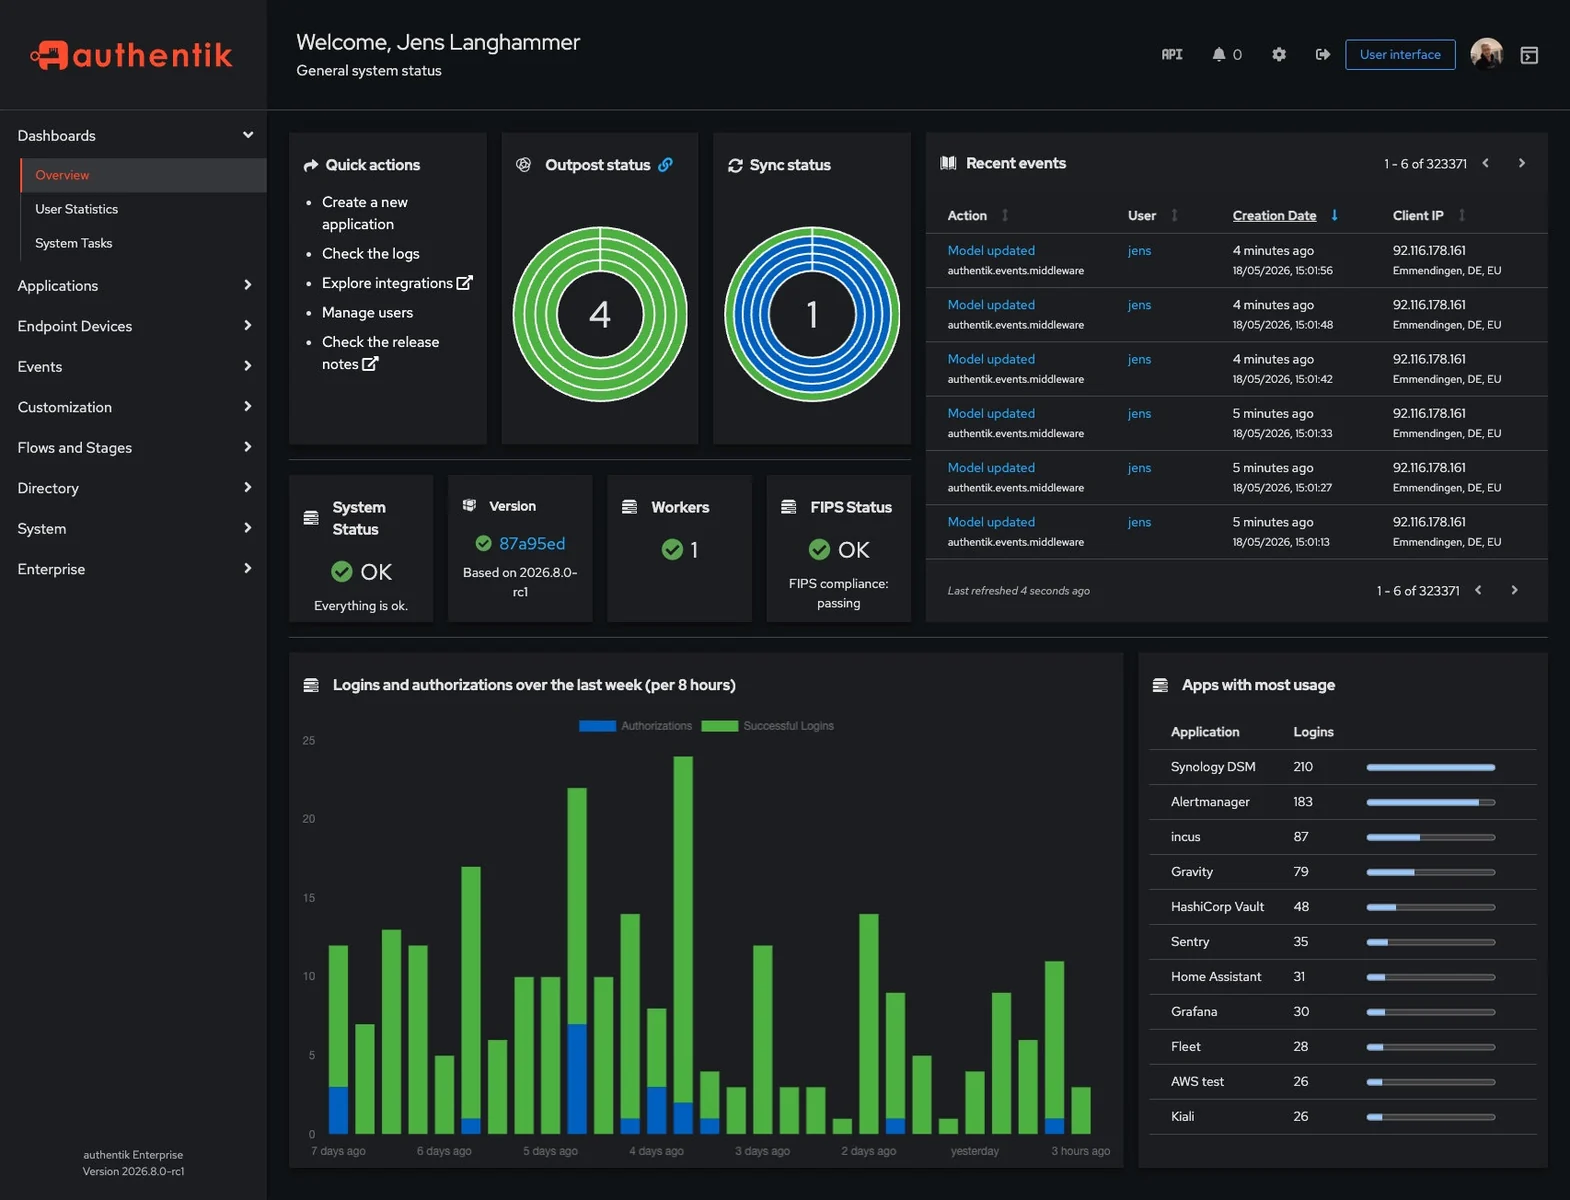 goauthentik/authentik
Provides open-source SSO and identity provider functionality with SAML, OAuth2/OIDC, LDAP, and RADIUS support for centralized authentication,…
 oauth2-proxy/oauth2-proxy
A reverse proxy that provides authentication with Google, Azure, OpenID Connect and many more identity providers.
 pomerium/pomerium
Identity-aware reverse proxy that delivers zero-trust access to internal apps and services via context-aware policy, continuous verification, and no…
 drk1wi/modlishka
Modlishka. Reverse Proxy.
 ory/oathkeeper
A cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
 vicanso/pingap
A reverse proxy like nginx, built on pingora, simple and efficient.