
exploit-mikrotik-2026
 blackhatexploitation/exploit-mikrotik-2026
CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit
authenticationexploitationinformation-gathering+4
13
blackhatexploitation/exploit-mikrotik-2026CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit
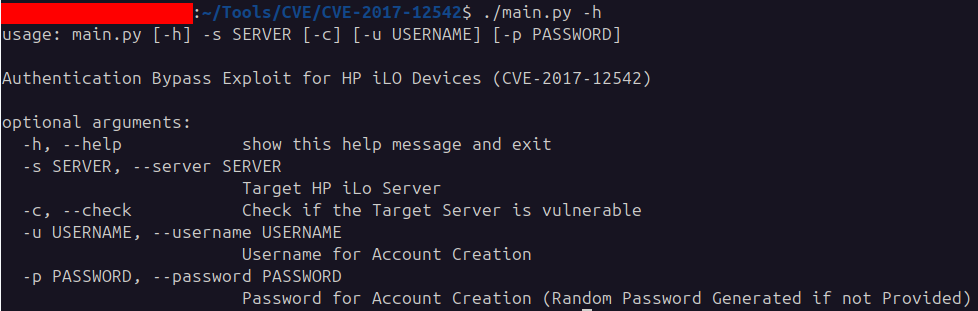 gill-singh-a/cve-2017-12542-exploit
Proof-of-concept exploit for CVE-2017-12542, an authentication bypass vulnerability in HP iLO. Allows vulnerability detection and unauthorized…
 savsch/poc_cve-2019-0217
Proof-of-concept exploit for CVE-2019-0217, a race condition in Apache HTTP Server's mod_auth_digest allowing authentication bypass. Includes…
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 rmhowe425/poc-cve-2026-93680
Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
 malikhamza7/cve-2026-22794-poc
🔴 CVE-2026-22794 - Appsmith Password Reset Account Takeover via Origin Header Injection | PoC Exploit + Nuclei Template
 murrez/cve-2026-19660
Python PoC scanner and exploit for CVE-2026-14378, a pre-auth administrator session takeover in the DevKit Pro WordPress plugin via forged…
 murrez/cve-2026-14378
Python PoC scanner and exploit helper for CVE-2026-14378, an unauthenticated admin session takeover in the DevKit Pro WordPress plugin via forged…
 t0w0t/poc-cve-2026-18963
Proof-of-concept exploit for CVE-2026-18963, an authentication bypass in Keycloak's forgot-password flow, allowing password reset without proper…
 lorenzocamilli/cve-2026-45332-poc
Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…
 hunt-benito/ash-authentication-oauth2-oidc-account-takeover-cve-2026-49757-email-based-user-matching
Proof-of-concept exploit for CVE-2026-49757 demonstrating OAuth2/OIDC account takeover via email-based user matching in AshAuthentication, with…
 bugresearch/cve-2026-6274
Proof-of-concept exploit for CVE-2026-6274, an authentication bypass in Redline WR3200 routers allowing unauthorized password change via static…
 jake-young-dev/cve-2026-29000
Proof-of-concept exploit for CVE-2026-29000, an authentication bypass in pac4j-jwt, demonstrating JWT crafting with arbitrary roles for unauthorized…
 amirhosseinjamshidi64/cve-2026-7567-poc
Proof-of-concept exploit for CVE-2026-7567, an authentication bypass in WordPress Temporary Login Plugin <= 1.0.0, enabling account takeover. For…
 biitts/cve-2026-72001-pangolin-cross-org-auth-bypass
PoC for CVE-2026-72001 — Pangolin < 1.22.0 cross-organization resource authentication bypass via the share-link access-token endpoint (CWE-639, CVSS…
 hemp3l/cve-2017-6640-poc
Proof of concept for CVE-2017-6640 as burp extension
 kimdir01/cve-2026-9090-poc
PoC for CVE-2026-9090 — Casdoor SAML signature bypass (CWE-347). Reproduction-only; coordinated via CERT/CC VU#780781.
 dua2z3rr/cve-2026-29000-poc
CVE-2026-29000 - pac4j-jwt (< 4.5.9 / < 5.7.9 / < 6.3.3) JwtAuthenticator authentication bypass PoC