

CVE-2021-26088
 theogobinet/cve-2021-26088
PoC for CVE-2021-26088 written in PowerShell
authenticationeducationexploitation+3
3
theogobinet/cve-2021-26088PoC for CVE-2021-26088 written in PowerShell
 julesbsz/cve-2024-10924
POC for CVE-2024-10924 written in Python
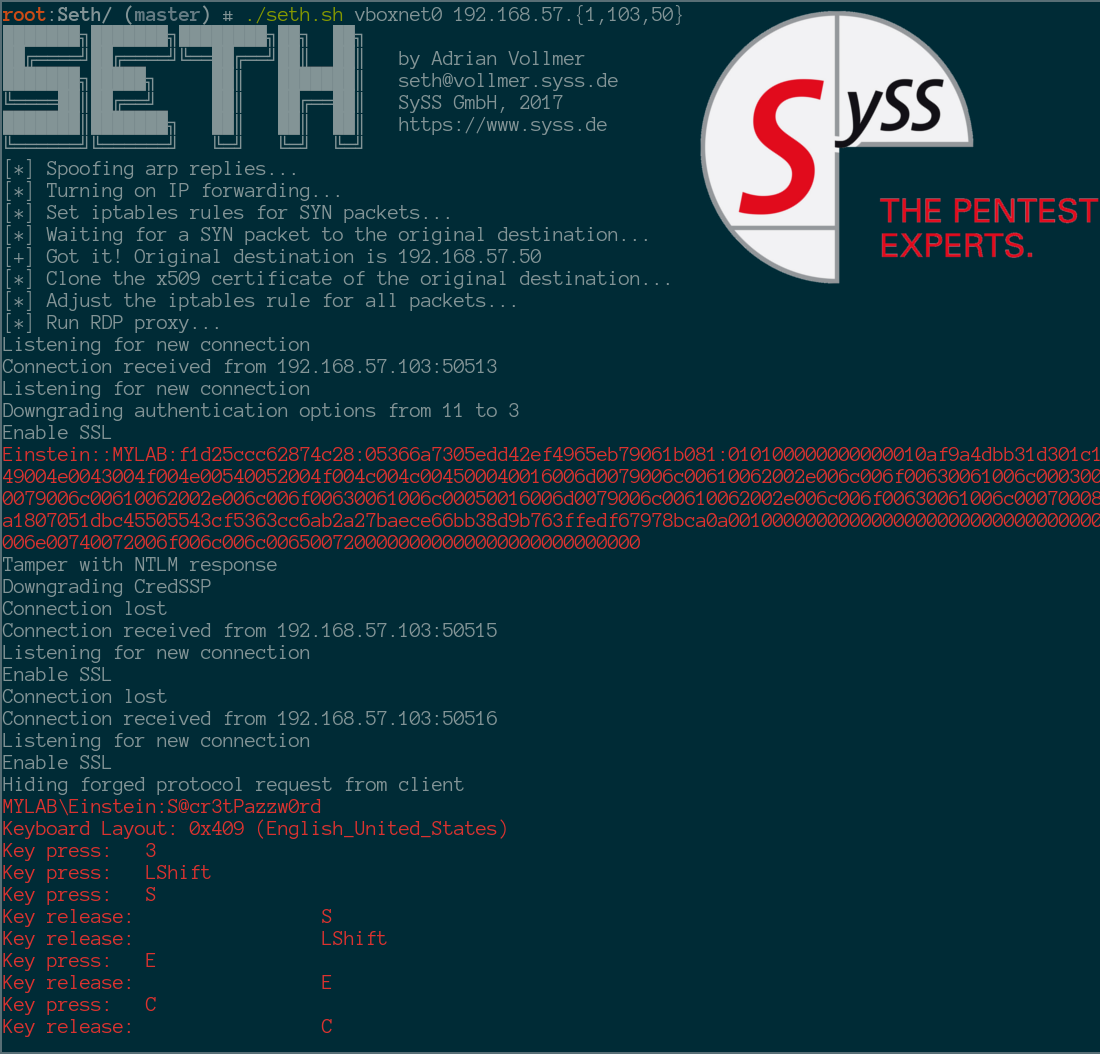 syss-research/seth
Perform a MitM attack and extract clear text credentials from RDP connections
 ory/oathkeeper
A cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
 brendan-rius/c-jwt-cracker
JWT brute force cracker written in C
 ustayready/credsniper
CredSniper is a phishing framework written with the Python micro-framework Flask and Jinja2 templating which supports capturing 2FA tokens.
 m0n1x90/adreaper
A fast enumeration tool for Windows Active Directory Pentesting written in Go
 adityathebe/poc-cve-2018-0114
POC for CVE-2018-0114 written in Go
 supabase/auth
A JWT based API for managing users and issuing JWT tokens
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.
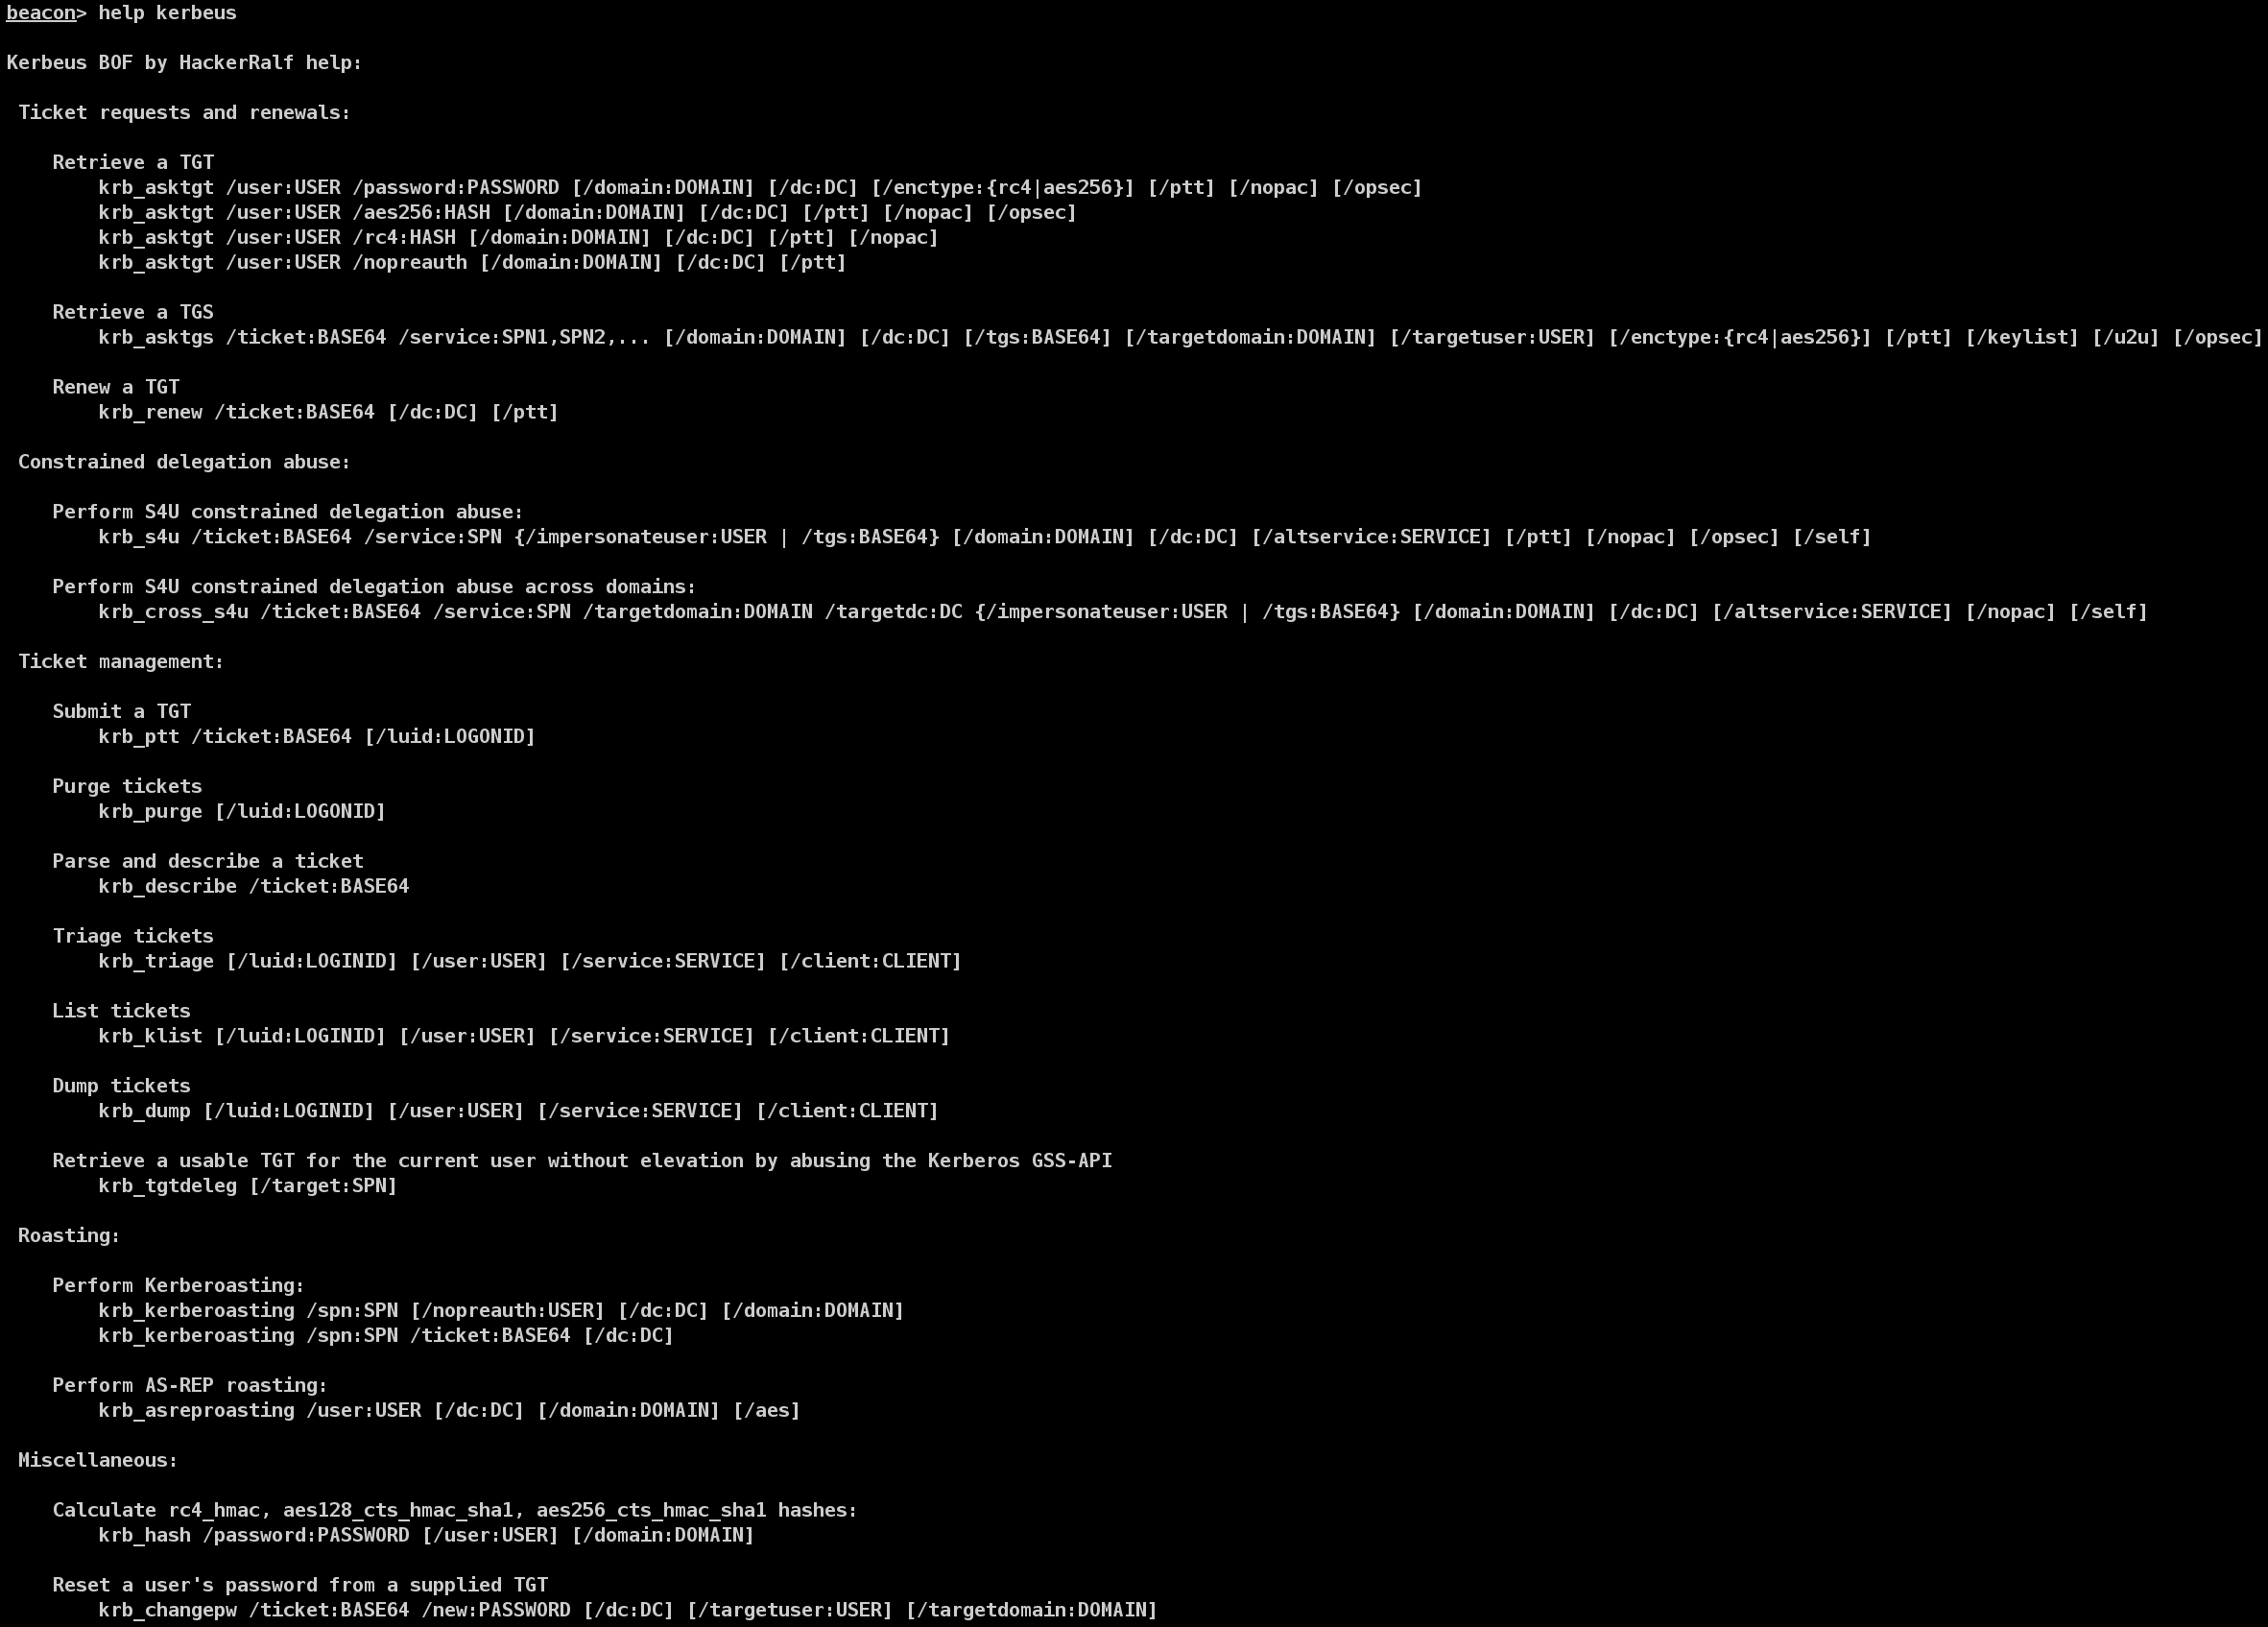 ralfhacker/kerbeus-bof
BOF for Kerberos abuse (an implementation of some important features of the Rubeus).
 trustedsec/ridenum
Rid_enum is a null session RID cycle attack for brute forcing domain controllers.
 praetorian-inc/ntlmrecon
A tool for performing light brute-forcing of HTTP servers to identify commonly accessible NTLM authentication endpoints.
 shellster/ldapper
LDAP Querying without the Suck
 iomoath/sharpspray
Active Directory password spraying tool. Auto fetches user list and avoids potential lockouts.
 opfour/op4
Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…