
CVE-2025-58434
 r3vpwnx/cve-2025-58434
Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…
authenticationexploitationpenetration-testing+3
r3vpwnx/cve-2025-58434Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…
 jumpseclabs/tokenflare
Serverless AITM Simulation Framework for Entra ID and M365
 deepsecurityresearch/cve-2025-14340
PoC for CVE-2025-14340: Admin account takeover in Payara Server
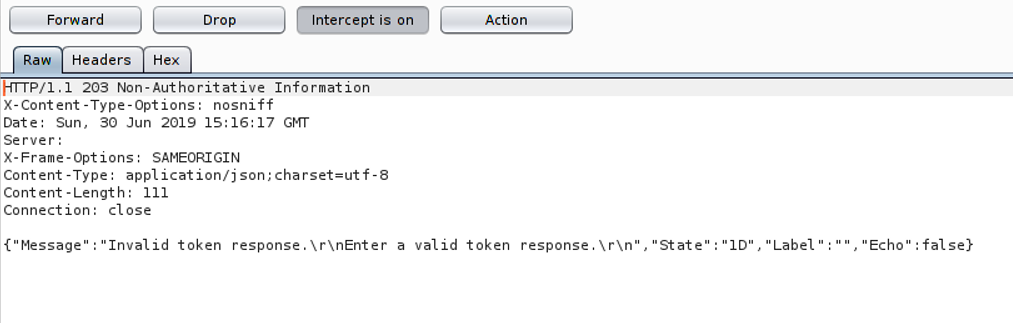 furqankhan1/cve-2019-13496
Proof-of-concept exploit demonstrating OTP bypass in One Identity Cloud Access Manager 8.1.3 via MITM/SSL-strip, SAML response replay, and injected…