

CVE-2025-13390
 nxploited/cve-2025-13390
WP Directory Kit <= 1.4.4 - Authentication Bypass to Privilege Escalation via Account Takeover
authenticationexploitationpayload-development+5
1
nxploited/cve-2025-13390WP Directory Kit <= 1.4.4 - Authentication Bypass to Privilege Escalation via Account Takeover
 rishuranjanofficial/jwtweak
Detects the algorithm of input JWT Token and provide options to generate the new JWT token based on the user selected algorithm.
 ap0dexme0/cve-2023-27350
Perfom With Massive Authentication Bypass In PaperCut MF/NG
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 praetorian-inc/adfsrelay
Proof of Concept Utilities Developed to Research NTLM Relaying Attacks Targeting ADFS
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 praetorian-inc/ntlmrecon
A tool for performing light brute-forcing of HTTP servers to identify commonly accessible NTLM authentication endpoints.
 l4rm4nd/pyadrecon
Python3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
 lazaars/ultrarealy_with_cve-2019-1040
Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit
 mihat2/resetnightmare-impacket
CVE-2026-27912 (ResetNightmare) — Linux/impacket port of Semperis Community's Invoke-ResetNightmare PoC
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
 sergiovks/ssh-user-enum-python3-cve-2018-15473
SSH User Enumerator in Python3, CVE-2018-15473, I updated the code of this exploit (https://www.exploit-db.com/exploits/45939) to work with python3…
 tony102741/cve-2026-15469
Advisory and technical analysis of CVE-2026-15469, a hard-coded RSA-512 mesh group private key in TP-Link Deco routers, including root cause, impact,…
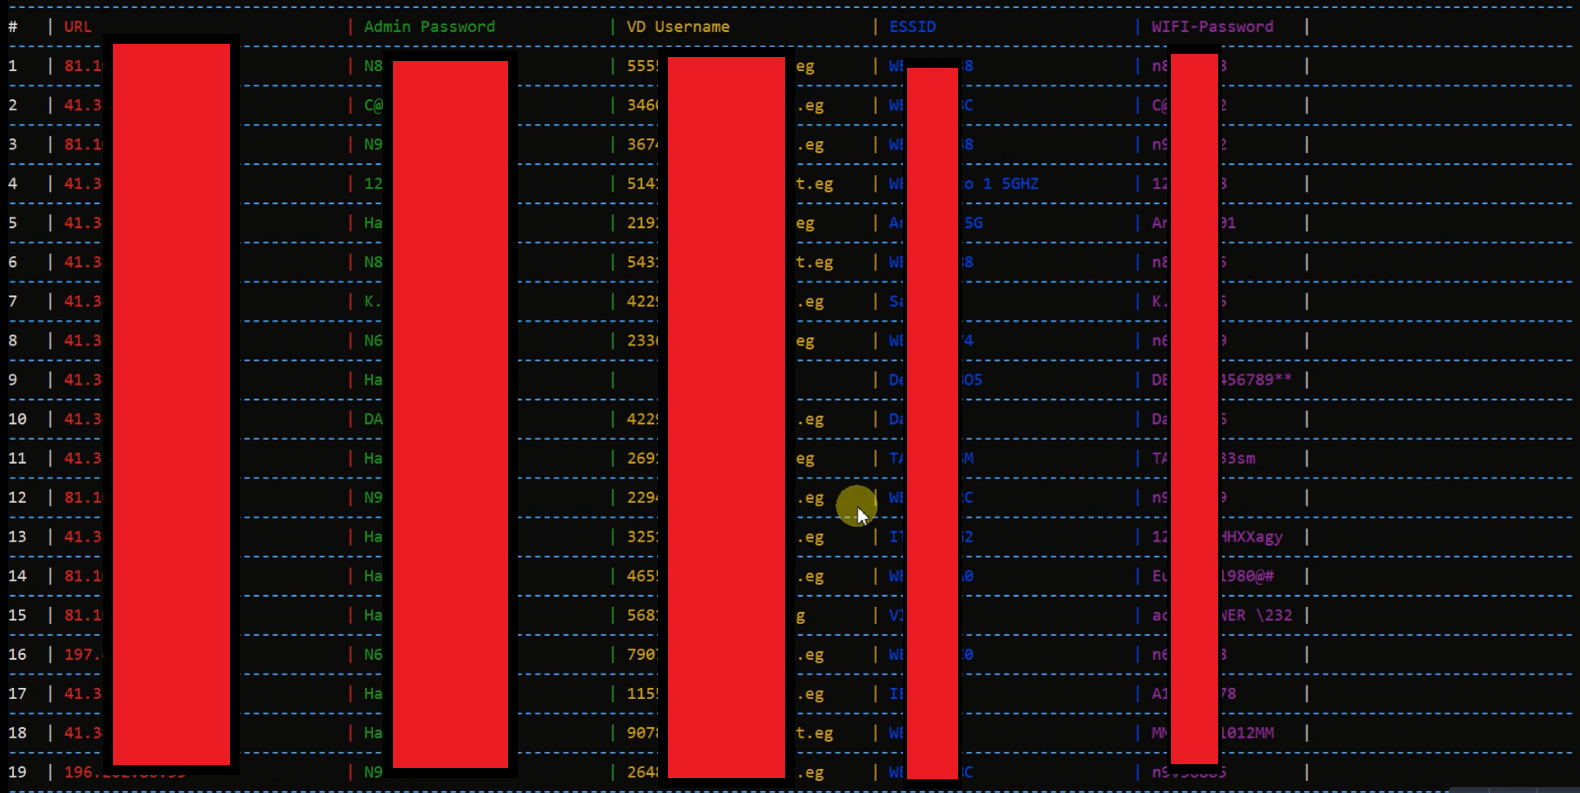 minanagehsalalma/cve-2026-34472-auth-bypass-zte-h188a-router
Technical breakdown of CVE-2026-34472, an auth bypass via leaked credentials affecting ZTE H188A routers.