
uptime-kuma-setup-toctou
 abraxas/uptime-kuma-setup-toctou
Proof-of-concept for a TOCTOU race in Uptime Kuma's first-run Socket.IO setup, letting an unauthenticated attacker plant a hidden second admin and…
authenticationexploitationlabs-practice+5
abraxas/uptime-kuma-setup-toctouProof-of-concept for a TOCTOU race in Uptime Kuma's first-run Socket.IO setup, letting an unauthenticated attacker plant a hidden second admin and…
 cyberharsh/libssh-server-cve-2018-10933
Proof-of-concept exploit for CVE-2018-10933, demonstrating SSH authentication bypass via MSG_USERAUTH_SUCCESS injection. Includes Docker setup and…
 gman0x00/keycloak-cve-2026-18963
PoC, Dockerfile playground and root cause from patch diff analysis.
 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
 hpt-intern-task-submission/cve-2022-46169
Step-by-step analysis of CVE-2022-46169: unauthenticated remote code execution in Cacti via authentication bypass and command injection, with Docker…
 hashicorp/vault
A tool for secrets management, encryption as a service, and privileged access management
 cyph/cyph
Cryptographically secure messaging and social networking service.
 fariszr/knocker
Knocker, a knock based access control service for your homelab
 red-darkin/cve-2026-18963-keycloak
Proof-of-concept exploit for CVE-2026-18963, a critical Keycloak reset-credentials bypass enabling unauthenticated account takeover. Includes lab…
 oscerd/cve-2026-66908
Proof-of-concept reproducer for Apache Camel JWT authentication bypass (CVE-2026-66908) demonstrating missing iss/aud validation in…
 rufflabs/crushftp_cve-2025-31161
Pre-built vulnerable CrushFTP 10.8.0 binary for authorized penetration testing of CVE-2025-31161, an unauthenticated authentication bypass…
 minh3102011/cve-2026-18963_analyst
Docker-based lab for reproducing Keycloak CVE-2026-18963, including vulnerable version setup, realm seeding, and source-level workflow analysis with…
 ltb-project/self-service-password
Web interface to change and reset password in an LDAP directory
 mdvpat/cve-2026-55957-poc
Reproducible Docker lab for the Apache Tomcat JNDIRealm GSSAPI authentication bypass
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 dinosn/cve-2026-82329-jfrog-artifactory
Reproducible Docker lab and Python PoC for CVE-2026-82329, an unauthenticated auth-bypass in JFrog Artifactory leading to admin takeover, with…
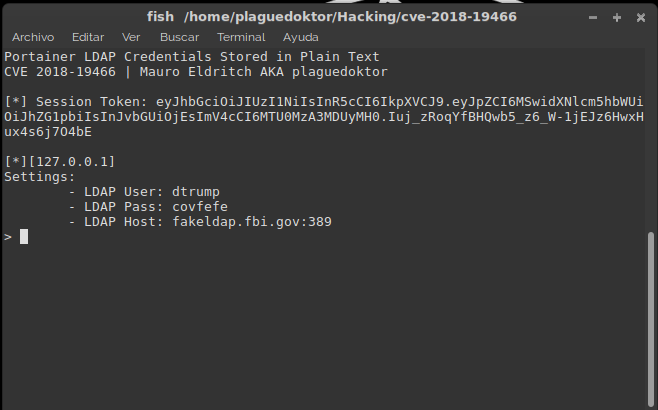 mauroeldritch/lempo
LEMPO (Ldap Exposure on POrtainer) is an exploit for CVE-2018-19466 (LDAP Credentials Disclosure on Portainer). Featured @ DevFest Siberia 2018
 eqstlab/cve-2026-49869
PoC and Docker lab for CVE-2026-49869, an unauthenticated RCE in Kestra OSS via an AuthenticationFilter path bypass that allows flow creation and…