
CVE-2022-39227
 user0x1337/cve-2022-39227
CVE-2022-39227 : Proof of Concept
authenticationctfexploitation+3
user0x1337/cve-2022-39227CVE-2022-39227 : Proof of Concept
 t0w0t/poc-cve-2026-18963
Proof-of-concept exploit for CVE-2026-18963, an authentication bypass in Keycloak's forgot-password flow, allowing password reset without proper…
 hemp3l/cve-2017-6640-poc
Proof of concept for CVE-2017-6640 as burp extension
 lorenzocamilli/cve-2026-45332-poc
Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…
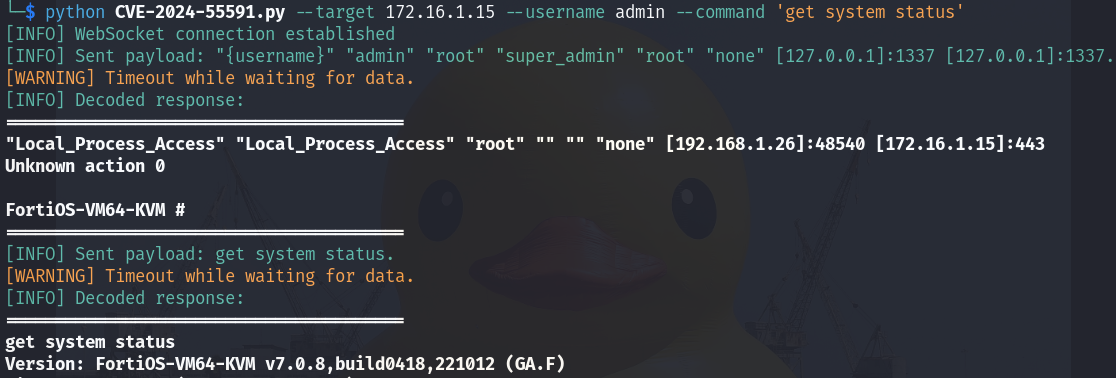 virus-or-not/cve-2024-55591
An Authentication Bypass Using an Alternate Path or Channel vulnerability [CWE-288] affecting FortiOS and FortiProxy may allow a remote attacker to…
 biitts/cve-2026-72001-pangolin-cross-org-auth-bypass
PoC for CVE-2026-72001 — Pangolin < 1.22.0 cross-organization resource authentication bypass via the share-link access-token endpoint (CWE-639, CVSS…
 kimdir01/cve-2026-9090-poc
PoC for CVE-2026-9090 — Casdoor SAML signature bypass (CWE-347). Reproduction-only; coordinated via CERT/CC VU#780781.
 dua2z3rr/cve-2026-29000-poc
CVE-2026-29000 - pac4j-jwt (< 4.5.9 / < 5.7.9 / < 6.3.3) JwtAuthenticator authentication bypass PoC
 hunt-benito/ash-authentication-oauth2-oidc-account-takeover-cve-2026-49757-email-based-user-matching
Proof-of-concept exploit for CVE-2026-49757 demonstrating OAuth2/OIDC account takeover via email-based user matching in AshAuthentication, with…
 xqi1337/poc-cve-2026-0073
CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC
 blackhatexploitation/exploit-mikrotik-2026
CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit
 zycoder0day/cve-2026-8181
CVE-2026-8181 - Burst Statistics 3.4.0-3.4.1.1 Unauthenticated Authentication Bypass to Admin Account Takeover | Proof of Concept
 boonjune/poc-cve-2022-30600
A proof of concept for CVE-2022-30600
 offensivebias20/cve-2026-34990-poc
Proof-of-concept research and technical analysis of CVE-2026-34990, a CUPS local privilege-escalation flaw via IPP request flow and…
 ajtazer/cve-2025-51471-poc
This PoC is for educational and authorized security testing purposes only. Do NOT use against systems you don't own.
 peace-maker/cve-2024-45337
Proof of Concept for CVE-2024-45337 against Gitea and Forgejo
 horizon3ai/cve-2024-28987
Proof-of-concept exploit for CVE-2024-28987 targeting SolarWinds Web Help Desk hardcoded credential vulnerability. Automates exploitation via URL…
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService