
CVE-2025-3616
 b4d-53ct0r/cve-2025-3616
Metasploit module exploiting arbitrary file upload in Greenshift WordPress plugin (CVE-2025-3616) to achieve RCE via MIME spoofing, with…
authenticationexploit-frameworkspayload-development+3
b4d-53ct0r/cve-2025-3616Metasploit module exploiting arbitrary file upload in Greenshift WordPress plugin (CVE-2025-3616) to achieve RCE via MIME spoofing, with…
 cravaterouge/bloodyad
LDAP-based Active Directory privilege escalation framework supporting pass-the-hash, pass-the-ticket, and certificate authentication for automated…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 gentilkiwi/mimikatz
A little tool to play with Windows security
 horizon3ai/cve-2022-40684
A proof of concept exploit for CVE-2022-40684 affecting Fortinet FortiOS, FortiProxy, and FortiSwitchManager
 jackofmosttrades/bluebox
Automated Exploit Toolkit for CVE-2015-6095 and CVE-2016-0049
 taroballzchen/cve-2022-40684-metasploit-scanner
An authentication bypass using an alternate path or channel in Fortinet product
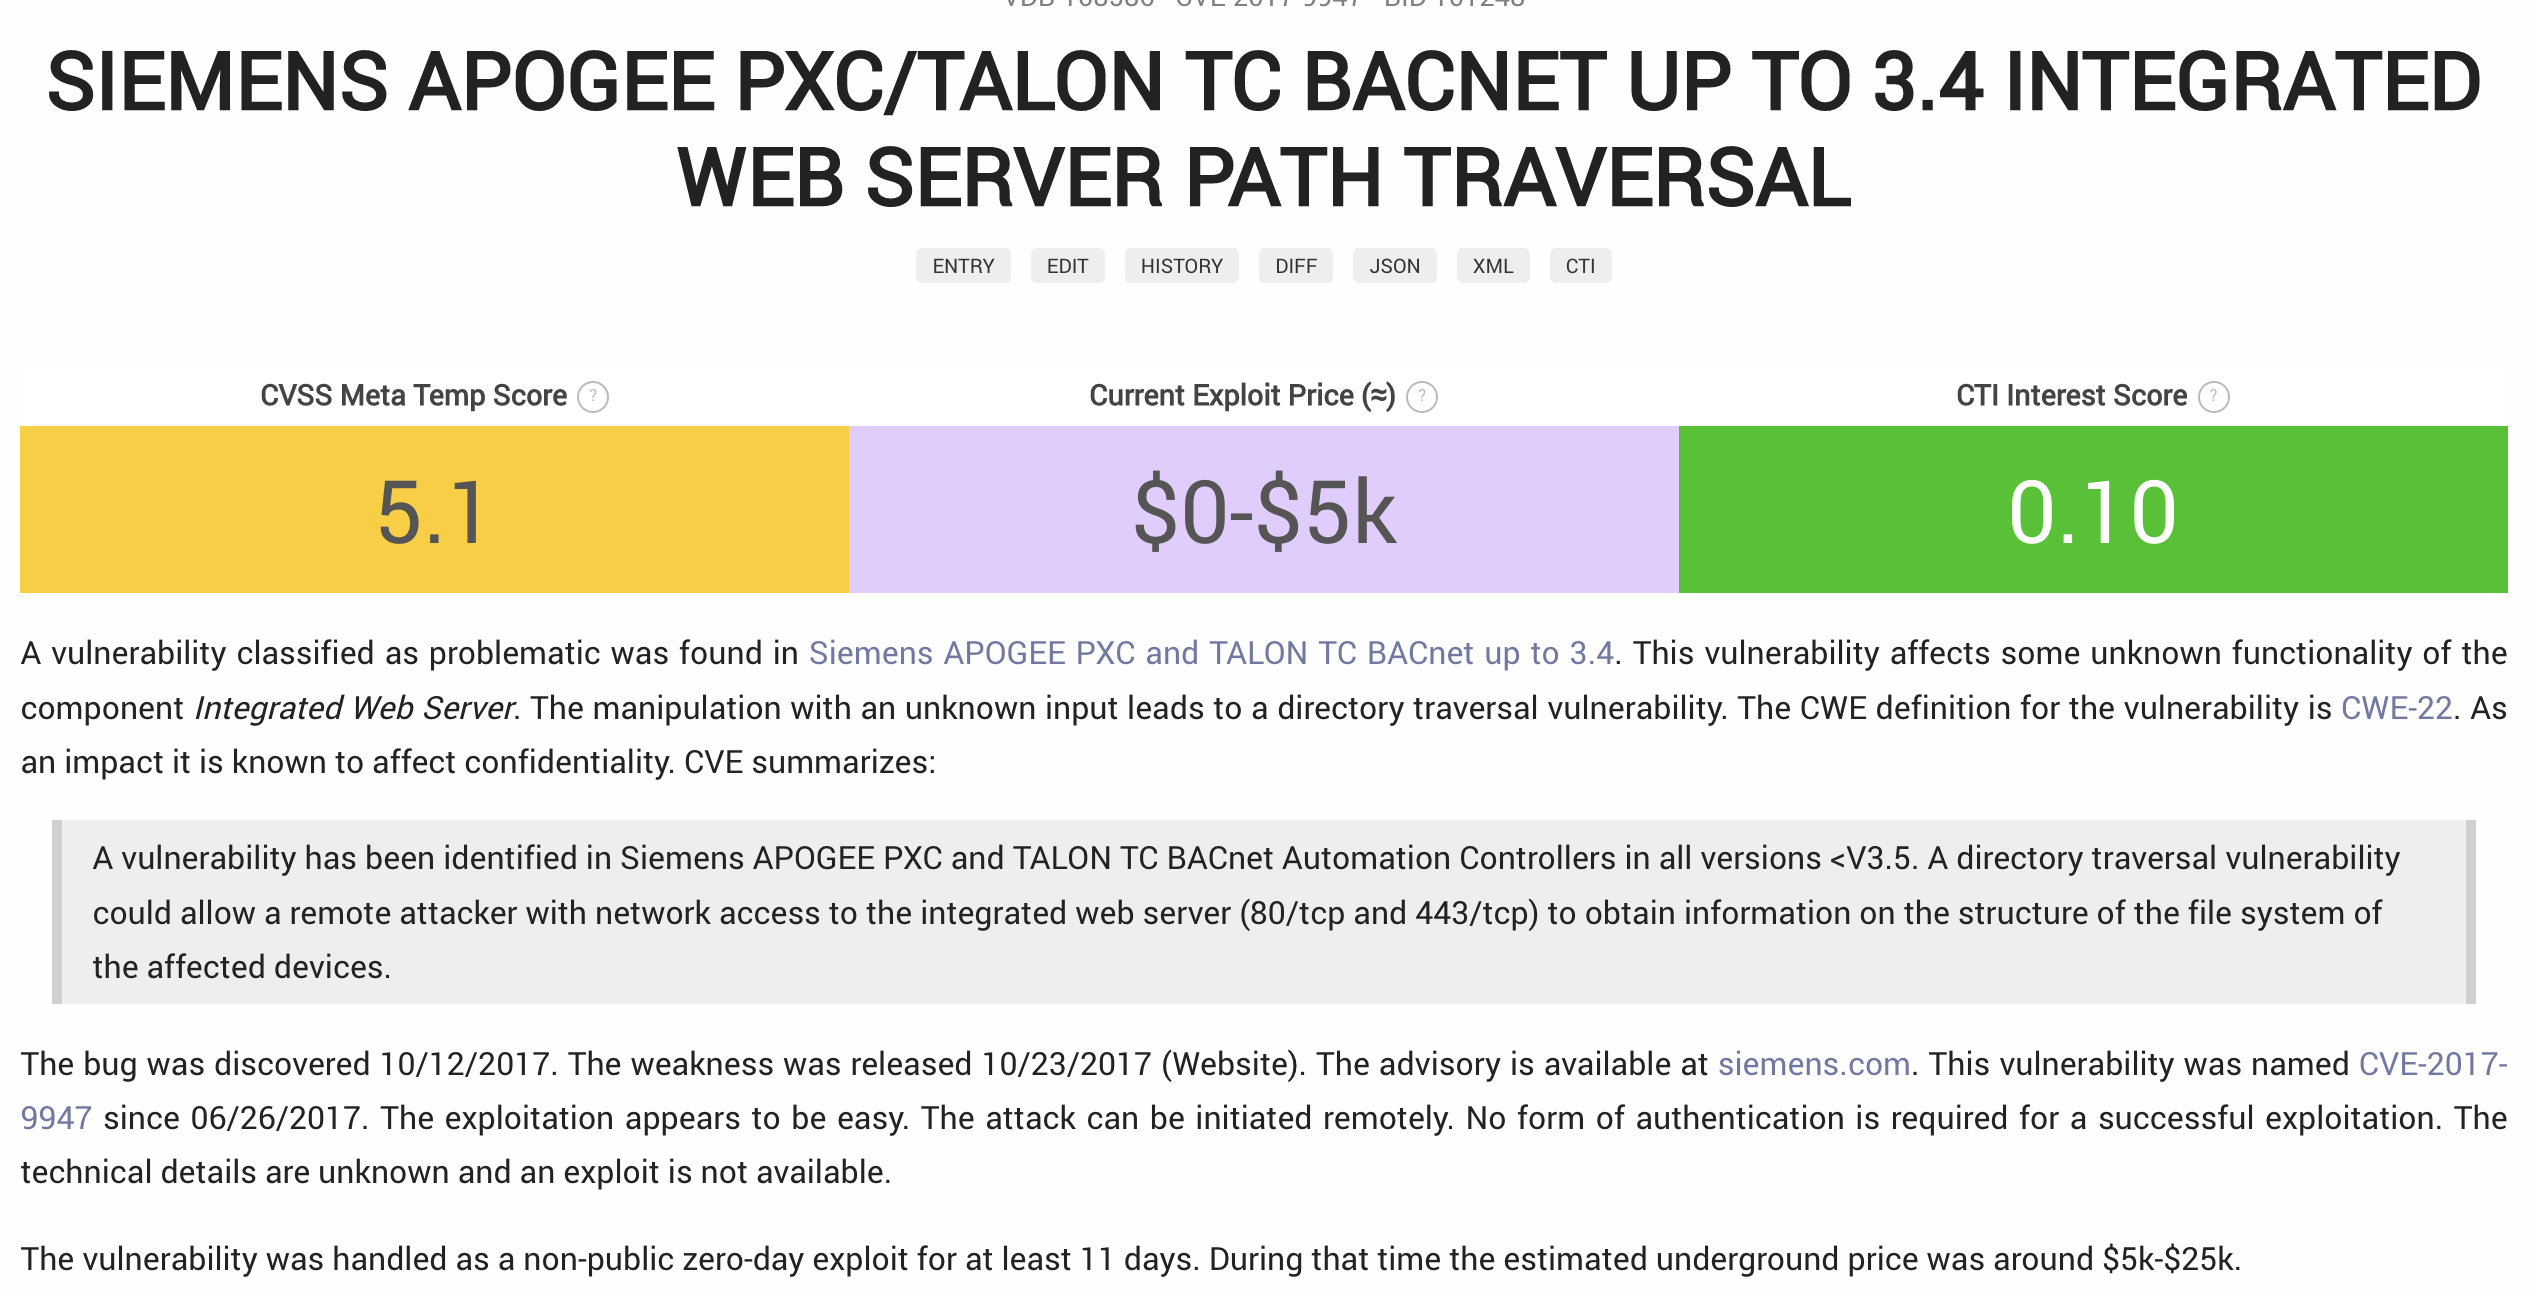 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 better-auth/better-auth
The most comprehensive authentication framework
 cossacklabs/themis
Easy to use cryptographic framework for data protection: secure messaging with forward secrecy and secure data storage. Has unified APIs across 14…
 flangvik/teamfiltration
Cross-platform framework for enumerating O365 accounts, password spraying, exfiltrating emails/Teams/OneDrive data, and backdooring EntraID accounts…
 jumpseclabs/tokenflare
Serverless AITM Simulation Framework for Entra ID and M365
 aahmad097/tritium
Kerberos-based password spraying framework for Active Directory with built-in lockout prevention, user enumeration integration, recursive password…
 aperocky/bepr
A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
 jakkxbt/cobraaudit
Bug-bounty audit scripts — API key validation, OAuth misconfig checks, password-reset auditing.
 envincion1991-cmyk/cve-2026-51954
Vulnerability Research