
LogHound
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
authenticationdigital-forensicsforensics+6
rnb-team/loghoundPost-Exploitation EVTX Analyzer for BloodHound Mapping
 commando-x/vuln-bank-mobile
A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…
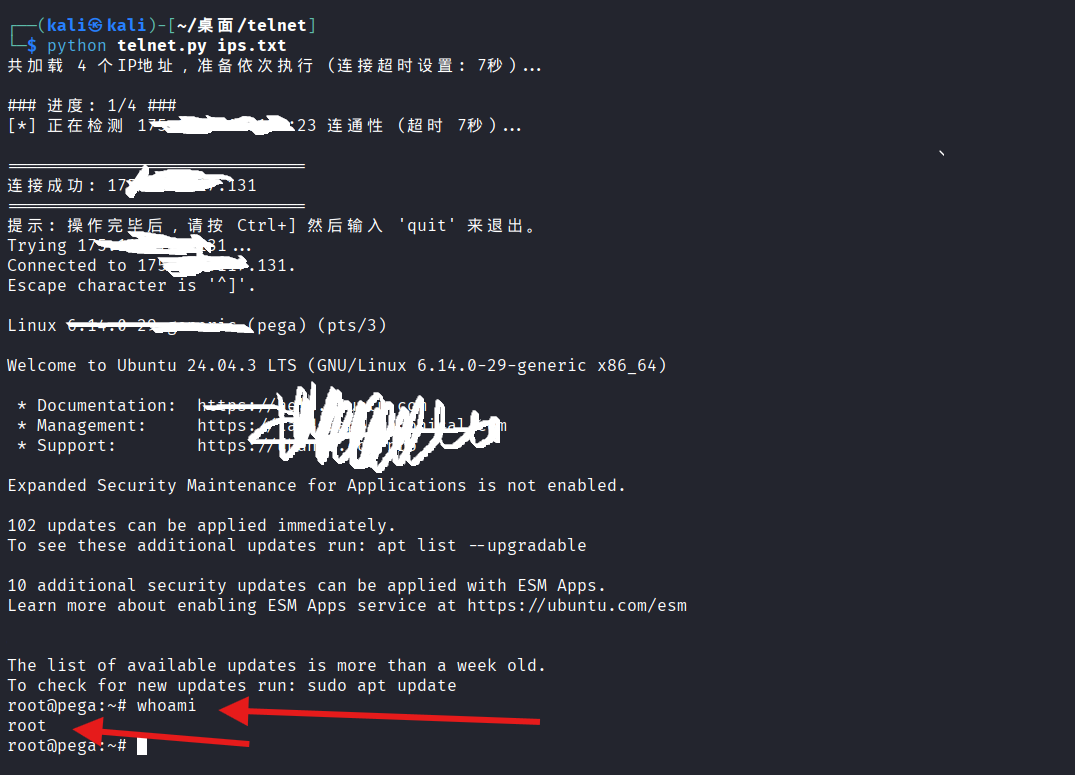 parameciumzhang/tell-me-root
Batch scanner for CVE-2026-24061 Telnet authentication bypass, with port liveness checks and automated payload attempts for authorized penetration…
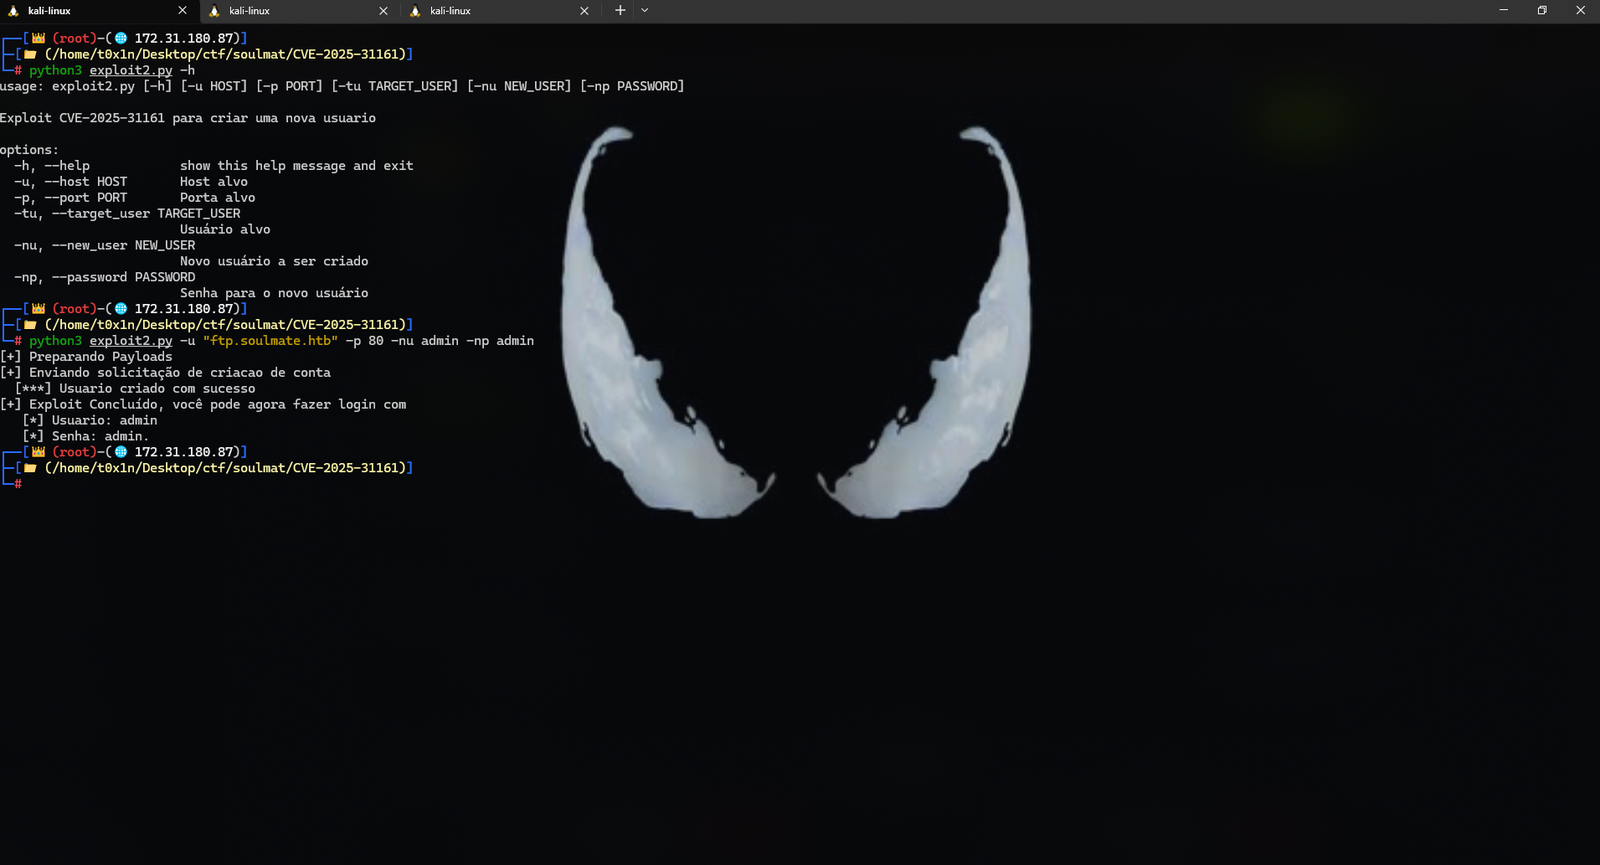 cesarbtakeda/cve-2025-31161
Exploit for CVE-2025-31161 with Python and C implementations, allowing authorized penetration testers to manipulate user accounts on target hosts.
 shoucheng3/apache__jspwiki_cve-2019-0225_2-11-0-m2
Exploit module for Apache JSPWiki CVE-2019-0225, enabling remote code execution via crafted requests. Designed for penetration testing and…
 redfox-security/digisol-dg-gr1321-s-password-policy-bypass-cve-2024-2257
Exploit for CVE-2024-2257: bypasses password policy on Digisol DG-GR1321 routers via crafted HTTP request, enabling unauthorized access for…
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 dirkjanm/mitm6
Exploits Windows IPv6 default configuration to spoof DNS via DHCPv6, redirecting victim traffic for credential relaying and man-in-the-middle attacks…
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
 syss-research/wirebug
WireBug is a toolset for Voice-over-IP penetration testing
 shac0x/wonka
Wonka is a sweet Windows tool that extracts Kerberos tickets from the Local Security Authority (LSA) cache. Like finding a ticket, but for security…
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
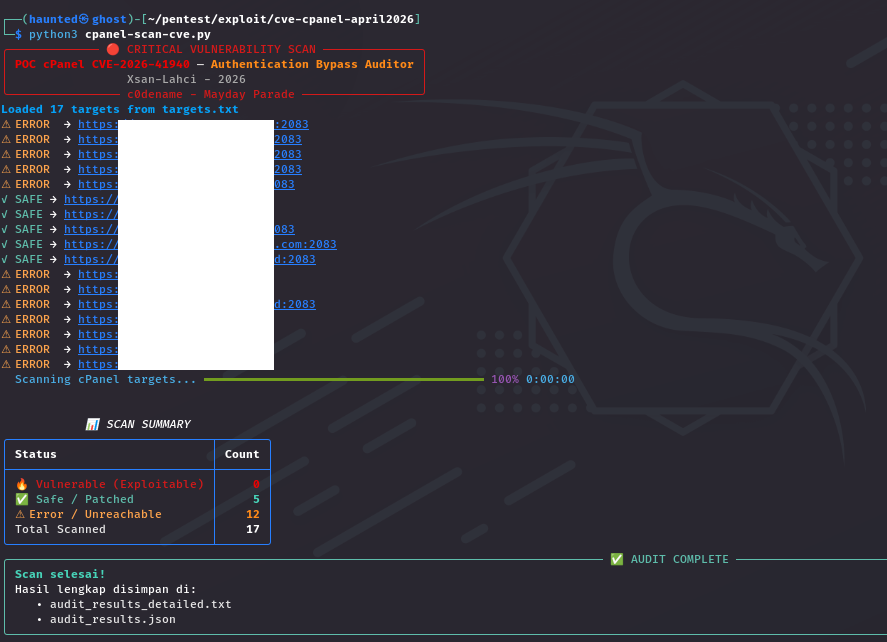 xsanflip/poc-cpanel-cve-2026-41940
Multi-threaded security auditing tool that detects CVE-2026-41940, an authentication bypass in cPanel/WHM, using CRLF injection and dynamic port…
 mostafasoliman/oracle-oam-padding-oracle-cve-2018-2879-exploit
Padding oracle exploit for Oracle Access Manager (CVE-2018-2879) enabling decryption of encrypted cookies and encryption of arbitrary plaintext for…
 zux0x3a/adfly
active directory query tool using LDAP Protocol , helps red teamer / penetration testers to validate users credentials , retrieve information about…
 e-m-e-k-a/moniker-link-lab-setup
Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…