
CVE-2026-48611-phpBB
 lxdwnpiper/cve-2026-48611-phpbb
Python proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
authenticationexploitationpassword-attacks+4
lxdwnpiper/cve-2026-48611-phpbbPython proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
 inflightsec/agent-vault-proxy
Just-in-time API keys for AI agents - and any other process you route through it: the caller only ever sees a placeholder.
 jfjallid/go-secdump
Tool to remotely dump secrets from the Windows registry
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 eliangonzi00/pockeycloakcve-2023-0264
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…
 foxboron/ssh-tpm-agent
SSH agent that creates and manages TPM-sealed keys for hardware-bound authentication, supporting key generation, import, wrapping, PIN protection,…
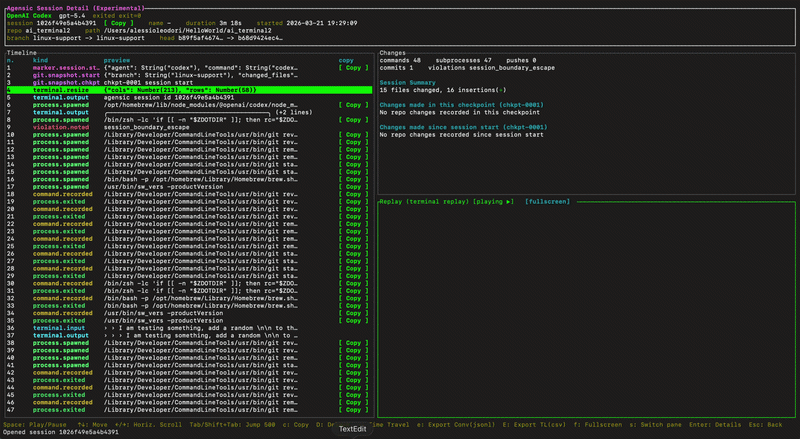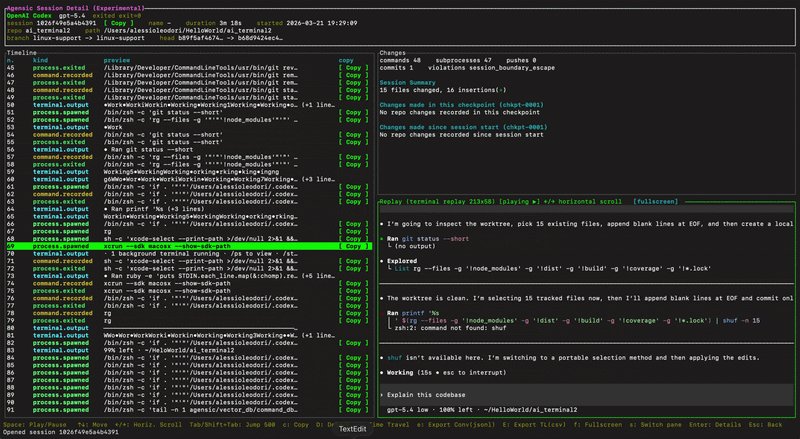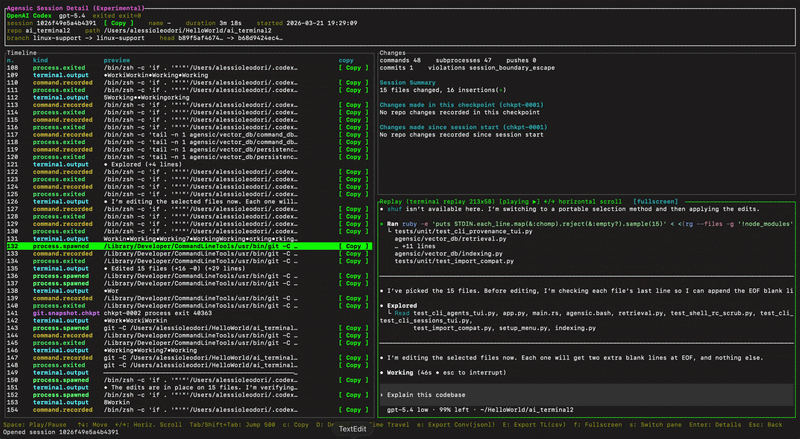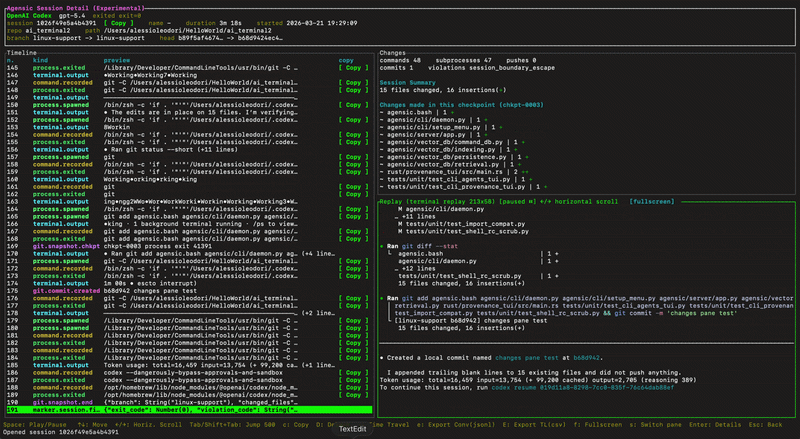 alex188dot/agensic
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…
 plunder707/attestos
Bazzite plus a TPM boot attestation layer. Work in progress: builds unverified, UKI mechanism unresolved. Spec: github.com/plunder707/attested-gaming
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
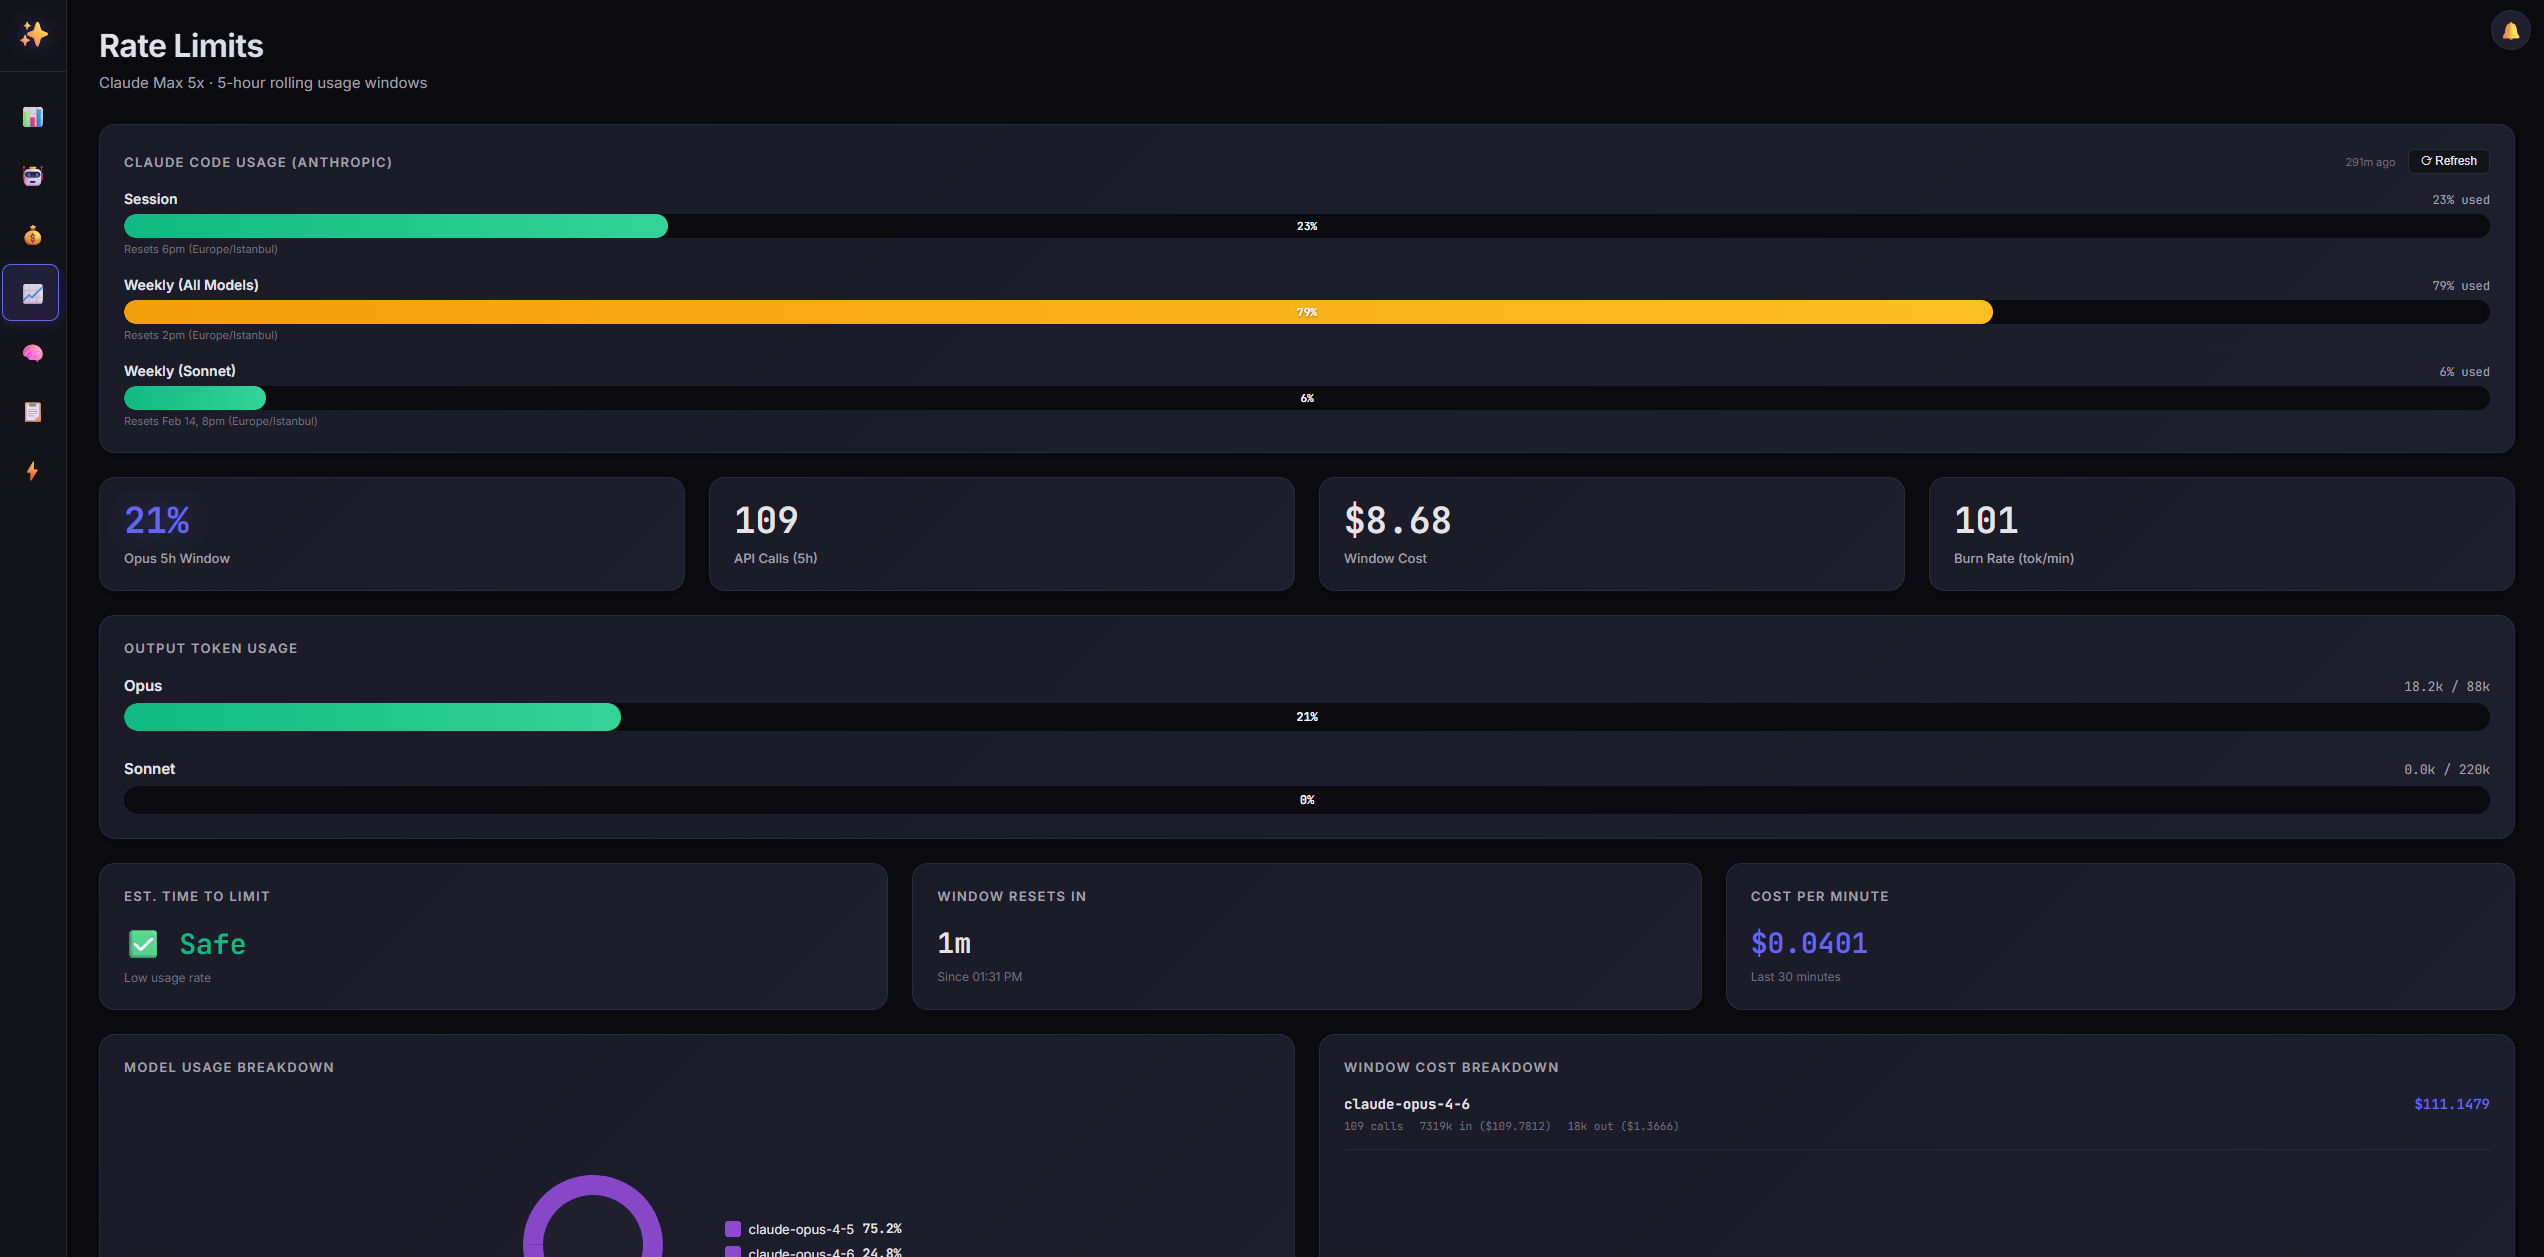 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
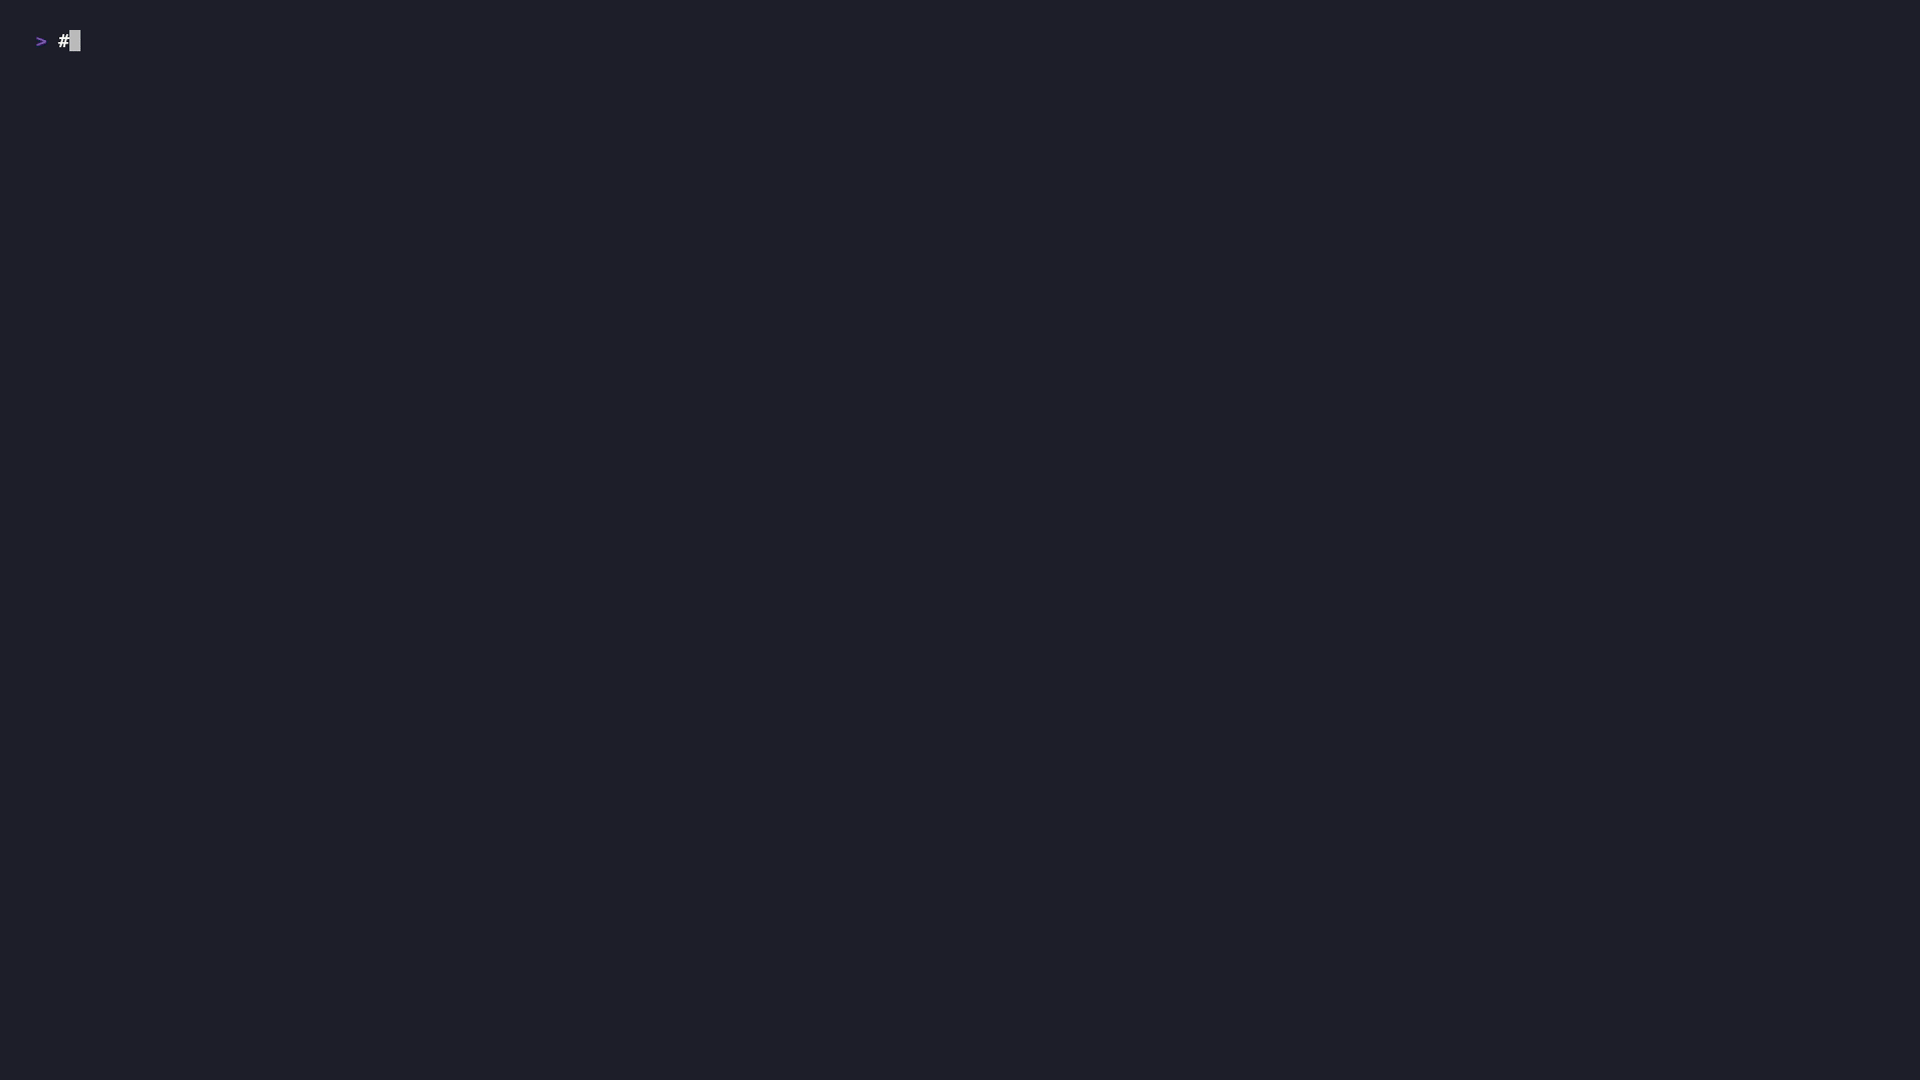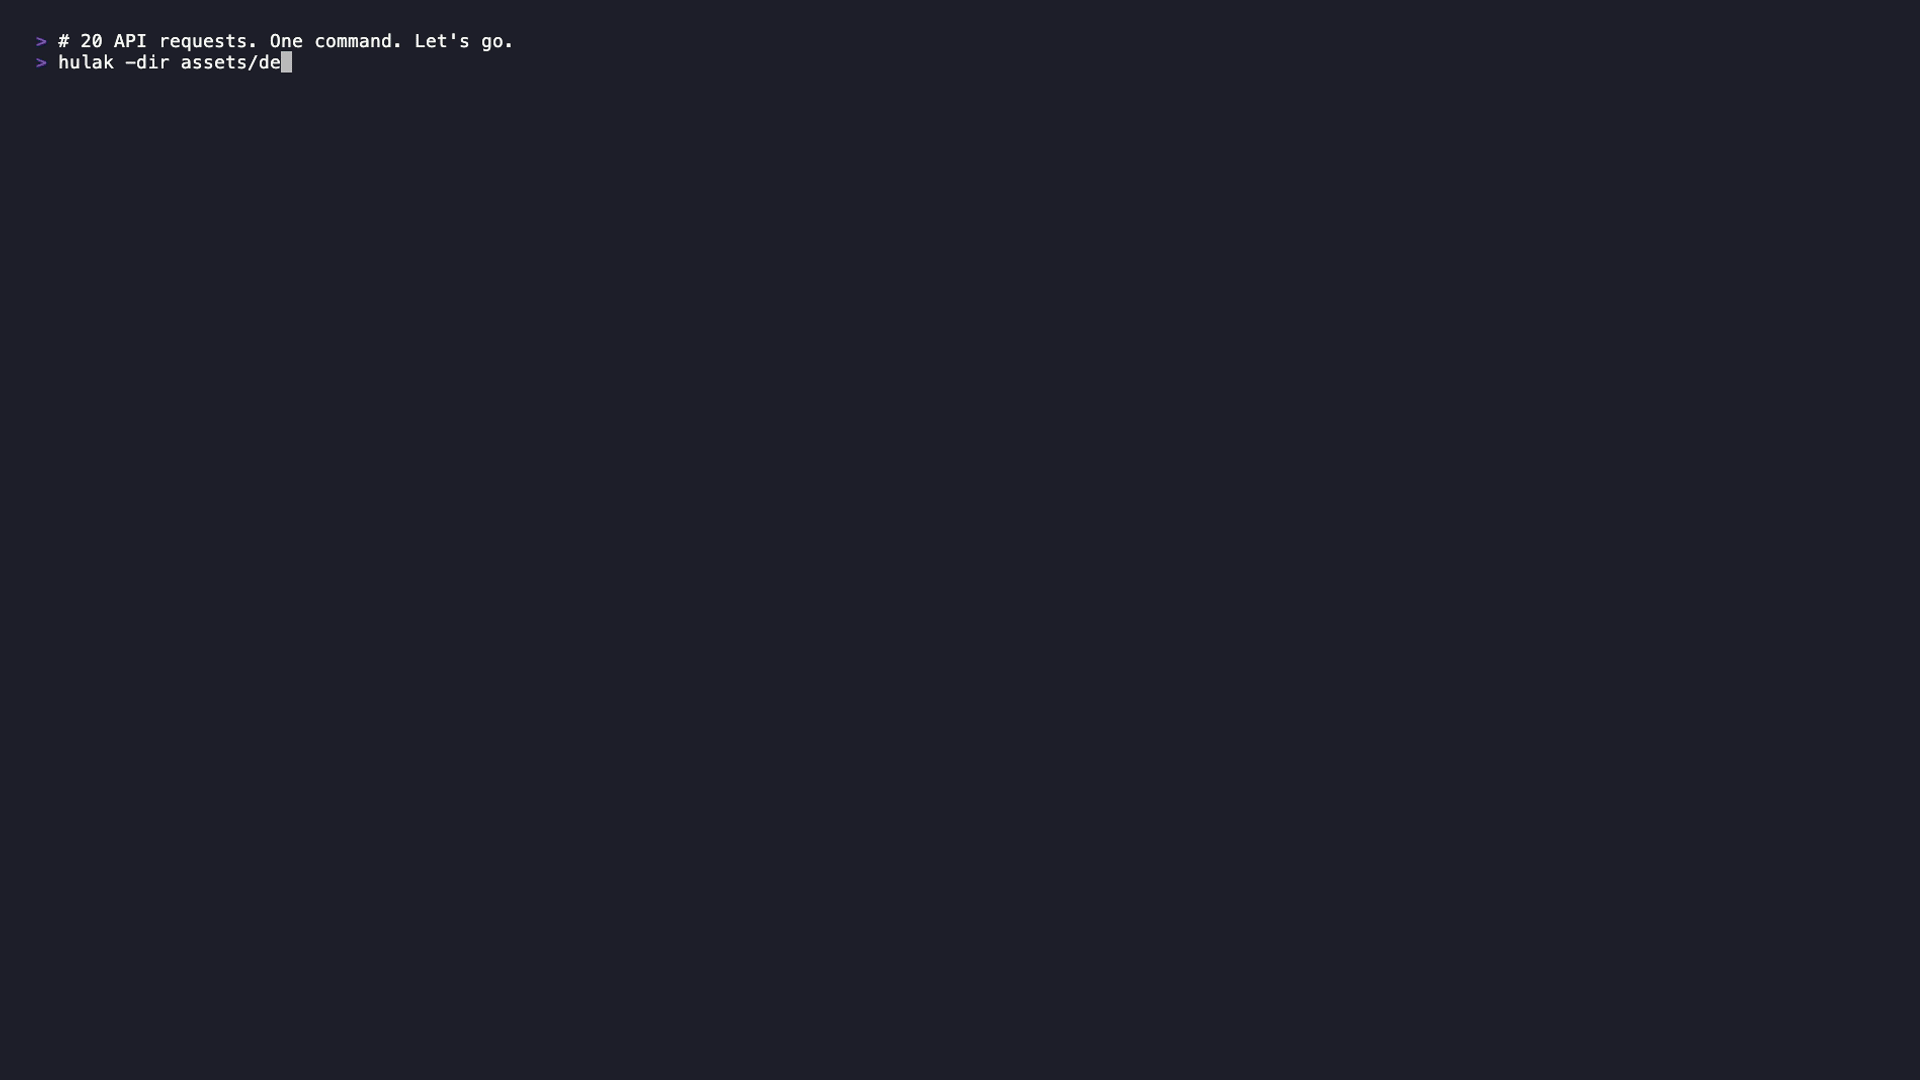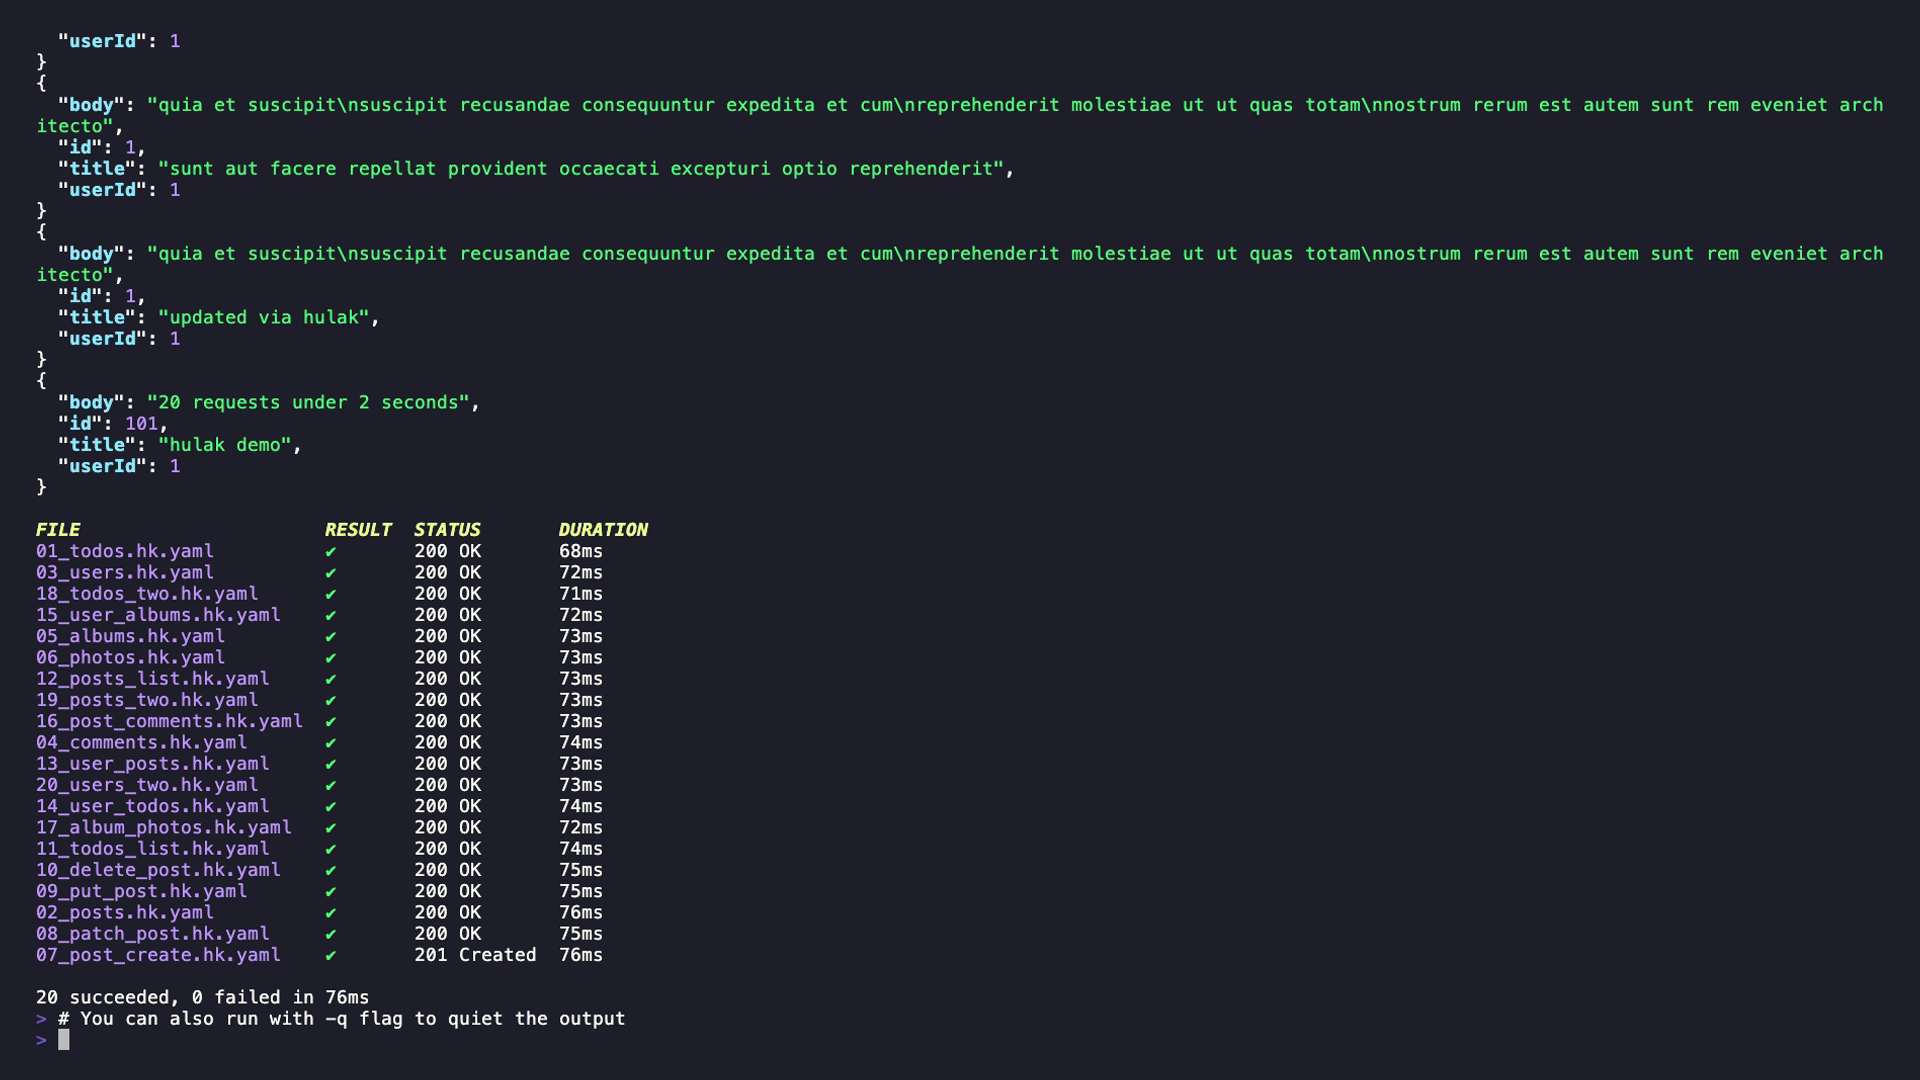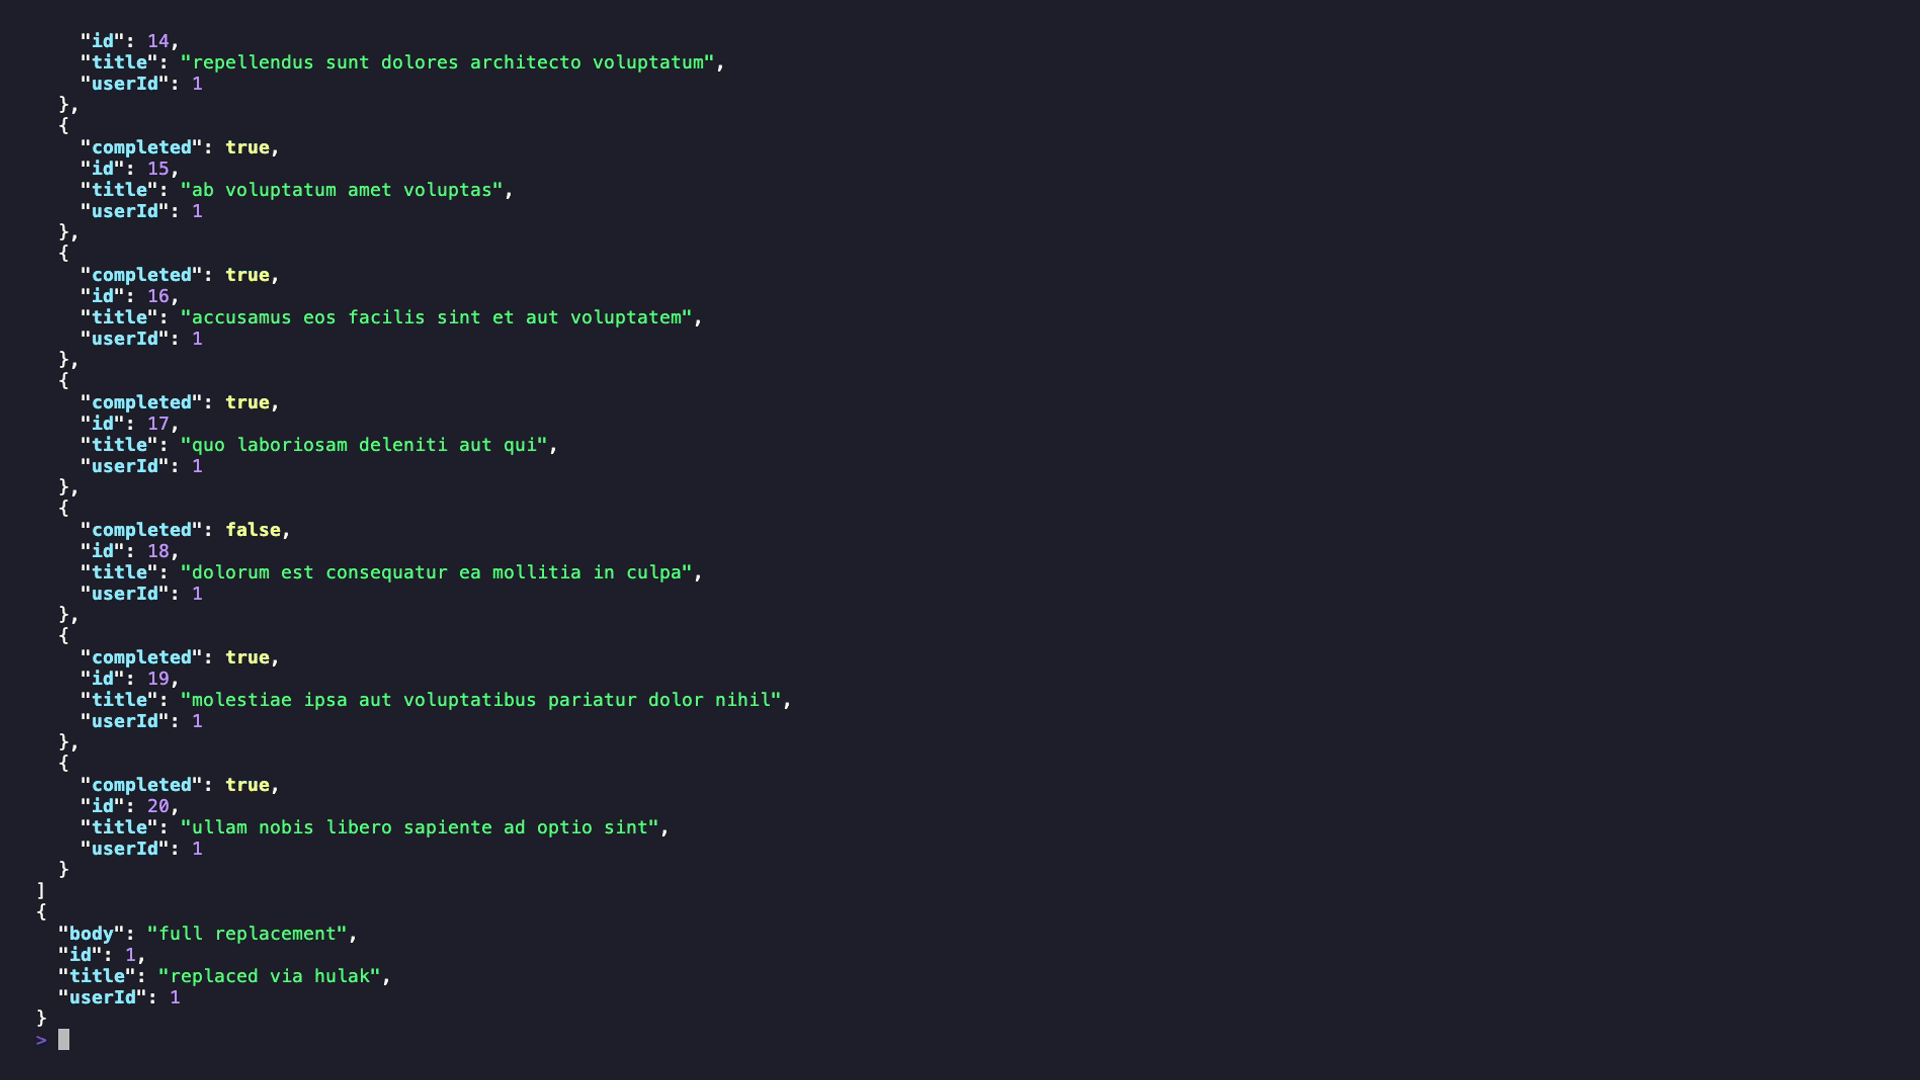 xaaha/hulak
A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.
 renich/genclave
Centralized, TPM 2.0 hardware-backed cryptographic identity enclave and multi-protocol bridge for Linux (FIDO2/CTAP2 WebAuthn Passkeys, OpenSSH…
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 cosignet/sdk
Thin TypeScript + zero-dep Python client and recipes to gate high-risk actions behind a payload-bound passkey approval.
 mondaycom/hatcha
CAPTCHA proves you're human. HATCHA proves you're not.
 obrunolima1910/cve-2026-24061
🚨 Exploit CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd, for instant root shell access without authentication.
 ricterz/cve-2021-3560-authentication-agent
PolicyKit CVE-2021-3560 Exploit (Authentication Agent)