
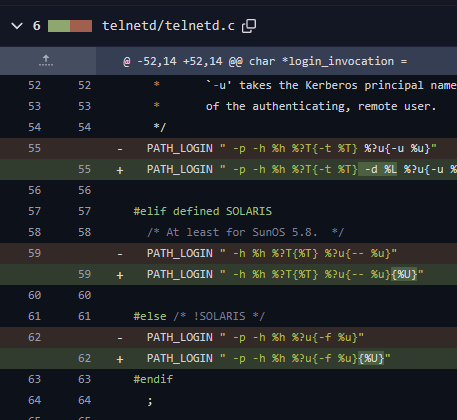
CVE-2026-24061
 lucaspdiniz/cve-2026-24061
Vulnerability in GNU InetUtils telnetd Enables Remote Root Access
authenticationexploitationpenetration-testing+2
lucaspdiniz/cve-2026-24061Vulnerability in GNU InetUtils telnetd Enables Remote Root Access
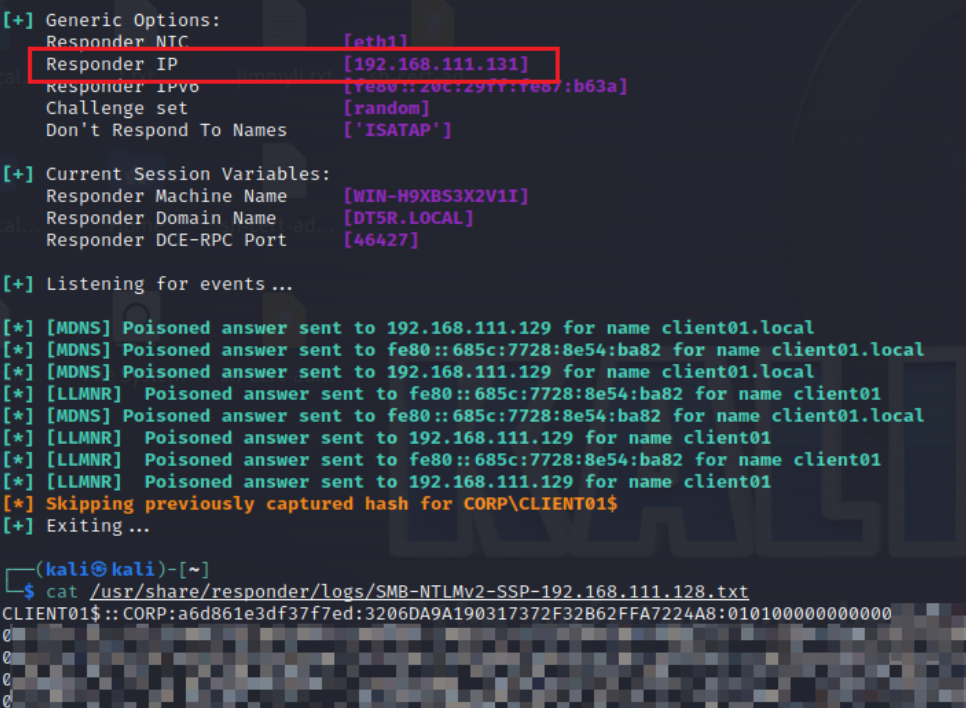 hagrid29/cve-2024-40586-windows-coerced-authentication-in-forticlient
Exploit for CVE-2024-40586: coerces Windows hosts to authenticate via a vulnerable FortiClient named pipe, enabling privilege escalation to SYSTEM or…
 saykino/cve-2025-56224
Documents an OTP verification bypass vulnerability in Ascertia SigningHub, allowing attackers to brute-force OTP codes and impersonate mobile…
 randomrobbiebf/cve-2023-36531
LiquidPoll – Advanced Polls for Creators and Brands <= 3.3.68 - Missing Authorization via activate_addon
 fabdotnet/cve-2023-27100
Exploit for CVE-2023-27100 bypassing pfSense anti-brute force protection via crafted X-Forwarded-For headers and anti-CSRF tokens to evade sshguard…
 giovannidispoto/cve-2017-13872-patch
Exploit for CVE-2017-13872 that escalates privileges by changing the root password on vulnerable systems. Requires execution and provides new root…
 boltgolt/howdy
🛡️ Windows Hello™ style facial authentication for Linux
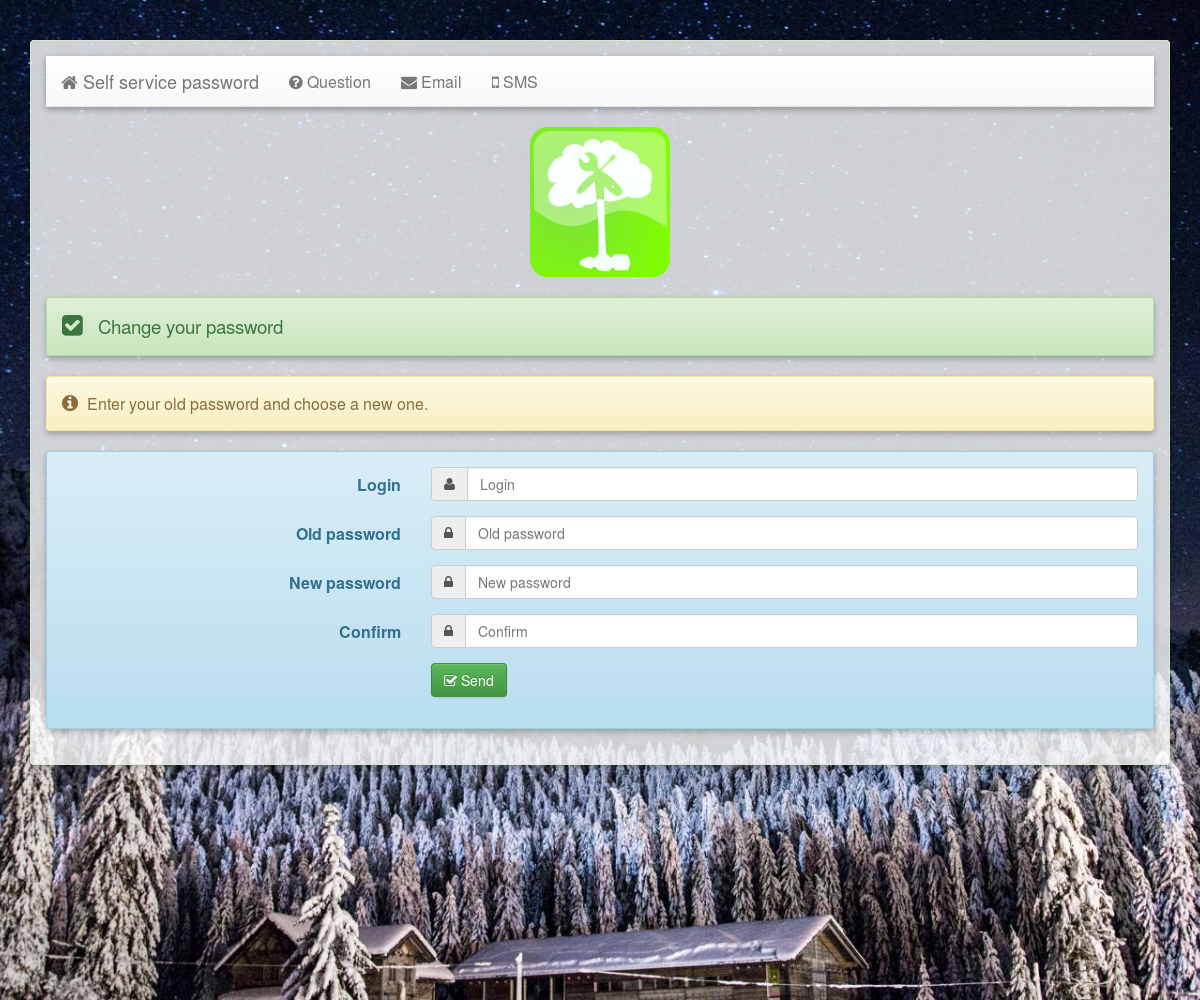 ltb-project/self-service-password
Web interface to change and reset password in an LDAP directory
 kevin-robertson/powermad
PowerShell MachineAccountQuota and DNS exploit tools
 yubico/libfido2
Provides library functionality for FIDO2, including communication with a device over USB or NFC.
 ustayready/credking
Password spraying using AWS Lambda for IP rotation
 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens
 ricardojoserf/adduser-samr
Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)
 praetorian-inc/oauthseeker
A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.
 synacktiv/captaincredz
CaptainCredz is a modular and discreet password-spraying tool.
 ccob/pivert
Emulates NIST SP 800-73 PIV smart cards on Windows using a PFX certificate and private key, enabling smart-card authentication for RDP, Citrix, and…
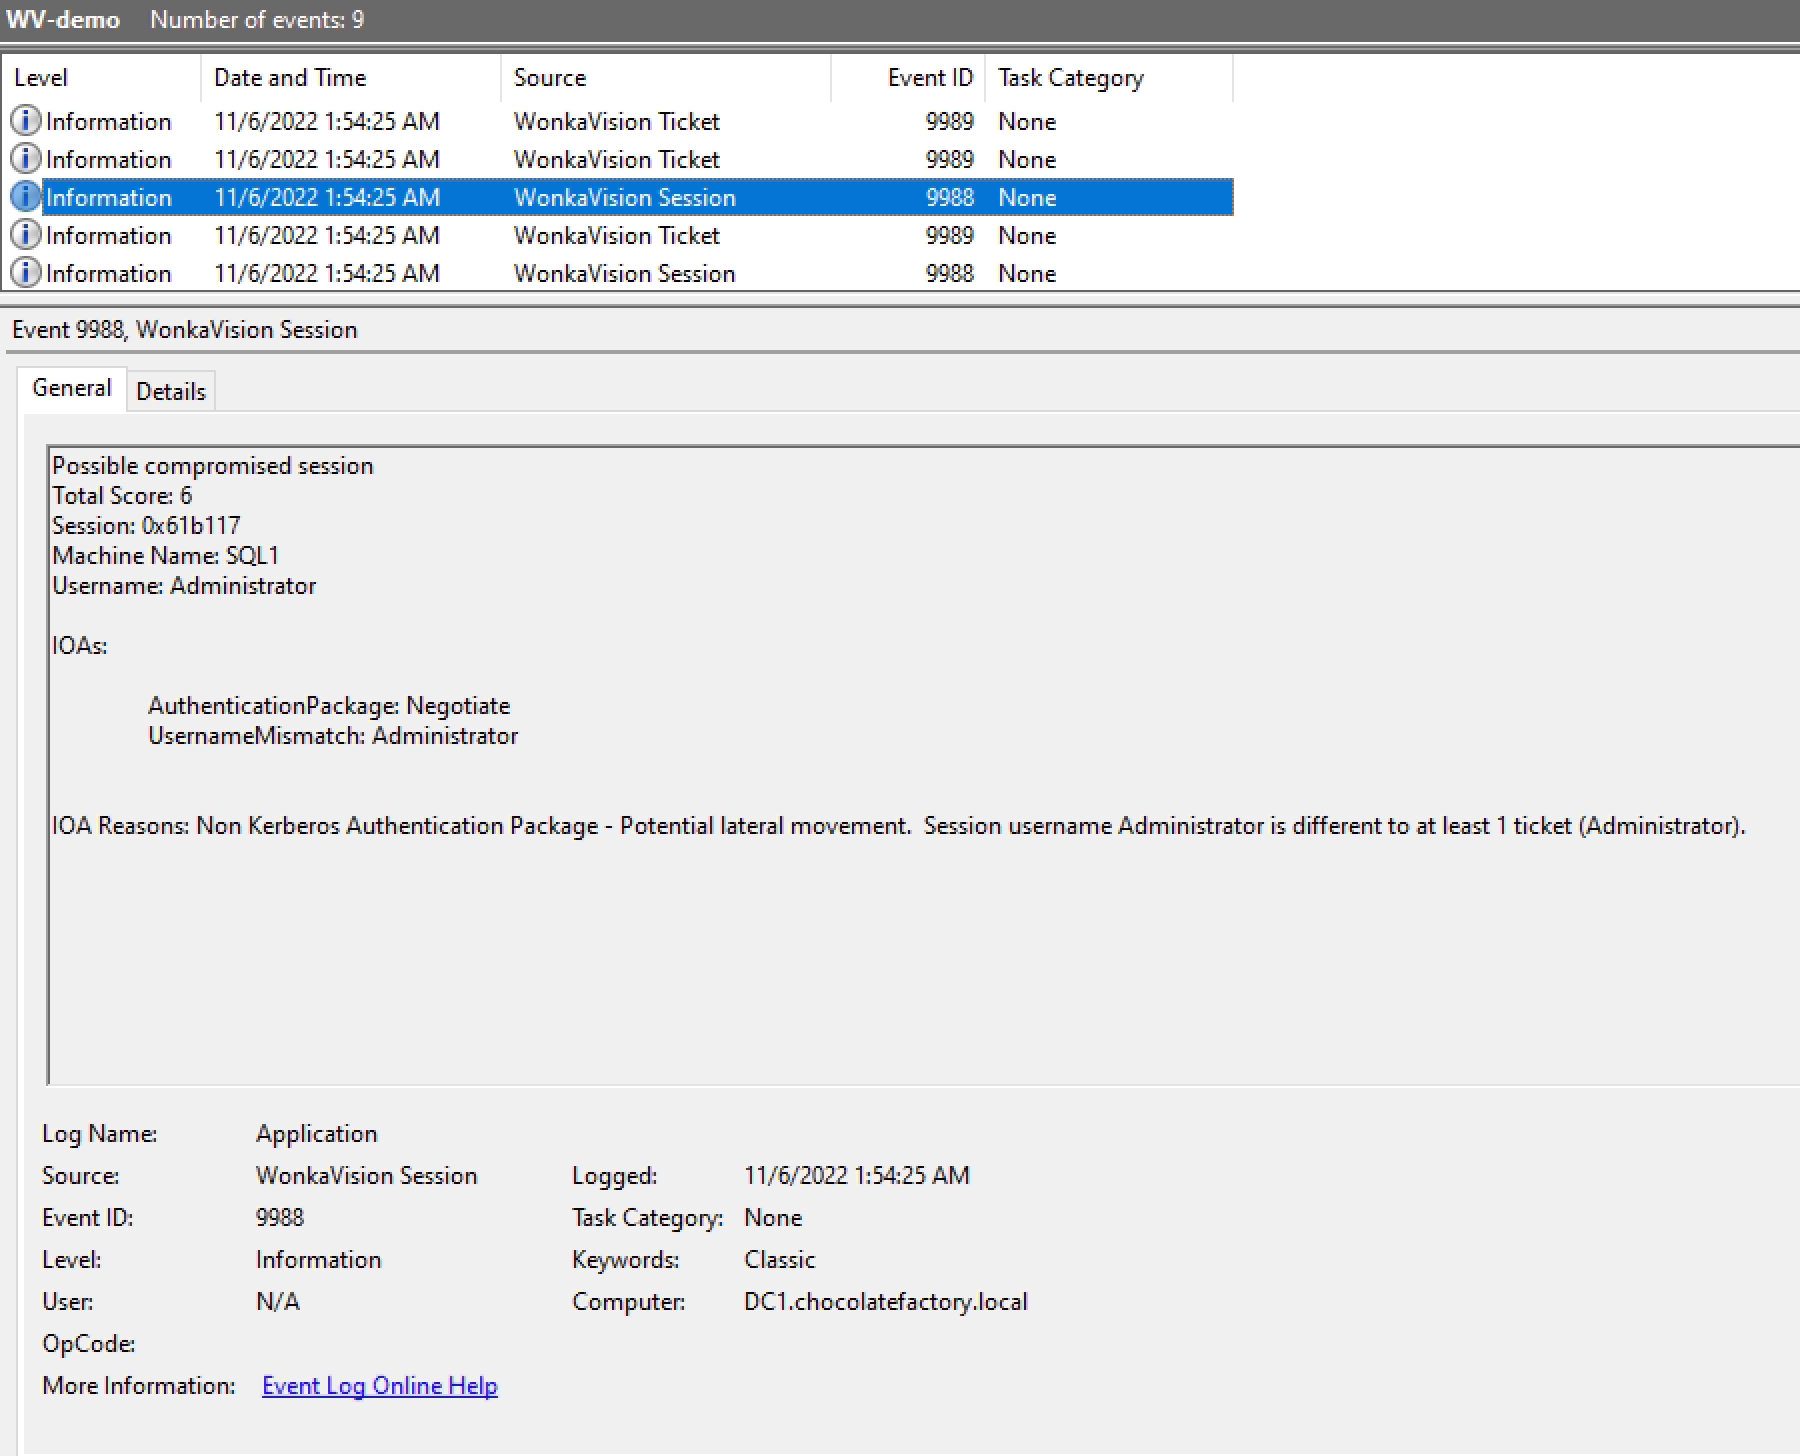 0xe7/wonkavision
Detects forged Kerberos tickets by dumping session and ticket data, scoring anomalies, and generating Windows event-log indicators for SIEM-based…