
CVE-2023-23752
 pushkarup/cve-2023-23752
Exploit for CVE-2023-23752 (4.0.0 <= Joomla <= 4.2.7).
authenticationexploitationinformation-gathering+3
1
pushkarup/cve-2023-23752Exploit for CVE-2023-23752 (4.0.0 <= Joomla <= 4.2.7).
 adityathebe/poc-cve-2018-0114
POC for CVE-2018-0114 written in Go
 cyberharsh/oracle-mysql-cve-2012-2122
Docker-based exploit environment for CVE-2012-2122 MySQL/MariaDB authentication bypass vulnerability. Demonstrates password comparison flaw allowing…
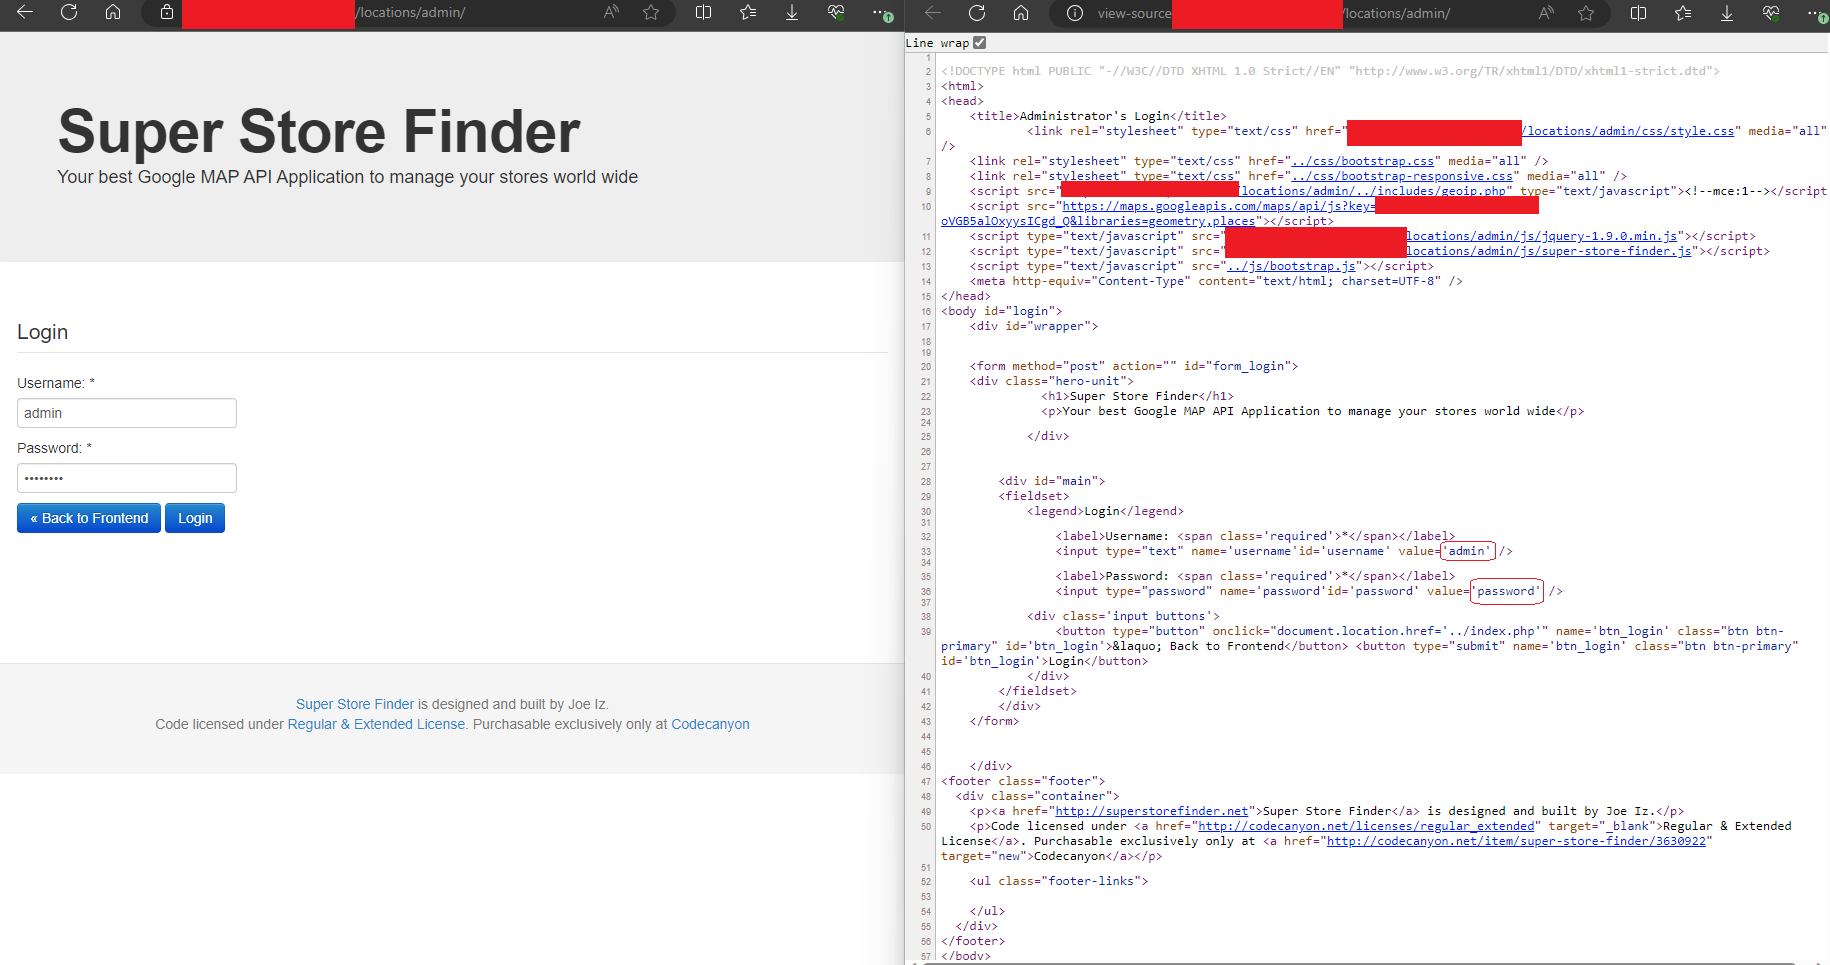 redblueteam/cve-2023-41508
CVE-2023-41508 - A hard-coded password in Super Store Finder v3.6 allows attackers to access the administration panel.
 sancliffe/cve-2026-29145-tester
This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.
 0xbs0d27/cve-2025-56643
Public reference for CVE-2025-56643 – Wiki.js 2.5.307 JWT Session Vulnerability
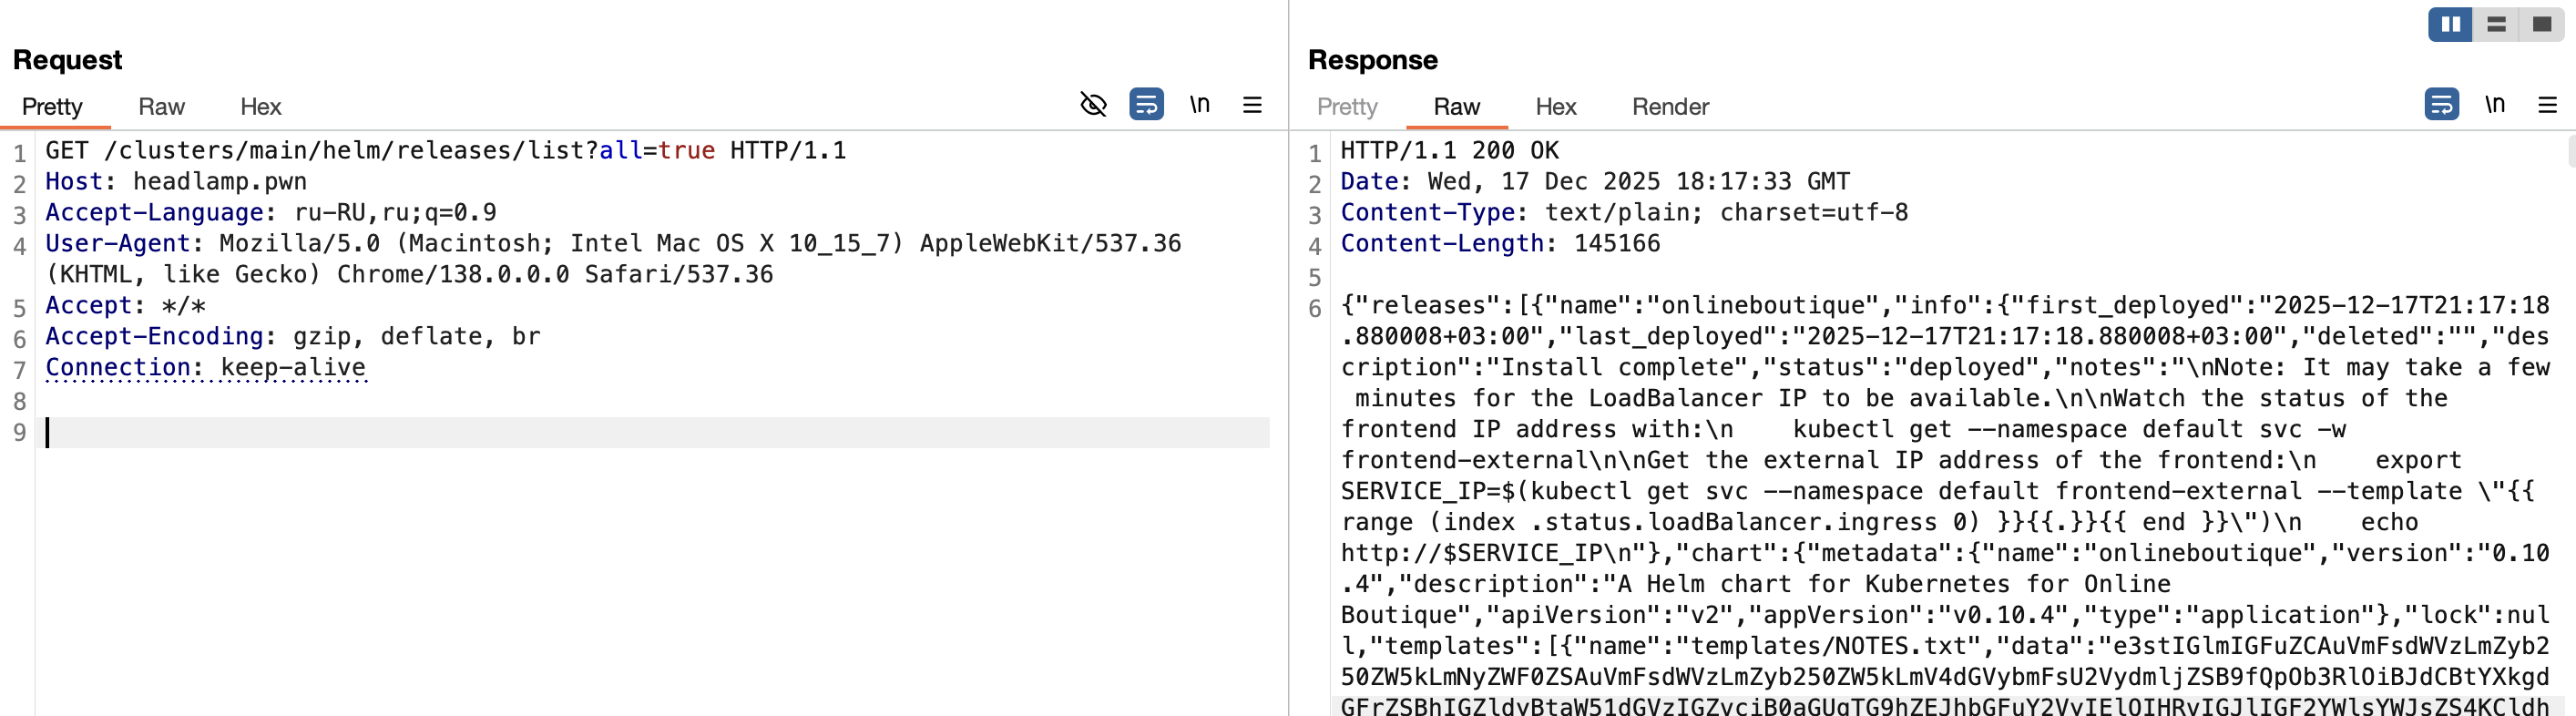 r0binak/cve-2025-14269
CVE-2025-14269 PoC exploit

 alexoslabs/ipmitest
Shell script for testing the IPMI cipher type zero authentication bypass vulnerability (CVE-2013-4784)
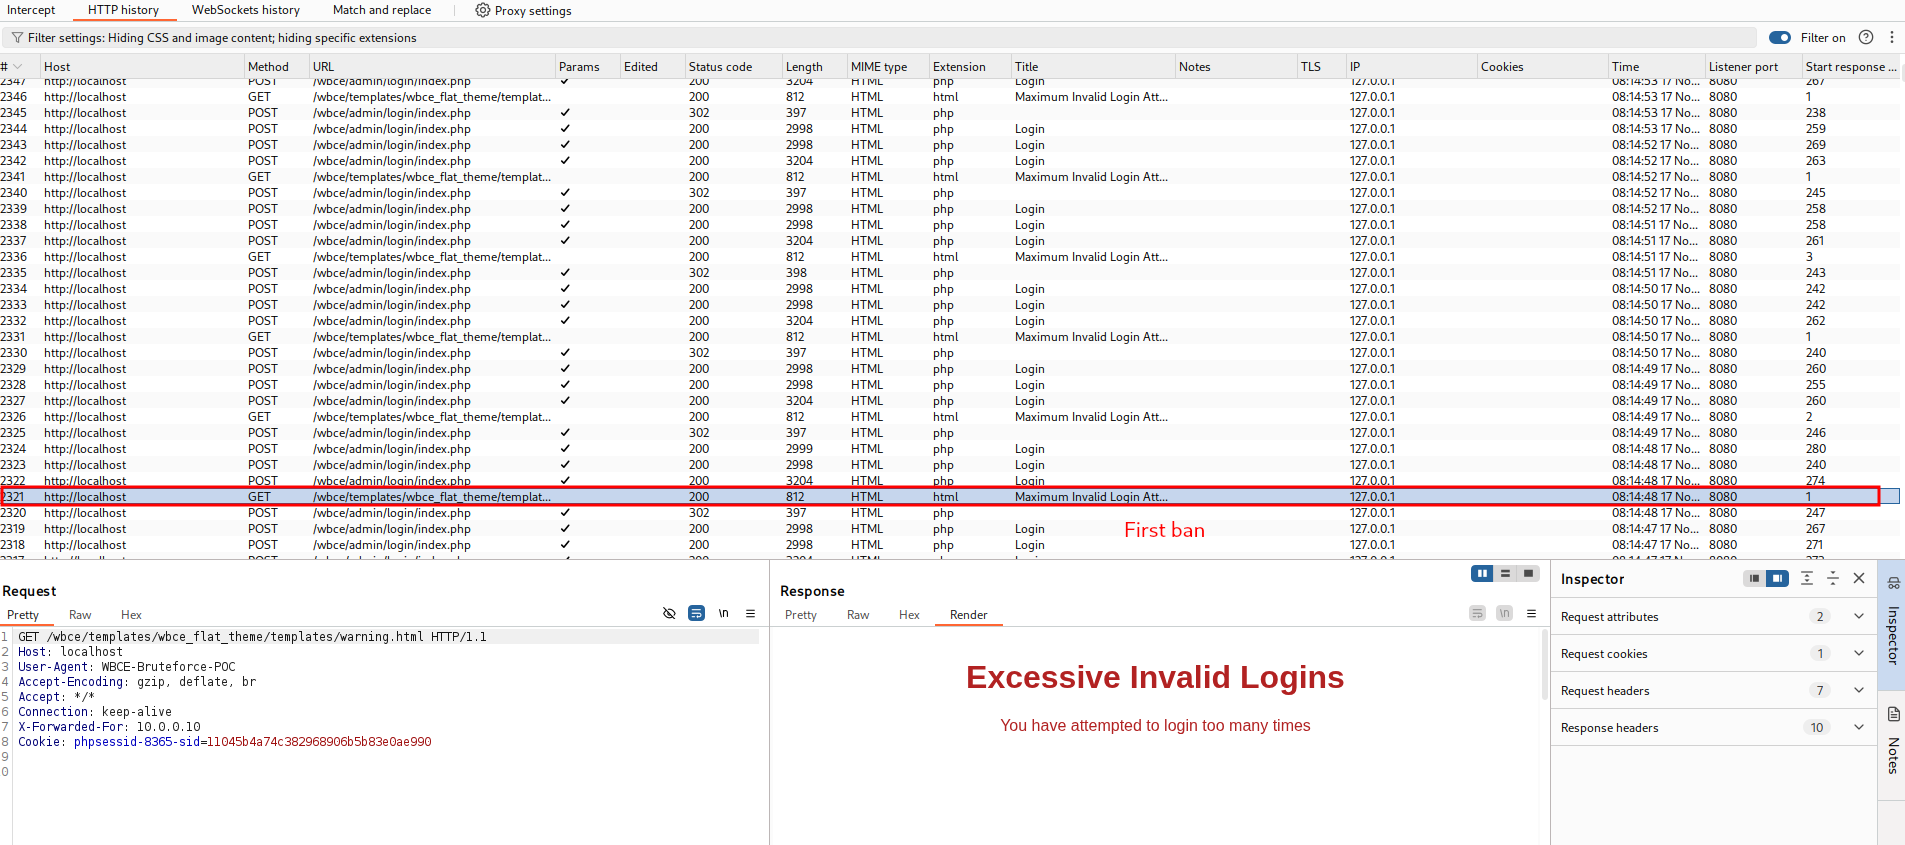 lukasz-rybak/cve-2025-66204
Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…
 skraft9/cve-2025-44823
Authenticated API Key Exposure in Nagios Log Server 2024R1.3.1
 hagrid29/cve-2024-40586-windows-coerced-authentication-in-forticlient
Exploit for CVE-2024-40586: coerces Windows hosts to authenticate via a vulnerable FortiClient named pipe, enabling privilege escalation to SYSTEM or…
 nxvh1337/cve-2025-15602-poc
Snipe-IT < 8.3.7 Mass Assignment Vulnerability Leading to Privilege Escalation
 realbatuhan/jwt-bruteforcer
Jwt Bruteforcer with CVE-2018-1000531 Test
 nrtlox/cve-2025-63587
CVE-2025-63587
 zgsnj123/cve-2025-45466
It is the details of CVE-2025-45466