
CVE-2025-11171
 snailsploit/cve-2025-11171
CVE-2025-11171
authenticationeducationexploitation+3
16 months ago
snailsploit/cve-2025-11171CVE-2025-11171
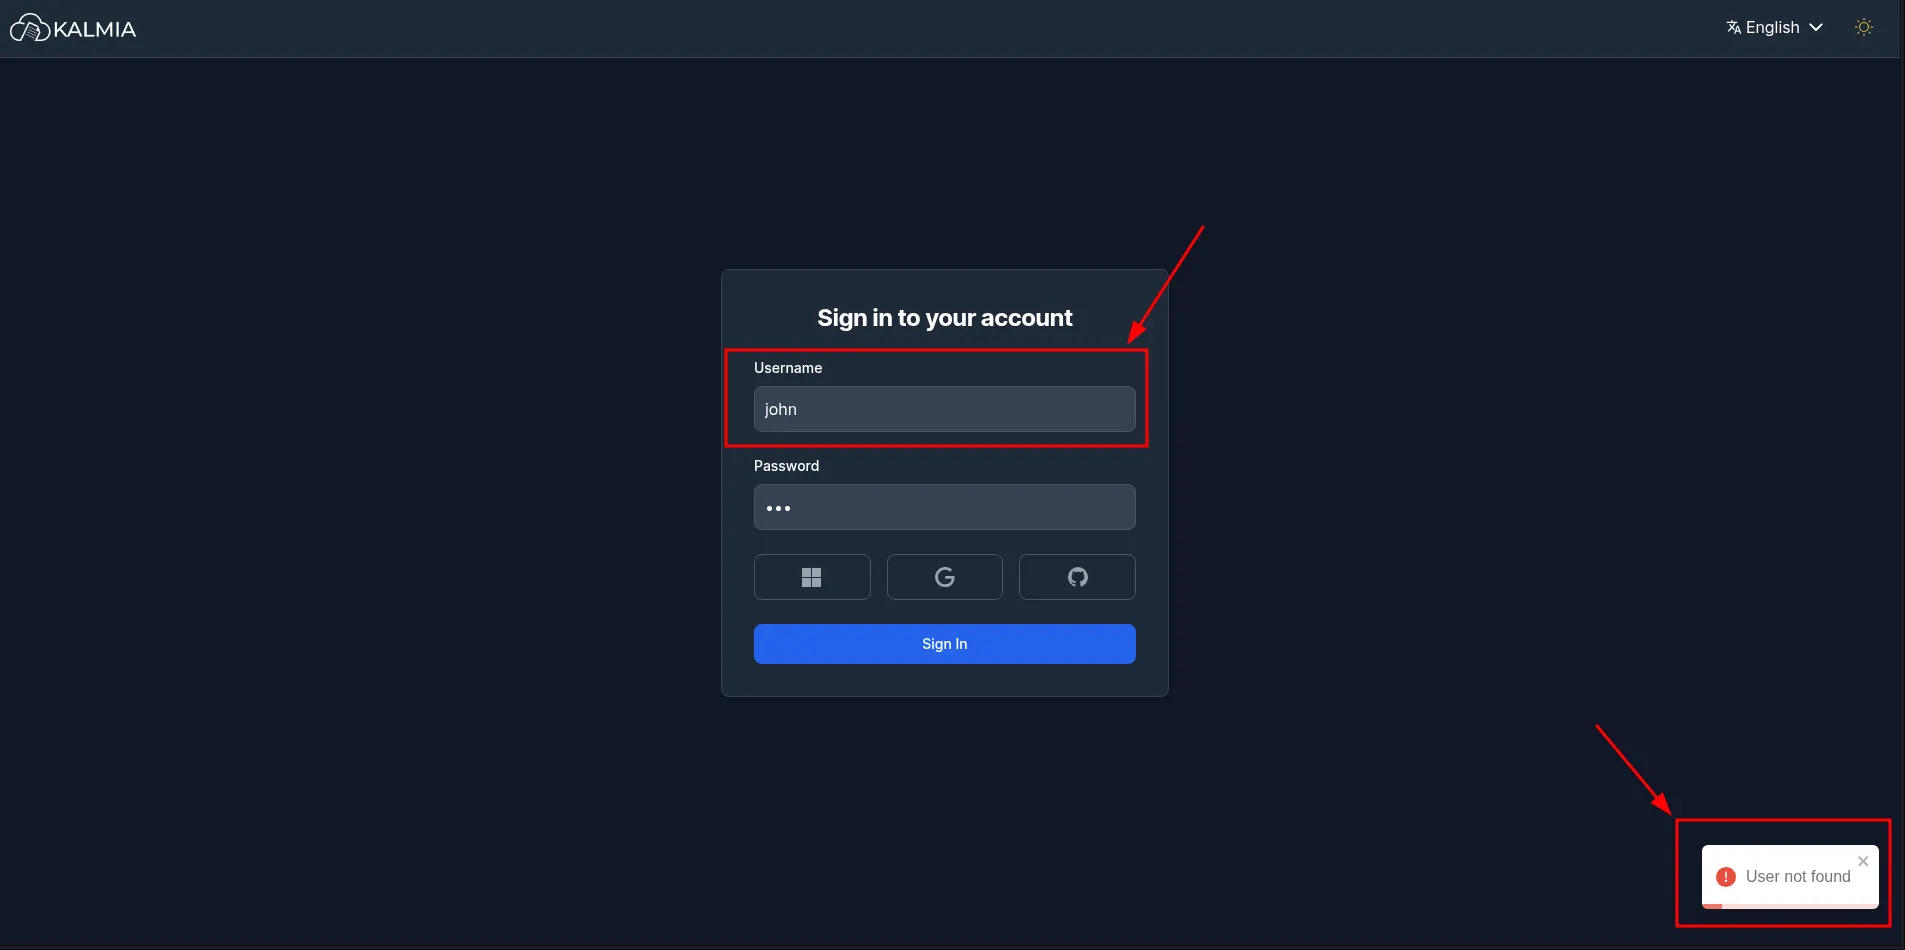 noxurge/cve-2025-65899
DifuseHQ Kalmia CMS version 0.2.0 is vulnerable to user enumeration through distinguishable error responses in the /kal-api/auth/jwt/create…
 xtremebeing/starlette-host-header-lab
Starlette Host-Header URL Confusion Lab (X41-2026-002) - CVE-2026-48710
 curtishoughton/cve-2025-20362-cisco-scanner
Safe Python scanner for CVE-2025-20362 (Cisco ASA/FTD WebVPN Authentication Bypass)
 ish3ng0m4/cve-2026-24061-telnetd
CVE-2026-24061 GNU Inetutils Telnetd Authentication Bypass
 elevenpaths/latch-plugin-openvpn-as
Latch plugin for OpenVPN Access Server enabling two-factor authentication (2FA) to secure VPN connections with time-based one-time passwords (TOTP).
 1872892142/jboss-autopwn-1
JBoss Autopwn as featured at BlackHat Europe 2010 - this version incorporates CVE-2010-0738 the JBoss authentication bypass VERB manipulation…
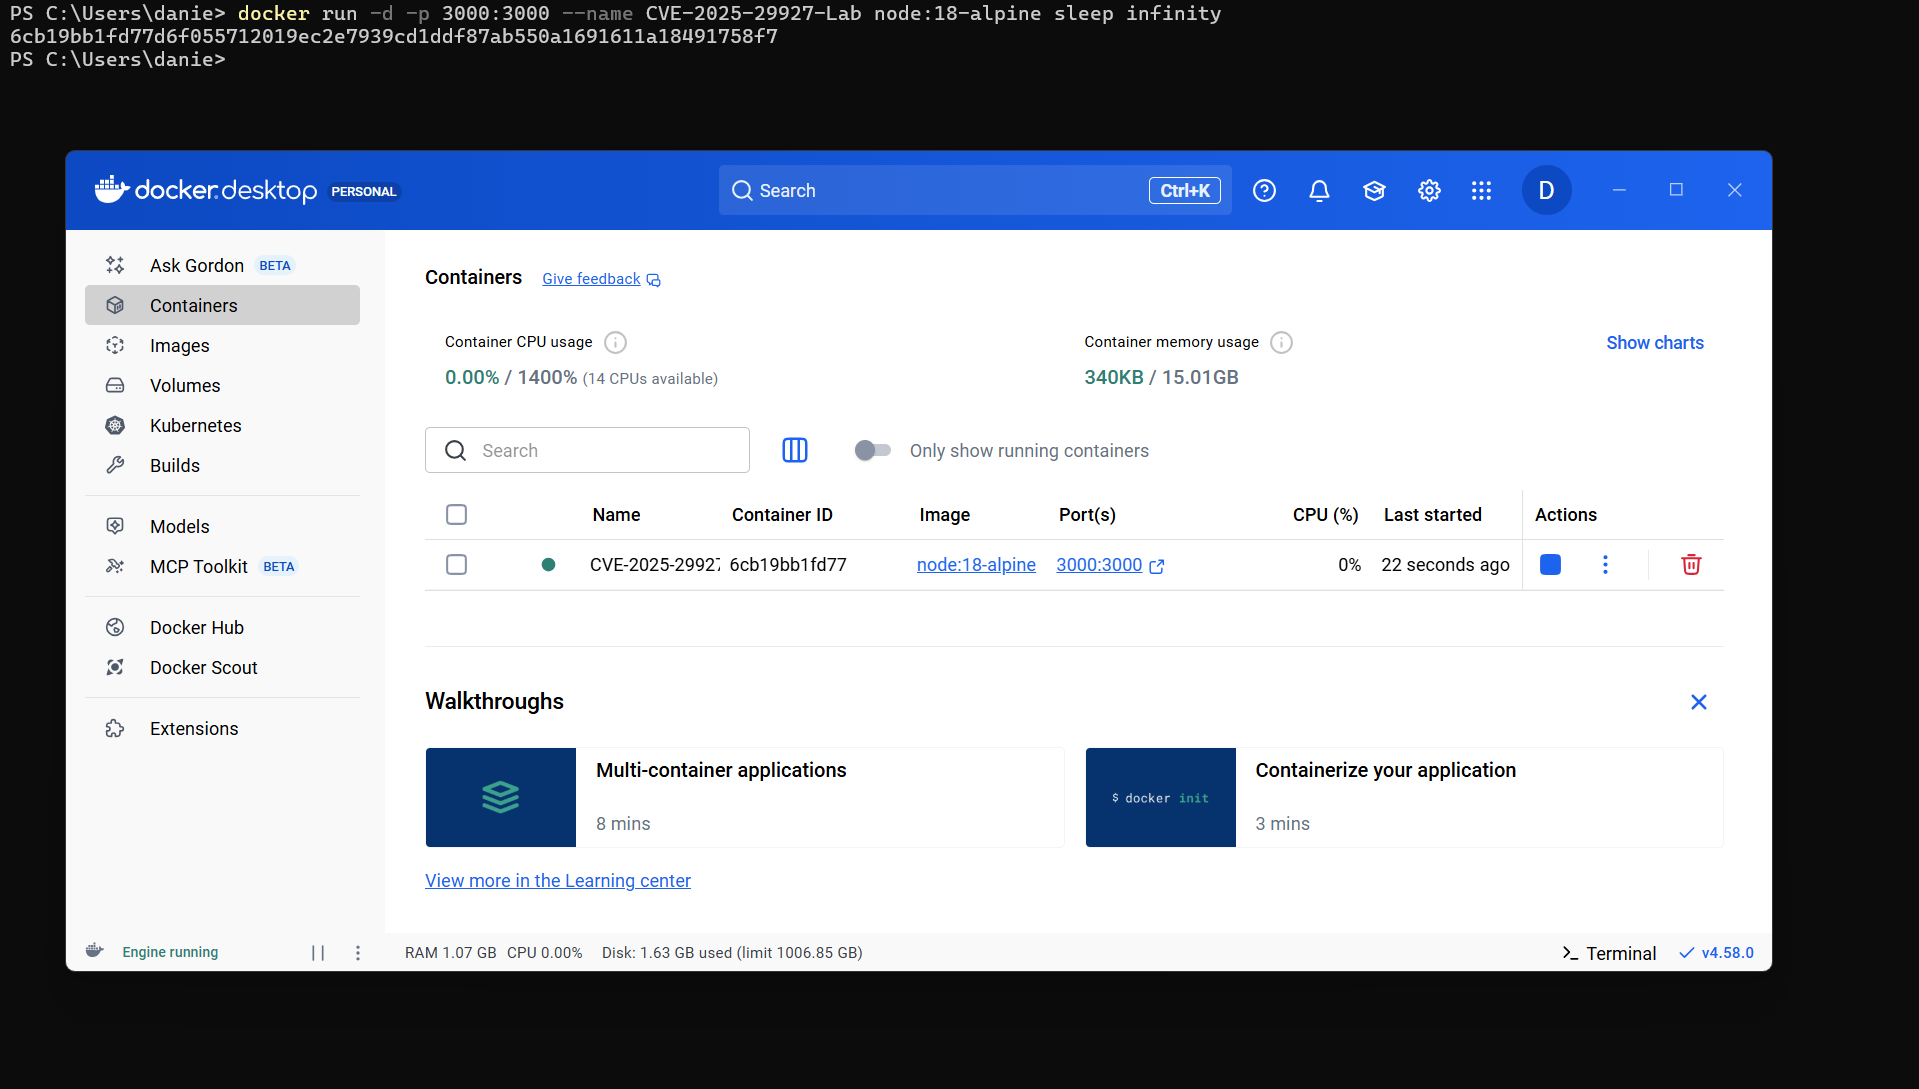 danielhallbro/cve-2025-29927-nextjs-bypass-poc
A Proof of Concept for CVE-2025-29927 demonstrating a middleware bypass in Next.js versions prior to 13.5.9
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
 eliasdekiniweek/cve-2022-26923
Exploitation de CVE-2022-26923
 itzvenom/cve-2023-6329
Python PoC exploit for CVE-2023-6329 authentication bypass in Control iD iDSecure. Reconstructs admin credentials via predictable password derivation…
 cyb3rmaddy/cve-2023-23397-report
An exploitation demo of Outlook Elevation of Privilege Vulnerability
 iveresk/cve-2022-31749
PoC checker for CVE-2022-31749 exploiting a parameter injection vulnerability in WatchGuard SSH interface to exfiltrate hashed user passwords via FTP.
 cveteam/flowiseai-critical-killchain
Critical unauthenticated kill chain leading to full RCE in FlowiseAI (CVE-2025-58434 + CVE-2025-59528)
 d0n601/cve-2025-4602
eMagicOne Store Manager for WooCommerce <= 1.2.5 - Unauthenticated Arbitrary File Read
 martinfrancois/cve-2021-36460
Advisory detailing a pass-the-hash vulnerability in VeryFitPro app (<=3.3.7) where SHA-1 password hashes are used for authentication, enabling…