Hack-Captive-Portal
This script helps to pass through the captive portals in public Wi-Fi networks. It hijacks IP and MAC from somebody who is already connected and…

This script helps to pass through the captive portals in public Wi-Fi networks. It hijacks IP and MAC from somebody who is already connected and…

Enumerate valid users within Microsoft Teams and OneDrive with clean output.

Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…

DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider

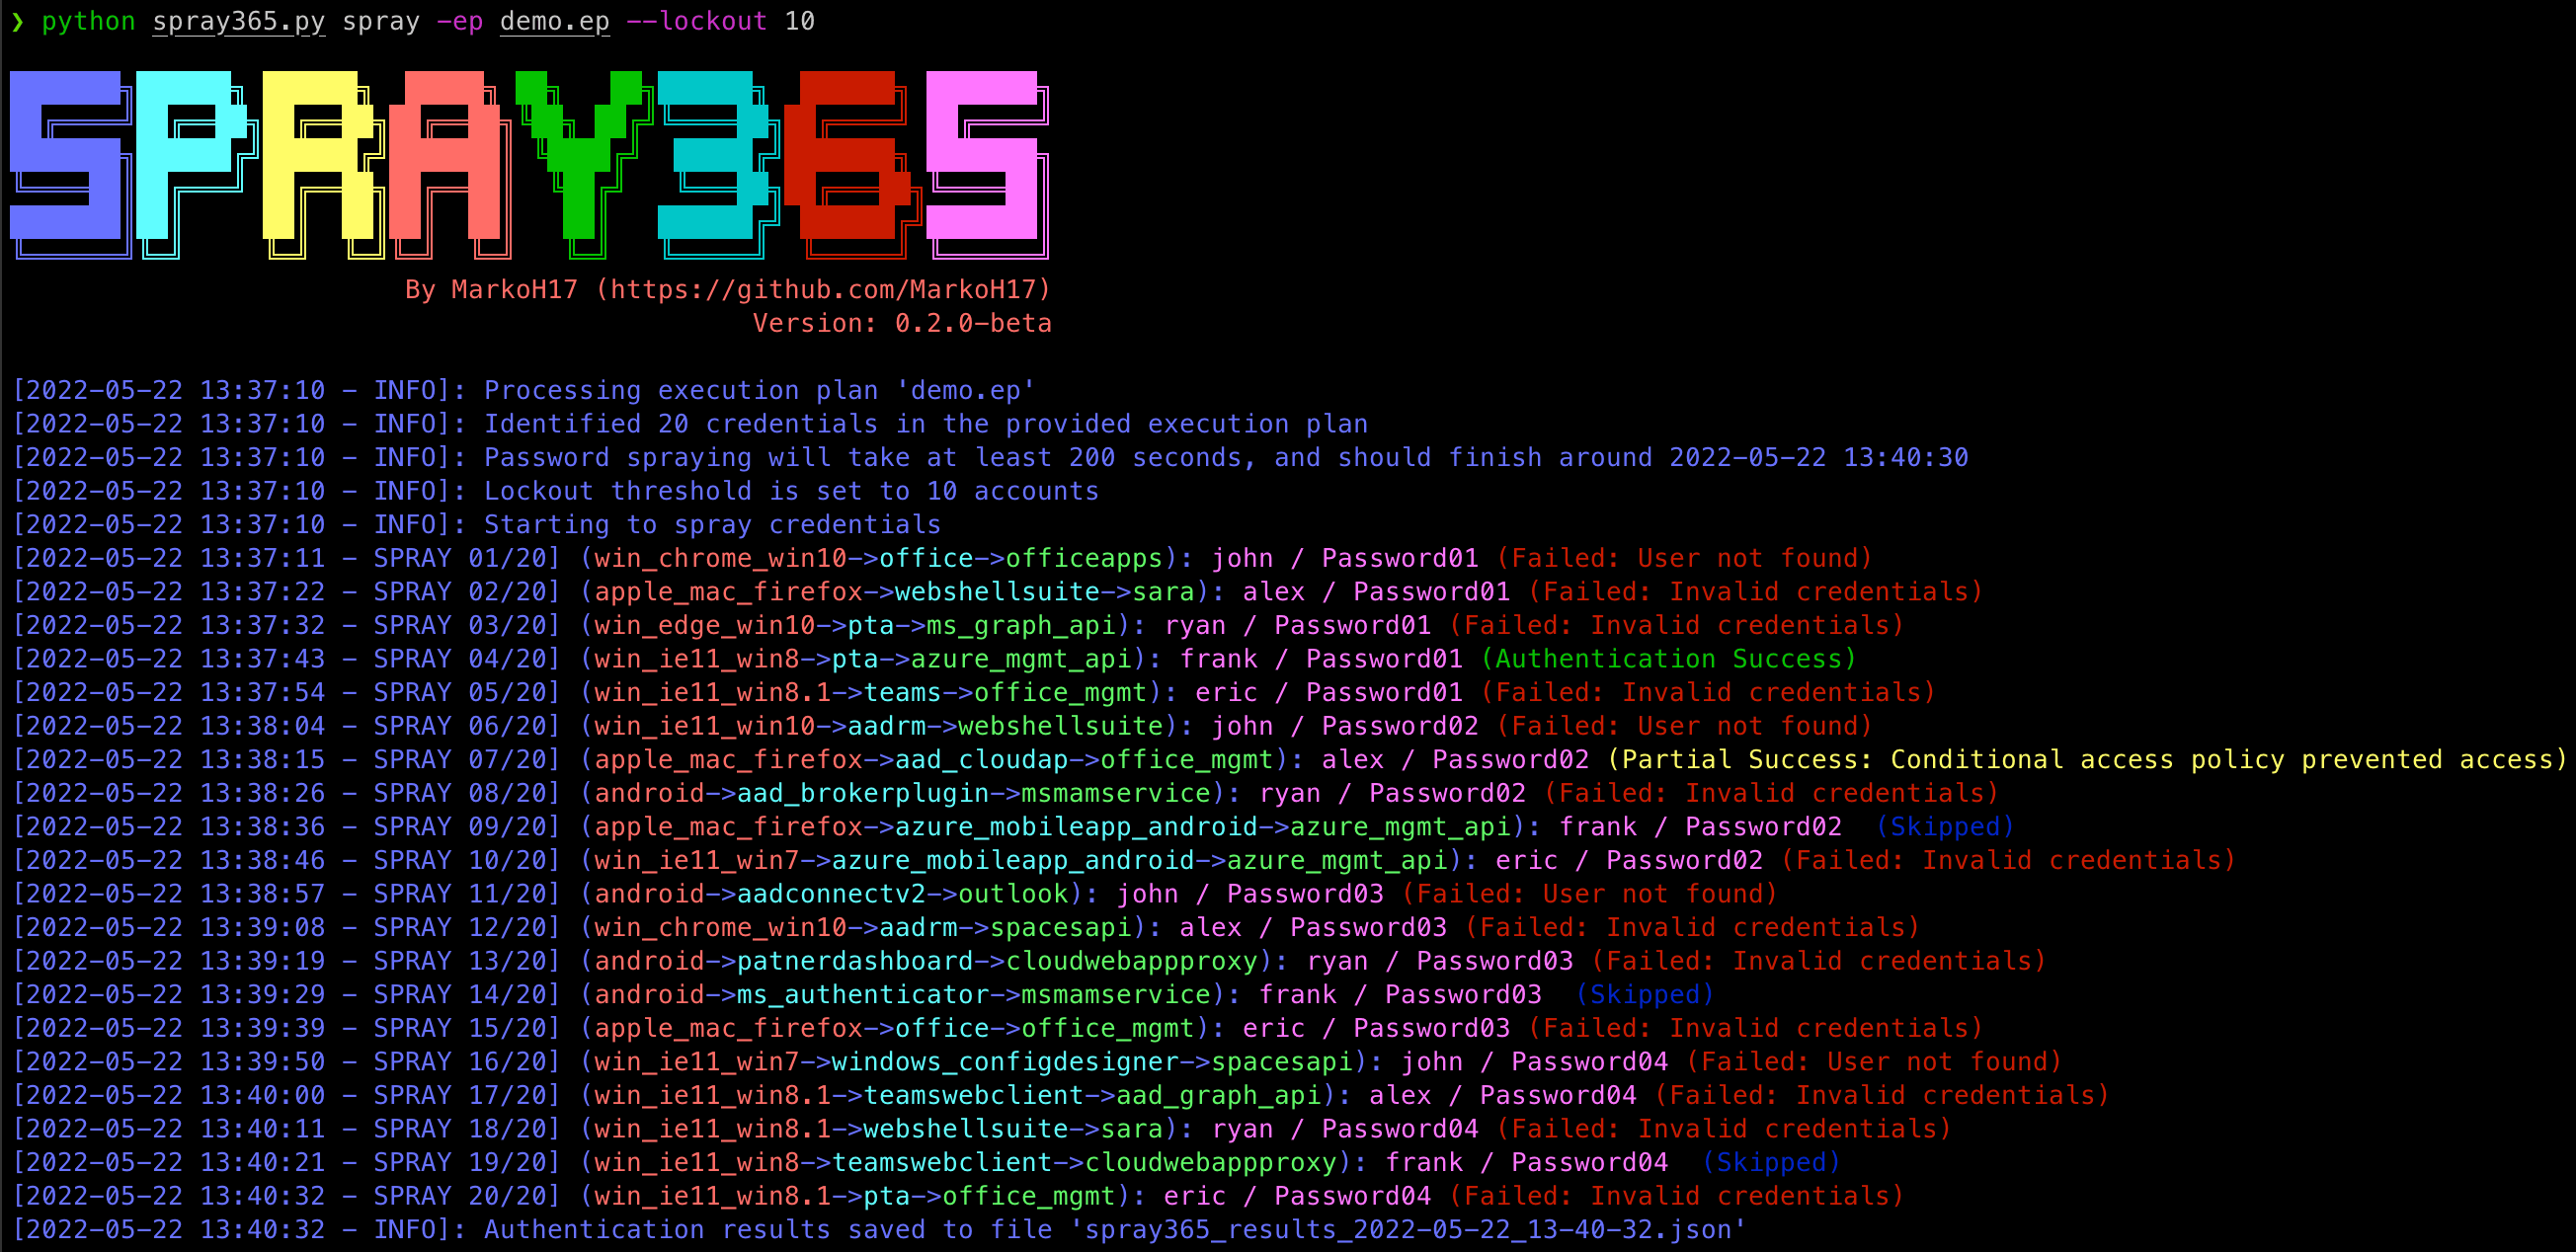
Spray365 makes spraying Microsoft accounts (Office 365 / Azure AD) easy through its customizable two-step password spraying approach. The built-in…

Password Lense: reveal character types in a password

A password guessing tool that targets the Kerberos and LDAP services within the Windows Active Directory environment.

Password attacks and MFA validation against various endpoints in Azure and Office 365

Modern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails

Cryptographic component from Zend Framework

A Dockerized Redash instance that is vulnerable to CVE-2021-21239

pfSense Plus MIM API toolkit b4acd7ca - High - Local - Privilege leftover - unix sock enroll no JWT

pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - Paramiko AutoAddPolicy enroll

Maintains the TUF repository that securely delivers the Sigstore trust root (trusted_root.json) to clients, using keyholder threshold signing, KMS…

Runnable Spring Boot and Quarkus proof-of-concept reproducing the Apache Camel camel-shiro thread-bound-subject authentication bypass, with affected…

Apache OpenMeetings 9.1.0 - High - Remote - 2FA skip - SOAP/REST password login skips TOTP

Apache OpenMeetings 9.1.0 - High - Remote - ATO - remember-me cookie replay authenticates without password