
telnet_scan
 ekomssavior/telnet_scan
scanner/exploiter CVE-2026-24061 & CVE-2026-32746
authenticationbinary-exploitationeducation+5
ekomssavior/telnet_scanscanner/exploiter CVE-2026-24061 & CVE-2026-32746
 gh-ost00/cve-2024-28987-poc
Web Help Desk Hardcoded Credential Vulnerability (CVE-2024-28987)
 chybeta/cve-2017-11427-demo
The Demo for CVE-2017-11427
 cartosys/domestic-system
Using @charmbracelet to create an Ethereum browser with style
 theogobinet/cve-2021-26088
PoC for CVE-2021-26088 written in PowerShell
 nxploited/cve-2026-12416-cve-2026-12417
Unauthenticated Account Takeover via Weak Password Reset Validation via 'reset_user_id' Parameter | Unauthenticated Privilege Escalation via Weak…
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 ap0dexme0/cve-2023-2732
Perform With Massive Authentication Bypass (Wordpress Mstore-API)
 bombobombone/cve-2026-73313
Proof-of-concept exploit for CVE-2026-73313, an MFA bypass in XenForo's passkey TFA provider allowing account takeover after password compromise.
 george0papasotiriou/cve-2026-5050-blind-ldap-injection-via-unescaped-filter
Reproduces CVE-2026-5050 with a simulated Flask LDAP server and exploit script, demonstrating blind LDAP injection via unescaped filters to bypass…
 cinno/cve-2015-7755-poc
Proof-of-concept exploit for CVE-2015-7755 targeting Juniper ScreenOS backdoor authentication bypass via SSH with hardcoded root credentials.
 rashidkhanpathan/cve-2022-38813
Authenticated Vertical Privilege Escalation Vulnerability in Blood Donor Management System
 lxdwnpiper/cve-2026-48611-phpbb
Python proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
 dairrow/cve-2025-31161
PoC Authentication Bypass to RCE to Exploit CVE-2025-31161
 0xbs0d27/cve-2025-56643
Public reference for CVE-2025-56643 – Wiki.js 2.5.307 JWT Session Vulnerability
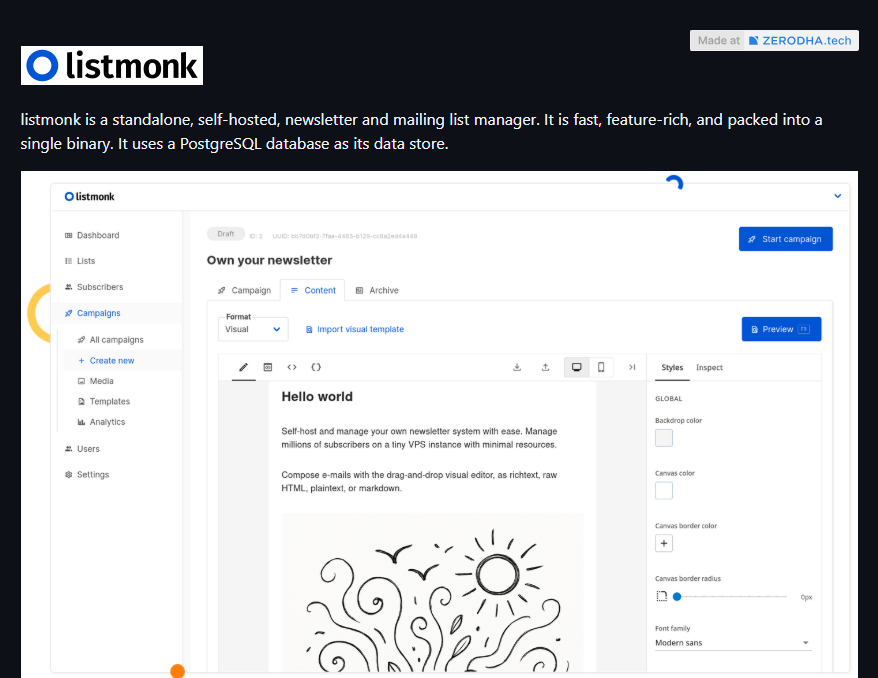 0xmrma/cve-2026-34828
listmonk’s Session Persistence After Password Reset and Password Change
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 ready2disclose/cve-2022-43110
CVE-2022-43110