watchTowr-vs-BMC-Footprints-RCE-CVE-2025-71257-CVE-2025-71260

Detection artifact generator that verifies BMC FootPrints instances for pre-authenticated RCE chain (CVE-2025-71257, CVE-2025-71260) by bypassing…

Detection artifact generator that verifies BMC FootPrints instances for pre-authenticated RCE chain (CVE-2025-71257, CVE-2025-71260) by bypassing…

This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.

Detects an authentication bypass vulnerability in Palo Alto PAN-OS (CVE-2025-0108).

Documentation of CVE-2026-36438: a vulnerability in Intelbras VIP 1230 B/D G4 devices allowing remote attackers to obtain administrator account…

CVE-2017-7921 is a critical vulnerability (CVSS score: 9.8) affecting multiple Hikvision IP camera and DVR models, first disclosed in 2017. It stems…

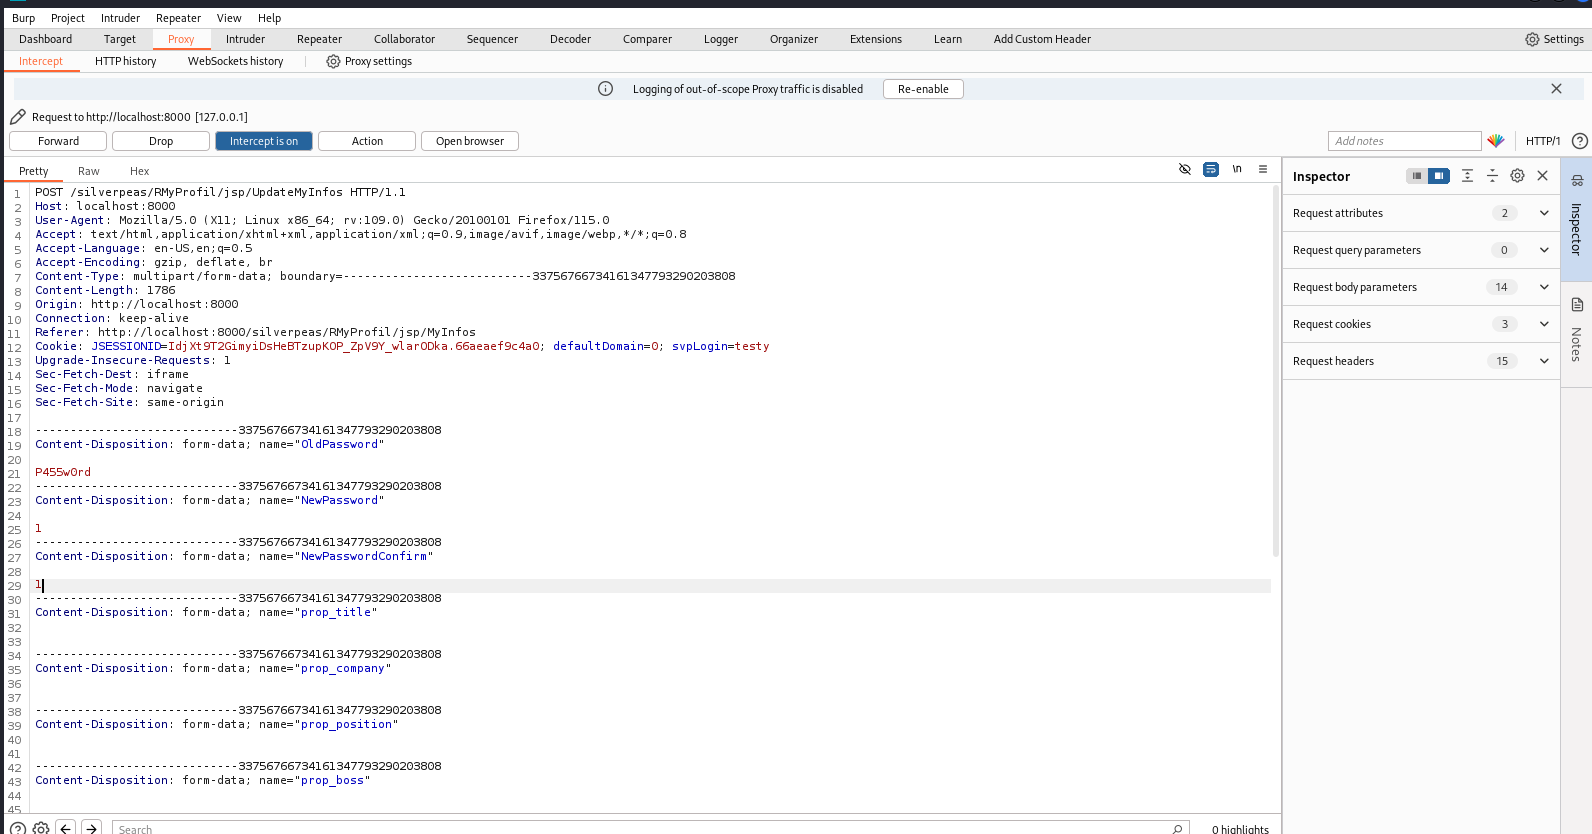
An issue in Silverpeas v6.4.2 and lower allows for the bypassing of password complexity requirements.

Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…

Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…

Technical documentation and proof-of-concept for CVE-2025-55462, a CORS misconfiguration in Eramba v3.26.0 allowing cross-origin authentication…

This is a little Python script to detect the "EvilSun" vulnerability (CVE-2020-14871) on Solaris systems. The vulnerability is a buffer overflow in…

Proof-of-concept exploit and advisory for CVE-2025-43921, an authentication bypass in GNU Mailman 2.1.39 that allows unauthenticated creation of…

Proof-of-concept for CVE-2021-3130: demonstrates credential exposure via HTML obfuscation bypass in Open-AudIT up to 4.0.2, revealing SSH, SNMP, and…

Patch for CVE-2024-10449: replaces vulnerable loginAction.php with a hardened version that requires database configuration for secure authentication.

Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…

🔥 A powerful MongoDB auditing and pentesting tool 🔥


Laravel TokenGuard authentication bypass through non-string API credentials

CVE-2024-29296 - User enumeration on Portainer CE - 2.19.4