
CVE-2026-29000
 otuva/cve-2026-29000
Proof-of-concept exploit for CVE-2026-29000, an authentication bypass in pac4j-jwt via nested PlainJWT with alg:none inside a JWE container.
authenticationexploitationpenetration-testing+2
1
otuva/cve-2026-29000Proof-of-concept exploit for CVE-2026-29000, an authentication bypass in pac4j-jwt via nested PlainJWT with alg:none inside a JWE container.
 cyberharsh/oracle-mysql-cve-2012-2122
Docker-based exploit environment for CVE-2012-2122 MySQL/MariaDB authentication bypass vulnerability. Demonstrates password comparison flaw allowing…
 sancliffe/cve-2026-29145-tester
This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.
 0xw1ld/cve-2026-29000
Rust-based exploit generator for CVE-2026-29000, an authentication bypass in pac4j-jwt via alg:none JWT nested in JWE, automating JWKS retrieval and…
 clayofgilgamesh/cve-2026-29000
CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 faccimatteo/cve-2022-4361
Proof-of-concept exploit for CVE-2022-4361, a reflected XSS vulnerability in Keycloak's OIDC authentication flow, with Docker-based test environment…
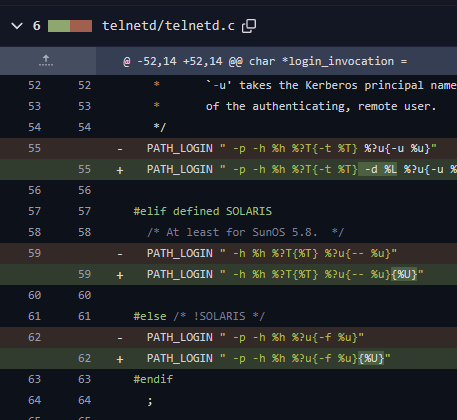 lucaspdiniz/cve-2026-24061
Vulnerability in GNU InetUtils telnetd Enables Remote Root Access
 bodoinon/cve-2024-10924
Demonstrates exploitation and mitigation of CVE-2024-10924, an authentication bypass in WordPress Really Simple Security, with automated Python…
 pannagkumaar/pentest-lab
Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…
 illera88/cve-2021-21239
Exploit for CVE-2021-21239: SAML signature validation bypass in pysaml2/Redash. Forges SAML responses with embedded public keys to impersonate users…
 youkergav/cve-2018-10933
Authentication Bypass in Server Code for LibSSH
 cipher1x1/cve-2026-29000
Proof-of-concept exploit for CVE-2026-29000, an authentication bypass in pac4j-jwt via JWE-wrapped unsigned JWT, enabling privilege escalation.
 savsch/poc_cve-2019-0217
Proof-of-concept exploit for CVE-2019-0217, a race condition in Apache HTTP Server's mod_auth_digest allowing authentication bypass. Includes…
 hunt3r850/cve-2024-10924-wordpress-docker
Dockerized exploit environment for CVE-2024-10924, an authentication bypass in WordPress Really Simple Security plugin (versions 9.0.0-9.1.1.1)…
 l1uk/nextjs-middleware-exploit
Research on Next.js middleware vulnerability (CVE-2025-29927) allowing authorization bypass and potential exploits.
 0xsu3ks/cve-2023-1665
CVE-2023-1665 - Twake App
 dev-sec/ansible-ssh-hardening
This Ansible role provides numerous security-related ssh configurations, providing all-round base protection.