

CVE-2021-42665
 0xdeku/cve-2021-42665
CVE-2021-42665 - SQL Injection authentication bypass vulnerability in the Engineers online portal system.
authenticationexploitationpenetration-testing+2
0xdeku/cve-2021-42665CVE-2021-42665 - SQL Injection authentication bypass vulnerability in the Engineers online portal system.
 randomrobbiebf/cve-2019-15896
LifterLMS <= 3.34.5 - Unauthenticated Options Import
 inflixim4be/cve-2020-15367
Exploit for CVE-2020-15367: brute-force authentication attack against Venki Supravizio BPM 10.1.2 login page, leveraging user enumeration to gain…
 ev3rpalestine/0xmiddleware
CVE-2025-29927: Next.js Middleware Exploit
 jet-pentest/cve-2020-29667
Proof-of-concept exploit for CVE-2020-29667 targeting insufficient session expiration and a hardcoded cookie value in Lan ATMService M3 ATM…
 stefandorresteijn/cve-2021-39409
Admin account registration in Online Student Rate System
 azhao1981/cve-2021-29441
Exploit for CVE-2021-29441 targeting Alibaba Nacos to add unauthorized accounts, enabling authentication bypass and unauthorized access.
 redfox-security/digisol-dg-gr1321-s-password-policy-bypass-cve-2024-2257
Exploit for CVE-2024-2257: bypasses password policy on Digisol DG-GR1321 routers via crafted HTTP request, enabling unauthorized access for…
 thetrueartist/abo.cms-login-sqli-cve-2024-25227
Unauthenticated SQL injection exploit for ABO.CMS 5.8 enabling login bypass and database takeover via the tb_login parameter.
 jet-pentest/cve-2020-27747
Possible Account Takeover | Brute Force Ability
 brunosergi/bloodit
Bludit 3.9.2 - Auth Brute Force Mitigation Bypass. CVE-2019-17240
 barcrange/cve-2025-0108-authentication-bypass-checker
Python script that tests PAN-OS devices for CVE-2025-0108 authentication bypass by sending crafted HTTP requests and analyzing responses.
 bombobombone/cve-2026-73311
Proof-of-concept exploit demonstrating OAuth2 authorization code reuse in XenForo before 2.3.13, allowing token replay and multiple token families.
 bombobombone/cve-2026-73310
Proof of concept and technical write-up for CVE-2026-73310, an OAuth2 authorization code redirect URI binding flaw in XenForo before 2.3.13,…
 hateshape/frevvomapexec
PoC Exploit for CVE-2018-8820
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 anir0y/sonicwall-audit-toolkit
SonicWall security audit toolkit with vulnerable CTF lab (CVE-2021-20038, CVE-2024-53704)
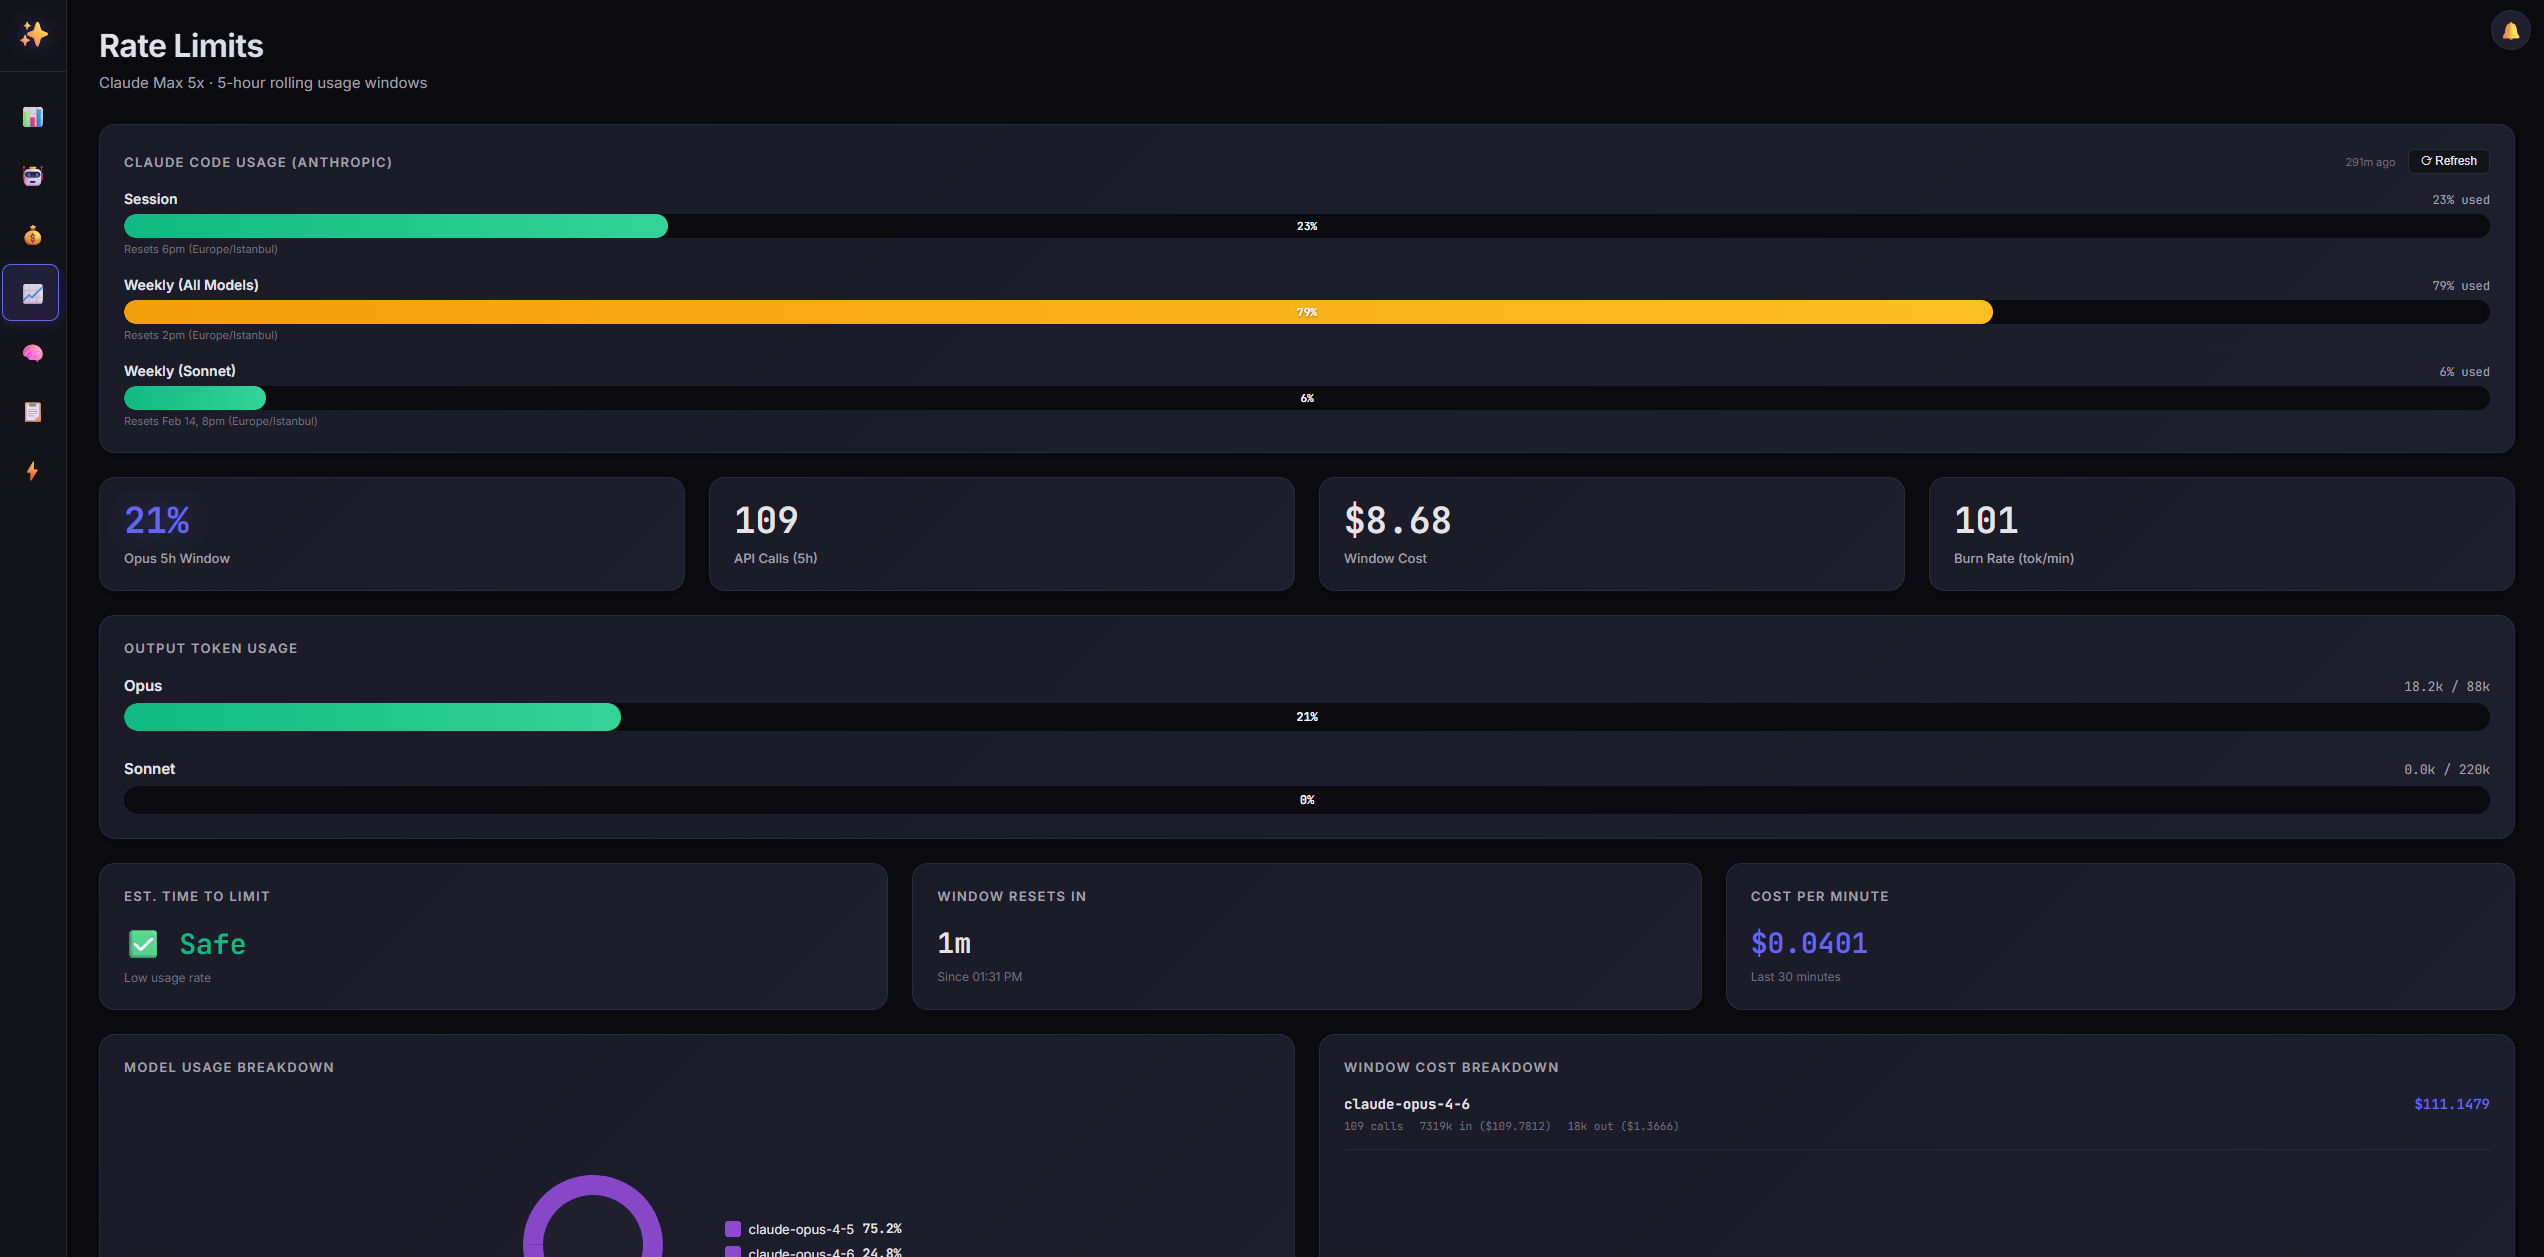 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.