
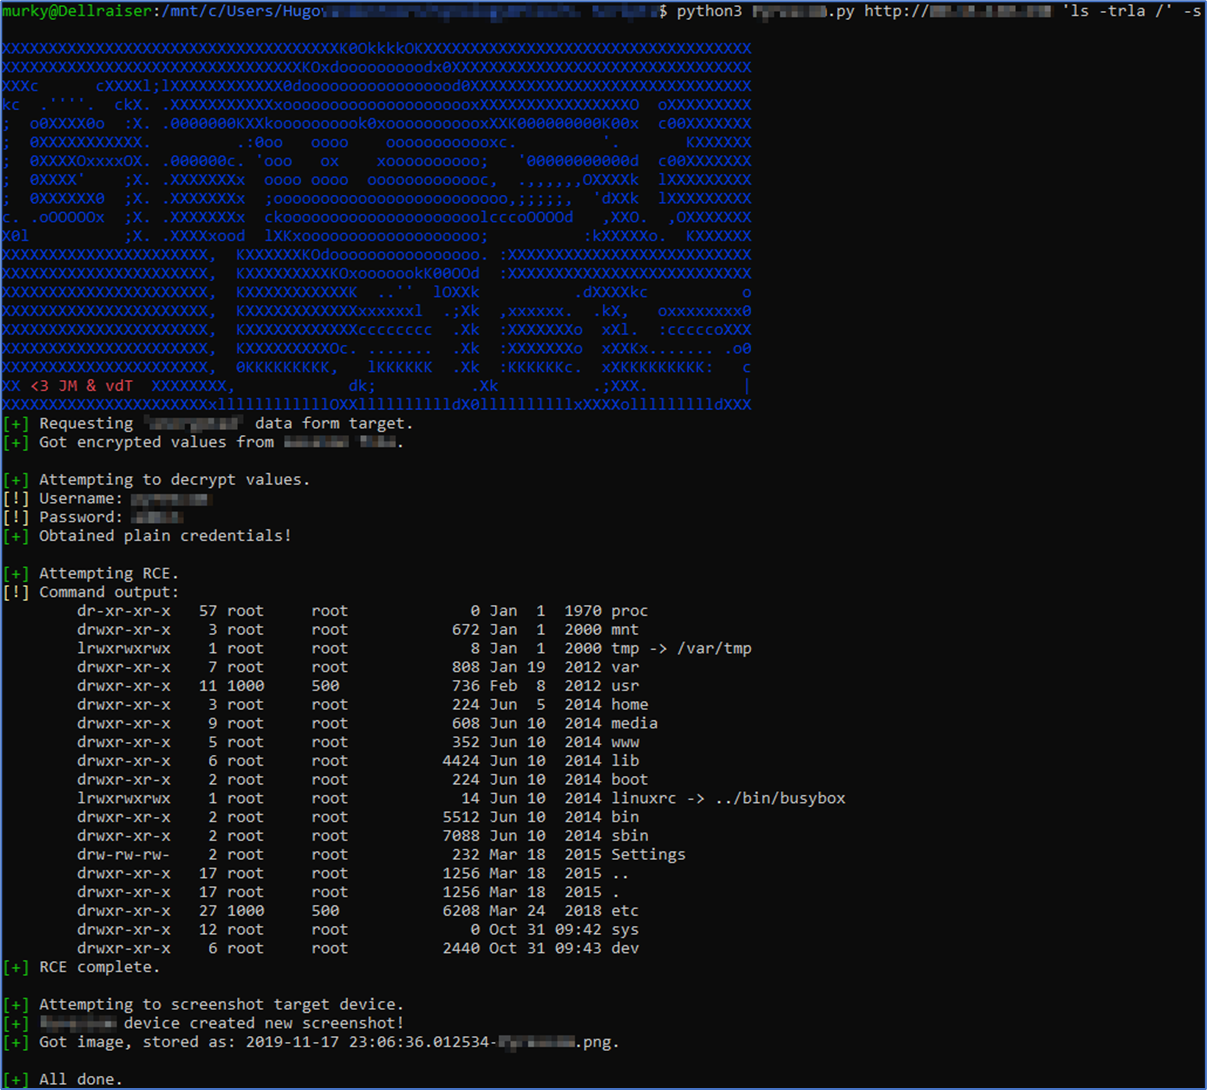
Pyrescom-Termod-PoC
 outpost24/pyrescom-termod-poc
Pyrescom Termod proof-of-concept code for CVE-2020-23160, CVE-2020-23161 and CVE-2020-23162
authenticationcommand-and-controlexploitation+5
outpost24/pyrescom-termod-pocPyrescom Termod proof-of-concept code for CVE-2020-23160, CVE-2020-23161 and CVE-2020-23162
 harydhk7/cve-2024-4358
Pre-authenticated remote code execution exploit for Telerik Report Server (CVE-2024-4358/CVE-2024-1800) with authentication bypass and…
 l1uk/nextjs-middleware-exploit
Research on Next.js middleware vulnerability (CVE-2025-29927) allowing authorization bypass and potential exploits.
 giovannidispoto/cve-2017-13872-patch
Exploit for CVE-2017-13872 that escalates privileges by changing the root password on vulnerable systems. Requires execution and provides new root…
 yowise/cve-2022-26923
Detailed technical write-up and proof-of-concept for CVE-2022-26923, an Active Directory Certificate Services privilege escalation vulnerability,…
 lcartey/proftpd-cve-2019-12815
Exploit for CVE-2019-12815 in ProFTPD 1.3.x, a configurable FTP daemon with virtual users, multiple authentication methods, and modular architecture…
 underprotection/cve-2020-24029
Proof-of-concept for CVE-2020-24029: unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege…
 leekenghwa/cve-2023-37755---hardcoded-admin-credential-in-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37755: hardcoded admin credentials (admin/admin) in i-doit Pro 25 and below, enabling unauthorized admin login via the…
 dante01yoon/cve-2025-29927
Demonstration of CVE-2025-29927: Next.js middleware authentication bypass via x-middleware-subrequest header spoofing. Includes vulnerable and fixed…
 notitssixtyn3in/cve-2025-4162029
Security advisory detailing a critical authentication vulnerability (CVE-2025-4162029) in Copilot, enabling unauthorized account access via user ID…
 notitssixtyn3in/cve-2025-4162025
Security advisory detailing a critical authentication vulnerability (CVE-2025-4162025) in Copilot, including impact analysis, affected versions, and…
 volodymyr-hladkyi-symphony/demo-cve-2022-21449
Educational demo of CVE-2022-21449 Java ECDSA signature bypass using real and fake JWT tokens to illustrate the vulnerability and its impact on…
 notitssixtyn3in/cve-2025-4162027
Security advisory detailing a critical authentication vulnerability in Copilot where user IDs are switched, enabling unauthorized account access and…
 huyvo2910/cve-2025-25749-weak-password-policy-in-hoteldruid-3.0.7
Proof-of-concept for CVE-2025-25749 demonstrating weak password policy in HotelDruid 3.0.7, with automated test scripts and mitigation…
 notitssixtyn3in/cve-2025-4162030
Security advisory detailing a critical authentication vulnerability (CVE-2025-4162030) in Copilot, involving user ID switching that could lead to…
 castro-ian/cve-2024-4573-mitigation-script
Detects NTLM authentication status by checking LmCompatibilityLevel registry value to assess exposure to CVE-2024-43451 and mitigate credential relay…
 h3x0v3rl0rd/gmsa_dumper
Python utility that reads accessible gMSA password blobs from Active Directory and extracts plaintext passwords for use in security audits and red…
 guy2610/tough-cookie-patch-cve-2023-26136
RFC6265-compliant cookie parsing and CookieJar management library for Node.js, with CVE-2023-26136 security patch. Supports cookie creation,…