

NextSploit
 anonkryptiquz/nextsploit
NextSploit is a command-line tool designed to detect and exploit CVE-2025-29927, a security flaw in Next.js
authenticationexploitationinformation-gathering+3
92
anonkryptiquz/nextsploitNextSploit is a command-line tool designed to detect and exploit CVE-2025-29927, a security flaw in Next.js
 randomrobbiebf/cve-2023-2982
WordPress Social Login and Register (Discord, Google, Twitter, LinkedIn) <= 7.6.4 - Authentication Bypass
 praetorian-inc/ntlmrecon
A tool for performing light brute-forcing of HTTP servers to identify commonly accessible NTLM authentication endpoints.
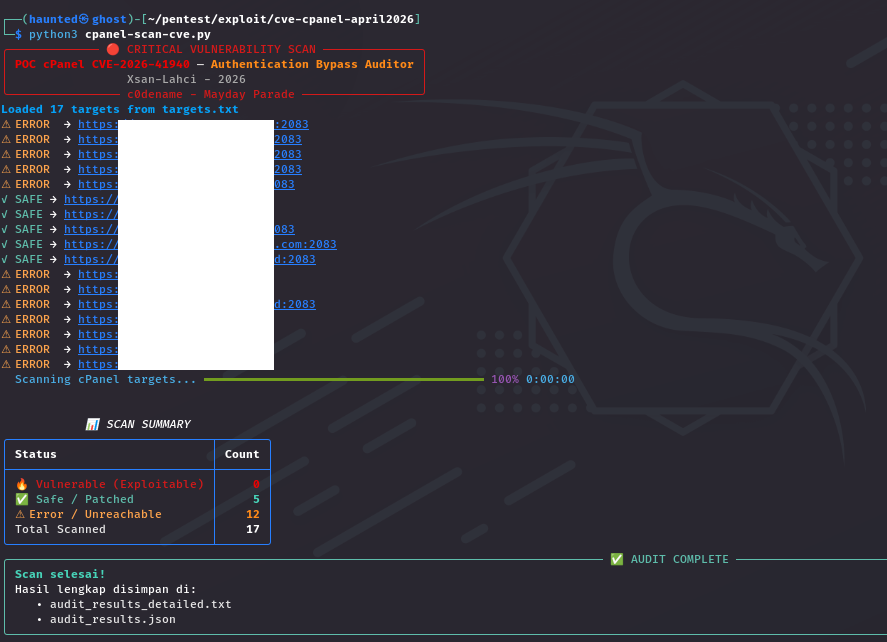 xsanflip/poc-cpanel-cve-2026-41940
Multi-threaded security auditing tool that detects CVE-2026-41940, an authentication bypass in cPanel/WHM, using CRLF injection and dynamic port…
 sourceincite/dashoverride
This is a pre-authenticated RCE exploit for VMware vRealize Operations Manager
 stuub/cve-2024-4040-ssti-lfi-poc
CVE-2024-4040 CrushFTP SSTI LFI & Auth Bypass | Full Server Takeover | Wordlist Support
 jazzpizazz/bloodhound.py-kerberos
A Python based ingestor for BloodHound
 pilfer/idictpy
A salty-ass 100% verified hacker status python script to turn apple id's into apple crisp #nicememe
 mihat2/resetnightmare-impacket
CVE-2026-27912 (ResetNightmare) — Linux/impacket port of Semperis Community's Invoke-ResetNightmare PoC
 blackhatexploitation/exploit-mikrotik-2026
CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit
 watchtowrlabs/watchtowr-vs-crushftp-authentication-bypass-cve-2025-54309
Proof-of-concept exploit for CVE-2025-54309, demonstrating an authentication bypass via race condition in CrushFTP WebInterface to enumerate users.
 kh4sh3i/cve-2022-23131
Python exploit for CVE-2022-23131 targeting Zabbix SAML SSO authentication bypass. Includes Shodan and FOFA dorks for vulnerable instance discovery.
 zux0x3a/adfly
active directory query tool using LDAP Protocol , helps red teamer / penetration testers to validate users credentials , retrieve information about…
 seckatie/cve-2019-8978
Banner Web Tailor and Banner Enterprise Identity Services Vulnerability Disclosure
 nccgroup/nlahoney
NLA Honeypot Associated Research
 horizon3ai/cve-2024-28987
Proof-of-concept exploit for CVE-2024-28987 targeting SolarWinds Web Help Desk hardcoded credential vulnerability. Automates exploitation via URL…
 gotr00t0day/cve-2024-4040
Exploit for CrushFTP SSTI vulnerability (CVE-2024-4040) enabling unauthenticated file read, authentication bypass, and remote code execution on…