
CVE-2025-59390-
 daeda1usuk/cve-2025-59390-
CVE-2025-59390 and ThreadLocalRandom Inverse
authenticationexploitationpassword-attacks+3
111 months ago
daeda1usuk/cve-2025-59390-CVE-2025-59390 and ThreadLocalRandom Inverse
 jfriedli/cve-2025-10658
Python exploit script for CVE-2025-10658: brute-forces 6-digit OTP in WordPress SupportCandy guest login to achieve full account takeover via…
 starawneh/cve-2025-4094
CVE-2025-4094 – WordPress Digits Plugin < 8.4.6.1 - OTP Authentication Bypass
 aakashtyal/2fa-bypass-using-a-brute-force-attack-cve-2025-60424
Demonstrates a brute-force attack bypassing two-factor authentication in Nagios Fusion due to missing rate limiting and lockout, with CVE-2025-60424…
 soy-oreocato/cve-2022-42176
Proof-of-concept for CVE-2022-42176: hard-coded credentials in PCSecure configuration file allow local privilege escalation to admin panel and…
 d0n601/buffalo
A python3 multithreaded SSH dictionary attack tool
 realbatuhan/jwt-bruteforcer
Jwt Bruteforcer with CVE-2018-1000531 Test
 jenderal92/prepos-login-checker
Prepostseo Login Checker
 randomrobbiebf/postgres-bruteforcer
This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.
 gmh5225/csrfbrute
专为红队行动设计的CSRF登录暴力破解工具,具备动态CSRF Token刷新、多线程并发和会话恢复功能,支持高并发操作和智能重试机制。
 inflixim4be/cve-2020-15367
Exploit for CVE-2020-15367: brute-force authentication attack against Venki Supravizio BPM 10.1.2 login page, leveraging user enumeration to gain…
 mind2hex/cve-2019-17240-bludit-3.9.2-auth-bruteforce-bypass
Bludit 3.9.2 auth bruteforce bypass
 ethancunt/cve-2022-45599
Proof-of-concept for CVE-2022-45599: PHP type juggling vulnerability in Aztech WMB250AC router login.php allowing admin authentication bypass via…
 jet-pentest/cve-2020-27747
Possible Account Takeover | Brute Force Ability
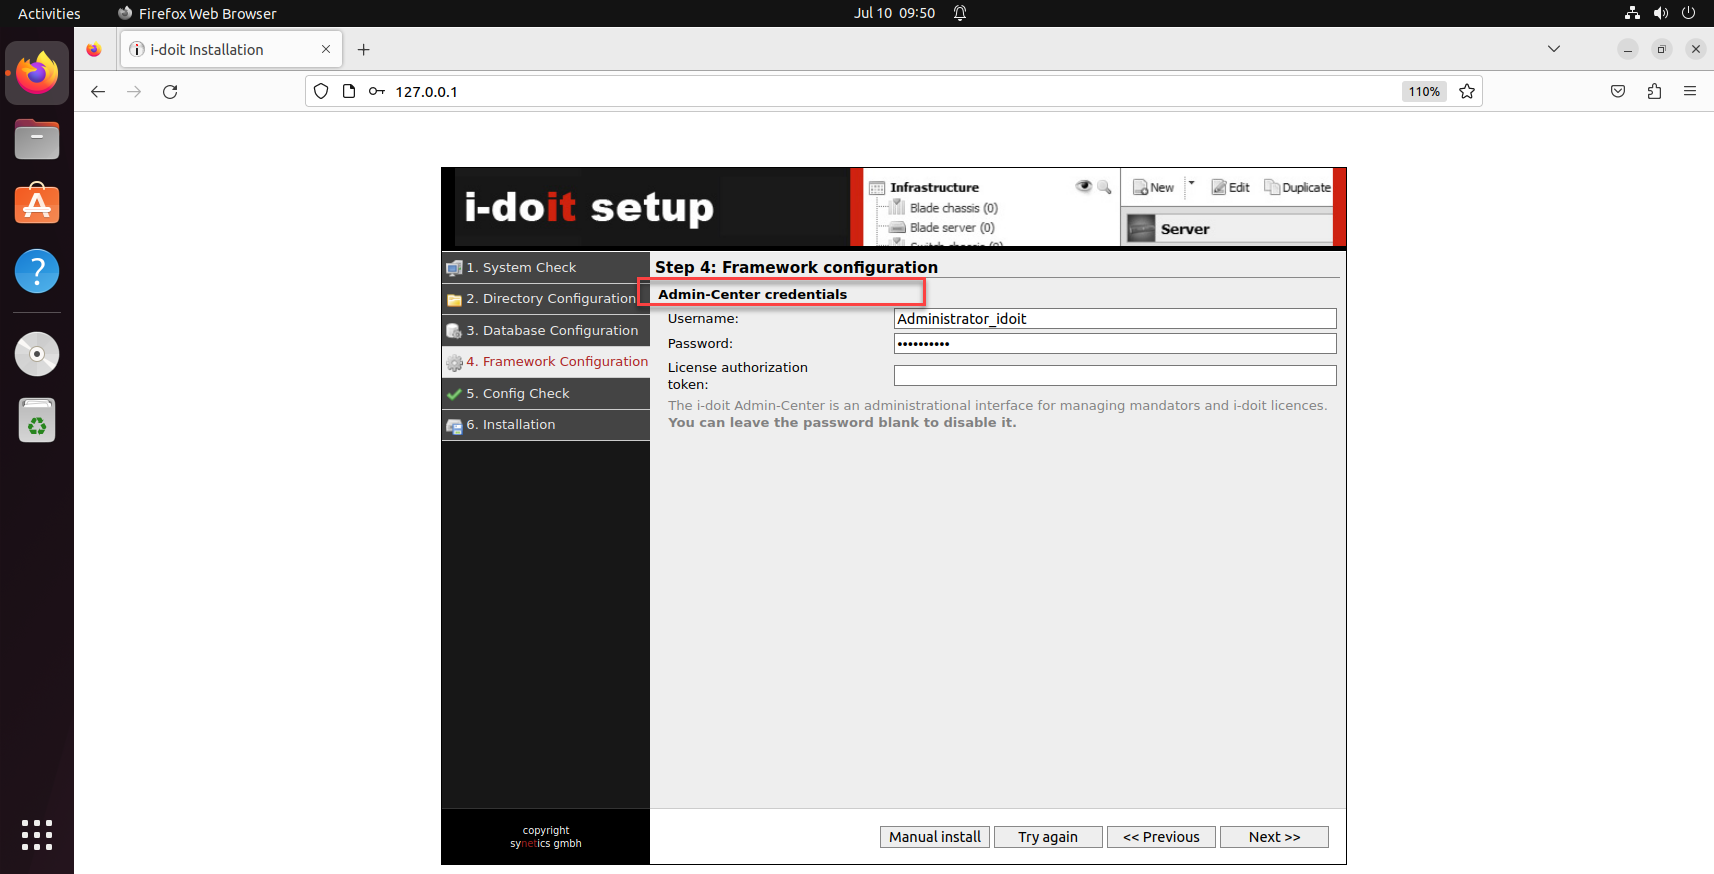 leekenghwa/cve-2023-37755---hardcoded-admin-credential-in-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37755: hardcoded admin credentials (admin/admin) in i-doit Pro 25 and below, enabling unauthorized admin login via the…
 nuid/nebulousad
NebulousAD automated credential auditing tool.
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.