
CVE-2026-8793
 h4zaz/cve-2026-8793
esponsible disclosure write-ups for CVE-2026-8793 - PaperCut NG 25.0.11
authenticationeducationexploitation+4
h4zaz/cve-2026-8793esponsible disclosure write-ups for CVE-2026-8793 - PaperCut NG 25.0.11
 george0papasotiriou/cve-2026-5050-blind-ldap-injection-via-unescaped-filter
Reproduces CVE-2026-5050 with a simulated Flask LDAP server and exploit script, demonstrating blind LDAP injection via unescaped filters to bypass…
 hsw109/cve-2018-10933
Education purpose for CVE-2018-10933
 george0papasotiriou/cve-2026-11116-snmpv3-authentication-bypass-via-default-engineid
Demonstrates CVE-2026-11116 SNMPv3 authentication bypass caused by guessable default EngineIDs, with a Python pysnmp simulation and guidance for…
 covepseng/cve-2026-43512-poc
Exploitability PoC for CVE-2026-43512 (Apache Tomcat Digest Authentication Bypass)
 aykhan32/cve-2026-51788
Detailed CVE-2026-51788 advisory for a DoS vulnerability in cleverange_auth v0.1.10, with technical analysis, CVSS scoring, and mitigation guidance…
 jwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report
Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…
 het-kalariya/cve-2026-20253
Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…
 cybervinner/cp-plus-ez-p21-cve-2026-65893-65894
Documents CP PLUS EZ-P21 IP camera CVEs: arbitrary code execution via debug feature and improper authentication of HTTP endpoints, with responsible…
 ap0dexme0/cve-2023-27350
Perfom With Massive Authentication Bypass In PaperCut MF/NG
 horkimhab/cve-2026-34348
CVE-2026-34348 - Draft or TODO
 dua2z3rr/cve-2026-29000-poc
CVE-2026-29000 - pac4j-jwt (< 4.5.9 / < 5.7.9 / < 6.3.3) JwtAuthenticator authentication bypass PoC
 ubaydev/cve-2024-10542
WordPress Spam protection, AntiSpam, FireWall by CleanTalk Plugin <= 6.43.2 is vulnerable to Unauthenticated Arbitrary Plugin Installation
 gh-ost00/cve-2024-4358
Telerik Report Server deserialization and authentication bypass exploit chain for CVE-2024-4358/CVE-2024-1800
 abdugafforov-bobur/cve-2026-54415-poc
PoC for CVE-2026-54415 — Azuriom CMS (<1.2.11) Broken Access Control → account takeover
 nxploited/cve-2025-47646
WordPress PSW Front-end Login & Registration Plugin <= 1.12 is vulnerable to Broken Authentication
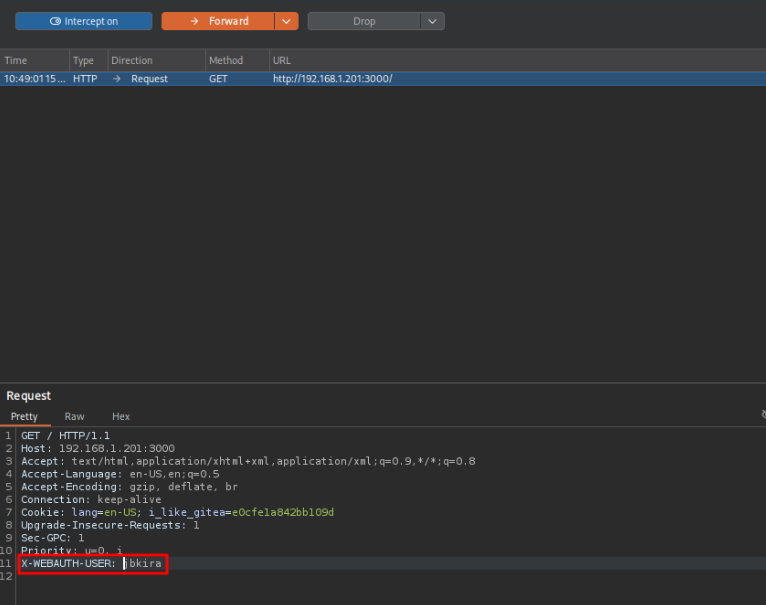 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
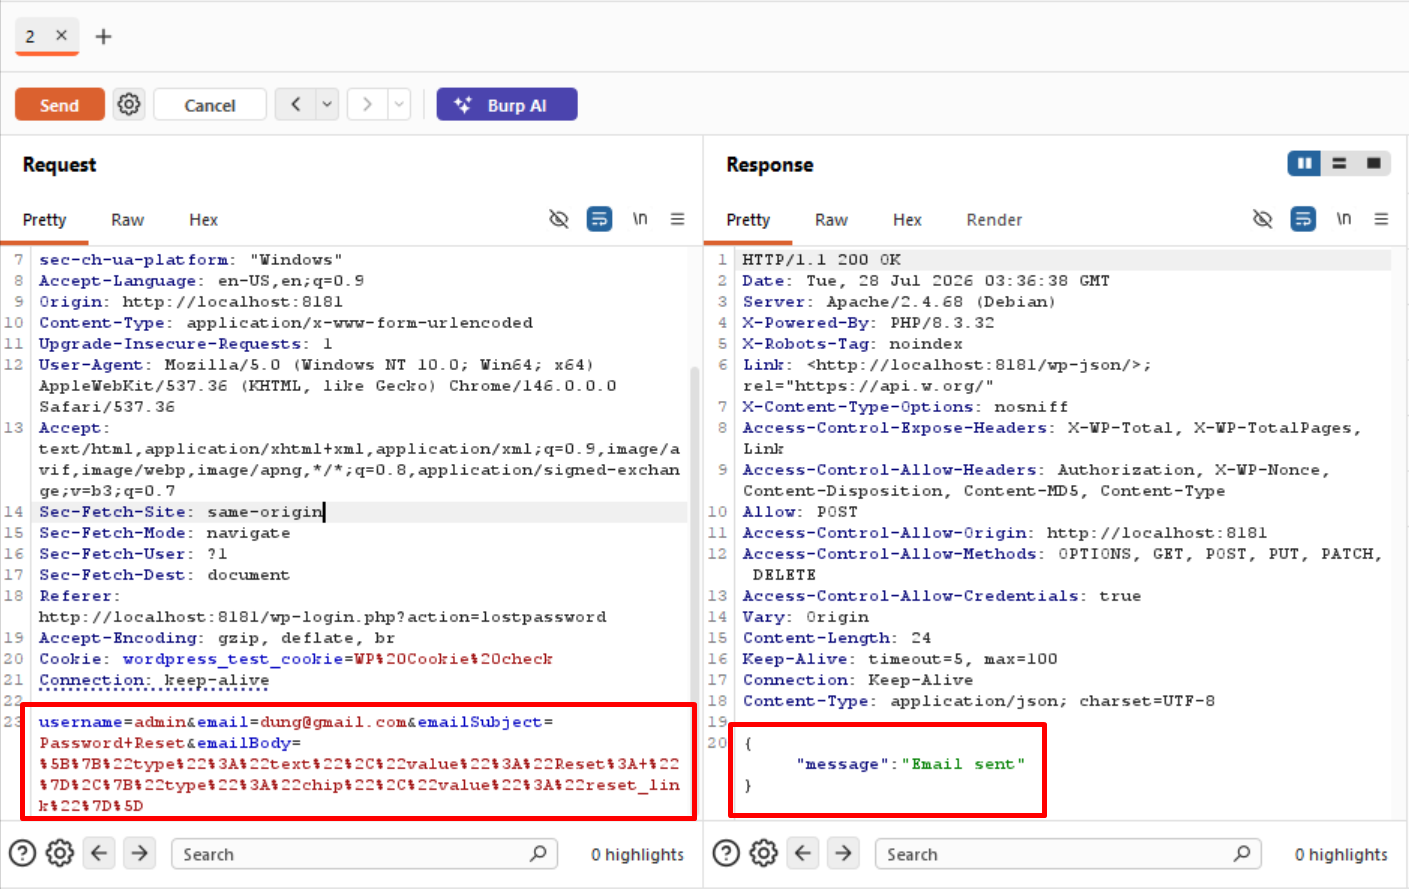 dungsocool/cve-2026-8206
CVE-2026-8206: Kirki Customizer Framework - Unauthenticated Account Takeover (CVSS 9.8)