cve-2022-22976-bcrypt-skips-salt

CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…

CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…

The Academy LMS – WordPress LMS Plugin for Complete eLearning Solution plugin for WordPress is vulnerable to privilege escalation via account…

Vatilon-based IP camera firmwares issue Session-Id tokens without verifying credentials, allowing attackers to obtain sessions and retrieve plaintext…

Original security research and proof-of-concept for CVE-2026-29145, an Apache Tomcat OCSP authentication bypass vulnerability, including technical…

PoC for CVE-2025-64513 — Milvus Proxy Authentication Bypass Vulnerability Batch scanner to verify unauthorized access and gather Milvus version,…

OAuth 2.0 client library for Kit applications supporting authorization code, PKCE, client credentials, and refresh token flows with built-in provider…

Python scanner that detects Next.js instances vulnerable to CVE-2025-29927, identifies versions, and tests for authentication bypass via the…

Proof-of-concept for CVE-2022-42176: hard-coded credentials in PCSecure configuration file allow local privilege escalation to admin panel and…

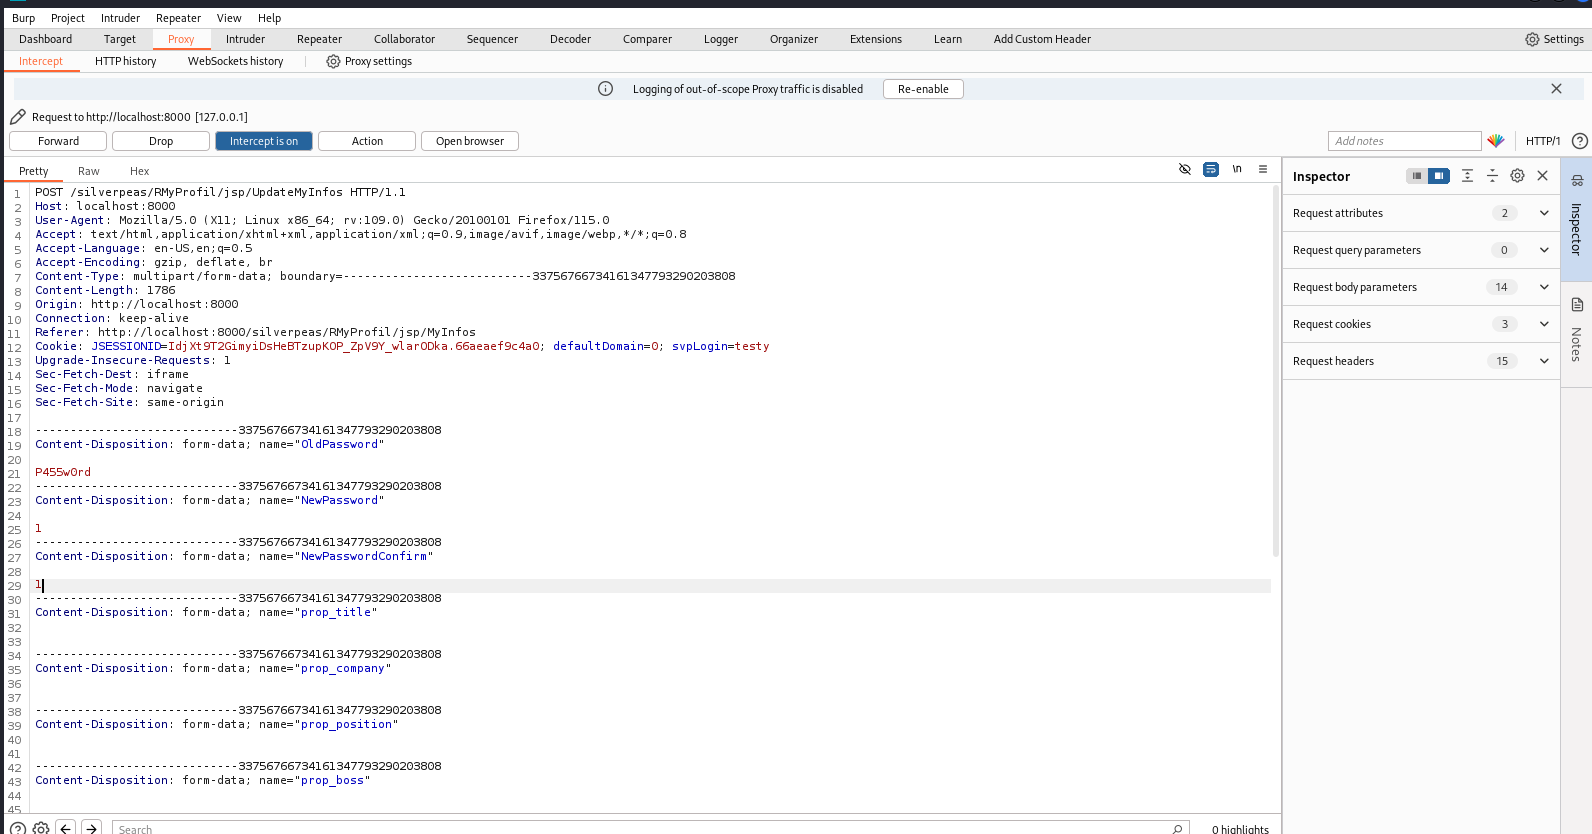
An issue in Silverpeas v6.4.2 and lower allows for the bypassing of password complexity requirements.

Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…

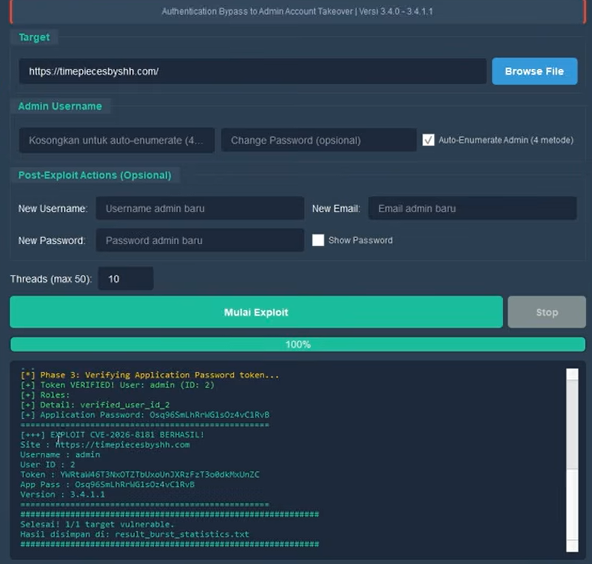
CVE-2026-8181 — Burst Statistics WordPress plugin Authentication Bypass (CVSS 9.8) to Admin Account Takeover. Mass scanner with FOFA/Shodan…

Revotech I6032W-FHW IP camera firmware fails to validate authentication fields in API requests, allowing attackers to bypass authentication and…

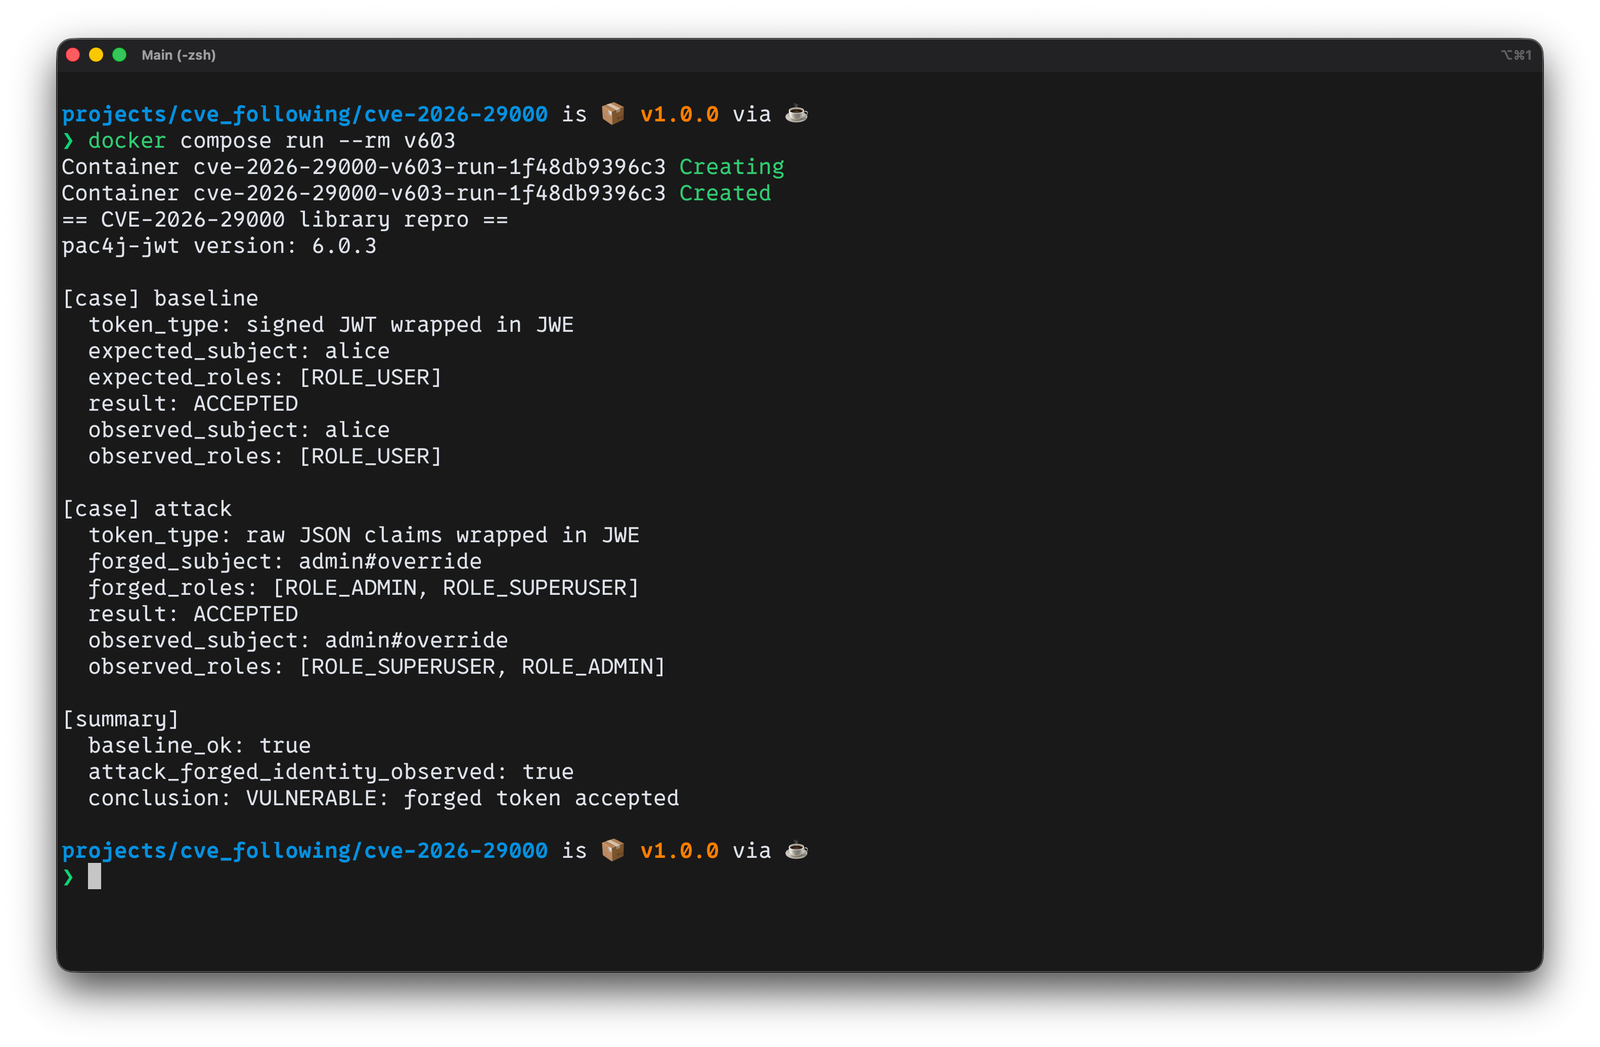
Library-level proof-of-concept lab demonstrating CVE-2026-29000 in pac4j-jwt, comparing vulnerable and patched versions with Docker to show forged…

Proof-of-concept for CVE-2026-31282: Totara LMS login page access control bypass enabling unauthenticated brute-force credential attacks. Includes…

Proof-of-concept for CVE-2025-66698: authentication bypass in Veda v5.4.8 via empty ticket parameter, enabling enumeration of users, policies, and…

Exploit script for CVE-2025-68860 targeting WordPress Mobile Builder plugin. Generates forged JWT tokens using a hardcoded secret to authenticate as…

Proof-of-concept exploit for CVE-2025-65427: missing rate limiting on Dbit N300 T1 Pro router login API enabling brute-force attacks and…

Python exploit script for ThinVNC 1.0b1 authentication bypass (CVE-2022-25226) that chains unauthenticated /cmd endpoint access with AMSI bypass and…