OpenSSL-1_0_1g_CVE-2015-3194

OpenSSL 1.0.1g source code snapshot, providing SSL/TLS and general-purpose cryptographic library with ciphers, digests, and X.509 certificate…

OpenSSL 1.0.1g source code snapshot, providing SSL/TLS and general-purpose cryptographic library with ciphers, digests, and X.509 certificate…

CVE-2019-14830

Fork of laravel/framework 10.50.2 with CVE-2026-48019 (CRLF injection in default email rule) backported into ValidatesAttributes::validateEmail.…

Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click remote code execution in OpenClaw via authentication token theft and cross-site…

JSON Web Token (JWT) encoding and decoding for Kit

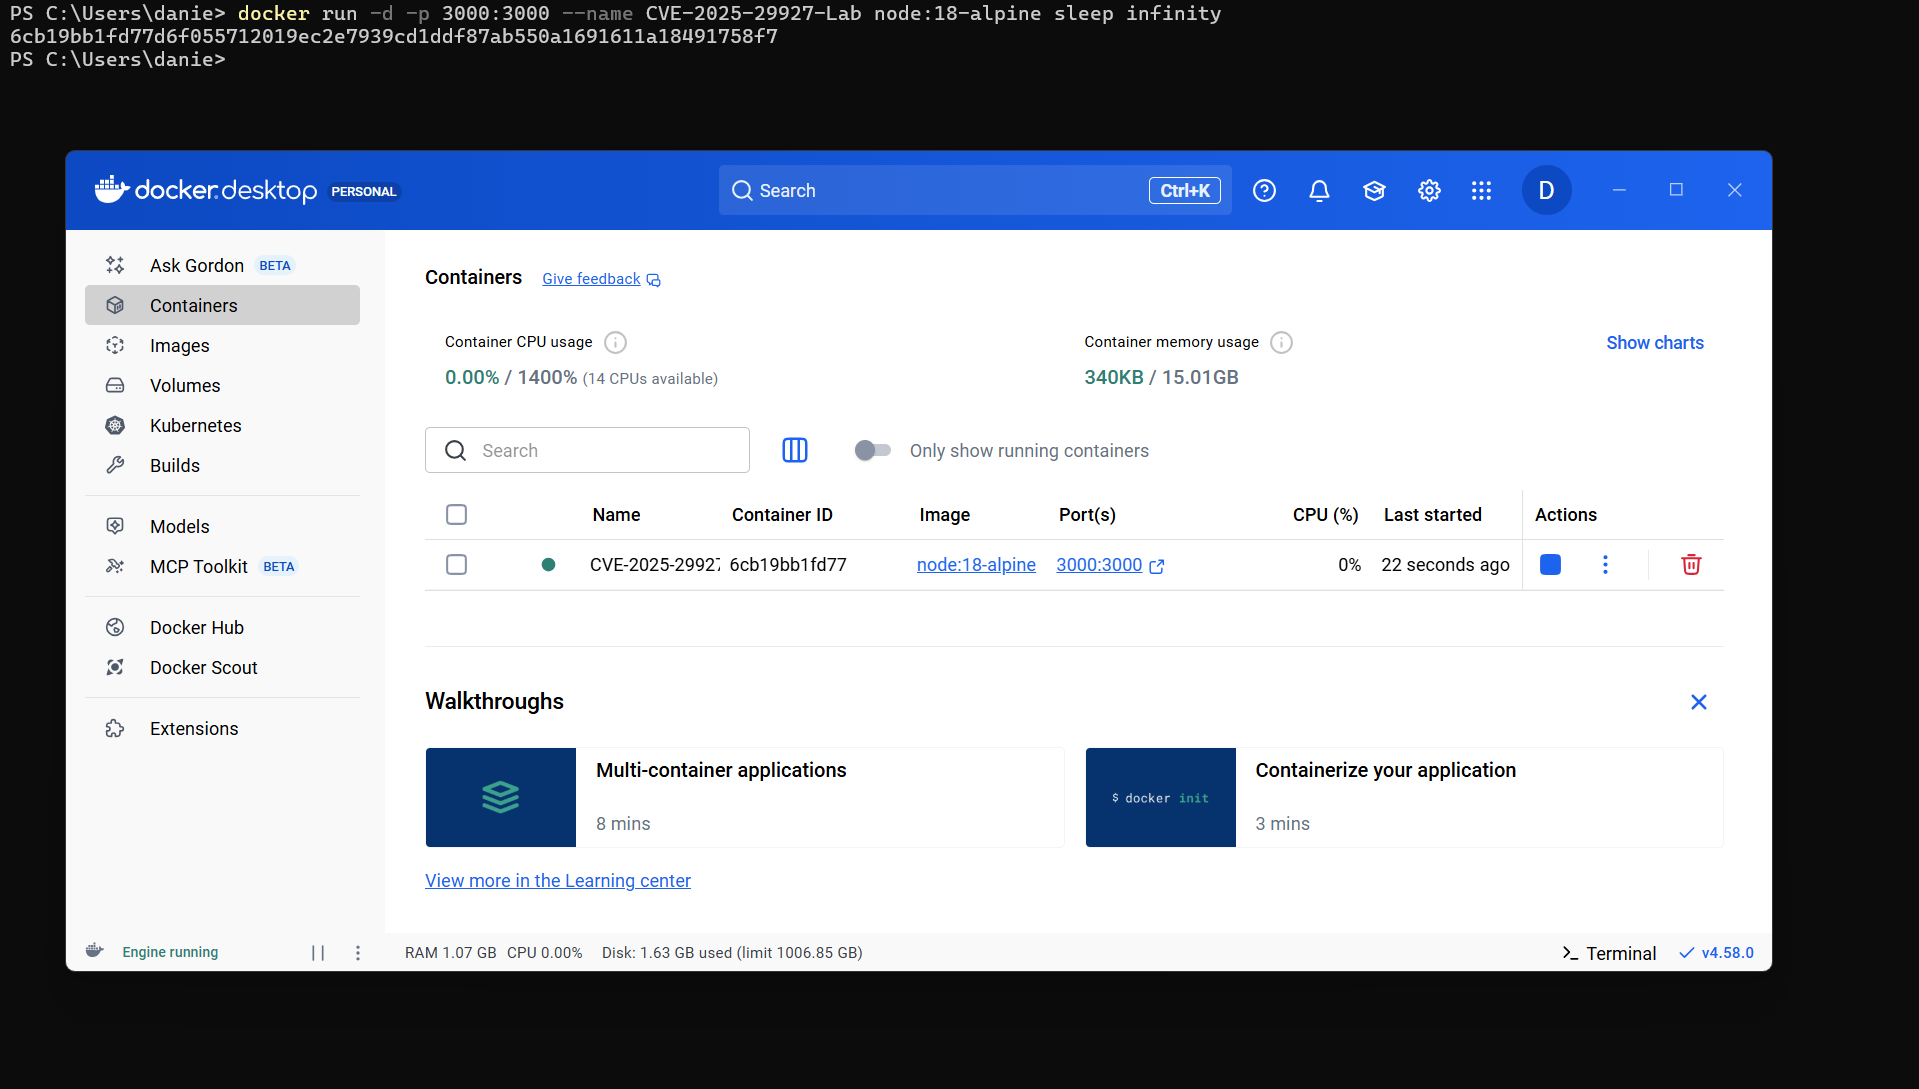
A Proof of Concept for CVE-2025-29927 demonstrating a middleware bypass in Next.js versions prior to 13.5.9

HikVision Auth Bypass CVE, tool is able to extract credentials, and take snapshots based on magic cookie or supplied credentials.

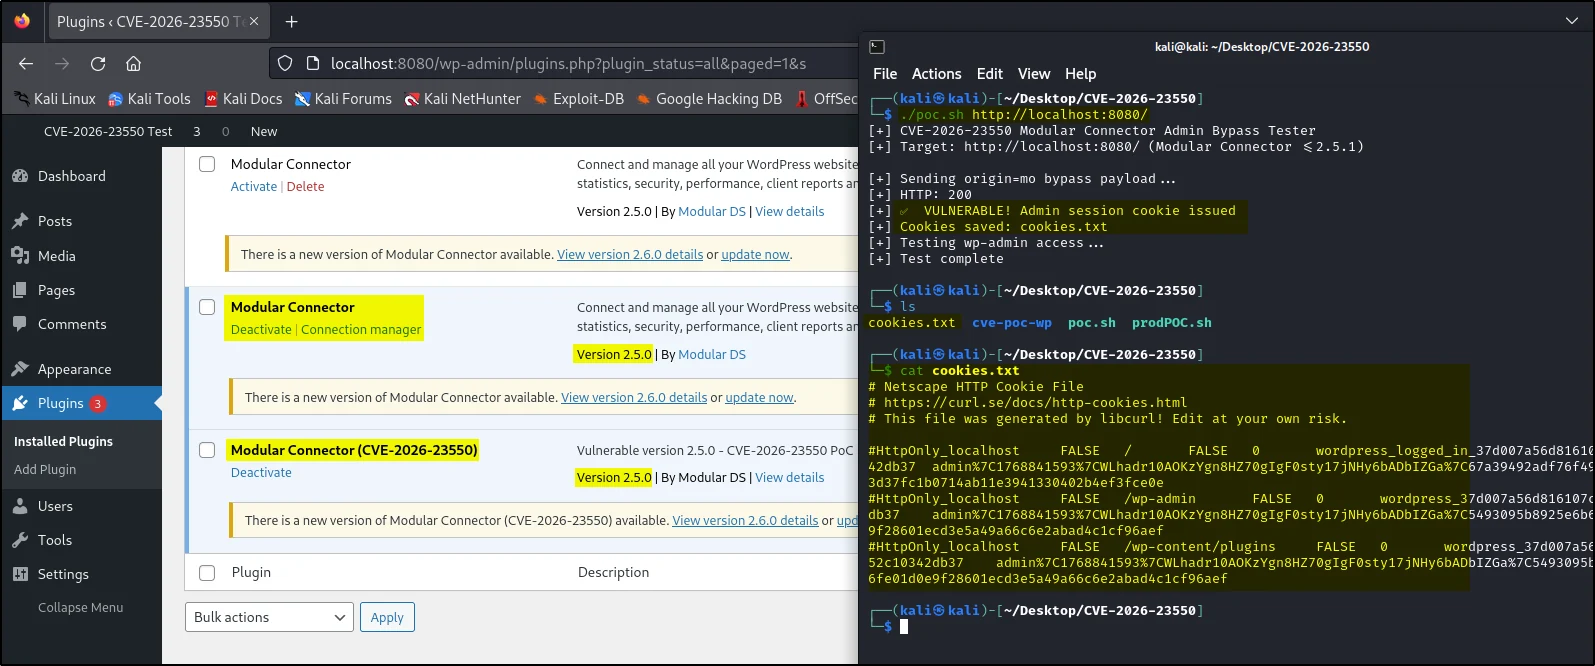
CVE-2026-23550 - Modular DS WordPress Plugin **Unauthenticated Admin Access**

Proof-of-concept exploit for CVE-2025-58434, demonstrating unauthenticated account takeover in Flowise via leaked password reset tokens. Includes…

Proof-of-concept for CVE-2022-2466 demonstrating unauthenticated GraphQL request context termination in Quarkus/SmallRye, bypassing authorization…

CVE-2017-7921 is a critical vulnerability (CVSS score: 9.8) affecting multiple Hikvision IP camera and DVR models, first disclosed in 2017. It stems…

Proof-of-Concept (PoC) for an authentication bypass vulnerability affecting applications using pac4j-jwt with JWE (JSON Web Encryption).

Relais 2FA <= 1.0 - Authentication Bypass

Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.

Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…

CVE-2025-40554 Exploitation

Proof-of-concept exploit for CVE-2023-47504 targeting Elementor WordPress plugin. Requires subscriber credentials and wp-config.php access to delete…

Exploitation de CVE-2022-26923