

CVE-2024-29296
 thaysolis/cve-2024-29296
CVE-2024-29296 - User enumeration on Portainer CE - 2.19.4
authenticationinformation-gatheringpenetration-testing+3
thaysolis/cve-2024-29296CVE-2024-29296 - User enumeration on Portainer CE - 2.19.4
 h4zaz/cve-2026-8794
Username Enumeration via Authentication Timing Side-Channel in PaperCut NG
 egcupcake/cupntlm-automated-exploit-for-cve-2025-33073-
cupntlm
 cappricio-securities/cve-2020-27838
CVE-2020-27838 - KeyCloak - Information Exposure
 ssh-mitm/ssh-mitm
Mirror moved — see GitHub and Codeberg
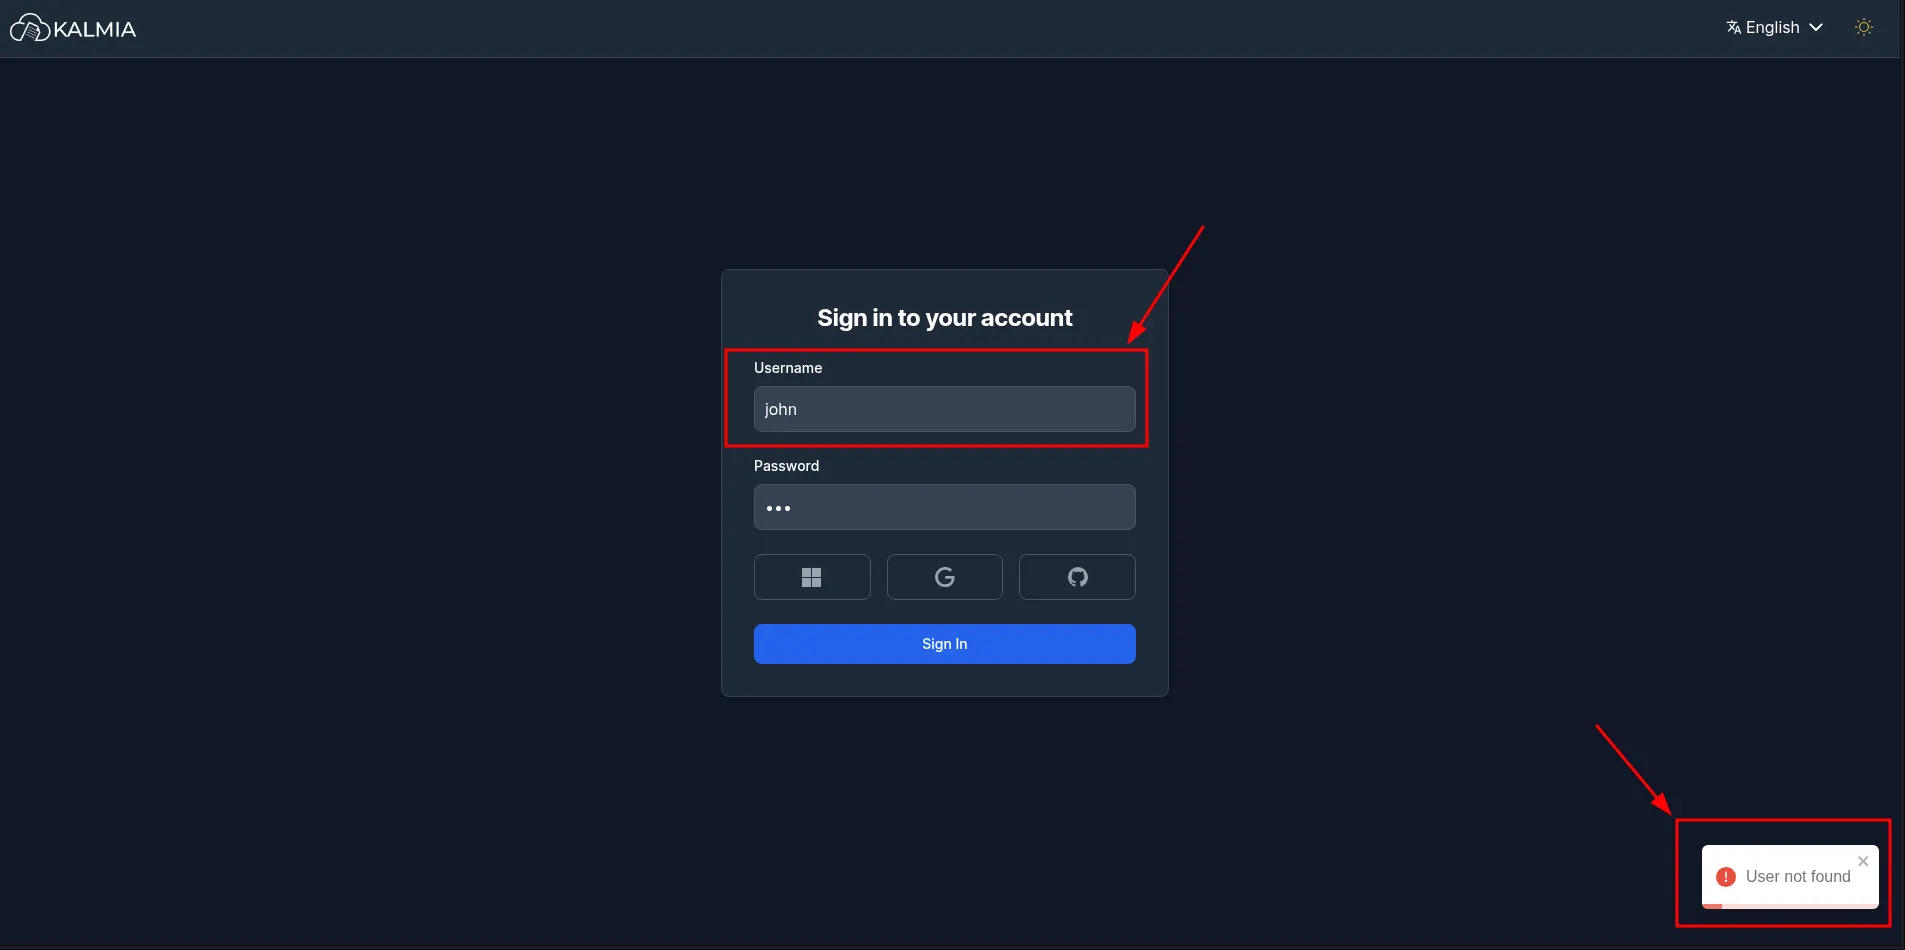 noxurge/cve-2025-65899
DifuseHQ Kalmia CMS version 0.2.0 is vulnerable to user enumeration through distinguishable error responses in the /kal-api/auth/jwt/create…
 obscura-cert/cve-2025-33073
Proof-of-concept tool that chains DNS injection, NTLM relay, and RPC-based coercion to test authentication relay paths in Windows Active Directory…
 curtishoughton/cve-2025-20362-cisco-scanner
Safe Python scanner for CVE-2025-20362 (Cisco ASA/FTD WebVPN Authentication Bypass)
 t3slaa/cve-2024-55374
CVE-2024-55374
 remenis/cve-2025-56764
Username Enumeration in Trivision NC-227WF
 soy-oreocato/cve-2022-33679_checker
Lightweight Python checker that tests Active Directory credentials for exposure to CVE-2022-33679 (Kerberos AS-REP roast without pre-authentication).…
 arturo-b-cmu/cve-2016-20012
Python script for SSH username enumeration using timing-based analysis to identify valid accounts on a target server.
 0xsu3ks/cve-2023-1665
CVE-2023-1665 - Twake App
 lukaszstu/smartasset-ue-cve-2020-26526
It is possible to enumerate valid usernames on the login page.
 h3x0v3rl0rd/gmsa_dumper
Python utility that reads accessible gMSA password blobs from Active Directory and extracts plaintext passwords for use in security audits and red…
 spiderlabs/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 byt3bl33d3r/mitmf
Framework for Man-In-The-Middle attacks