webauthn_tpm_portable

Portable, hardware-backed WebAuthn credentials using TPM 2.0. Deterministic parent key derived from a master seed enables cross-device credential…

Portable, hardware-backed WebAuthn credentials using TPM 2.0. Deterministic parent key derived from a master seed enables cross-device credential…

Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…

CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…

Rust-based exploit generator for CVE-2026-29000, an authentication bypass in pac4j-jwt via alg:none JWT nested in JWE, automating JWKS retrieval and…

Local lab simulating CVE-2026-29000 JWT/JWE authentication bypass in pac4j-jwt. Provides login, token forging, and dashboard APIs for practicing web…

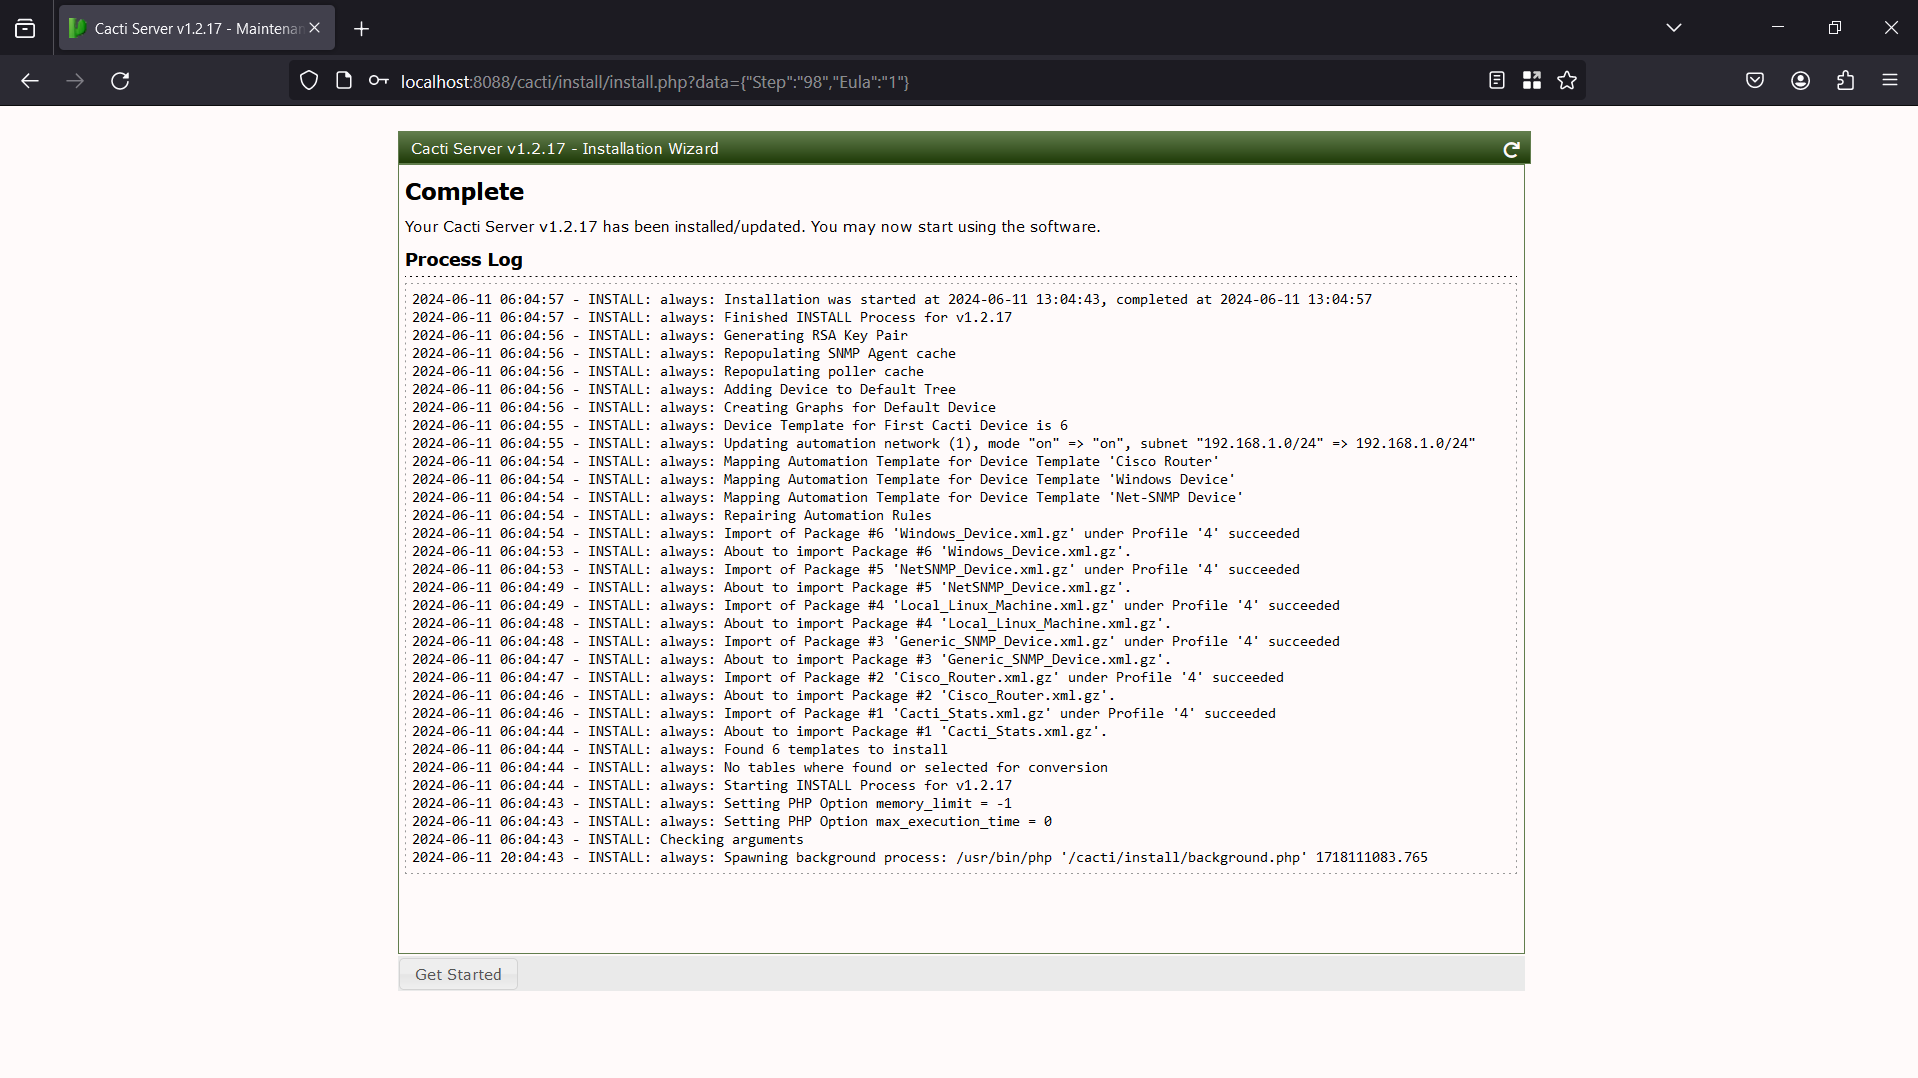
Step-by-step analysis of CVE-2022-46169: unauthenticated remote code execution in Cacti via authentication bypass and command injection, with Docker…

Bitwarden client apps (web, browser extension, desktop, and cli).

CVE-2025-0364: BigAnt Server RCE Exploit

CVE-2026-34348 - Draft or TODO

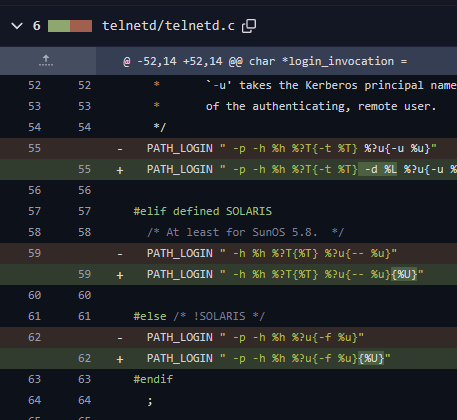
Vulnerability in GNU InetUtils telnetd Enables Remote Root Access

OWASP Passfault evaluates passwords and enforces password policy in a completely different way.

Critical unauthenticated kill chain leading to full RCE in FlowiseAI (CVE-2025-58434 + CVE-2025-59528)

Research on Next.js middleware vulnerability (CVE-2025-29927) allowing authorization bypass and potential exploits.