
CVE-2022-22845-Exploit
 omribaso/cve-2022-22845-exploit
Exploit for CVE-2022-22845 - Unauthenticated Admin Takeover On QXIP SIPCAPTURE Homer-App up to 1.4.27
authenticationexploitationpenetration-testing+2
2
omribaso/cve-2022-22845-exploitExploit for CVE-2022-22845 - Unauthenticated Admin Takeover On QXIP SIPCAPTURE Homer-App up to 1.4.27
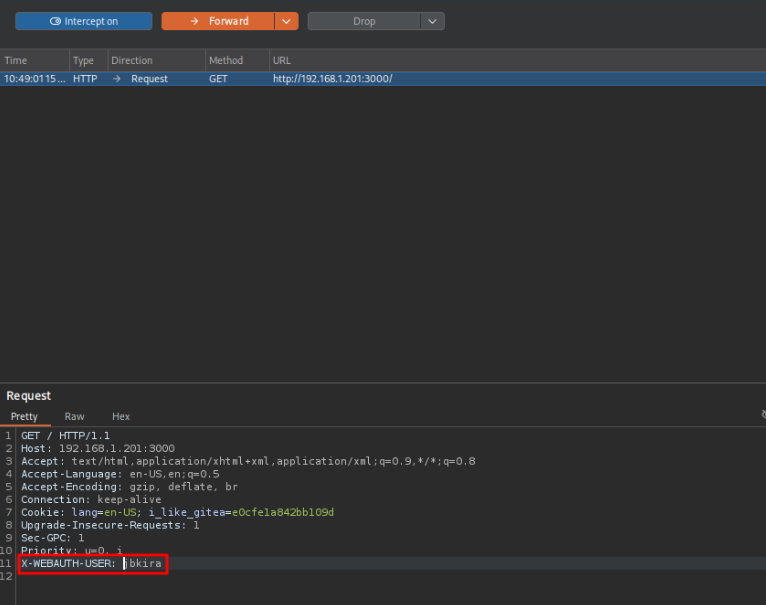 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 fa1c0n35/securabv-cve-2020-1472
Python script using Impacket to test for the Zerologon vulnerability (CVE-2020-1472) by attempting Netlogon authentication bypass on Domain…
 0xrixet/craftcms-poc-cve-2026-31266
Security research on Craft CMS authentication mechanism
 joaoaugustom/papercut-authentication_bypass_and_rce
This exploit is based on CVE-2023-27350 and was built upon the original exploit by horizon3ai and the Metasploit module.
 michaeladamgroberman/cve-2026-32646
CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
 4minx/cve-2024-8682
PoC exploit for CVE-2024-8682, enabling unauthenticated user registration on JNews WordPress themes via crafted AJAX requests.
 kirubel-cve/cve-2026-36959
Proof-of-concept exploit for CVE-2026-36959, a missing rate limiting vulnerability in U-SPEED Router firmware allowing brute-force attacks on the…
 oscerd/cve-2026-40022
Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths
 alessandrobertoldi/research
Published security research repository featuring academic papers on domain hijacking, 2FA bypass, and large-scale spoofing techniques, authored by…
 michaeladamgroberman/cve-2026-28766
CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 sh4den/cve-2025-48827
This repository contains a proof-of-concept exploit for CVE-2025-48827, a critical authentication bypass vulnerability affecting vBulletin…
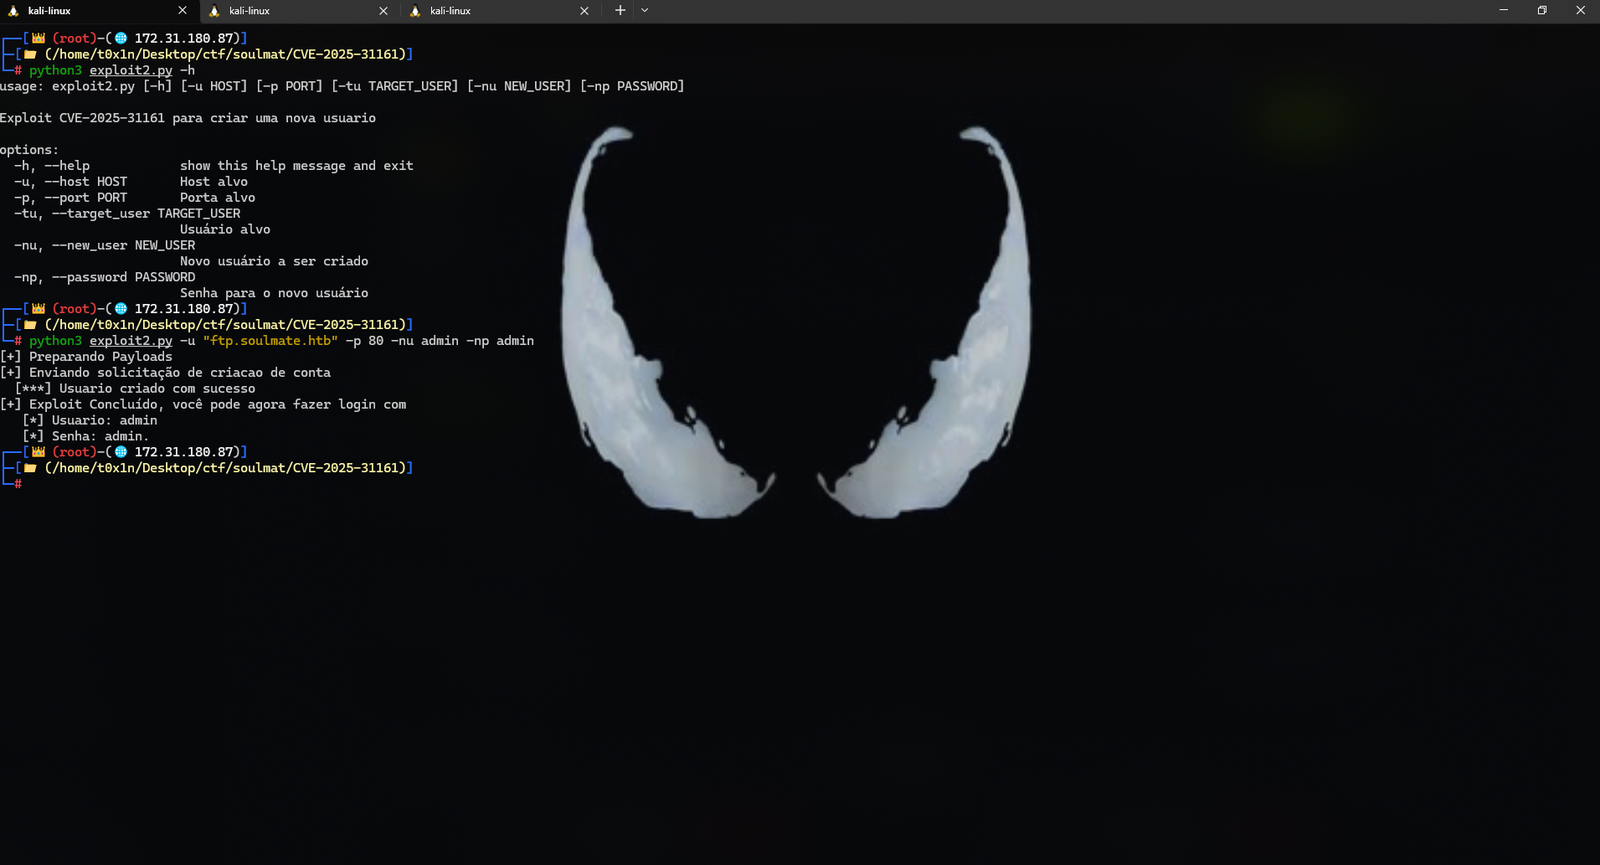 cesarbtakeda/cve-2025-31161
Exploit for CVE-2025-31161 with Python and C implementations, allowing authorized penetration testers to manipulate user accounts on target hosts.
 unteikyou/cve-2026-41940-authbypass-detector
Detection tool for cPanel/WHM CVE-2026-41940 (CRLF injection auth bypass). Verify vulnerability on servers you own or have permission to test. For…
 bimboxh4/cve-2025-66039_cve-2025-61675_cve-2025-61678_reepbx
This vulnerability allows both authenticated and unauthenticated remote attackers to execute remote code on vulnerable FreePBX instances. These…
 graysignal/apache-ofbiz-auth-bypass-and-rce-exploit-cve-2023-49070-cve-2023-51467
This exploit scans whether the provided target is vulnerable to CVE-2023-49070/CVE-2023-51467 and also exploits it depending on the choice of the…
 0xnehru/ssh_enum_vaild
A Bash script to enumerate valid SSH usernames using the CVE-2018-15473 vulnerability. It checks for valid usernames on an OpenSSH OpenSSH 7.2p2…