
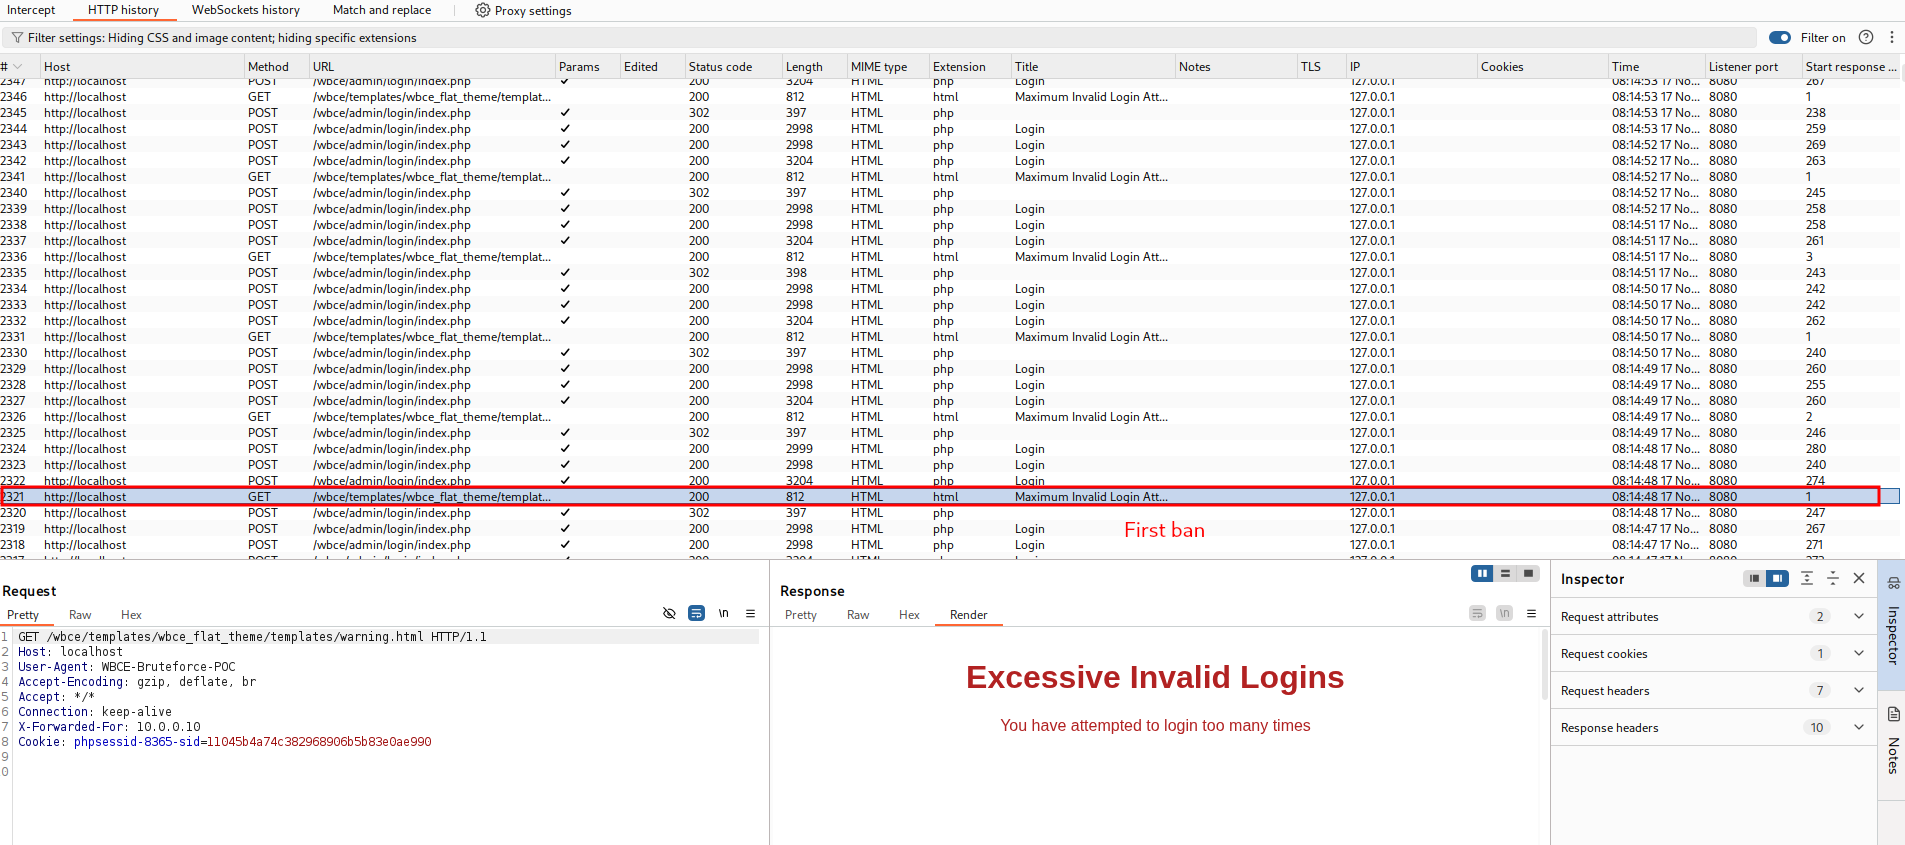
CVE-2025-66204
 lukasz-rybak/cve-2025-66204
Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…
authenticationeducationpapers-research+3
lukasz-rybak/cve-2025-66204Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…
 clayofgilgamesh/cve-2026-29000
CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…
 kartik2005221/cve-2025-58434-poc
Proof-of-concept exploit for CVE-2025-58434, demonstrating unauthenticated account takeover in Flowise via leaked password reset tokens. Includes…
 lucastran05/cve-2026-29000
Local lab simulating CVE-2026-29000 JWT/JWE authentication bypass in pac4j-jwt. Provides login, token forging, and dashboard APIs for practicing web…
 xxconi/cve-2026-5229
CVE-2026-5229: Form Notify Auth Bypass via LINE OAuth Callback (CVSS 9.8)

 rootdirective-sec/cve-2026-44338-lab
Docker-based lab demonstrating CVE-2026-44338 authentication bypass in PraisonAI's legacy Flask API. Includes vulnerable and patched services with…
 sercanokur/cve-2026-41940-cpanel-whm-verification-tool
Python verification script for CVE-2026-41940, an authentication bypass in cPanel & WHM, enabling authorized defensive validation and patching…
 eliasdekiniweek/cve-2022-26923
Exploitation de CVE-2022-26923
 smileyface101/crushftp-as2-bypass-research-cve-2025-54309
Research on CrushFTP AS2 authentication bypass allowing unauthenticated admin access. Includes PoC scripts, detection rules, and technical analysis…
 e-m-e-k-a/moniker-link-lab-setup
Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…
 idealzh/cve-2025-22235-demo
Demonstrates CVE-2025-22235 Spring Boot authentication bypass via EndpointRequest.to() misconfiguration. Includes environment setup, reproduction…
 enochgitgamefied/nextjs-cve-2025-29927
Intentionally vulnerable Next.js application demonstrating CVE-2025-29927 authentication bypass via middleware WAF evasion. Designed for security…
 ensimag-security/cve-2018-10933
Academic exploit implementation for CVE-2018-10933, a libssh authentication bypass vulnerability, with a detailed report and Shodan search…
 harydhk7/cve-2024-4358
Pre-authenticated remote code execution exploit for Telerik Report Server (CVE-2024-4358/CVE-2024-1800) with authentication bypass and…
 sajaljat/cve-2023-46449
Proof-of-concept exploit for CVE-2023-46449: IDOR in Sourcecodester inventory management system v1.0 password change function enabling remote account…