
CVE-2026-18963
 alt3kx/cve-2026-18963
Detection and verification tool for CVE-2026-18963, a Keycloak reset-credentials state bypass. Performs version fingerprinting, realm/client/user…
authenticationexploitationinformation-gathering+4
4
alt3kx/cve-2026-18963Detection and verification tool for CVE-2026-18963, a Keycloak reset-credentials state bypass. Performs version fingerprinting, realm/client/user…
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 huyvo2910/cve-2025-25749-weak-password-policy-in-hoteldruid-3.0.7
Proof-of-concept for CVE-2025-25749 demonstrating weak password policy in HotelDruid 3.0.7, with automated test scripts and mitigation…
 kxisxr/bash-script-cve-2019-17662
ThinVNC 1.0b1 is vulnerable to arbitrary file read, which leads to a compromise of the VNC server. The vulnerability exists even when authentication…
 rxerium/cve-2024-7593
Incorrect implementation of an authentication algorithm in Ivanti vTM other than versions 22.2R1 or 22.7R2 allows a remote unauthenticated attacker…
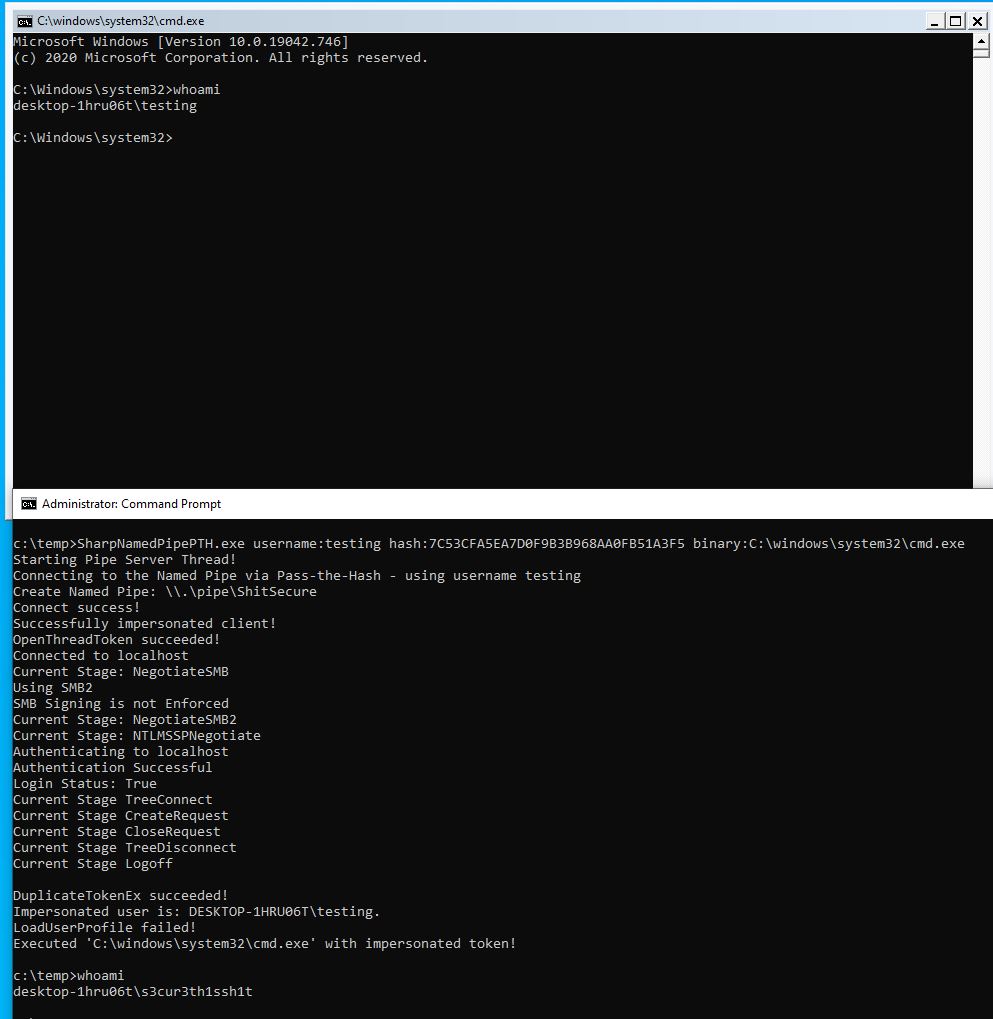 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
 pingport80/cve-2019-17240
This is the exploit of CVE-2019-17240.
 nxploited/cve-2025-13390
WP Directory Kit <= 1.4.4 - Authentication Bypass to Privilege Escalation via Account Takeover
 shinyseam/cve-2025-64513
PoC for CVE-2025-64513 — Milvus Proxy Authentication Bypass Vulnerability Batch scanner to verify unauthorized access and gather Milvus version,…

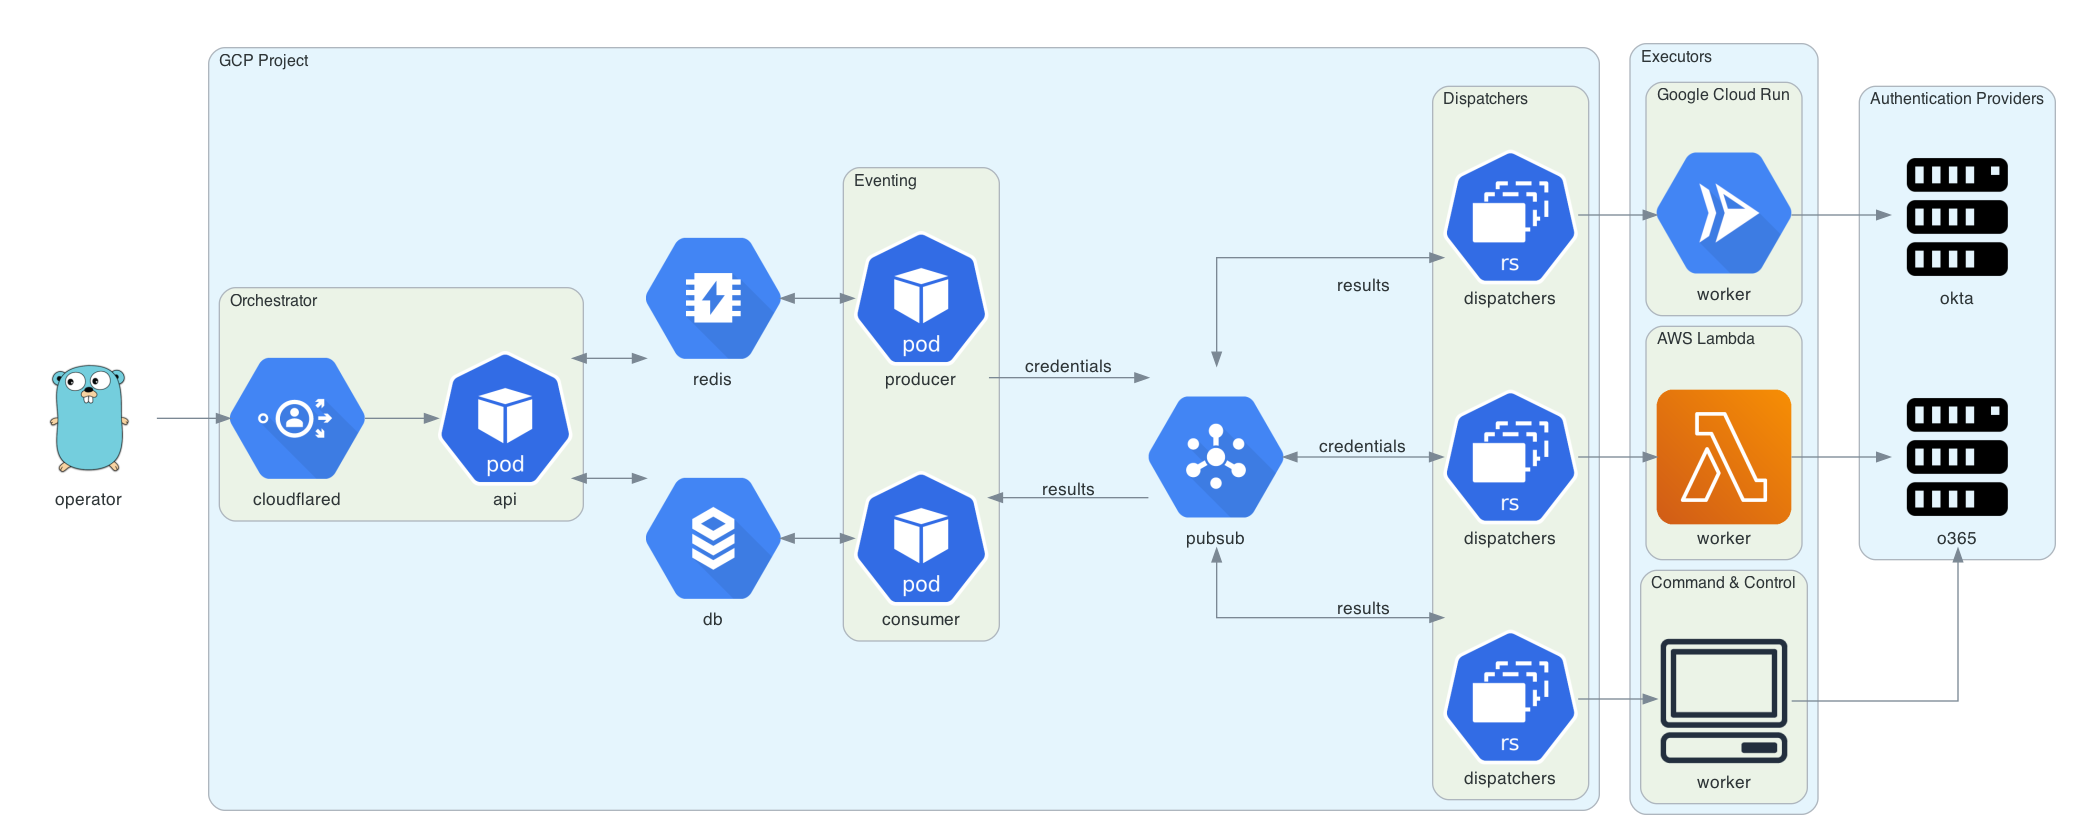 praetorian-inc/trident
automated password spraying tool
 hateshape/frevvomapexec
PoC Exploit for CVE-2018-8820
 v-jfanca/cve-2026-20833-rc4-kerberos
Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)
 bats3c/adcspwn
A tool to escalate privileges in an active directory network by coercing authenticate from machine accounts and relaying to the certificate service.
 optiv/knockknock
Enumerate valid users within Microsoft Teams and OneDrive with clean output.
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
 jfjallid/go-secdump
Tool to remotely dump secrets from the Windows registry
 g0ldengunsec/powerpriv
A Powershell implementation of PrivExchange designed to run under the current user's context