
sshamble
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
authenticationdefensive-toolsinformation-gathering+6
1.2k
runzeroinc/sshambleResearch tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
 apple/swift-nio-ssh
SwiftNIO SSH is a programmatic implementation of SSH using SwiftNIO
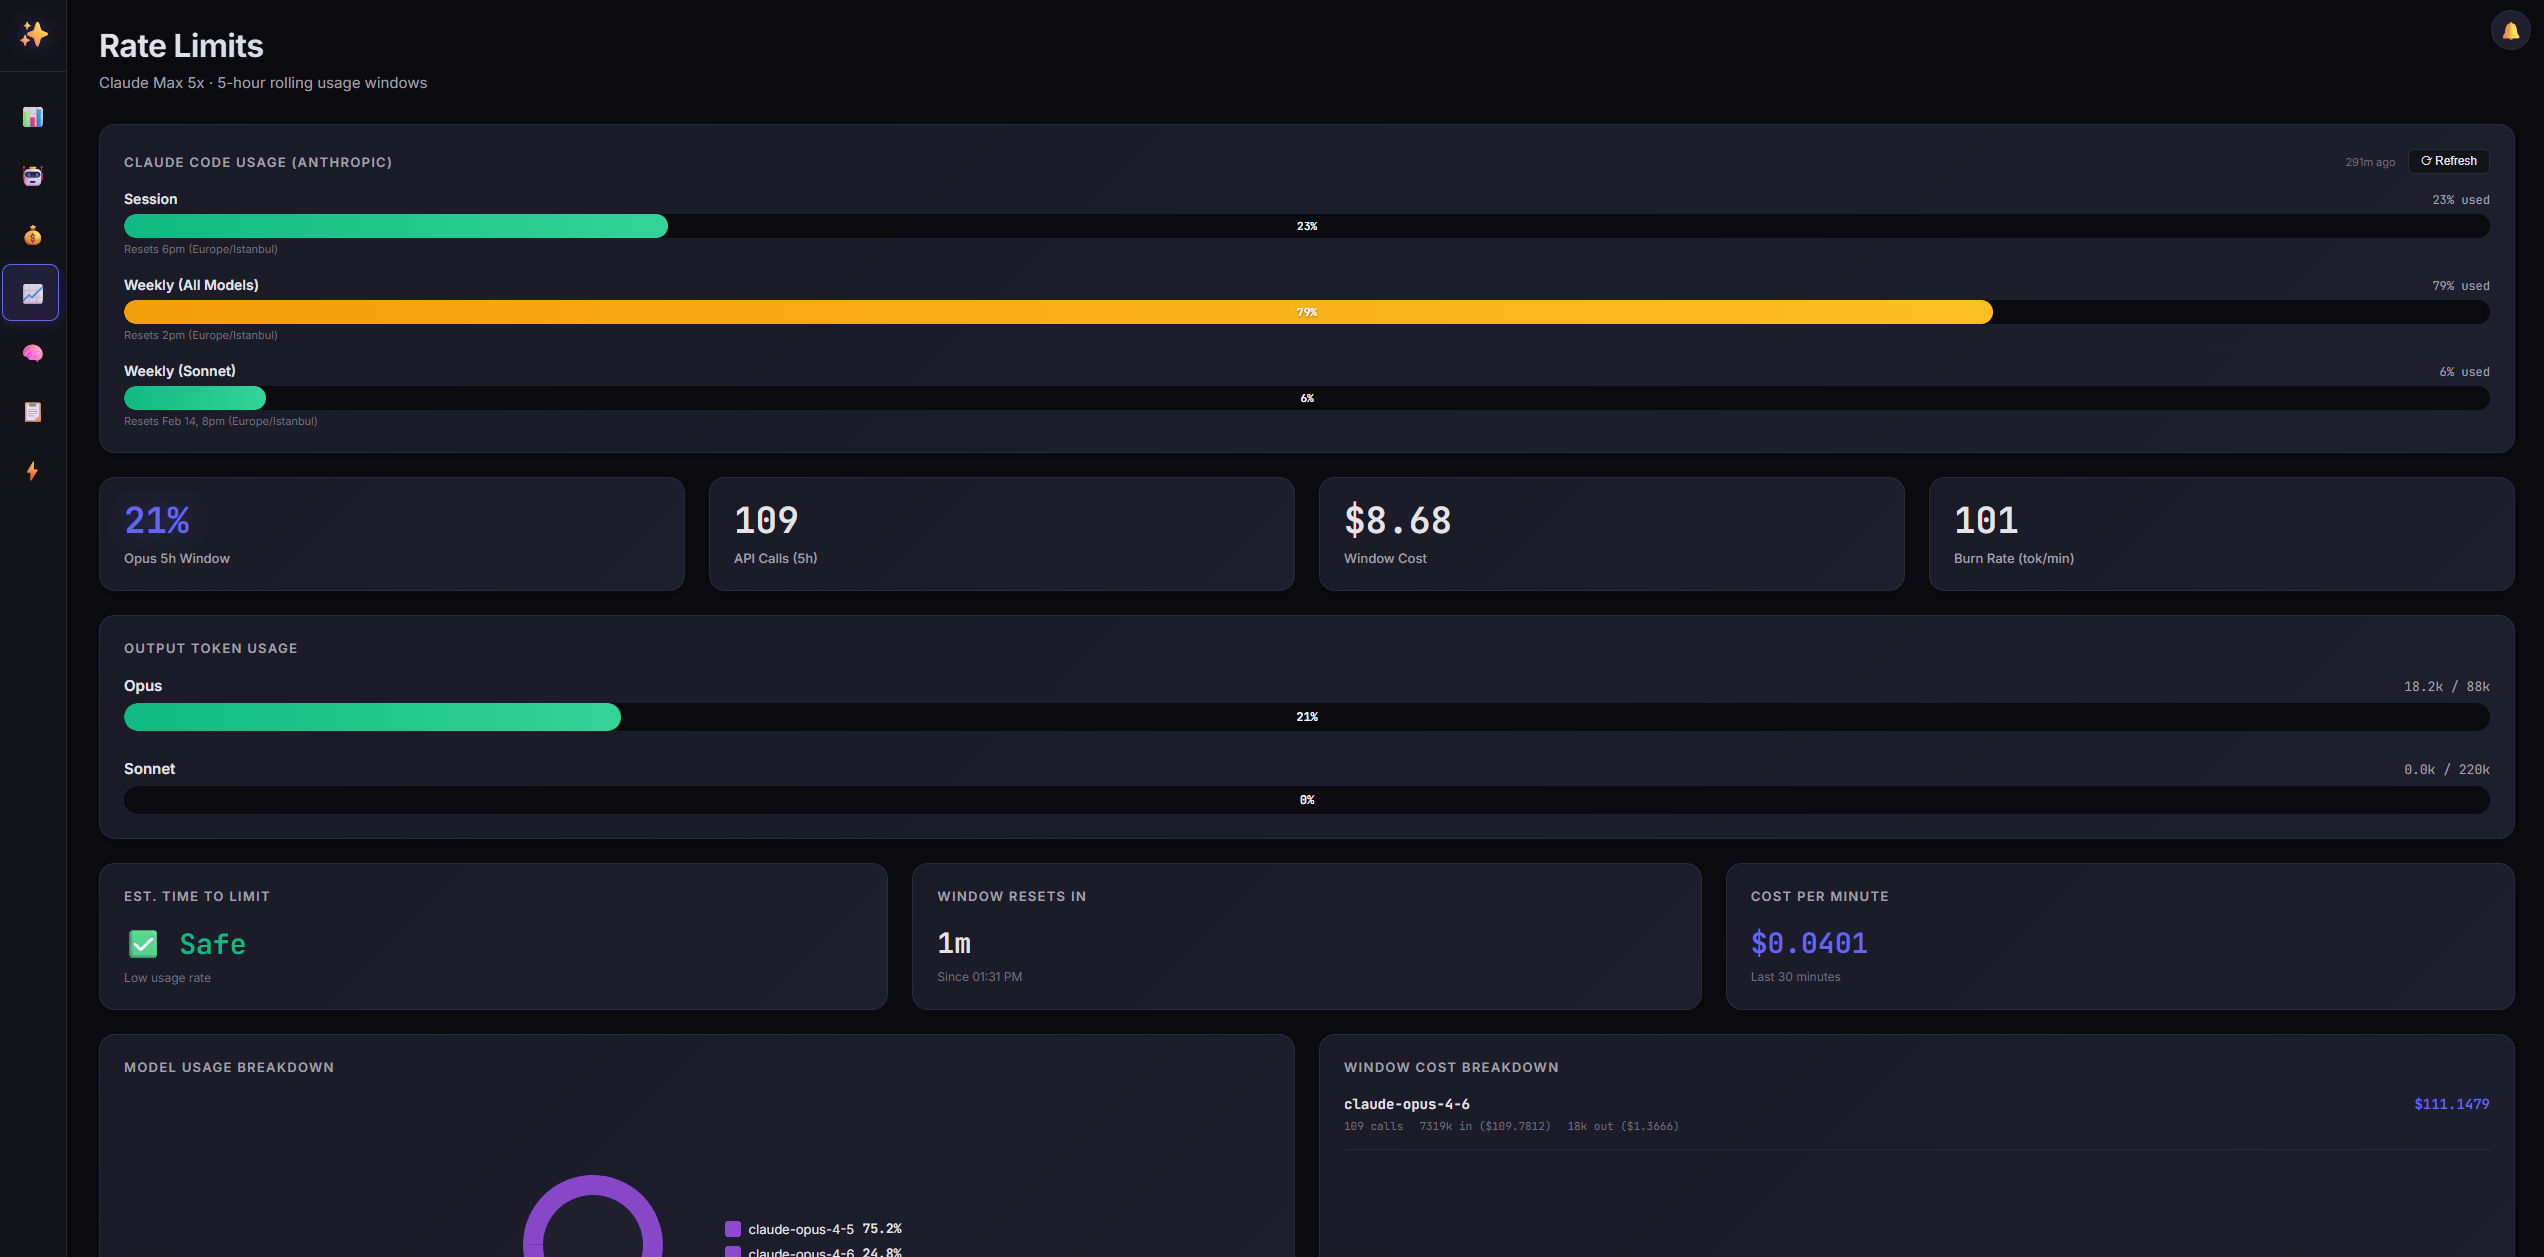 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
 wavvs/nanorobeus
COFF file (BOF) for managing Kerberos tickets.
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 kh4sh3i/cve-2022-23131
Python exploit for CVE-2022-23131 targeting Zabbix SAML SSO authentication bypass. Includes Shodan and FOFA dorks for vulnerable instance discovery.
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
 nel-droid/cve-2026-71206-poc
PoC: Shiori JWT CheckToken never re-validates account state (CVE-2026-71206, High 8.2)
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 remenis/cve-2025-63667
Vatilon-based IP camera firmwares issue Session-Id tokens without verifying credentials, allowing attackers to obtain sessions and retrieve plaintext…
 jfriedli/cve-2025-12028
Proof-of-concept exploit for CVE-2025-12028 demonstrating CSRF-based OAuth token theft in WordPress IndieAuth plugin, enabling unauthorized API…
 anir0y/sonicwall-audit-toolkit
SonicWall security audit toolkit with vulnerable CTF lab (CVE-2021-20038, CVE-2024-53704)
 pervinzahidli/cve-2026-103977
Session-scoped TOTP rate limiting permits repeated verification attempts
 twwd/cve-2023-0264
A small PoC for the Keycloak vulnerability CVE-2023-0264
 shadowforge-cyber/cve-2026-76504-proof-of-concept
EUVD-2026-89950 Improper Handling of URL Encoding (Hex Encoding) (CWE-177)