

vibe-coding-security
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
ai-securityapi-securityauthentication+9
15
boxed-dev/vibe-coding-securityPre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 racerz-fighting/cve-2024-32113-poc
Apache OfBiz vulns
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
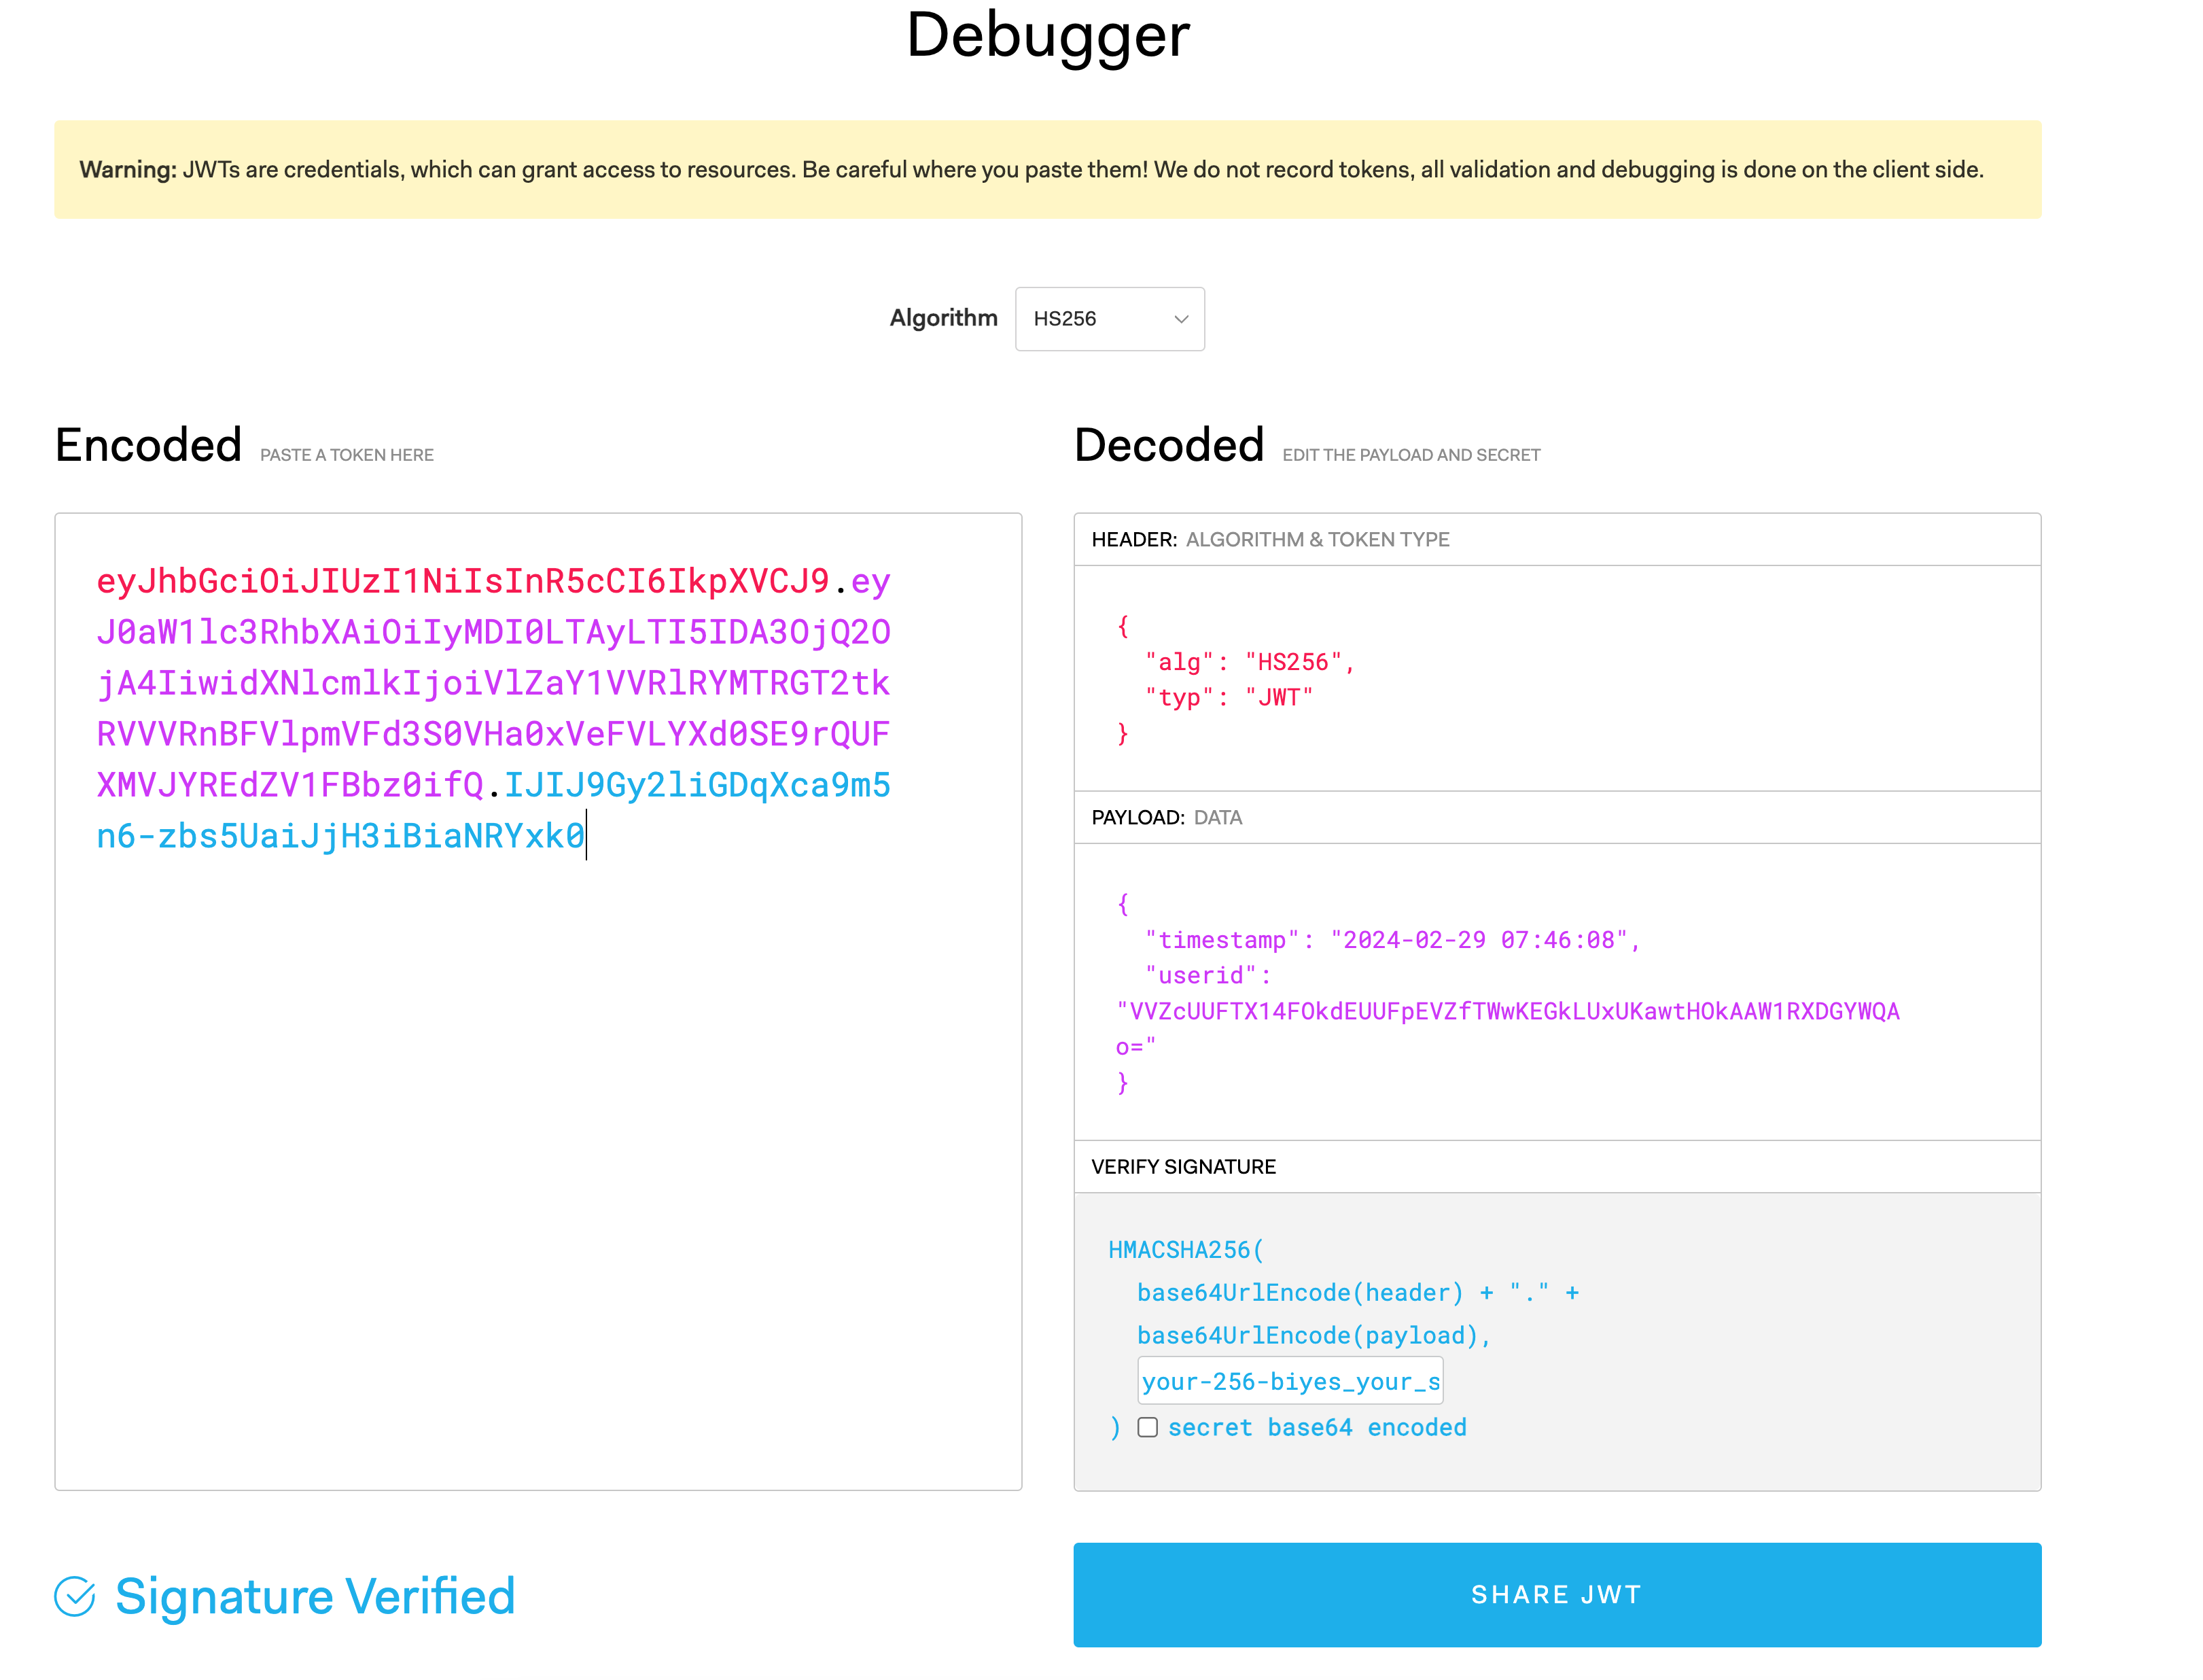 password123456/some-tweak-to-hide-jwt-payload-values
Lightweight Python library for obfuscating JWT payload values using XOR encryption with timestamp-based keys, preventing plaintext decoding of…
 hunt-benito/the-token-was-a-row-number-cve-2026-67602-phpipam-rest-api-authentication-bypass
Exploit and PoC for CVE-2026-67602, an authentication bypass in phpIPAM REST API via object-cache key collision, including a logic-level PoC and…
 isaca0315/cve-2026-44351-poc
Proof-of-concept for CVE-2026-44351, an authentication bypass in fast-jwt <6.2.4 where an empty HMAC key lets attackers forge arbitrary JWTs accepted…
 squeeze440/inference-gateway-poc
PoC — cross-origin requests reuse the configured provider API key in inference-gateway (GHSA-5293-fcm6-fh8v, CVE-2026-87009, CVSS 5.4).
 diegoarias008/cve-2026-20079-checker
Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…
 envincion1991-cmyk/cve-2026-51954
Vulnerability Research
 wildandeveloper/cve-2026-58231
Non-destructive detection and precondition-verification tool for CVE-2026-58231, probing SAP Commerce Cloud Data Hub endpoints, default OAuth…
 cyberency/cve-2025-6514
mcp-remote exposed to OS command injection
 supermagnum/galdralag-firmware
A cryptographic framework for Baochip-1x .
 twinson333/cve-2026-33032-scanner
Non-destructive vulnerability scanner for Nginx-UI MCP Endpoint Authentication Bypass (CVE-2026-33032)
 s3v3n-jg/cve-2026-76460
Educational Flask lab simulating CVE-2026-76460 authentication bypass, with vulnerable, secure, and strict modes plus a PoC exploit script and…
 mreza-en/cve-2021-21994_poc
Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.
 squeeze440/cve-2026-73519-wolfstack-poc
PoC for CVE-2026-73519 - WolfStack hardcoded cluster secret leads to unauthenticated RCE (CVSS 9.8)
 biitts/cve-2026-49230-apisix-jwe-decrypt-auth-bypass
PoC for CVE-2026-49230: Apache APISIX jwe-decrypt authentication bypass (missing AES-GCM tag validation, CWE-354, CVSS 9.1)
 cosignet/sdk
Thin TypeScript + zero-dep Python client and recipes to gate high-risk actions behind a payload-bound passkey approval.