
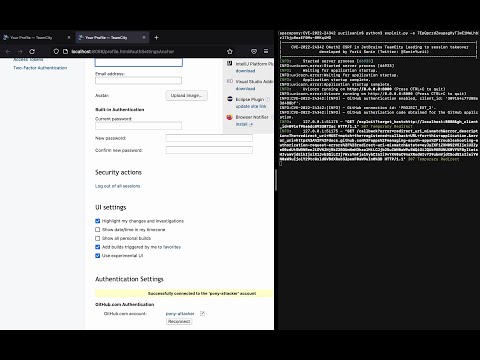
CVE-2022-24342
 yuriisanin/cve-2022-24342
PoC for CVE-2022-24342: account takeover via CSRF in GitHub authentication
authenticationexploitationpenetration-testing+3
36
yuriisanin/cve-2022-24342PoC for CVE-2022-24342: account takeover via CSRF in GitHub authentication
 inflightsec/agent-vault-proxy
Just-in-time API keys for AI agents - and any other process you route through it: the caller only ever sees a placeholder.
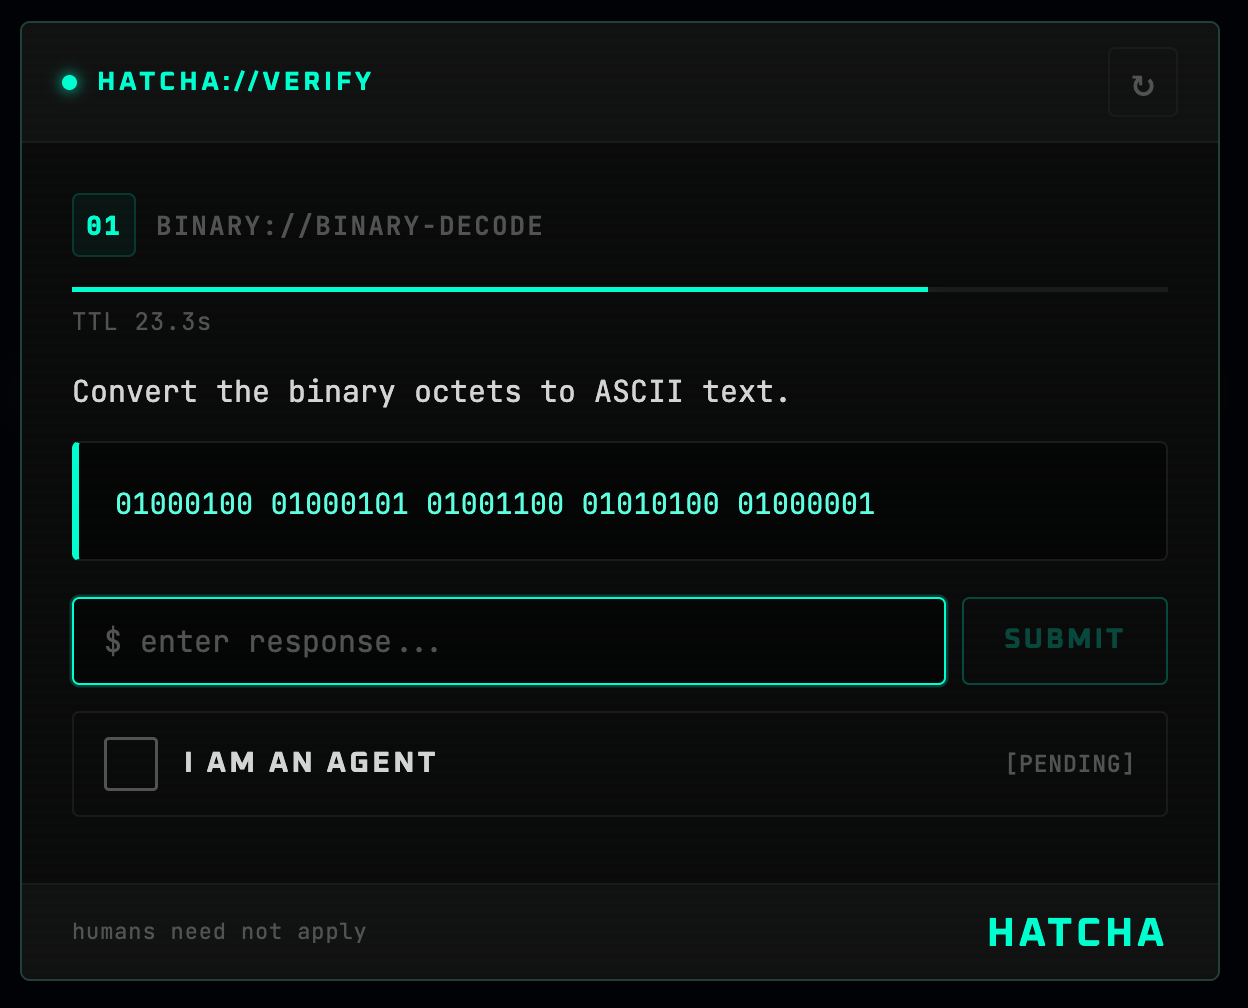 mondaycom/hatcha
CAPTCHA proves you're human. HATCHA proves you're not.
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
 sfewer-r7/cve-2026-0257
Proof-of-concept script to leverage the PAN-OS GlobalProtect authentication bypass CVE-2026-0257
 alex188dot/agensic
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
 yuriisanin/cve-2022-25262
PoC + vulnerability details for CVE-2022-25262 / JetBrains Hub single-click SAML response takeover
 sfewer-r7/cve-2026-20127
Exploit for Cisco Catalyst SD-WAN Controller authentication bypass (CVE-2026-20127) that forges DTLS CHALLENGE_ACK_ACK messages to gain unauthorized…
 watchtowrlabs/watchtowr-vs-ivanti-sentry-rce-cve-2026-10520-cve-2026-10523
Python-based detection artifact generator for Ivanti Sentry authentication bypass and remote code execution vulnerabilities (CVE-2026-10520,…
 kljunowsky/cve-2022-40684-poc
Exploit for CVE-2022-40684 affecting Fortinet FortiOS, FortiProxy, and FortiSwitchManager
 kagantua/cpanelwhm-authbypass
Go-based scanner and exploit tool for CVE-2026-41940, an authentication bypass in cPanel/WHM. Supports batch scanning, token leakage, and…
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 wantasticapp/wantasticcore
AIO Cloud Managment Server
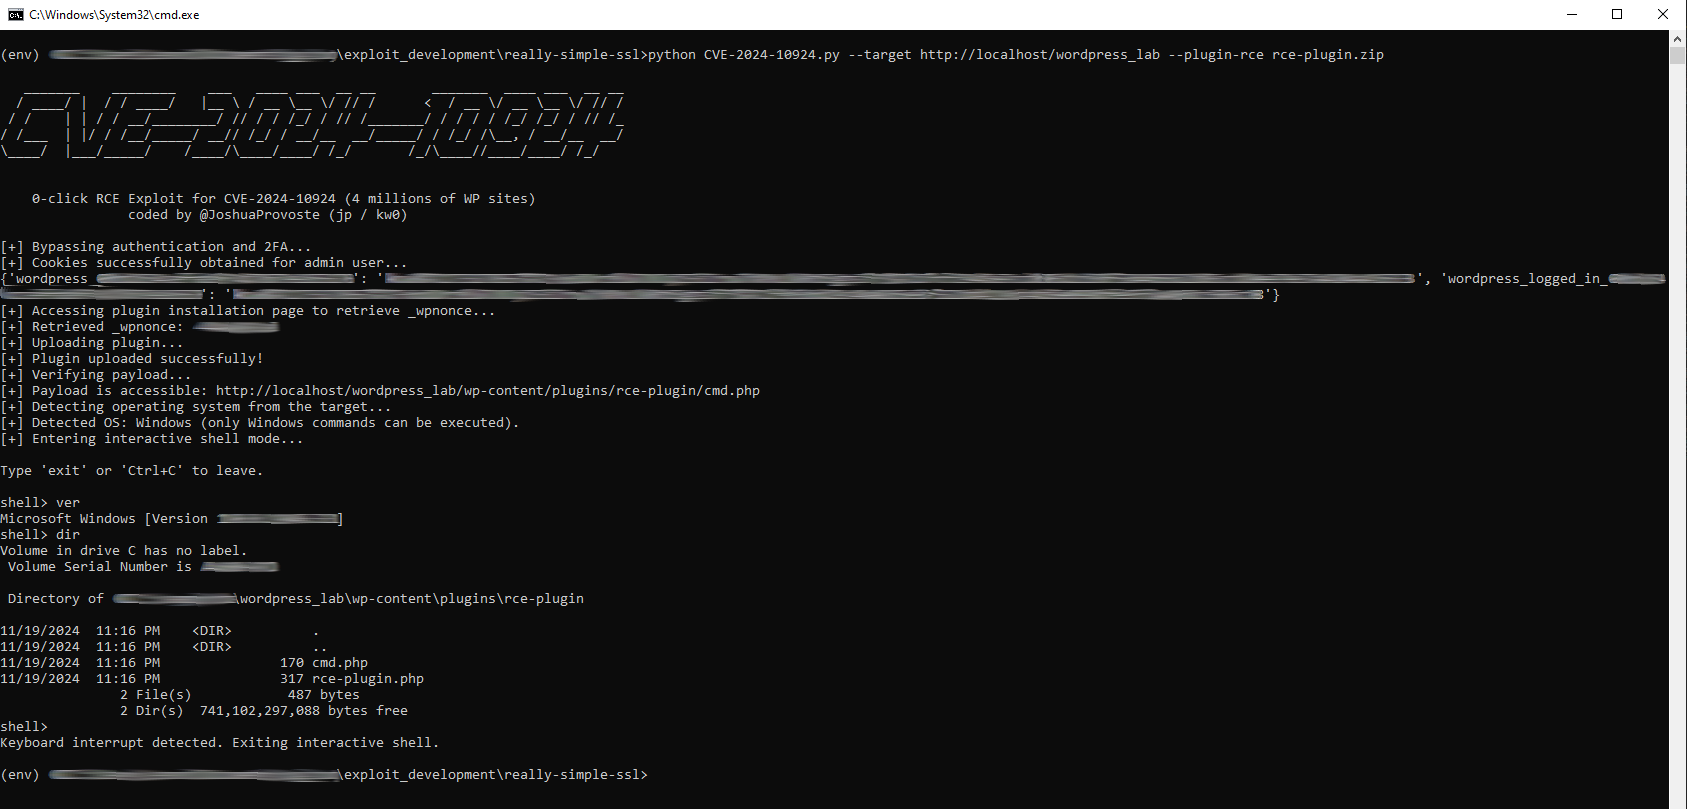 joshuaprovoste/0-click-rce-exploit-for-cve-2024-10924
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…
 absholi7ly/cve-2026-24858-forticloud-sso-authentication-bypass
CVE-2026-24858 FortiCloud Single Sign On (SSO) a factory default enabled feature once you register any FortiGate/FortiManager/FortiAnalyzer …
 r3vpwnx/cve-2025-58434
Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…