
 zux0x3a/adfly
active directory query tool using LDAP Protocol , helps red teamer / penetration testers to validate users credentials , retrieve information about…
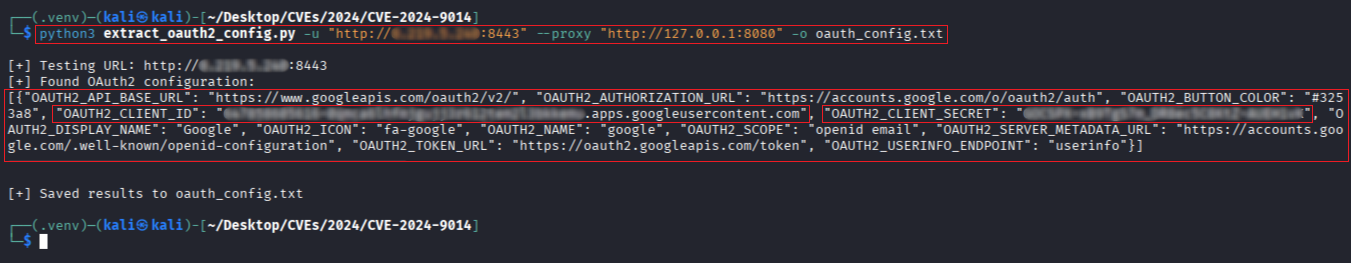 r0otk3r/cve-2024-9014
Scripts to detect and exploit CVE-2024-9014 OAuth2 authentication bypass in pgAdmin 4, including vulnerability checking and OAuth2 configuration…
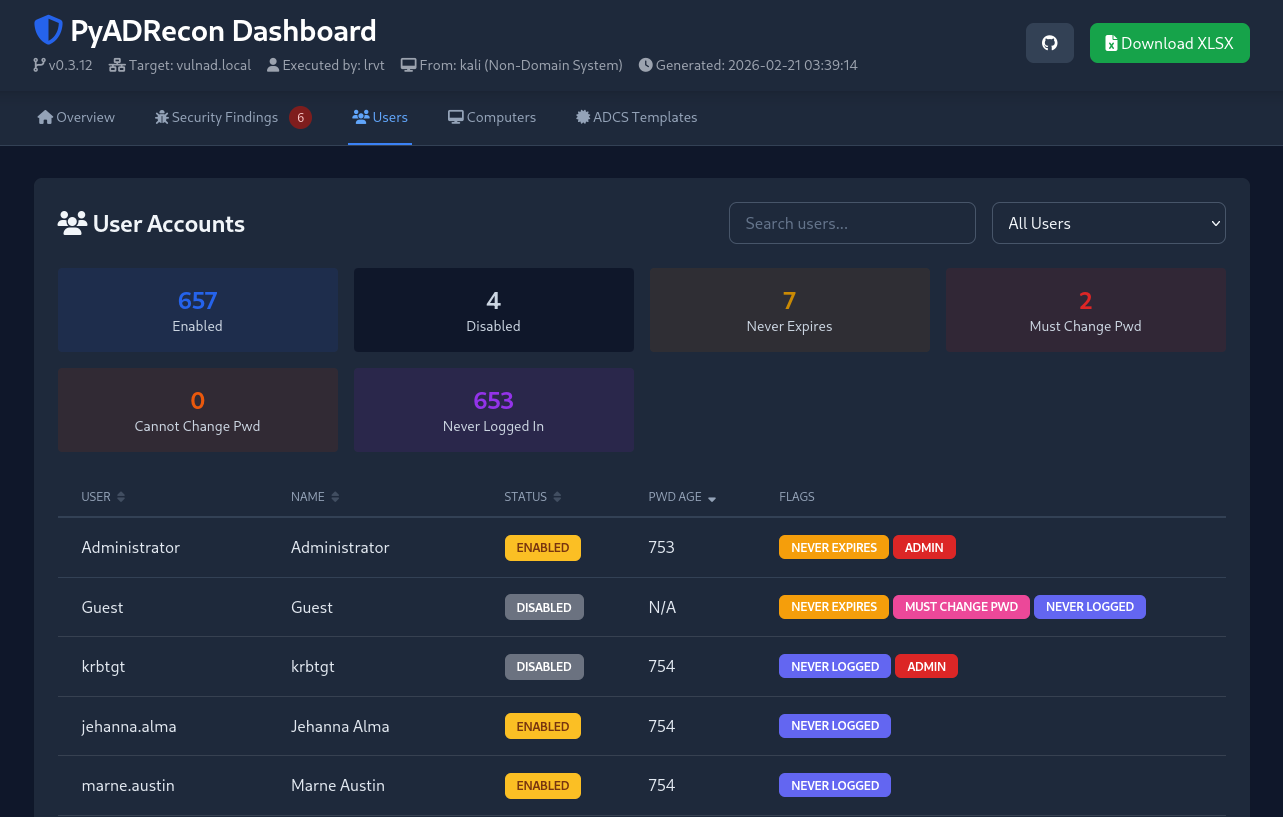 l4rm4nd/pyadrecon
Python3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…
 murrez/cve-2026-19660
Python PoC scanner and exploit for CVE-2026-14378, a pre-auth administrator session takeover in the DevKit Pro WordPress plugin via forged…
 skelsec/kerberoast
Pure-Python toolkit for Kerberos-based attacks including ASREProast, SPNroast, and LDAP enumeration to identify and exploit vulnerable Active…
 dirkjanm/mitm6
Exploits Windows IPv6 default configuration to spoof DNS via DHCPv6, redirecting victim traffic for credential relaying and man-in-the-middle attacks…
 kh4sh3i/cve-2022-23131
Python exploit for CVE-2022-23131 targeting Zabbix SAML SSO authentication bypass. Includes Shodan and FOFA dorks for vulnerable instance discovery.
 aix567/c-a-s
C.A.S-Exploit — Python-based security research and proof-of-concept toolkit for CVE-2017-5689 (Intel AMT authentication bypass), featuring Shodan…
 ssh-mitm/ssh-mitm
Mirror moved — see GitHub and Codeberg
 optiv/knockknock
Enumerate valid users within Microsoft Teams and OneDrive with clean output.
 mgeeky/azurert
AzureRT - A Powershell module implementing various Azure Red Team tactics
 pshlyundin/ldap_shell
Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…
 zildanz/cve-2026-41940
Mass authentication bypass exploit for CVE-2026-41940 with single-target and batch scanning modes. Automates password-based bypass testing across…
 grayxploit/cve-2026-0257
Automated vulnerability scanner for CVE-2026-0257 (PAN-OS GlobalProtect Authentication Bypass) with TLS certificate enumeration, authentication…
 keraattin/cve-2026-35616
Detection toolkit for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Includes Python scanner and Nmap NSE script for identifying…
 h3x0v3rl0rd/gmsa_dumper
Python utility that reads accessible gMSA password blobs from Active Directory and extracts plaintext passwords for use in security audits and red…
 notitssixtyn3in/cve-2025-4162029
Security advisory detailing a critical authentication vulnerability (CVE-2025-4162029) in Copilot, enabling unauthorized account access via user ID…