
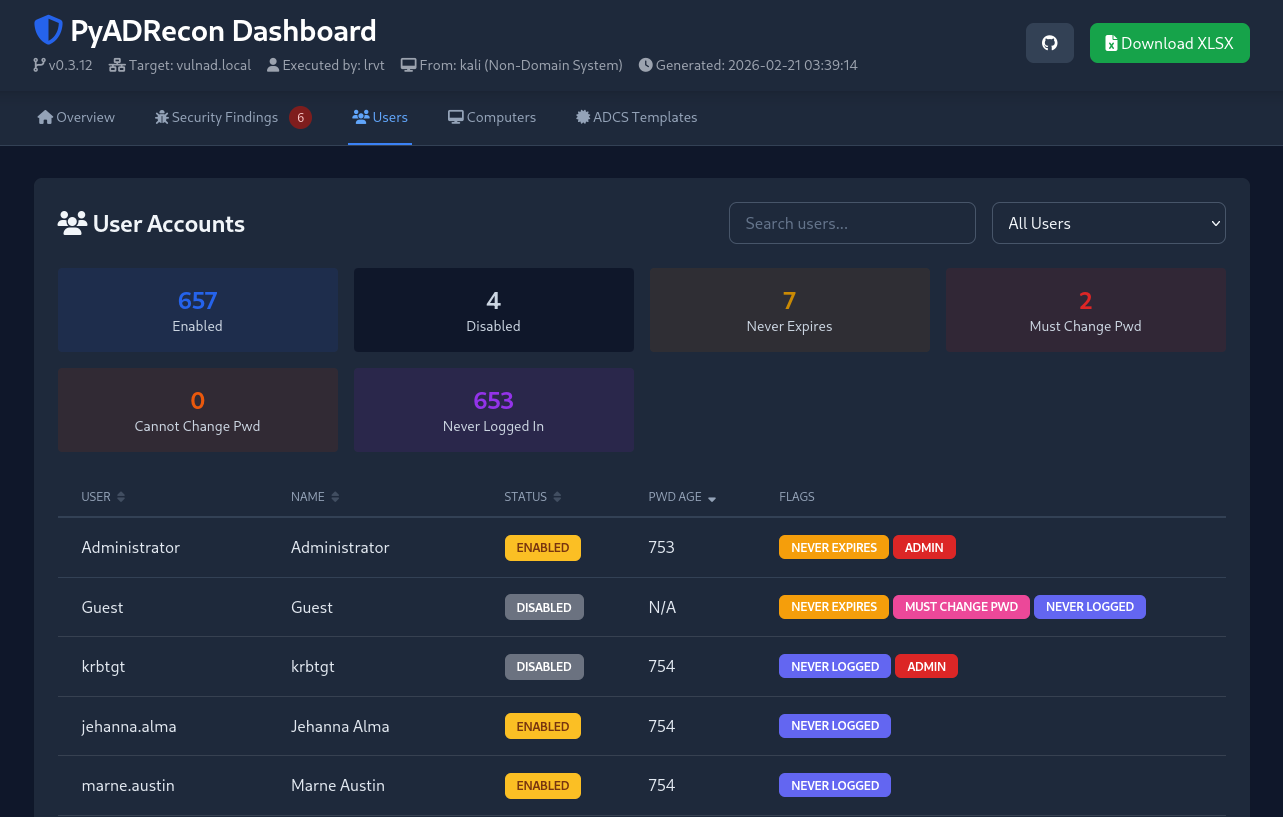
PyADRecon
 l4rm4nd/pyadrecon
Python3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…
authenticationinformation-gatheringpenetration-testing+4
68
l4rm4nd/pyadreconPython3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…
 akefallonitis/larac2shell
Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 e-m-e-k-a/moniker-link-lab-setup
Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…
 squeeze440/linux-entra-sso-poc
PoC — origin validation error enabling Entra ID PRT SSO cookie exfiltration in linux-entra-sso (GHSA-g9vc-5j77-f2cm, CVE-2026-87005, CVSS 5.3).
 fadidevv/clawdguard
🦞 Security hardening patch for Clawdbot/Moltbot. Detects and fixes exposed gateways automatically.
 bugch3ck/imposter
Proof of concept for CVE-2015-0006. Fixed in MS15-005 https://docs.microsoft.com/en-us/security-updates/SecurityBulletins/2015/ms15-005 .
 grayxploit/cve-2026-0257
Automated vulnerability scanner for CVE-2026-0257 (PAN-OS GlobalProtect Authentication Bypass) with TLS certificate enumeration, authentication…
 ull0a/cve-2026-50751
Bypass de autenticación por certificado en la VPN Remote-Access de Check Point (IKEv1).
 chenjp/cve-2026-29145-tester
This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.
 sancliffe/cve-2026-29145-tester
This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.
 lucastran05/cve-2026-29000
Local lab simulating CVE-2026-29000 JWT/JWE authentication bypass in pac4j-jwt. Provides login, token forging, and dashboard APIs for practicing web…
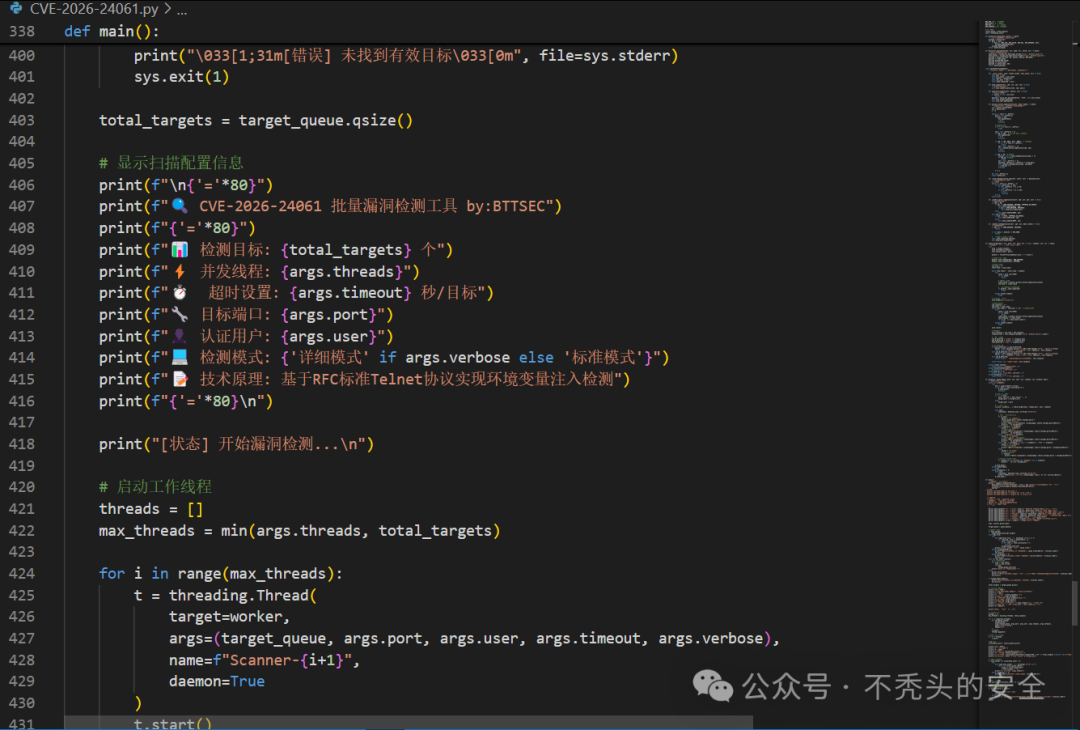 my0723/gnu-inetutils-telnet-cve-2026-24061-
GNU Inetutils telnet远程认证绕过漏洞(CVE-2026-24061),该漏洞源于 GNU Inetutils telnetd 组件中对环境变量处理不当,攻击者可利用该漏洞,通过构造恶意的 USER 环境变量并发送至受影响的 telnet…
 aperocky/bepr
A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.
 1872892142/jboss-autopwn-1
JBoss Autopwn as featured at BlackHat Europe 2010 - this version incorporates CVE-2010-0738 the JBoss authentication bypass VERB manipulation…
 eynaexp/cve-2024-27198-poc
proof-of-concept mass scanner targeting JetBrains TeamCity instances affected by CVE-2024-27198
 0xnehru/ssh_enum_vaild
A Bash script to enumerate valid SSH usernames using the CVE-2018-15473 vulnerability. It checks for valid usernames on an OpenSSH OpenSSH 7.2p2…
 hd0x01/cve-2026-24061-nse
The script performs a full Telnet negotiation mirroring the exact byte sequence of a real telnet -a client session.