
CVE-2026-8181
 zycoder0day/cve-2026-8181
CVE-2026-8181 - Burst Statistics 3.4.0-3.4.1.1 Unauthenticated Authentication Bypass to Admin Account Takeover | Proof of Concept
authenticationctfeducation+4
6
zycoder0day/cve-2026-8181CVE-2026-8181 - Burst Statistics 3.4.0-3.4.1.1 Unauthenticated Authentication Bypass to Admin Account Takeover | Proof of Concept
 christian93111/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 chybeta/cve-2017-11427-demo
The Demo for CVE-2017-11427
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
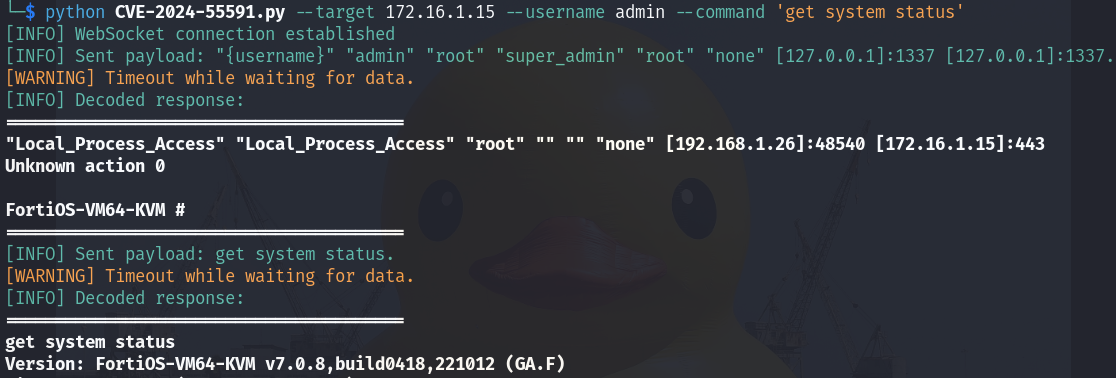 virus-or-not/cve-2024-55591
An Authentication Bypass Using an Alternate Path or Channel vulnerability [CWE-288] affecting FortiOS and FortiProxy may allow a remote attacker to…
 geniuszly/gencrushsstiexploit
is a PoC for CVE-2024-4040 tool for exploiting the SSTI vulnerability in CrushFTP
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 strobes-security/nextjs-vulnerable-app
CVE-2025-29927 lab
 xaoczenon/cve-2026-20896
this is a modified POC of rz1027 for CVE-2026-20896
 j4ck3lsyn-gen2/cve-2026-48558
SimpleHelp OIDC Authentication Bypass PoC
 muhammad-usama-sardar/intra-handshake-fail
Early Attestation Considered Very Harmful (CVE-2026-92701, CVE-2026-92702, CVE-2026-33697, and more to come)
 exfil0/cve-2025-59718-poc
Fortinet announced two closely related authentication‑bypass vulnerabilities on 9 December 2025. Both flaws involve improper verification of…
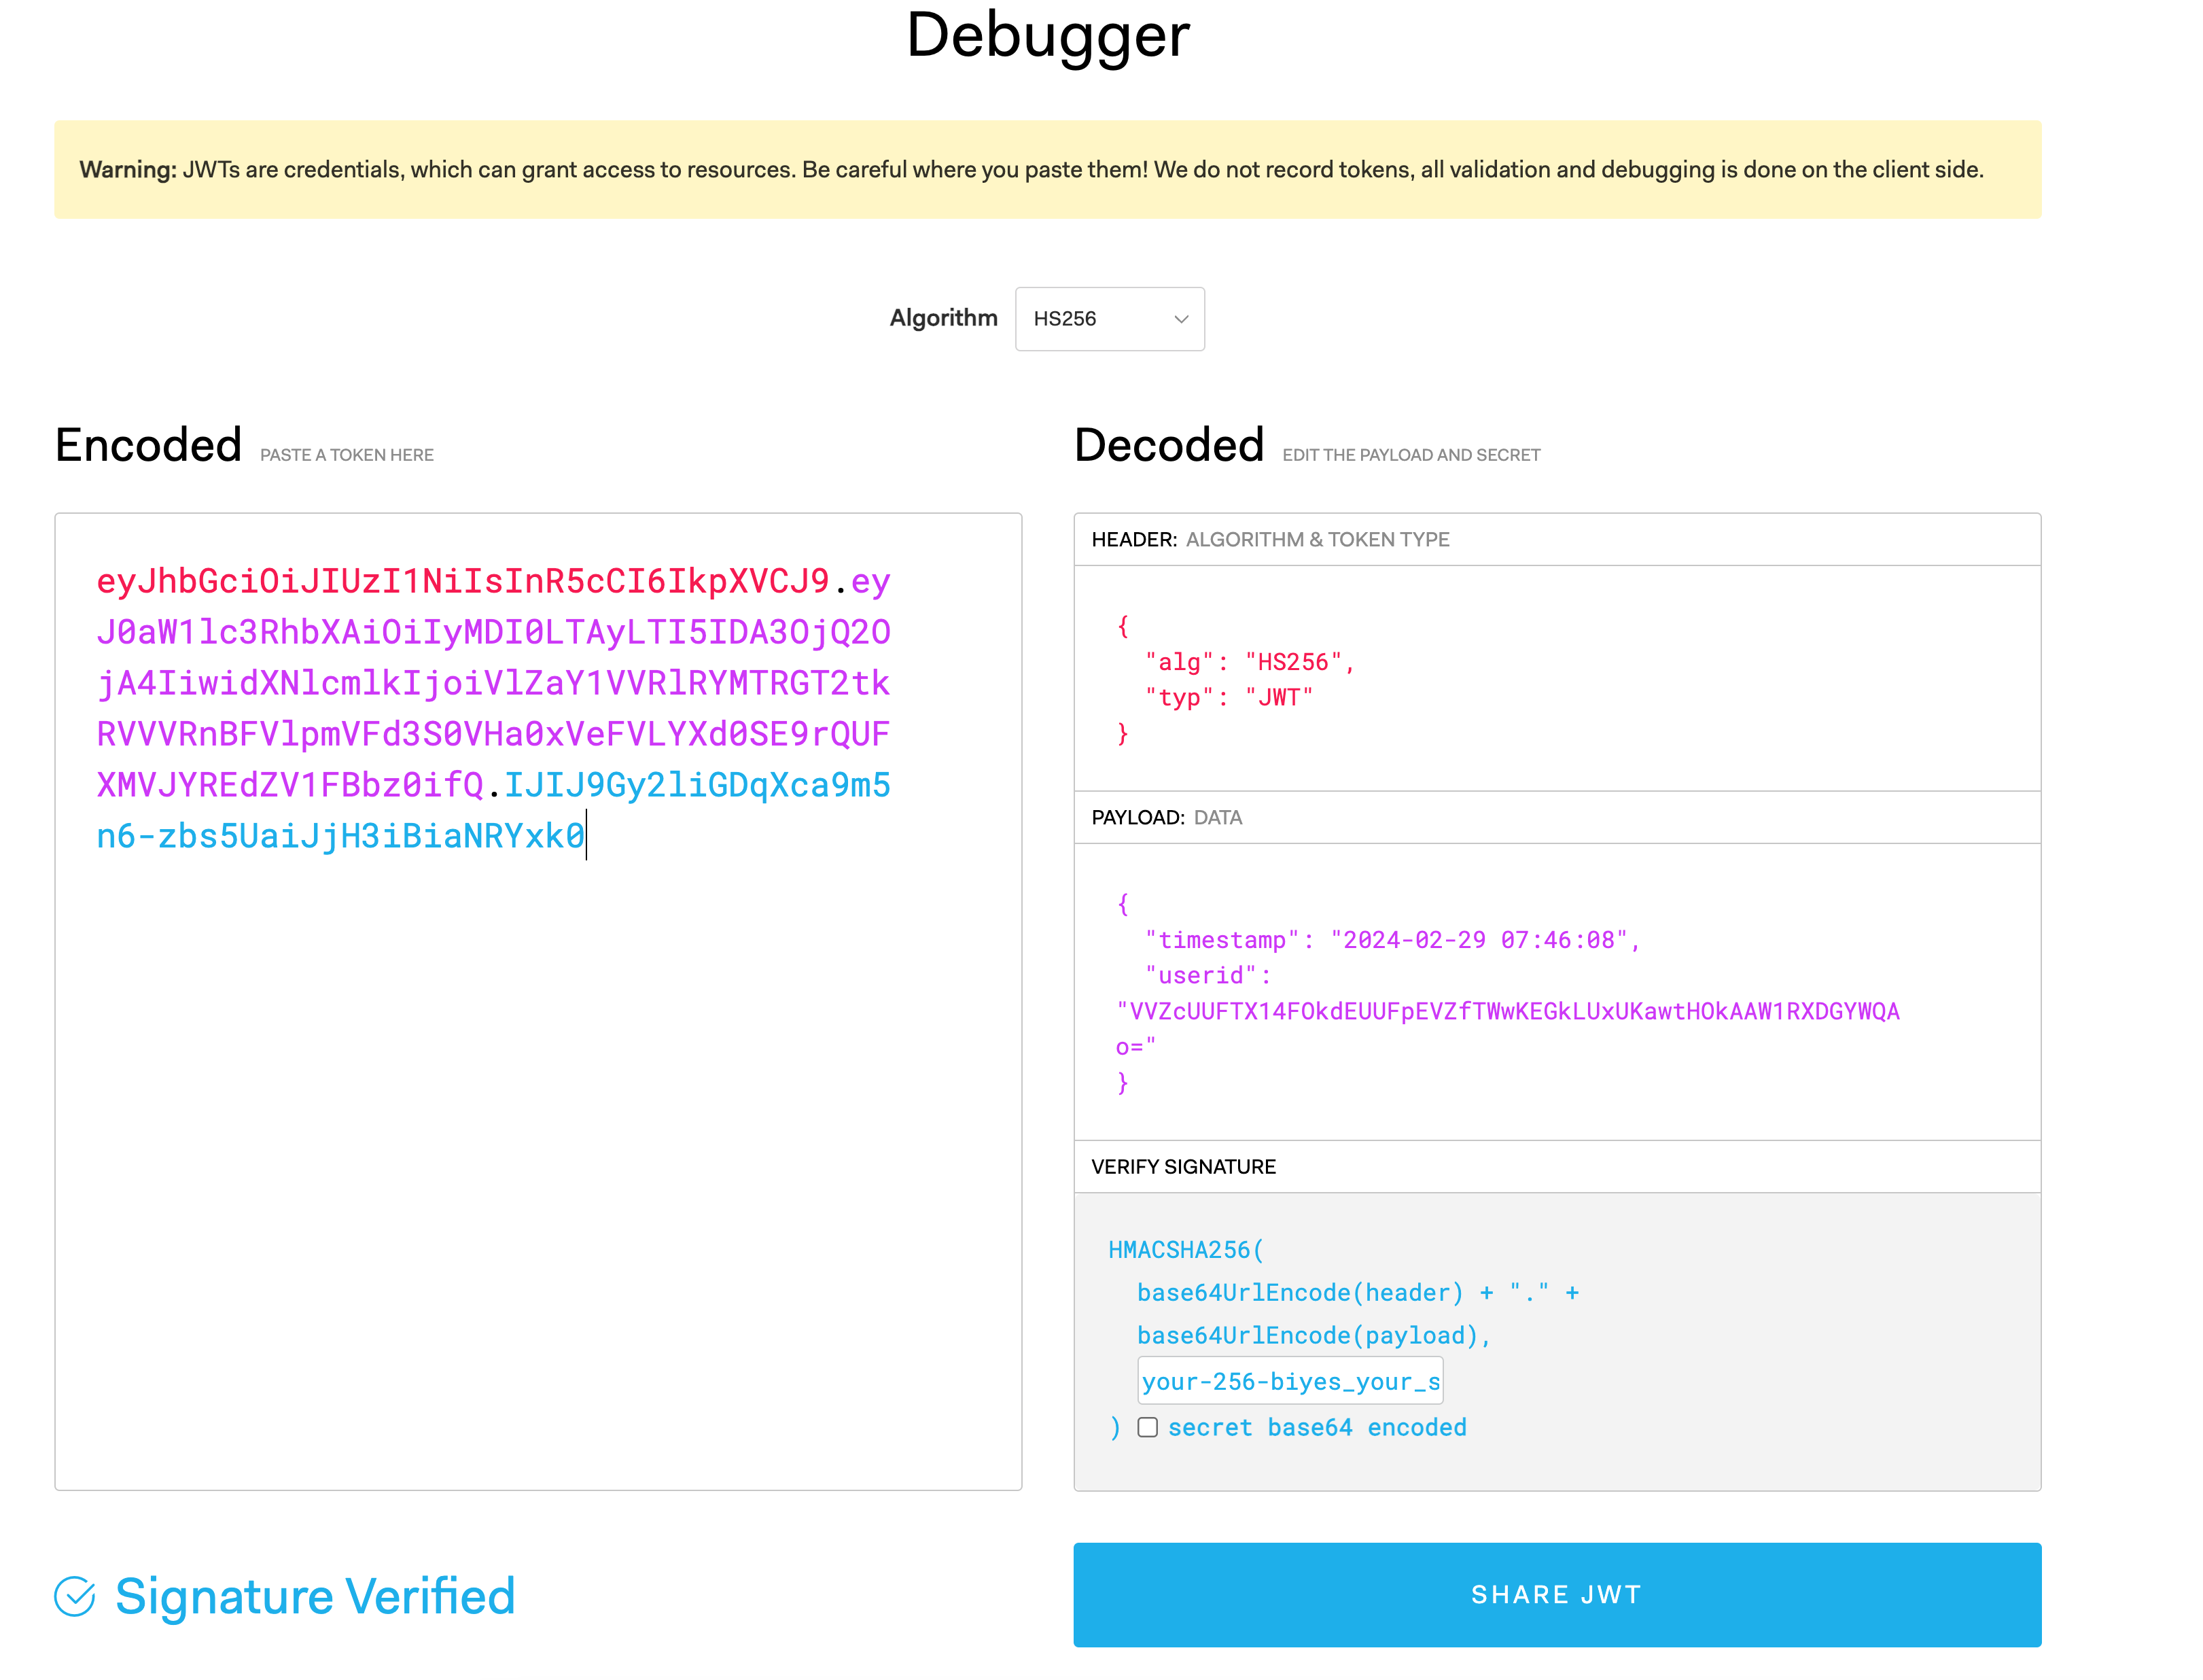 password123456/some-tweak-to-hide-jwt-payload-values
Lightweight Python library for obfuscating JWT payload values using XOR encryption with timestamp-based keys, preventing plaintext decoding of…
 gagaltotal/cve-2026-mikrotik-poc
CVE-2026-86060 - CVE-2026-67279 - CVE-2026-67276 RouterOS SSH
 sh4den/cve-2026-24061
Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…
 rz1027/cve-2026-20896
Public PoC and detector for CVE-2026-20896 ("Gitea Docker: One Header, Any User")
 k3ystr0k3r/cve-2024-27198-exploit
A PoC exploit for CVE-2024-27198 - JetBrains TeamCity Authentication Bypass
 userconnecting/exploit-cve-2023-49070-and-cve-2023-51467-apache-ofbiz
Authentication Bypass Vulnerability Apache OFBiz < 18.12.10.