Flowise-CVE-2025-58434-Chain-59528

FlowiseAI CVE-2025-58434 & CVE-2025-59528 exploit PoC, demonstrating unauthenticated ATO via reset token leakage, followed by authenticated RCE.…

FlowiseAI CVE-2025-58434 & CVE-2025-59528 exploit PoC, demonstrating unauthenticated ATO via reset token leakage, followed by authenticated RCE.…

Demonstrates CVE-2025-22235 Spring Boot authentication bypass via EndpointRequest.to() misconfiguration. Includes environment setup, reproduction…

Dockerized exploit environment for CVE-2024-10924, an authentication bypass in WordPress Really Simple Security plugin (versions 9.0.0-9.1.1.1)…

Isolated educational lab simulating CVE-2025-4679 OAuth credential exposure. Learn offensive and defensive security through hands-on exercises,…

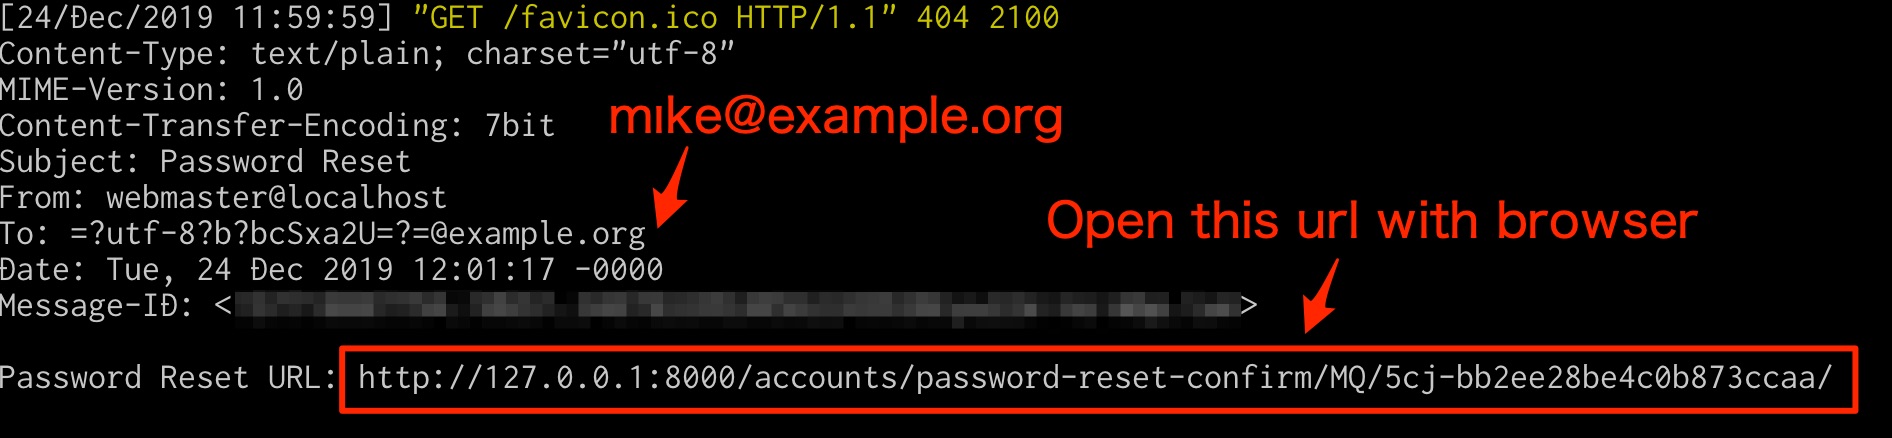
PoC for CVE-2019-19844(https://www.djangoproject.com/weblog/2019/dec/18/security-releases/)

This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.

This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.

Proof-of-concept exploit for CVE-2022-23131, a Zabbix SAML SSO authentication bypass vulnerability. Includes environment setup and a Go-based checker…

Proof-of-concept exploit for CVE-2022-4361, a reflected XSS vulnerability in Keycloak's OIDC authentication flow, with Docker-based test environment…

Proof-of-concept exploit for CVE-2026-24061, a telnetd authentication bypass via argument injection in the USER environment variable, allowing…

Proof-of-concept exploit for CVE-2019-0217, a race condition in Apache HTTP Server's mod_auth_digest allowing authentication bypass. Includes…

POC for CVE-2025-54918 and a technical demonstration.

this is a modified POC of rz1027 for CVE-2026-20896

Exploit for Red Hat / GlusterFS CVE-2018-1088 & CVE-2018-1112, featured @ DEFCON 26, Las Vegas!

Starlette Host-Header URL Confusion Lab (X41-2026-002) - CVE-2026-48710

Reproduces CVE-2025-0108 path confusion vulnerability in Nginx/Apache stacks. Includes a vulnerable PoC and a patched implementation demonstrating…

Reproducible Docker lab and Python PoC for CVE-2026-82329, an unauthenticated auth-bypass in JFrog Artifactory leading to admin takeover, with…

Proof-of-concept exploit for CVE-2026-13447, a critical authentication bypass in the WordPress MStore API plugin via forged Firebase JWT tokens, with…