
CVE-2026-20896
 xaoczenon/cve-2026-20896
this is a modified POC of rz1027 for CVE-2026-20896
authenticationeducationexploitation+3
xaoczenon/cve-2026-20896this is a modified POC of rz1027 for CVE-2026-20896
 derrickschoen/laravel-framework
Fork of laravel/framework 10.50.2 with CVE-2026-48019 (CRLF injection in default email rule) backported into ValidatesAttributes::validateEmail.…
 rz1027/cve-2026-20896
Public PoC and detector for CVE-2026-20896 ("Gitea Docker: One Header, Any User")
 google/longfellow-zk
Implementation of the Google Zero-Knowledge library for Identity Protocols.
 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
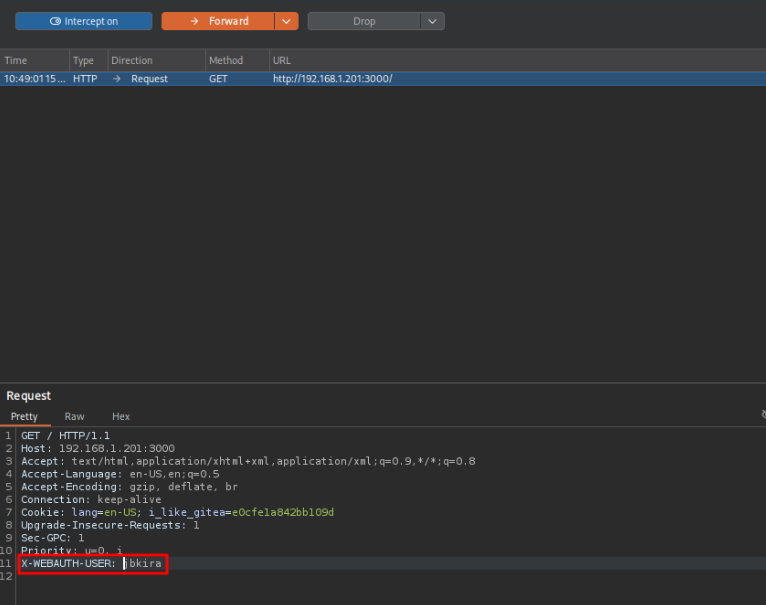 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 eliangonzi00/pockeycloakcve-2023-0264
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…
 authelia/authelia
The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.
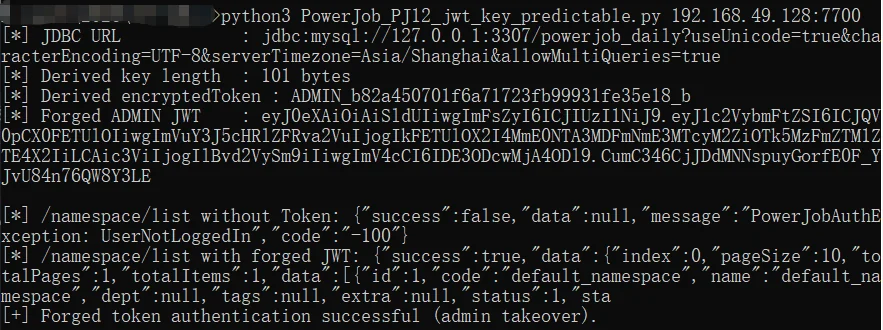 unpredictable21/cve-2026-75431_powerjob_jwt_key_predictable
Demonstrates a critical JWT signing key predictability vulnerability in PowerJob Server, allowing offline key derivation and token forgery for admin…
 leonjza/inetutils-telnetd-auth-bypass
A small docker lab to play with cve-2026-24061, the inetutils-telnetd authentication bypass.
 chandrimanath04-hue/cve-2024-31218-webhood-lab
Docker-based lab reproducing CVE-2024-31218, an unauthenticated PocketBase admin creation flaw in Webhood, with PoC, detection, and remediation…
 illera88/cve-2021-21239
Exploit for CVE-2021-21239: SAML signature validation bypass in pysaml2/Redash. Forges SAML responses with embedded public keys to impersonate users…
 biitts/cve-2026-49230-apisix-jwe-decrypt-auth-bypass
PoC for CVE-2026-49230: Apache APISIX jwe-decrypt authentication bypass (missing AES-GCM tag validation, CWE-354, CVSS 9.1)
 jayglxr/cve-2026-24061-poc
Proof-of-concept exploit for CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd via crafted NEW_ENVIRON USER variable,…
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
 youkergav/cve-2018-10933
Authentication Bypass in Server Code for LibSSH
 oriolrius/kafka-keycloak-oauth
Apache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction
 red-darkin/cve-2026-18963-keycloak
Proof-of-concept exploit for CVE-2026-18963, a critical Keycloak reset-credentials bypass enabling unauthenticated account takeover. Includes lab…