CVE-2025-25749-Weak-Password-Policy-in-HotelDruid-3.0.7

Proof-of-concept for CVE-2025-25749 demonstrating weak password policy in HotelDruid 3.0.7, with automated test scripts and mitigation…

Proof-of-concept for CVE-2025-25749 demonstrating weak password policy in HotelDruid 3.0.7, with automated test scripts and mitigation…

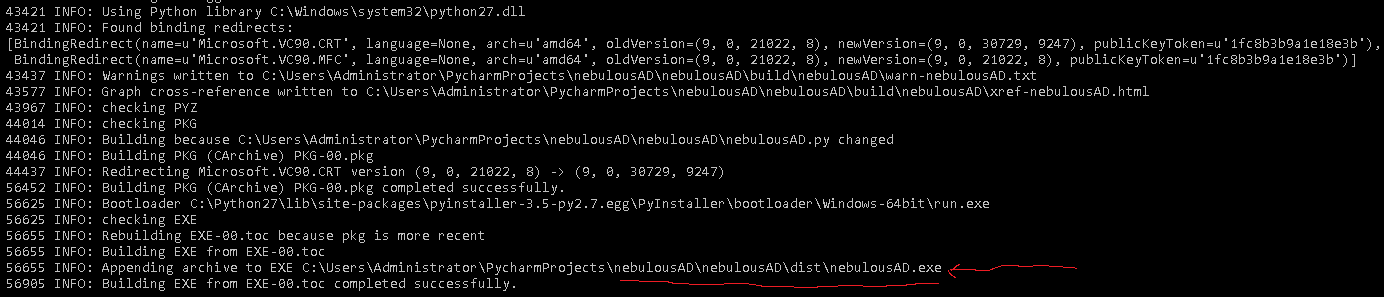
NebulousAD automated credential auditing tool.

Testing tool for the Mikrotrick exploit (CVE-2026-67276)

WordPress社交登录和注册(Discord,Google,Twitter,LinkedIn)<=7.6.4-绕过身份验证

Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.

Strelka Web UI for File Submission and Analysis

Proof-of-concept exploit and analysis for command injection and hardcoded backdoor credentials in D-Link NAS devices, enabling unauthenticated remote…

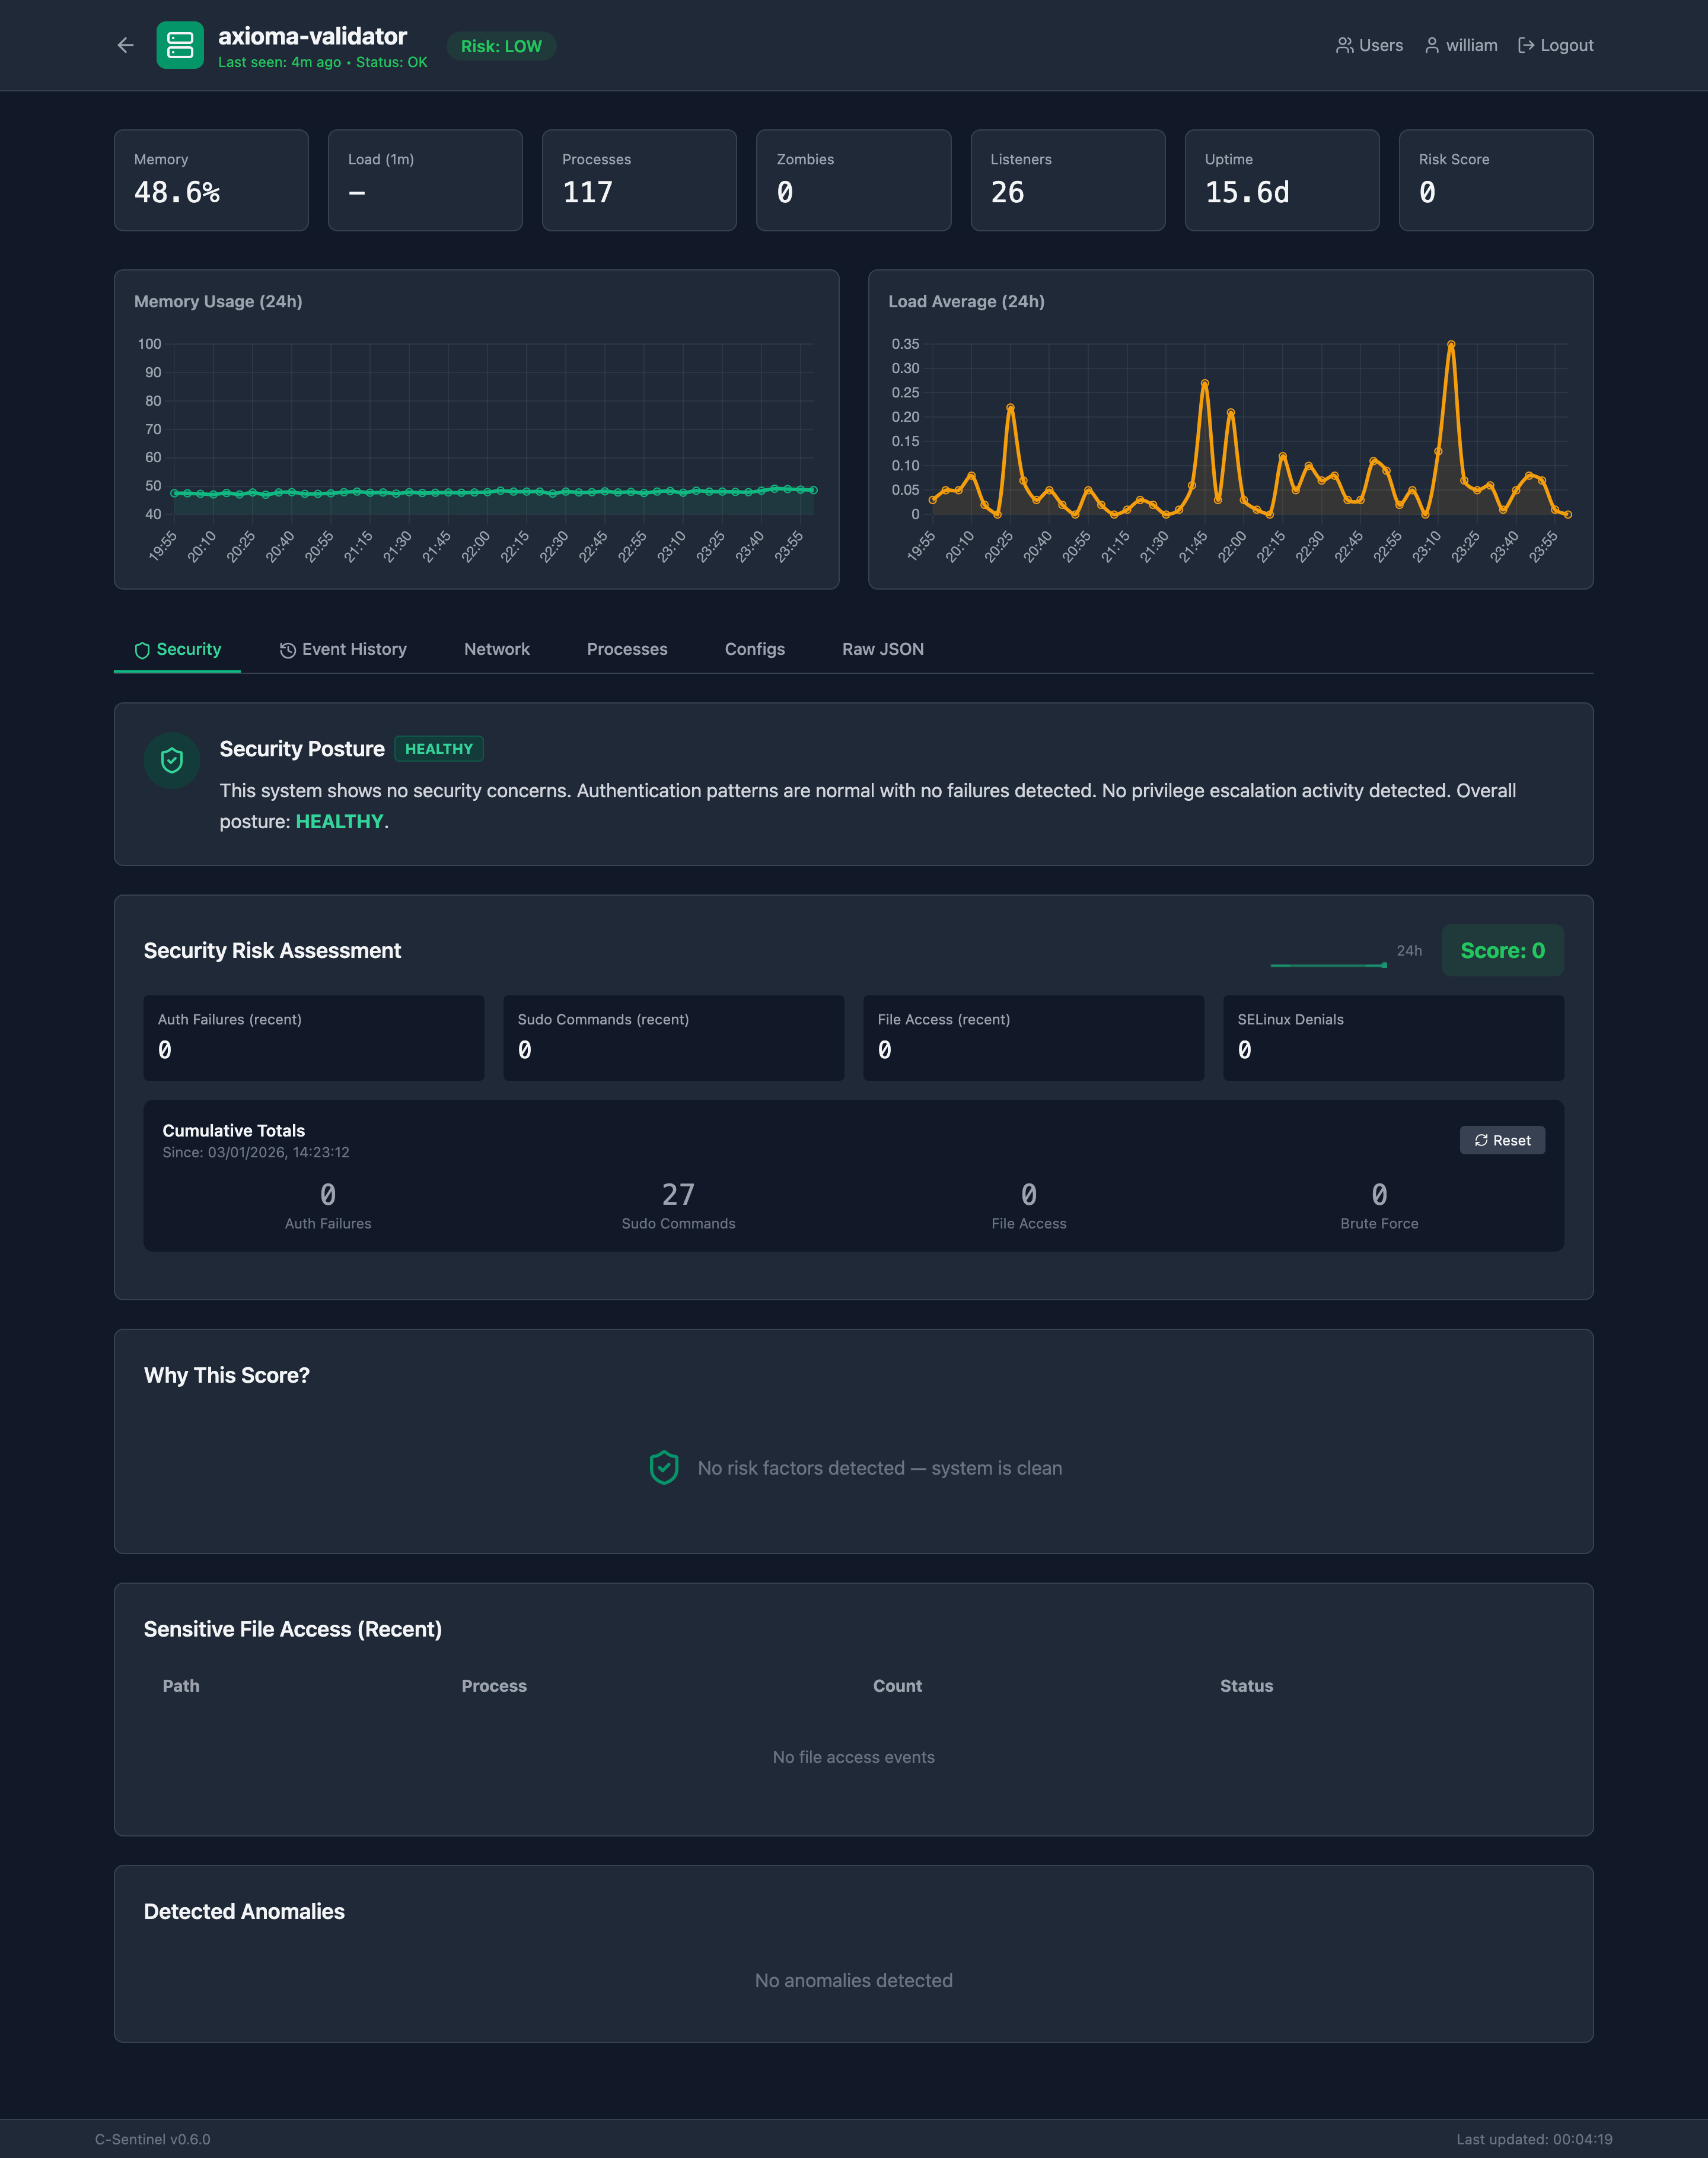
Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis

NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC

Reproducible Docker lab and Python PoC for CVE-2026-82329, an unauthenticated auth-bypass in JFrog Artifactory leading to admin takeover, with…

Defensive analysis, patch breakdown, and detection scanner for CVE-2026-14378 (WordPress DevKit Pro Plugin <= 2.3.0).

Research on CrushFTP AS2 authentication bypass allowing unauthenticated admin access. Includes PoC scripts, detection rules, and technical analysis…

Advisory and technical analysis of CVE-2026-15469, a hard-coded RSA-512 mesh group private key in TP-Link Deco routers, including root cause, impact,…

CVE-2026-49268 — Analysis and Remediation of an LDAP Injection Authentication Bypass Vulnerability

Technical analysis and PoC of CVE-2026-52824: default APP_SECRET in the Kimai Docker image enabling unauthenticated login link forgery. Affects <=…

Threat intelligence report repository for CVE-2026-9830, an authentication bypass vulnerability in BookingPress Pro WordPress plugin, with detailed…

Proof-of-concept exploit toolkit for SharePoint ToolPane RCE (CVE-2025-53770) with scanner, payload analysis, and multiple exploitation methods for…

Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…