
VibeSec-Skill
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.
ai-securityapi-securityauthentication+8
1.3k7 months ago
behisecc/vibesec-skillThis skill helps Claude write secure code and prevent common vulnerabilities.
 yubico/libfido2
Provides library functionality for FIDO2, including communication with a device over USB or NFC.
 rustcrypto/rsa
Pure Rust library for RSA public-key cryptography: key generation, PKCS#1 v1.5 and OAEP encryption/decryption, PSS signatures, plus key import/export.
 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
 compasssecurity/samlraider
SAML2 Burp Extension
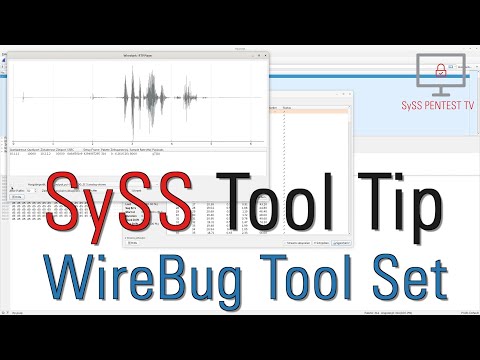 syss-research/wirebug
WireBug is a toolset for Voice-over-IP penetration testing
 libssh/libssh-mirror
C library implementing the SSH protocol for secure remote access, authentication, and encrypted communication. Includes fuzzing support via OSS-Fuzz…
 alt3kx/cve-2022-1388_poc
F5 BIG-IP RCE exploitation (CVE-2022-1388)
 blacksky-algorithms/atproto
Fork of the AT Protocol reference implementation with performance-optimized AppView, Rust-based firehose indexer, Redis caching, and community…
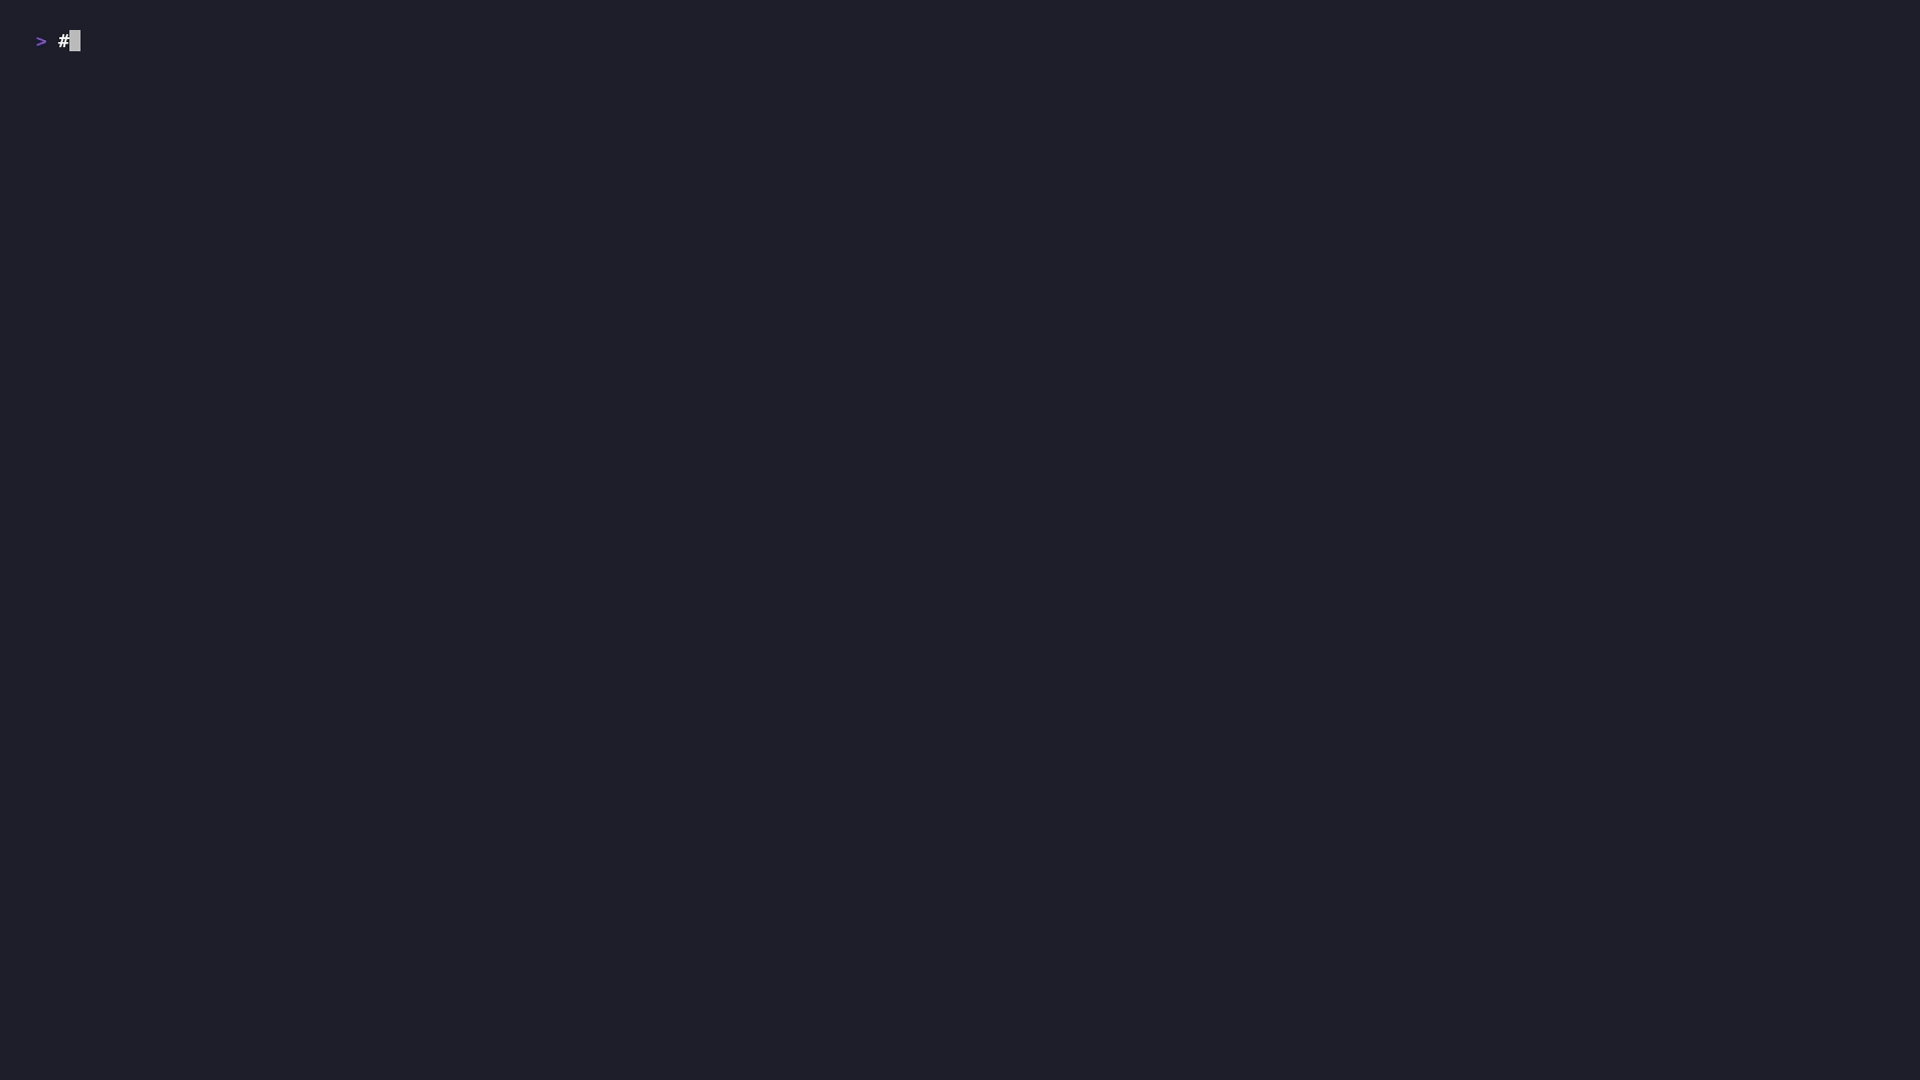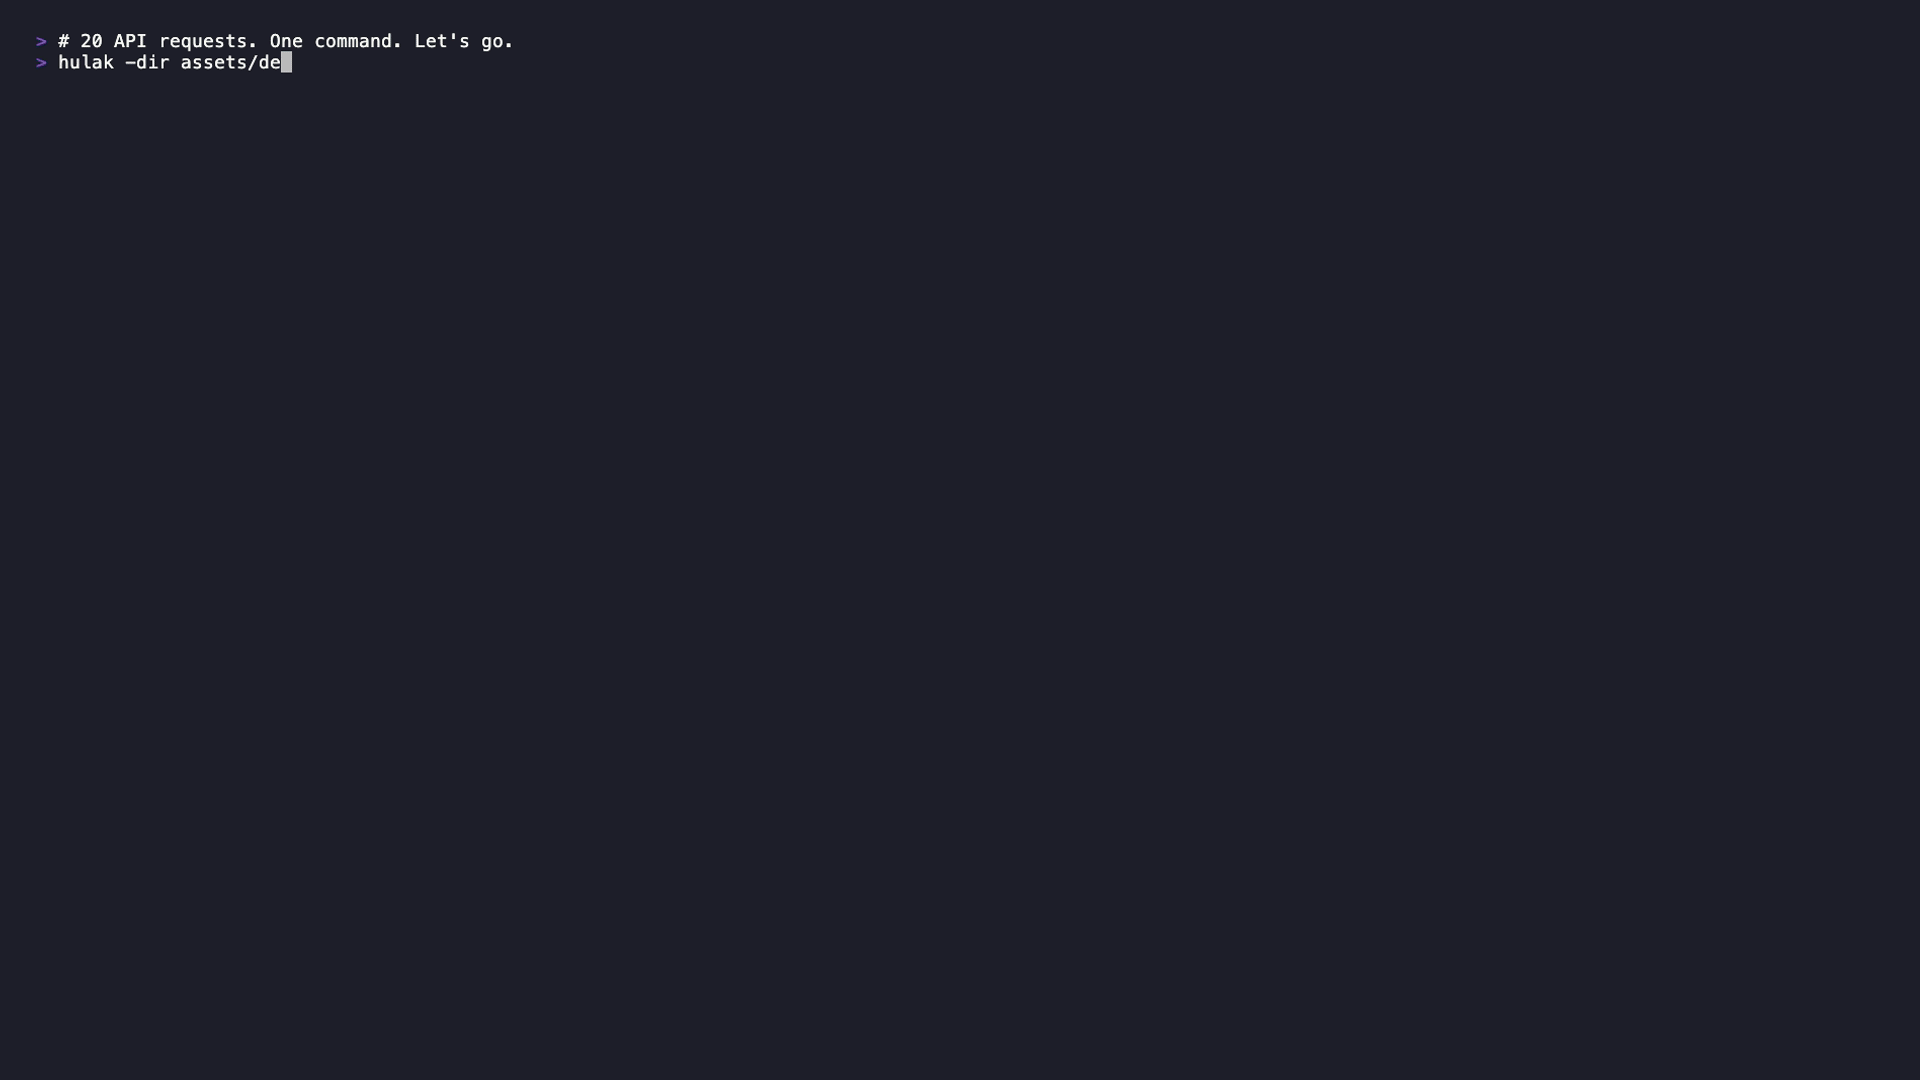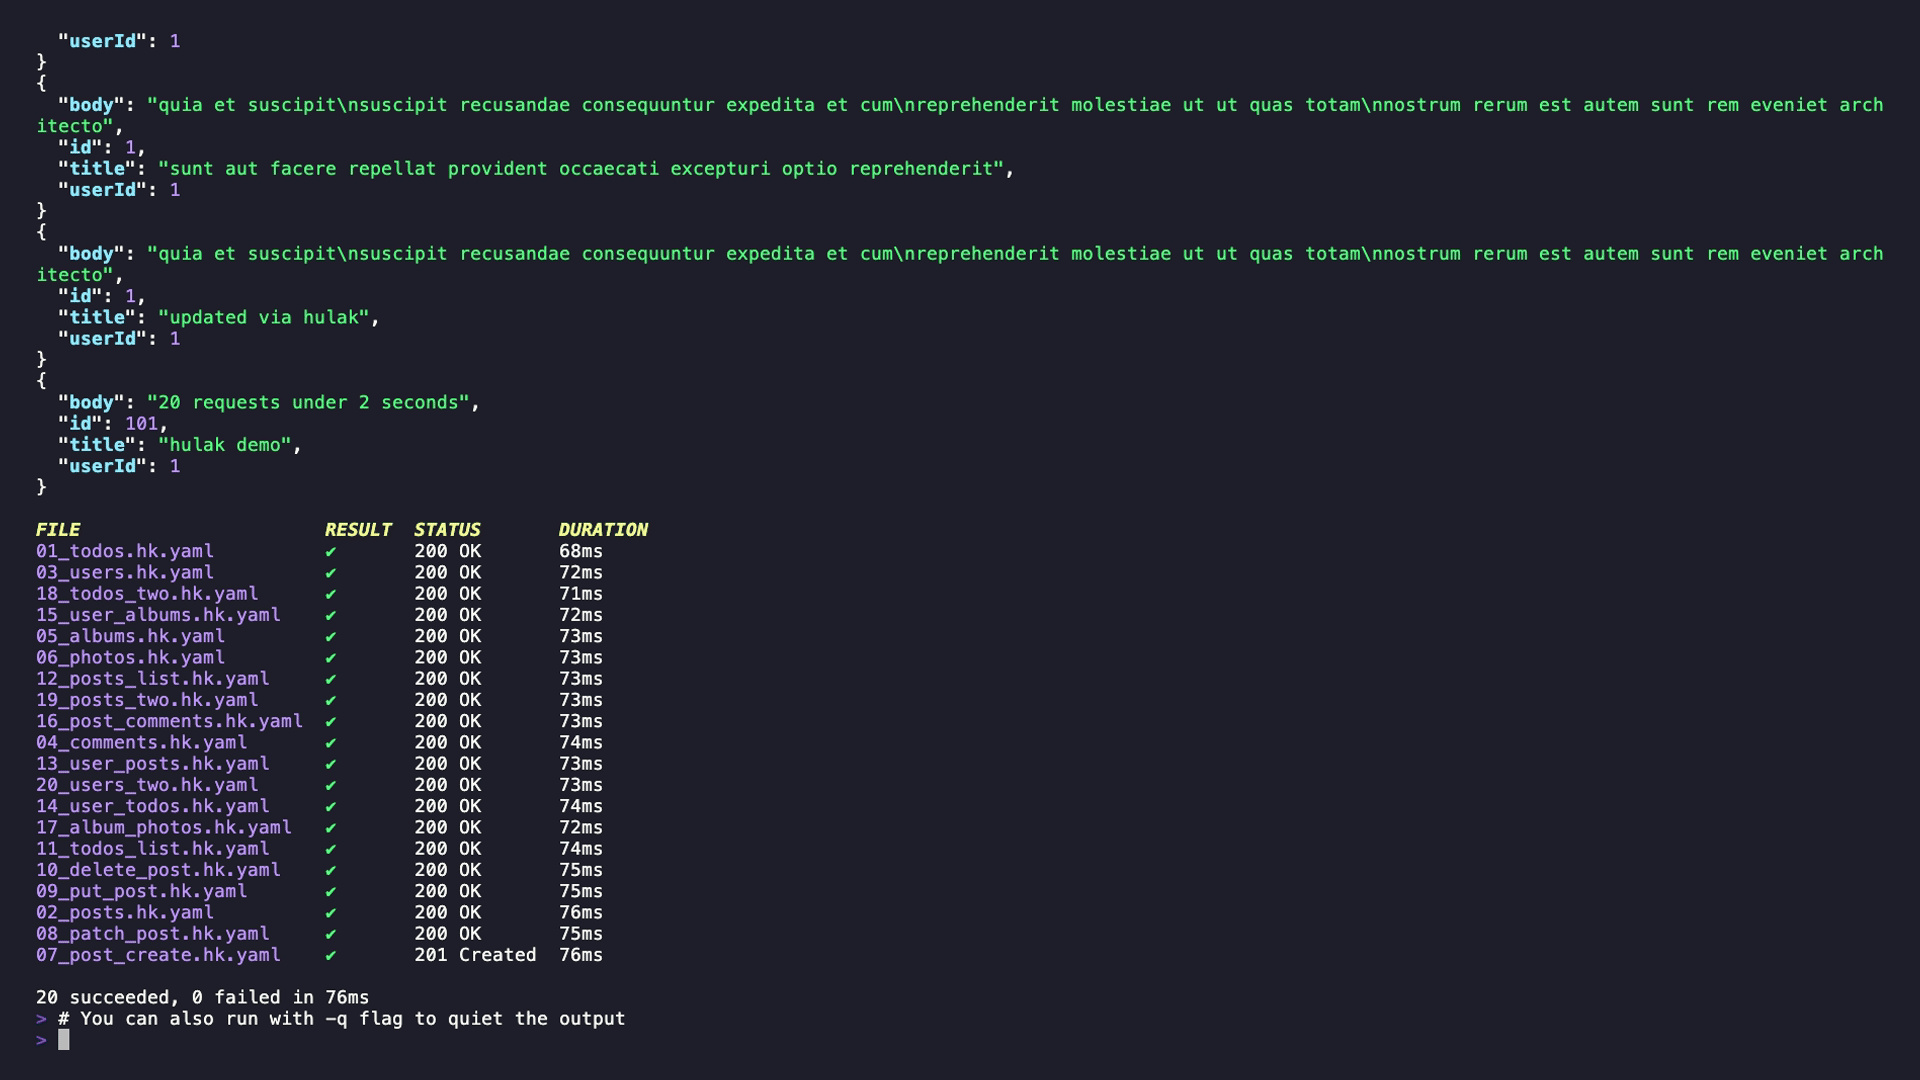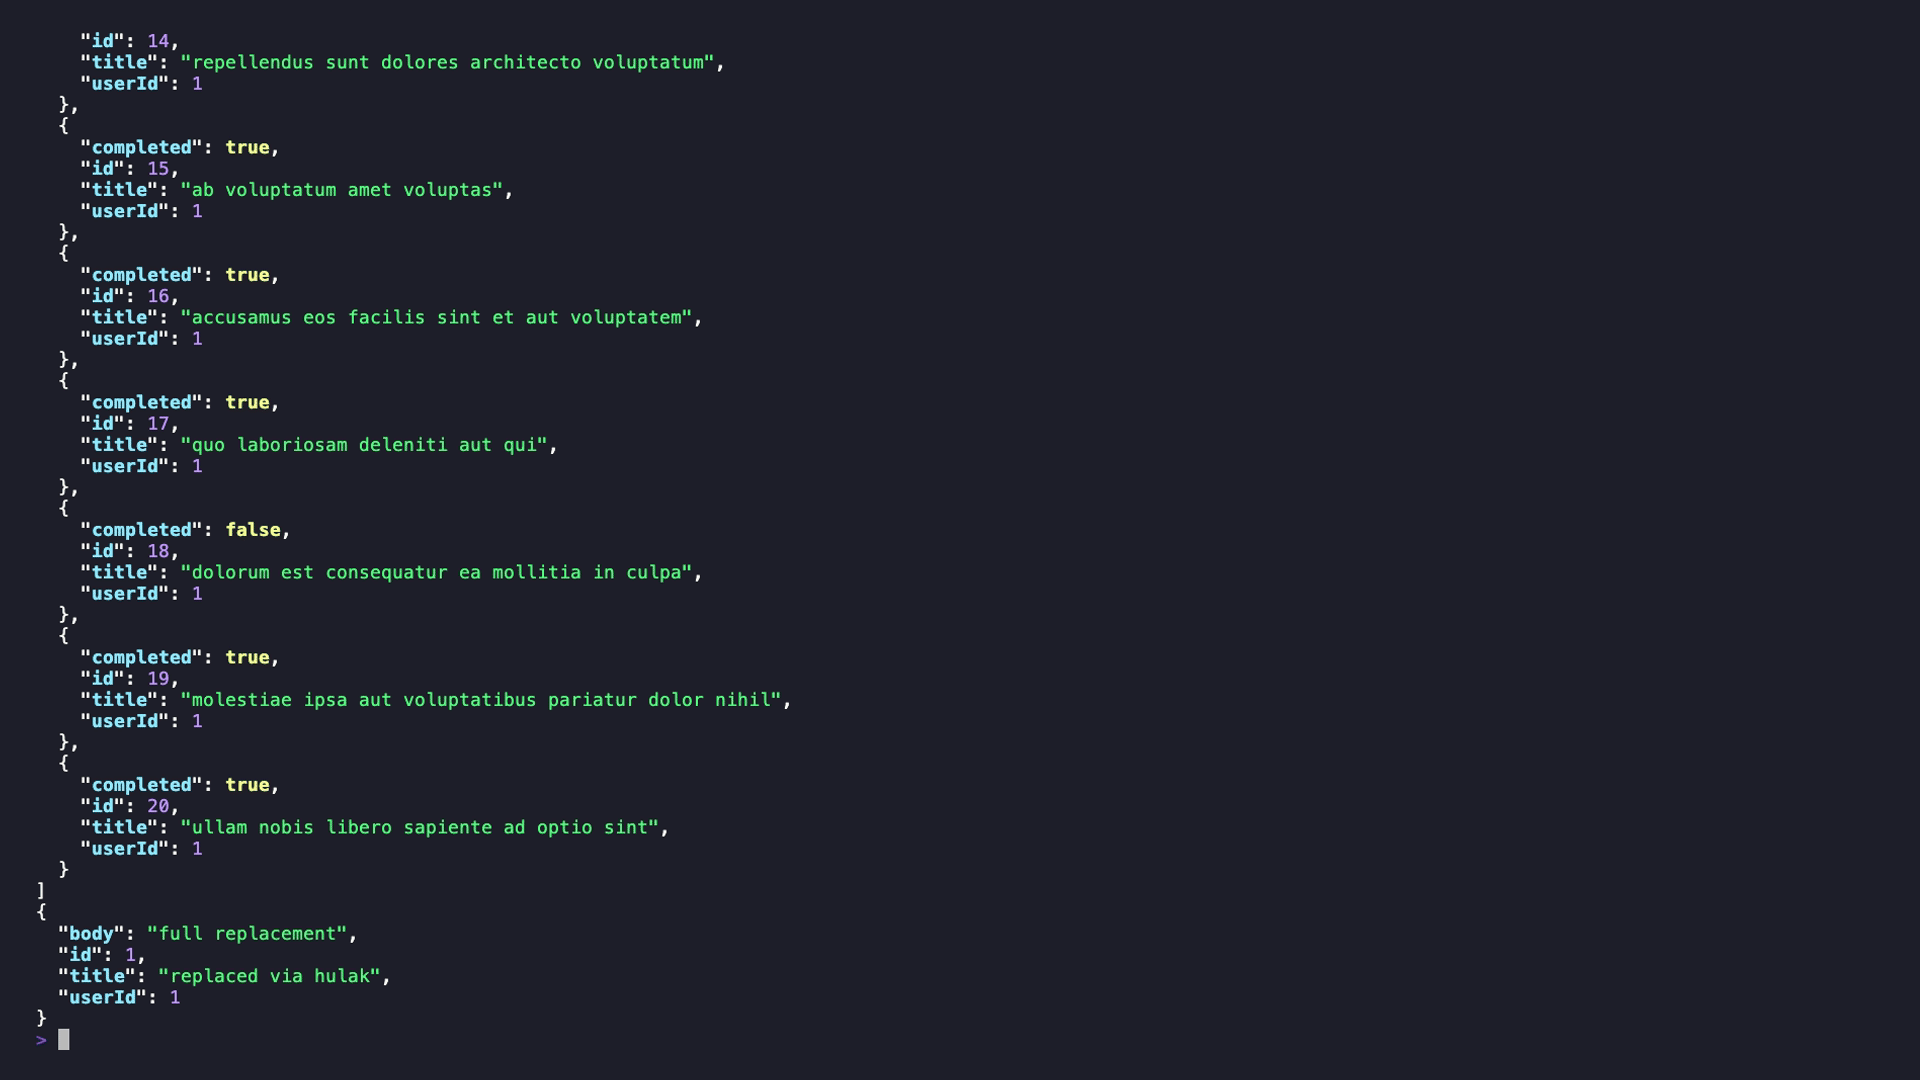 xaaha/hulak
Lightweight file-based CLI API client with age-encrypted secrets, first-class GraphQL support and MCP server for agentic workflow.
 fariszr/knocker
Knocker, a knock based access control service for your homelab
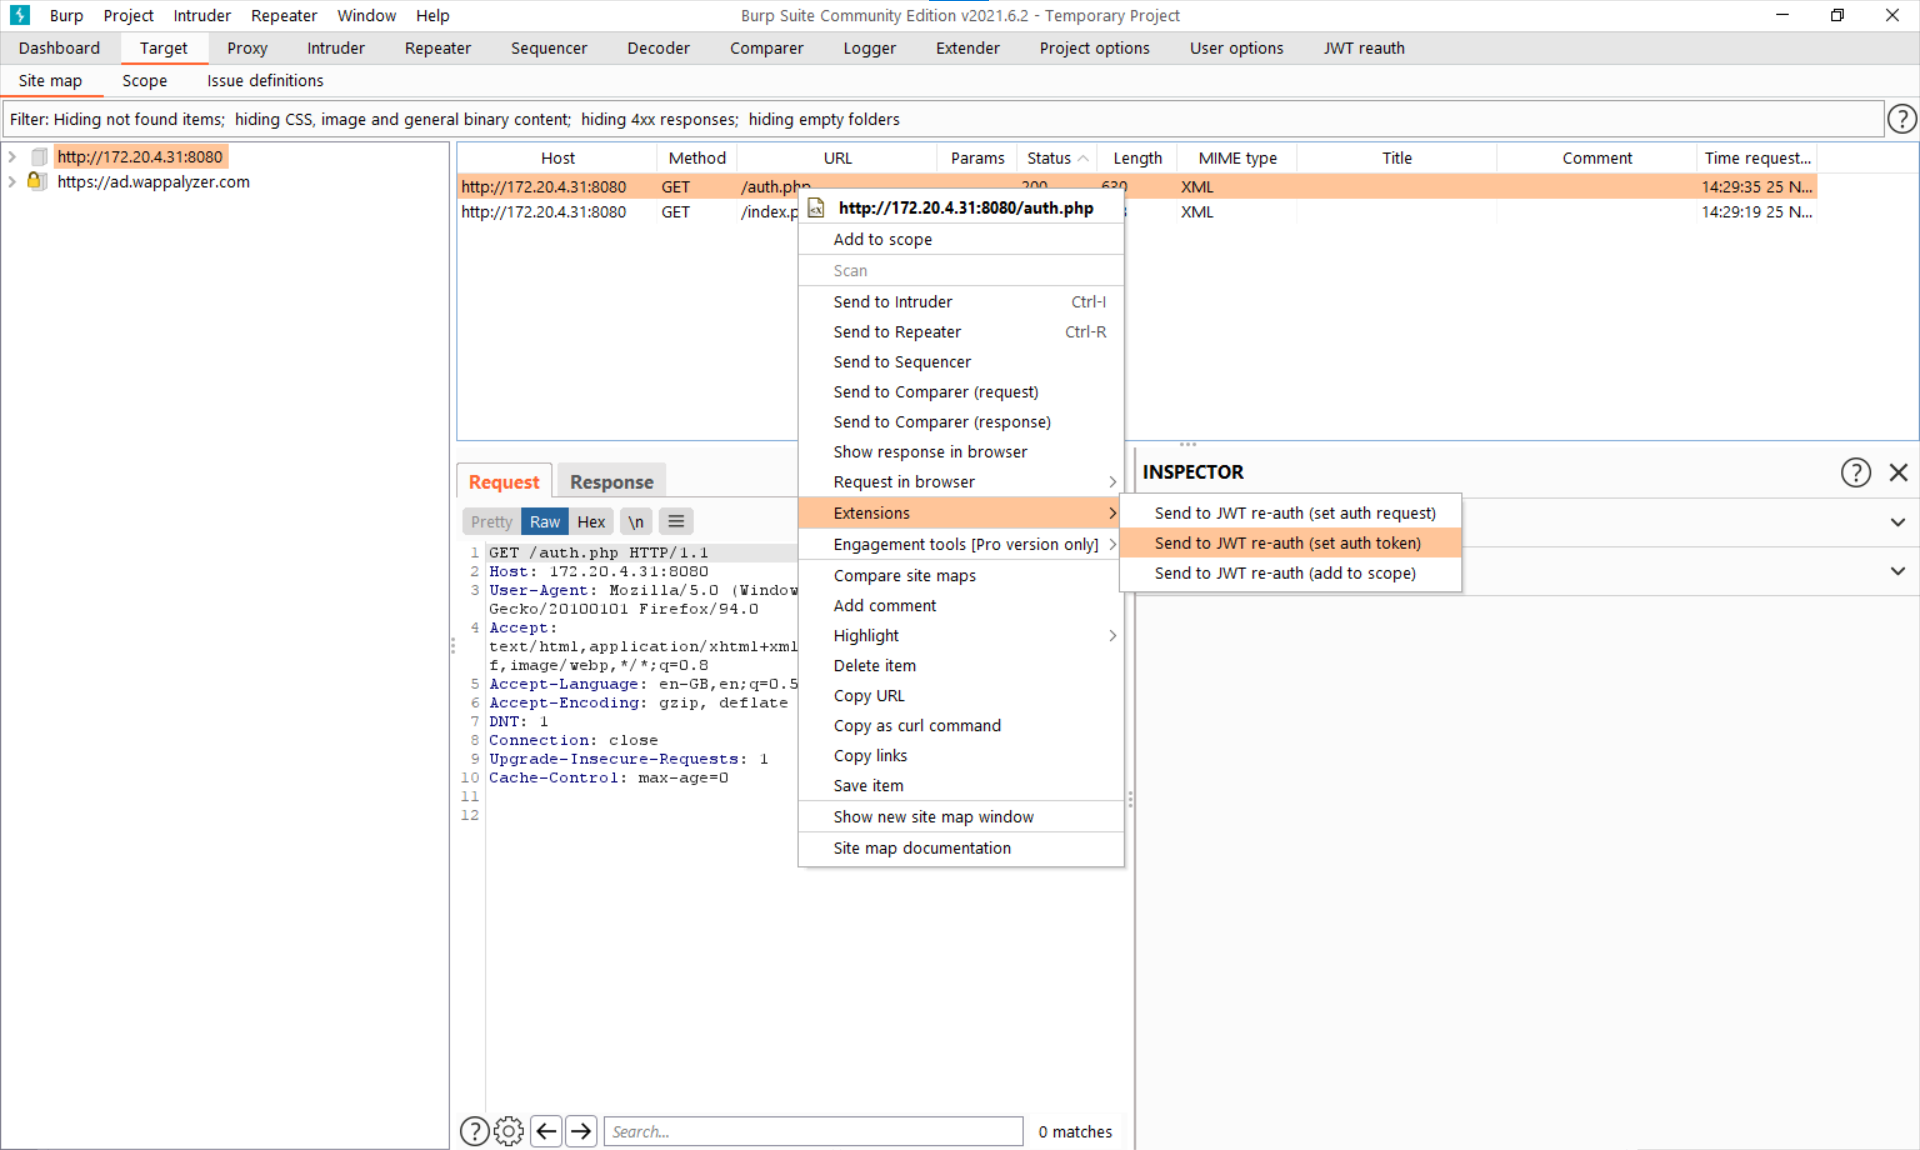 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
 vhscom/private-landing
🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…
 0xf4n9x/cve-2022-46169
CVE-2022-46169 Cacti remote_agent.php Unauthenticated Command Injection.
 n7on/dllspy
Discover input surfaces and security issues in compiled .NET assemblies — without running them.
 inflightsec/agent-vault-proxy
Just-in-time API keys for AI agents - and any other process you route through it: the caller only ever sees a placeholder.
 loadingalias/rscrypto
Rust crypto w/ zero default deps: BLAKE3, Ed25519/X25519, hashes, MACs, KDFs, AEADs, and checksums w/ full SIMD/ASM acceleration
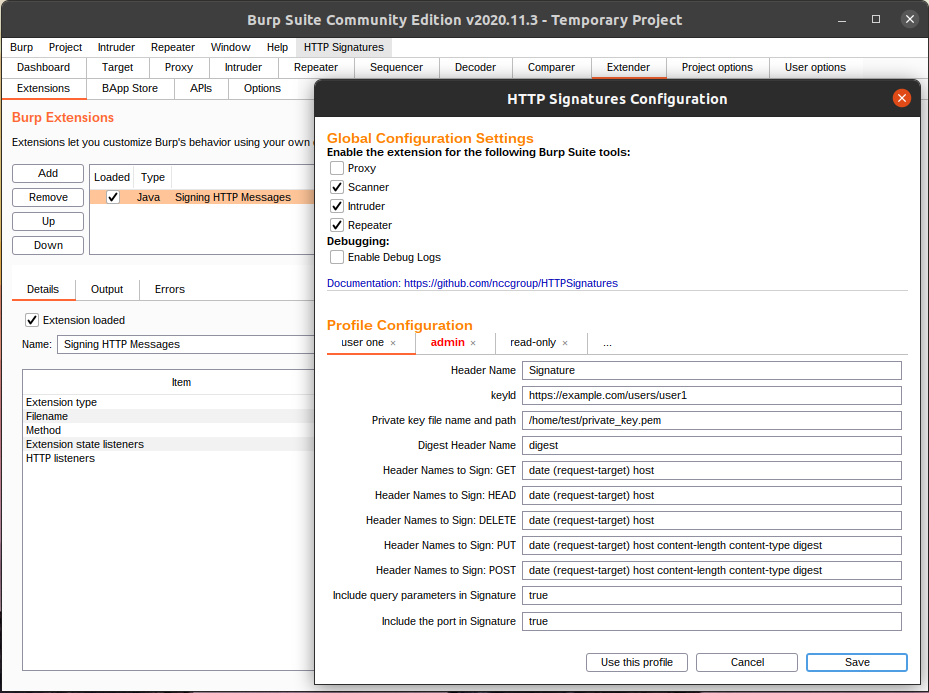 nccgroup/httpsignatures
A Burp Suite extension implementing the Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 draft.