
ResetNightmare-impacket
 mihat2/resetnightmare-impacket
CVE-2026-27912 (ResetNightmare) — Linux/impacket port of Semperis Community's Invoke-ResetNightmare PoC
authenticationexploitationinformation-gathering+4
1
mihat2/resetnightmare-impacketCVE-2026-27912 (ResetNightmare) — Linux/impacket port of Semperis Community's Invoke-ResetNightmare PoC
 lazaars/ultrarealy_with_cve-2019-1040
Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 sergiovks/ssh-user-enum-python3-cve-2018-15473
SSH User Enumerator in Python3, CVE-2018-15473, I updated the code of this exploit (https://www.exploit-db.com/exploits/45939) to work with python3…
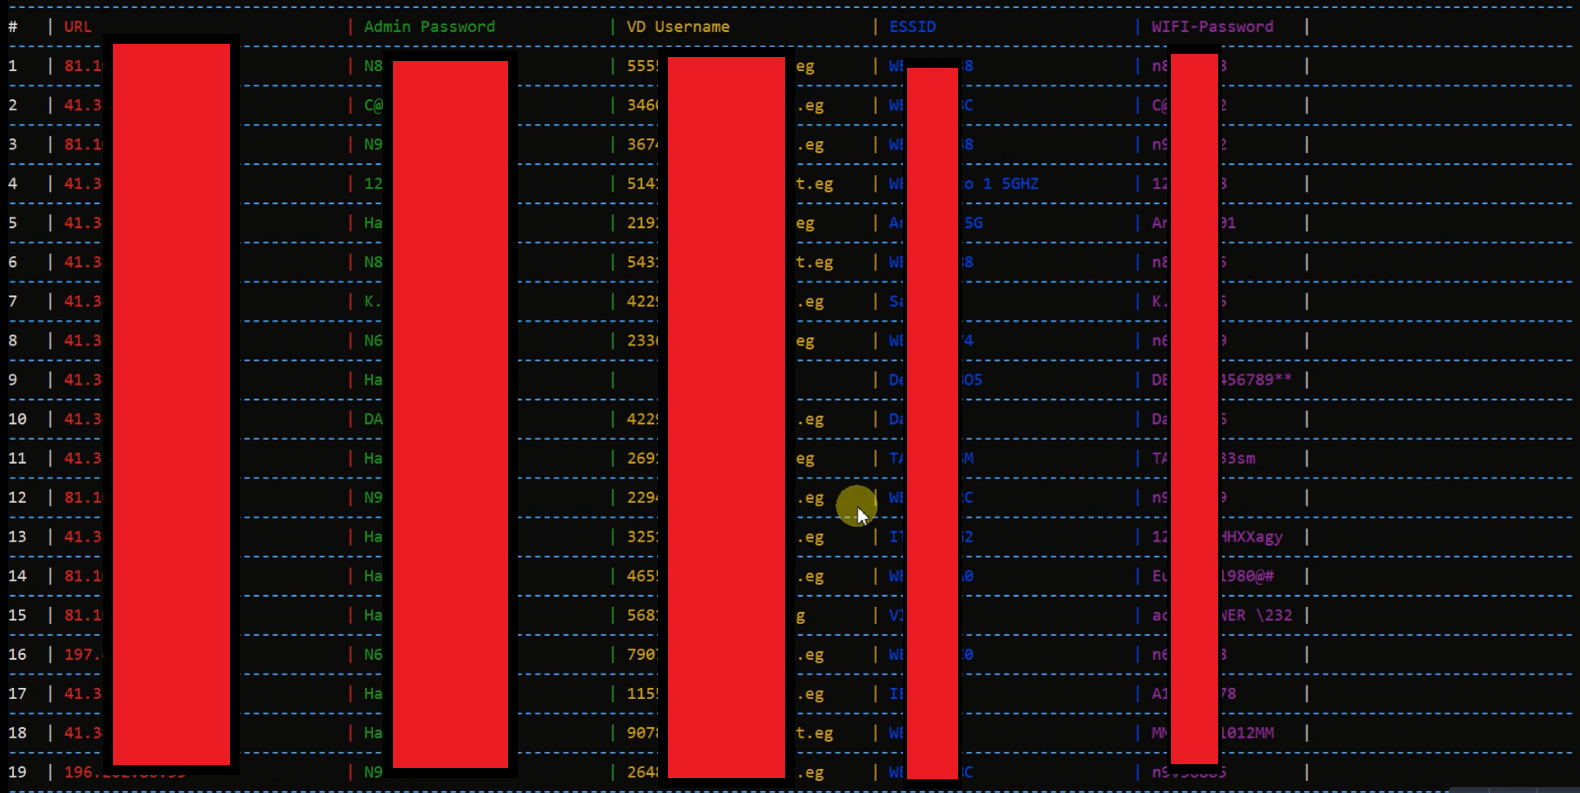 minanagehsalalma/cve-2026-34472-auth-bypass-zte-h188a-router
Technical breakdown of CVE-2026-34472, an auth bypass via leaked credentials affecting ZTE H188A routers.
 redteambrasil/cve-2020-24029
Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…
 itres-labs/usbcoercer
USBCoercer turns an ESP32 development board with native USB-OTG into an Ethernet-over-USB gadget capable of coercing proxy configuration via WPAD.
 lorenzocamilli/cve-2026-45332-poc
Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…
 perunchess/cve-2025-66698
Proof-of-concept for CVE-2025-66698: authentication bypass in Veda v5.4.8 via empty ticket parameter, enabling enumeration of users, policies, and…
 0xmandor/cve-2025-50433
Proof of concept for a critical Monnit Cloud account takeover (CVE-2025-50433), exploiting missing token-email validation in password reset and…
 ayewo/fortios-ldap-mitm-poc-cve-2019-5591
The default configuration of LDAP on FortiOS v6.0.x to v6.2.0 does not check server identity for LDAP/S leading to MITM attacks. This PoC demos full…
 kxisxr/bash-script-cve-2019-17662
ThinVNC 1.0b1 is vulnerable to arbitrary file read, which leads to a compromise of the VNC server. The vulnerability exists even when authentication…
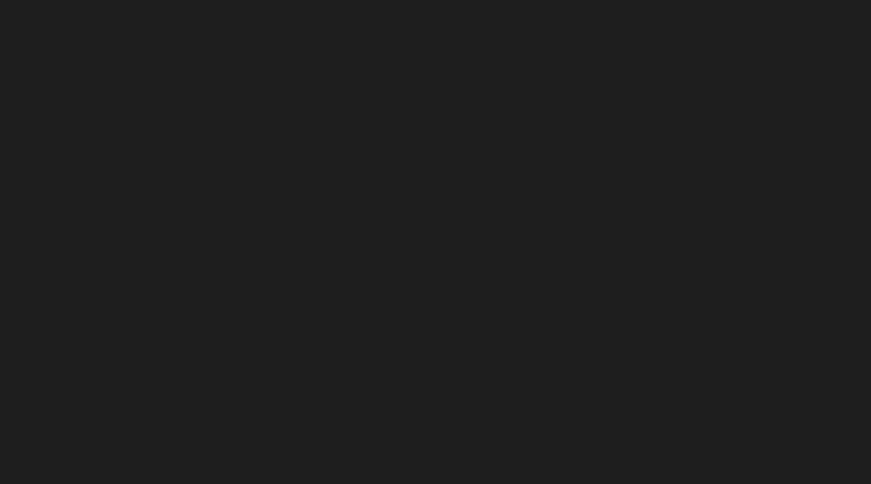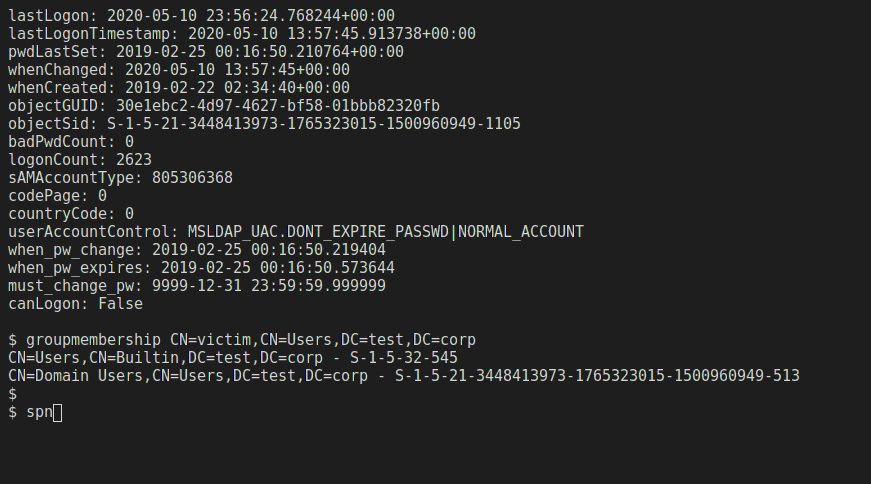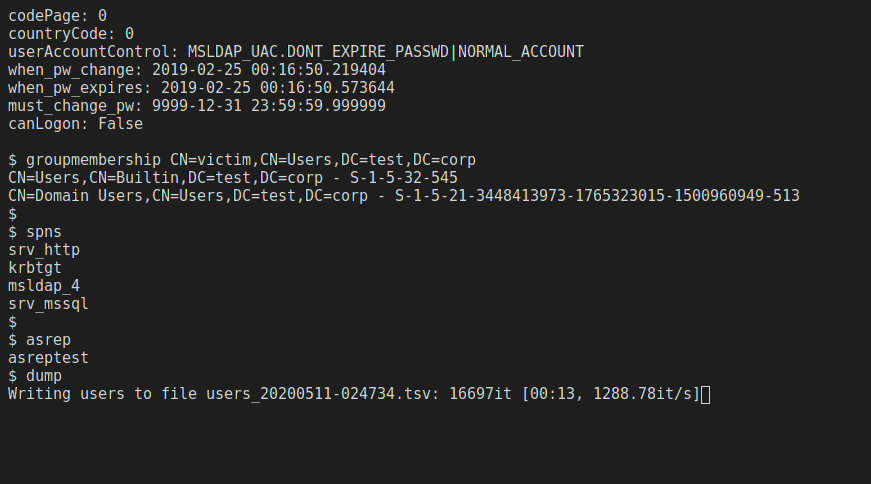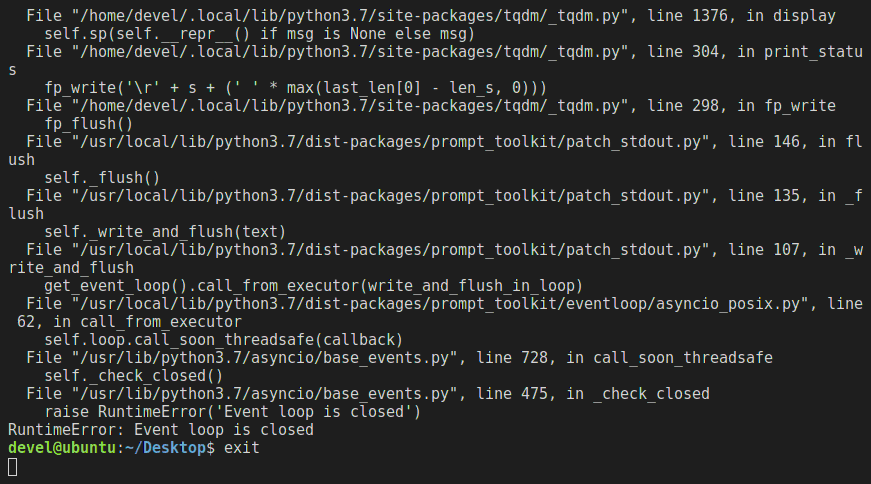 skelsec/msldap
Python library for auditing Microsoft Active Directory via LDAP, supporting NTLM, Kerberos, SSPI authentication, channel binding, encryption, and…
 pshlyundin/ldap_shell
Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.