
CVE-2024-56071
 nxploited/cve-2024-56071
Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation
authenticationexploitationmisconfiguration+5
nxploited/cve-2024-56071Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation
 b1g-b33f/cve-2020-14882
PoC for testing if a target is vulnerable to RCE
 quarantyne/quarantyne
Modern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails
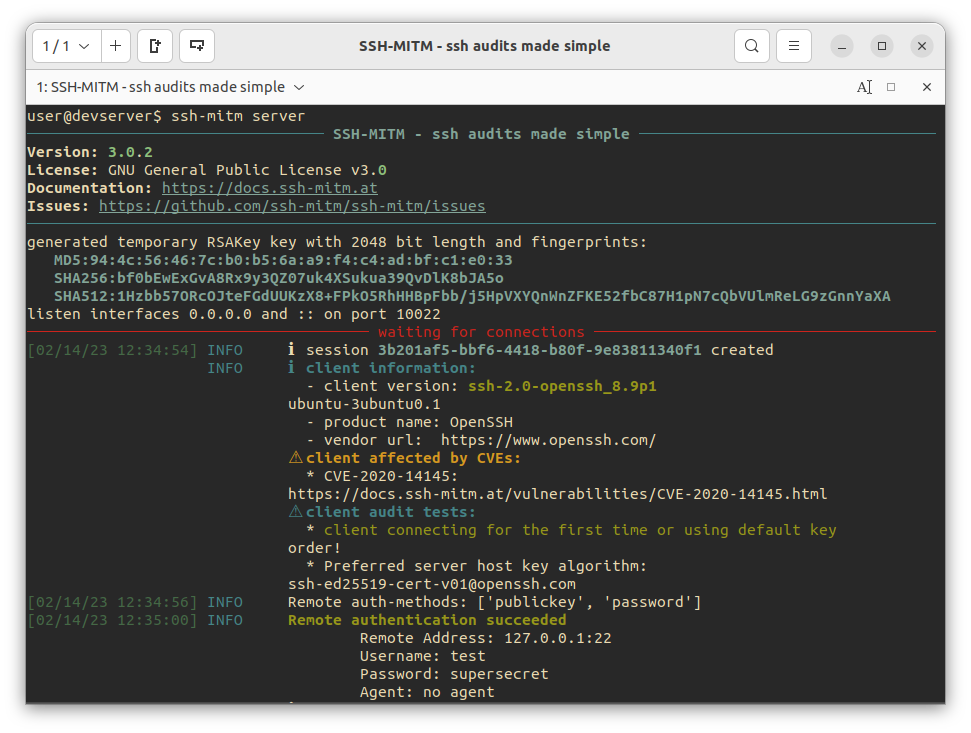 ssh-mitm/ssh-mitm
SSH-MITM - ssh audits made simple
 jazzband/django-defender
A simple super fast django reusable app that blocks people from brute forcing login attempts
 lmammino/jwt-cracker
Simple HS256, HS384 & HS512 JWT token brute force cracker.
 doyensec/cve-2022-39299_poc_generator
A Simple CVE-2022-39299 PoC exploit generator to bypass authentication in SAML SSO Integrations using vulnerable versions of passport-saml
 kn6869610/cve-2018-10933
Leveraging it is a simple matter of presenting the server with the SSH2_MSG_USERAUTH_SUCCESS message, which shows that the login already occurred…
 flaviupopescu/cve-2022-28601
A Two-Factor Authentication (2FA) bypass vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor
 m3ssap0/wordpress-really-simple-security-authn-bypass-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Really Simple Security < 9.1.2 authentication bypass (CVE-2024-10924). Run it…
 flaviupopescu/cve-2022-28986
A Insecure direct object references (IDOR) vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor
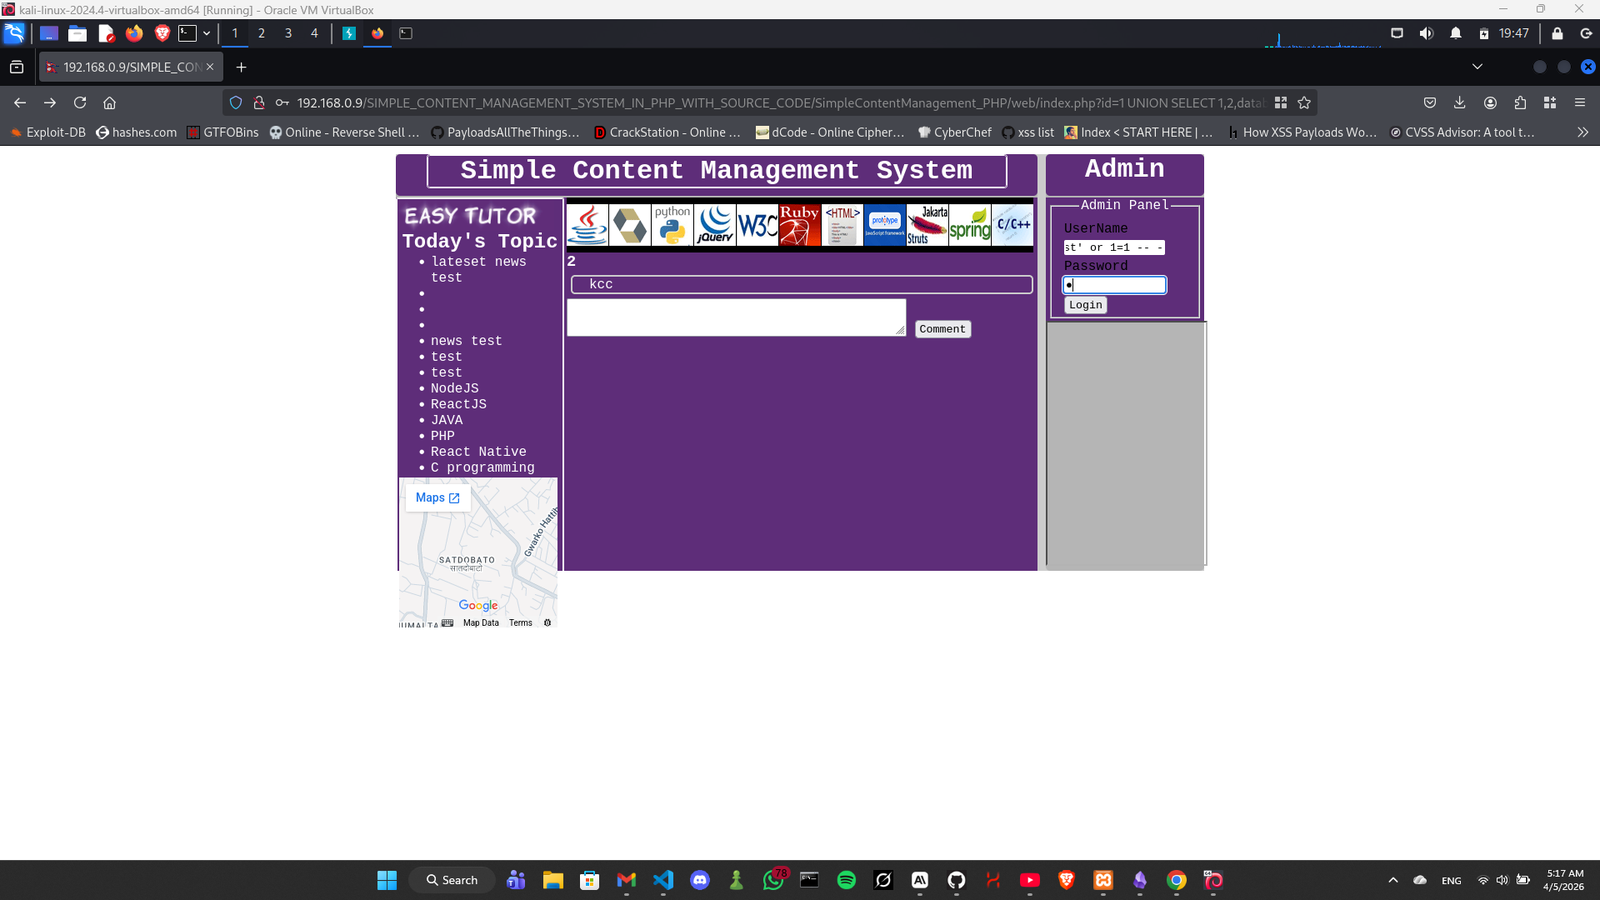 xmyronn/cve-2026-6182-sqli-auth
Proof-of-concept for SQL injection authentication bypass in Simple Content Management System PHP, allowing unauthenticated attackers to gain admin…
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
 seecret.it/seecret.it
Seecret.it est un service sécurisé de partage d’informations sensibles via des liens chiffrés et à usage unique. Idéal pour transmettre mots de…
 cy3erdr4g0n/cve-2024-10924
Exploit for CVE-2024-10924, a critical authentication bypass in WordPress Really Simple Security plugin (versions 9.0.0-9.1.1.1). Allows…
 lc-at/f609-brute
Simple brute force tool for Telkom Indonesia's ZTE F609 routers
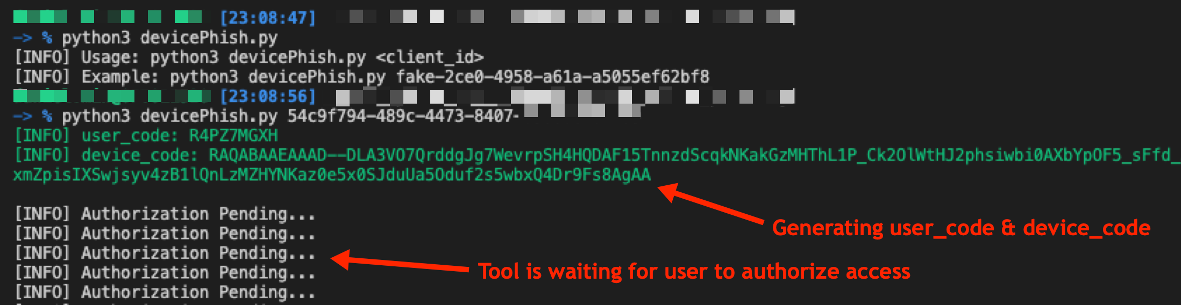 optiv/microsoft365_devicephish
A proof-of-concept script to conduct a phishing attack abusing Microsoft 365 OAuth Authorization Flow
 sensepost/cve-2025-64446
A scanner for the FortiNet vulnerability CVE-2025-64446